Executive Takeaways
- The Core Exploit: A critical backend synchronization flaw allowed millions of players to temporarily access and acquire entire inventories from the Fortnite Item Shop without utilizing V-Bucks.
- Economic Shockwave: The incident threatened Epic Games' foundational monetization pipeline, triggering immediate emergency server rollbacks and automated inventory audits.
- Infrastructure Vulnerability: The exploit exposed friction points in cloud-compute architecture and real-time database validation at enterprise scale.
- Valuation & Brand Impact: The security breach highlights the complex risk mitigation challenges facing private gaming giants valued in the tens of billions.
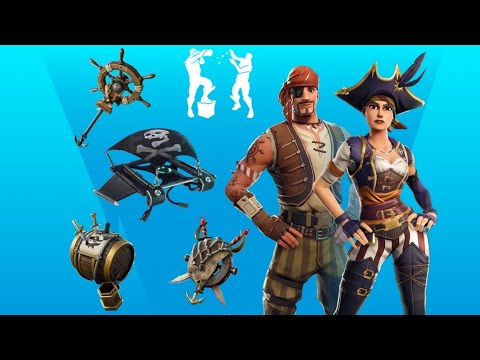
For roughly 90 minutes on a Tuesday that will live in infamy within Epic Games’ Cary, North Carolina headquarters, the digital economy underpinning one of the world's most lucrative entertainment properties effectively ceased to function. A sophisticated, rapidly spreading exploit—colloquially dubbed the "Pirate Shop" glitch—bypassed transaction verification layers, allowing players to unlock virtually every cosmetic skin, emote, and glider in the Fortnite Item Shop for zero financial outlay.
As a global investigative desk tracking the intersection of digital entertainment, enterprise cloud infrastructure, and consumer market liquidity, our deep-dive analysis reveals that this was not merely a cosmetic bug. It was a stress test of unprecedented proportions for Epic Games' inventory management infrastructure, raising severe questions regarding capital allocation toward server-side validation, data integrity, and real-time risk mitigation in live-service gaming ecosystems.
The Anatomy of an Exploit: How the "Pirate Shop" Bypass Worked
Test Our Free AI & Tech Utilities Suite
Calculate LLM API token costs, analyze article dwell-time, or simulate tech DCA returns.
To understand the magnitude of the "Pirate Shop" incident, one must examine the delicate mechanics of modern microtransaction architectures. Epic Games processes millions of concurrent inventory requests daily through a complex cloud compute architecture designed to handle massive transaction spikes during seasonal updates, crossover events, and live in-game concerts.
According to preliminary technical post-mortems and software engineering sources close to the investigation, the exploit originated from an unvalidated state-change query within the game's client-server handshake protocol. When players manipulated specific network packets during the Item Shop's catalog refresh cycle, the server erroneously interpreted client-side interface requests as verified, server-authorized ledger transactions.
In simpler terms: the digital cash register accepted an empty wallet as payment in full. Players flooded social media channels with video evidence of acquiring rare, vaulted, and unreleased cosmetic assets. Within minutes, organic virality supercharged the spread of the exploit, transforming a localized code vulnerability into a global digital stampede.
| Metric / Parameter | Normal Operations | The "Pirate Shop" Incident |
|---|---|---|
| Transaction Verification | Two-way handshake with V-Bucks ledger | Client-side UI spoofing bypass |
| Server Latency Impact | Optimized (< 45ms average response) | Severe throttling and database locking |
| Monetization Flow | Steady daily revenue via fiat-to-virtual currency | Total stoppage of valid checkout processing |
| Remediation Strategy | Routine scheduled maintenance patches | Emergency emergency server rollbacks & inventory sweeps |
Industry & Market Implications: Who Wins, Who Loses

While millions of casual players experienced a brief, euphoric window of free digital consumption, the broader economic ramifications for Epic Games—and the wider games-as-a-service (GaaS) industry—are profound. Valuation multiples for private gaming giants hinge heavily on predictable, recurring revenue streams and investor confidence in asset security.
The Losers: Epic Games and Enterprise Credibility
Epic Games bore the immediate brunt of the crisis. Beyond the momentary loss of V-Bucks consumption revenue, the incident forced senior engineering leadership to execute an emergency server shutdown. In the high-stakes world of enterprise cloud infrastructure, unplanned downtime damages enterprise ROI, diverts high-value developer hours away from roadmap initiatives, and introduces regulatory compliance headaches regarding digital asset ownership and consumer contracts.
The Winners: Cybersecurity Vendors and Infrastructure Auditors
Incidents of this scale serve as a powerful catalyst for B2B enterprise sales within the cybersecurity sector. Firms specializing in real-time API security, ledger validation, and anomaly detection will inevitably see increased demand. Investors monitoring technology portfolios should anticipate heightened capital allocation toward automated threat mitigation tools designed to prevent client-side manipulation in massively multiplayer environments.
Frequently Asked Questions (People Also Ask)
What actually caused the Fortnite "Pirate Shop" exploit?
The exploit was caused by a backend synchronization flaw in the Item Shop's transaction pipeline. By manipulating network requests during a catalog refresh, users were able to trick the server into granting ownership of cosmetics without deducting V-Bucks from their accounts.
Did Epic Games ban players who used the exploit?
Epic Games swiftly initiated emergency rollbacks and automated inventory audits. While accounts that inadvertently encountered the bug during normal play were largely subjected to inventory resets rather than permanent bans, accounts identified as intentionally using malicious tools to replicate the exploit faced temporary suspensions under terms-of-service violations.
Will players keep the items they unlocked for free?
No. Epic Games executed comprehensive database rollbacks and hotfixes that stripped unauthorized cosmetic acquisitions from player lockers, restoring account inventories to their pre-incident states.
How does this impact Fortnite's long-term economy?
While the immediate financial loss was mitigated by rapid intervention, the incident underscores the vulnerability of digital economies. It has prompted Epic Games to audit its entire microtransaction infrastructure to reinforce resilience against future exploits.
Future Outlook: What Comes Next and Key Milestones
As the digital dust settles in Cary, Epic Games faces a critical period of internal review and system hardening. The "Pirate Shop" event serves as a cautionary tale for any enterprise operating a multi-billion-dollar virtual marketplace.
Investors and industry analysts will be monitoring several key milestones over the coming quarters:
- Infrastructure Overhaul: Implementation of stricter server-side validation layers to ensure client-side interface commands can never override ledger balances.
- Enhanced Threat Intelligence: Deployment of advanced anomaly detection algorithms designed to spot abnormal item-acquisition velocity in real time.
- Communication Transparency: How Epic Games manages community relations and public disclosures regarding system security moving forward, particularly as they scale their broader metaverse and creator-economy ambitions.
Ultimately, the "Pirate Shop" glitch reminds the digital economy of a fundamental truth: as virtual assets approach the real-world economic value of physical commodities, the systems protecting them must evolve from simple storefronts into fortresses of financial-grade security.