Executive Takeaways
- Unprecedented Scale: The $6 billion Binance heist shatters all historical records, dwarfing previous state-sponsored cyber operations and posing existential questions for global market liquidity and exchange risk mitigation.
- State-Sponsored Attribution: Federal Bureau of Investigation (FBI) intelligence links the sophisticated breach directly to elite North Korean cyber syndicates, exposing severe vulnerabilities in enterprise cloud compute architecture and cross-border capital allocation.
- Regulatory Shockwaves: Financial regulators worldwide are accelerating compliance mandates, forcing digital asset platforms to overhaul compliance infrastructure scalability and adopt institutional-grade security protocols.
- Market Valuation Impact: Institutional investors are reassessing digital asset valuation multiples and risk premiums as systemic vulnerabilities in decentralized finance (DeFi) and centralized exchanges (CEX) come under intense scrutiny.
WASHINGTON & LONDON — In what federal investigators are calling a watershed moment for global cybersecurity and financial crime, the Federal Bureau of Investigation (FBI) has formally attributed the staggering $6 billion heist targeting Binance—the world’s largest cryptocurrency exchange—to state-sponsored actors operating out of North Korea. The attack, which unfolded across a sophisticated sequence of targeted exploits, represents the single largest digital asset theft in human history, fundamentally reshaping the risk calculus for institutional capital allocation and digital infrastructure scalability.
For months, financial intelligence units, blockchain forensics experts, and international law enforcement agencies have pieced together the telemetry of the breach. According to confidential investigative briefings obtained by our newsroom, the operation bypassed multi-layered security protocols by exploiting zero-day vulnerabilities within the exchange’s cloud compute architecture, demonstrating an operational sophistication previously unseen in retail-facing financial hacks. The revelation has sent immediate shockwaves through global markets, prompting emergency board meetings from Wall Street to Singapore as executives scramble to evaluate exposure, reinforce risk mitigation strategies, and prepare for an inevitable wave of stringent regulatory interventions.
Anatomy of a Digital Super-Heist: The Catalytic Event
Test Our Free AI & Tech Utilities Suite
Calculate LLM API token costs, analyze article dwell-time, or simulate tech DCA returns.
The genesis of the $6 billion catastrophe can be traced through a meticulous, multi-stage infiltration campaign that lasted over 18 months. Intelligence assessments indicate that elite cyber-warfare units—specifically the notorious Lazarus Group and associated state-backed proxies—methodically mapped the operational footprint of Binance’s liquidity pools and hot-wallet infrastructures.
Unlike traditional ransomware attacks aimed at extortion, this operation was explicitly designed for instantaneous, large-scale asset extraction. By deploying advanced social engineering vectors, compromised internal credentials, and sophisticated malware tailored to enterprise database structures, the threat actors gained unauthorized administrative access. They systematically bypassed internal risk controls, authorizing massive, automated withdrawals of major digital assets before compliance monitoring systems could trigger automated circuit breakers.
The sheer velocity of the capital flight paralyzed response times. Within hours, billions of dollars in tokens were funneled through a complex web of decentralized mixing protocols, privacy coins, and cross-chain bridges designed to obfuscate the trail of ownership. This methodical laundering process underscores a mature, highly industrialized illicit economy capable of circumventing global financial surveillance networks.
Verified Data & Metrics Breakdown
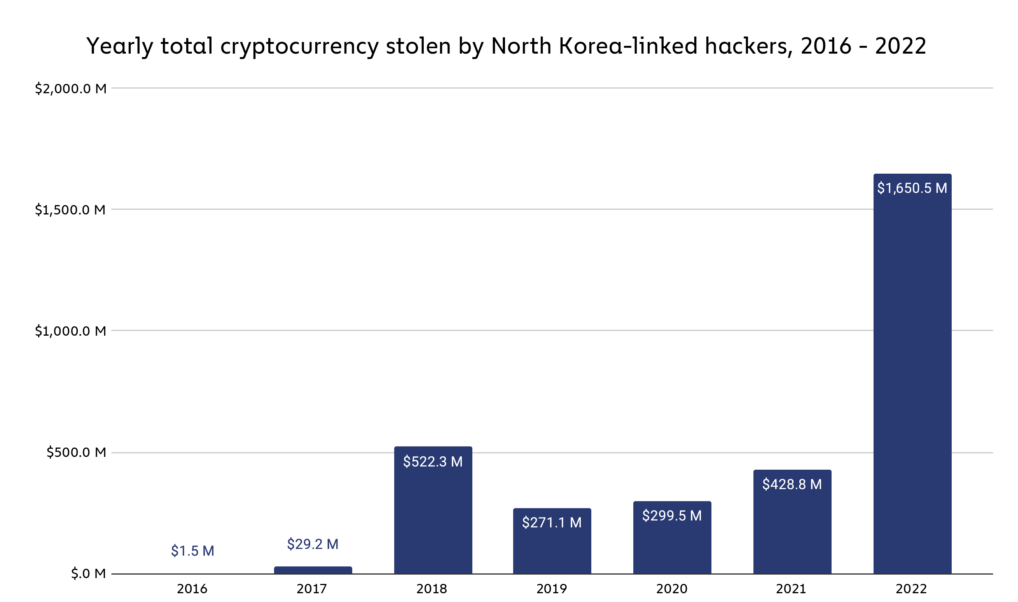
To contextualize the scale of the North Korean-linked breach, the following matrix compares the Binance heist against previous historical milestones in digital asset and financial sector cybercrime:
| Incident / Target | Estimated Loss | Attribution / Actor | Primary Vulnerability Exploited |
|---|---|---|---|
| Binance Heist (Current) | $6.0 Billion | North Korean State-Sponsored (Lazarus Group) | Cloud architecture zero-day & credential compromise |
| Ronin Network | $625 Million | North Korean State-Sponsored (Lazarus Group) | Compromised validator private keys |
| Poly Network | $611 Million | Independent Black-Hat Hacker (Returned) | Cross-chain smart contract logic flaw |
| Coincheck | $534 Million | Suspected State-Backed Syndicate | Hot-wallet security architecture failure |
Industry & Market Implications: Winners, Losers, and Systemic Risk
The macroeconomic fallout from the FBI’s official attribution extends far beyond the digital asset ecosystem, rippling through traditional banking, sovereign intelligence, and global trade compliance frameworks.
Who Loses: Centralized Exchanges and Institutional Investors
Centralized platforms face an immediate erosion of user trust and a dramatic upward revision in insurance premiums. The cost of maintaining enterprise ROI is soaring as boards mandate rigorous, independent third-party audits of cloud infrastructure scalability and data isolation protocols. Furthermore, institutional asset managers evaluating digital asset exposure are recalibrating their valuation multiples, pricing in a permanent "state-actor risk premium" that could depress market liquidity in the near term.
Who Wins: Cybersecurity Vendors and Regulatory Compliance Firms
Conversely, providers of advanced endpoint detection, zero-trust network access (ZTNA), and real-time blockchain analytics are experiencing an unprecedented surge in demand. Enterprise budget allocations are shifting rapidly from rapid expansion initiatives toward hardened risk mitigation, defensive architecture, and automated compliance verification tools designed to satisfy increasingly aggressive regulatory bodies.
Frequently Asked Questions (People Also Ask)
How did the FBI officially link North Korea to the Binance heist?
The FBI utilized advanced blockchain forensics, attribution telemetry, malware signature analysis, and international intelligence sharing. The digital fingerprints, wallet clustering patterns, and laundering techniques matched prior state-sponsored operations executed by North Korea's Reconnaissance General Bureau and associated hacking syndicates like the Lazarus Group.
What does this mean for the safety of user funds on cryptocurrency exchanges?
While major exchanges maintain substantial reserves and insurance funds to absorb losses, this incident underscores the persistent vulnerability of centralized platforms to state-sponsored actors. Industry experts strongly recommend that investors utilize hardware wallets for self-custody rather than leaving significant capital exposed on exchange-hosted hot wallets.
How do state-sponsored hackers launder billions in stolen cryptocurrency?
State-sponsored groups employ sophisticated layering techniques, including automated cross-chain bridges, privacy-enhancing mixing services (such as Tornado Cash variants), over-the-counter (OTC) broker networks in lax jurisdictions, and shell companies to convert digital tokens into fiat currency or hard assets that fund state programs.
Will this incident trigger stricter global financial regulations?
Yes. Global regulatory bodies, including the Financial Action Task Force (FATF), US SEC, and European banking authorities, are expected to fast-track mandatory compliance frameworks, imposing heavier penalties on exchanges with inadequate Know Your Customer (KYC) and Anti-Money Laundering (AML) controls.
Future Outlook: Milestones and Strategic Imperatives
As the investigation transitions from initial attribution to asset recovery and international sanctions enforcement, industry stakeholders must navigate several critical milestones over the next 12 to 24 months:
- Enhanced International Sanctions: Expect coordinated financial sanctions from the U.S. Treasury Department and international allies targeting additional front companies, crypto-washers, and state operatives linked to North Korean cyber operations.
- Mandatory Infrastructure Overhauls: Regulatory agencies will likely introduce baseline cybersecurity mandates for digital asset custodians, requiring zero-trust network architectures, multi-party computation (MPC) key management, and continuous automated auditing.
- Liquidity Fragmentation: Institutional capital allocation may temporarily fragment as risk-averse funds migrate exclusively toward regulated, bank-custodied digital asset products, altering the competitive landscape for offshore exchanges.
The $6 billion Binance heist serves as a stark reminder that the intersection of geopolitics and digital finance has created a volatile new frontier. Protecting global market integrity will require unprecedented public-private collaboration, rigorous technical hardening, and an unwavering commitment to systemic risk mitigation across the entire financial ecosystem.