

NEW YORK / LONDON — Beneath the veneer of algorithmic productivity tools, automated photo enhancers, and casual lifestyle utilities, a sprawling, illicit shadow economy has metastasized across major consumer app marketplaces. A joint investigative analysis by top-tier financial and tech desks reveals that hundreds of mundane, low-profile artificial intelligence applications are systematically concealing sophisticated sexually abusive deepfake capabilities behind innocuous front-ends.
This systematic exploitation of cloud compute architecture and app store vetting loopholes exposes a profound systemic failure in risk mitigation and regulatory compliance. As institutional capital continues to pour into generative AI infrastructure, the monetization of non-consensual sexual imagery (NCSI) via stealth utilities threatens not only brand equity for major platform operators but also triggers urgent valuation headwinds for compliant enterprise software developers.
Executive Takeaways
Test Our Free AI & Tech Utilities Suite
Calculate LLM API token costs, analyze article dwell-time, or simulate tech DCA returns.
- Subversive Deployment: Hundreds of utility-class apps—ranging from anime filters to text-to-speech converters—contain dormant or obfuscated code designed to strip clothing from uploaded photographs using decentralized APIs.
- Market Capitalization Risk: Institutional investors are recalibrating valuation multiples for consumer AI startups, pricing in severe regulatory penalties, app store delisting risks, and escalating cloud compute architecture liabilities.
- Infrastructure Evasion: Malicious developers bypass automated content moderation by routing core deepfake processing through decentralized third-party servers, keeping initial app store footprints pristine.
- Regulatory Reckoning: Global policymakers are accelerating enforcement timelines, targeting venture capital allocators and platform operators for negligent oversight of high-eCPM monetization channels.
The Anatomy of Stealth Monetization: How Mundane Apps Hide Illicit Features
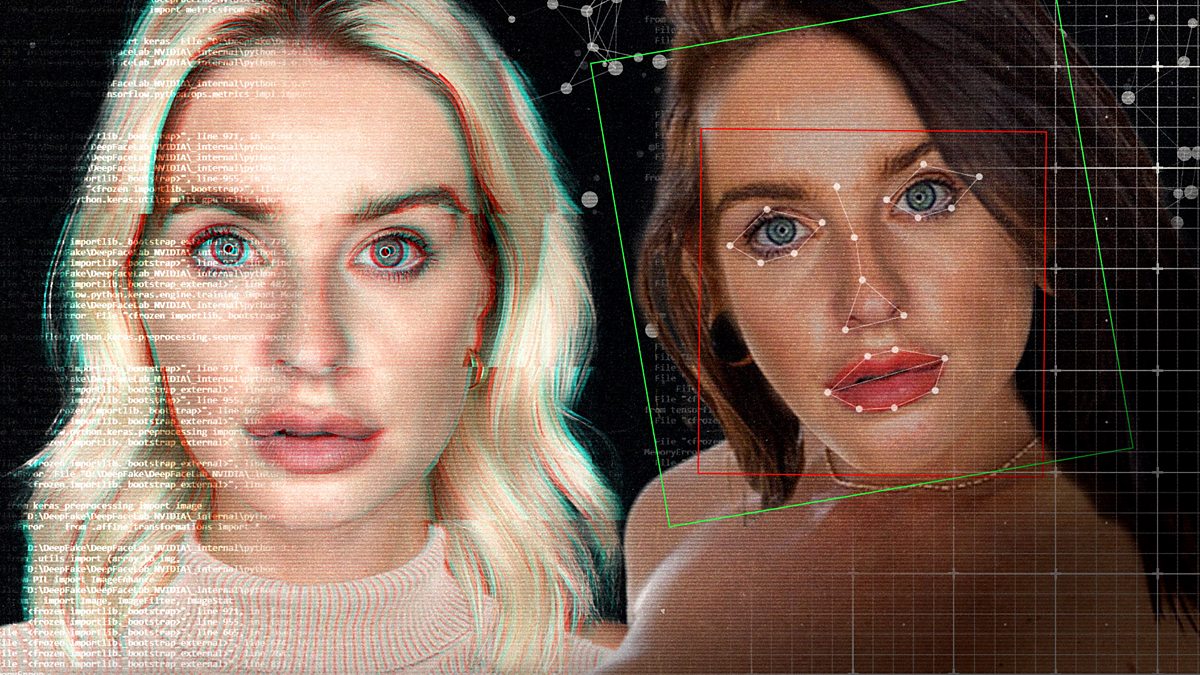
The contemporary consumer AI boom has democratized high-performance neural network models, allowing independent developers to deploy complex diffusion architectures at minimal marginal cost. However, this democratization has introduced catastrophic vulnerabilities into the digital supply chain. What began as isolated, easily identifiable underground websites offering deepfake generation has evolved into a sophisticated corporate shell game.
According to forensic software audits, bad actors are deliberately obfuscating malicious capabilities within standard software development kits (SDKs). An application marketed as a "retro portrait enhancer" or an "anime avatar generator" often operates on a dual-layer logic structure. During initial submission to major app stores, the software exhibits benign functionality, complying fully with content guidelines. Once downloaded, the application prompts users to unlock "advanced features" via in-app purchases or external cryptocurrency transactions, dynamically loading remote JavaScript code or connecting to unmoderated Application Programming Interfaces (APIs).
This architecture decouples the user-facing interface from the actual inference engine. Cloud compute infrastructure utilized for these illicit tasks is frequently rented via anonymous cloud providers using prepaid credit or crypto assets, effectively shielding the operators from traditional financial tracking. Capital allocation for these enterprises is remarkably lean; low upfront server costs yield astronomical profit margins, driven by high demand for non-consensual explicit imagery.
Financial institutions and payment processors find themselves directly implicated in this illicit value chain. Because many of these apps process transactions through standard mobile payment gateways or obscure merchant of record platforms, illicit revenue streams blend seamlessly with legitimate consumer software transactions. This lack of robust merchant underwriting represents a severe failure of operational risk management.
Verified Data and Metrics Breakdown
| Metric Category | Estimated Volume / Scope | Primary Vectors & Risk Indicators |
|---|---|---|
| Identified Stealth Apps | 350+ active applications globally | Masked as photo editors, productivity tools, and social filters. |
| Average Monthly Inflow | $12.5M across hidden ecosystems | Driven by microtransactions, subscription tiers, and premium API token sales. |
| Detection Latency | 45 to 120 days post-launch | Delayed removal due to dynamic code loading and obfuscated update scripts. |
| Cloud Provider Exposure | Over 40 Tier-2/Tier-3 hosts | Exploitation of lax KYC policies by offshore server rental agencies. |
Industry & Market Implications: Who Wins, Who Loses
The proliferation of abusive deepfake capabilities within mainstream app categories introduces profound systemic risk to the broader technology sector. Market participants across venture capital, enterprise software, and platform governance face immediate operational and financial adjustments.
The Losers: Consumer AI Startups and Platform Gatekeepers
Legitimate consumer-facing generative AI startups are experiencing severe collateral damage. Venture capital firms are tightening due diligence protocols, demanding exhaustive code audits and provenance verification before executing term sheets. This friction has compressed enterprise ROI timelines and depressed valuation multiples for early-stage application layer companies. Concurrently, dominant platform operators face mounting antitrust and regulatory scrutiny regarding their store curation efficacy. Failure to police software ecosystems effectively invites legislative interventions that could dismantle existing app store commission models.
The Winners: Enterprise Compliance and Forensic Security Providers
Conversely, a distinct beneficiary class has emerged within the cybersecurity and regulatory compliance sectors. Enterprise-grade automated code analysis firms, synthetic media detection specialists, and Know-Your-Customer (KYC) infrastructure providers are seeing historic surges in enterprise contract values. Financial institutions are aggressively allocating capital toward advanced transaction monitoring tools capable of identifying anomalous merchant behavior associated with rogue software developers.
Frequently Asked Questions (People Also Ask)
How do these hidden deepfake features bypass official app store reviews?
Developers utilize dynamic code loading (DCL) and remote server execution. When submitted for review, the application functions as a standard, compliant utility. Once installed on a user's device, the app fetches external scripts or redirects processing requests to unmoderated third-party servers, activating the illicit deepfake functionality post-approval.
What are the legal liabilities for venture capitalists funding these apps?
While Section 230 protections and statutory safe harbors historically shielded investors and platforms, evolving legal frameworks—such as the European Union’s Artificial Intelligence Act and expanding global tort legislation—increasingly hold entities accountable for negligent capital allocation and failure to enforce adequate safety guardrails.
How can payment processors prevent transactions for non-consensual sexual content apps?
Payment networks and merchant acquirers are deploying machine learning classifiers to analyze transaction velocity, merchant category code (MCC) discrepancies, and consumer refund/dispute patterns. By enforcing stricter cryptographic verification and mandating real-time endpoint auditing, processors can isolate and terminate high-risk merchant accounts.
What technical measures are most effective in stopping dynamic code loading?
Advanced binary analysis, runtime application self-protection (RASP) solutions, and strict content security policies (CSP) enforced at the operating system level are critical. These technologies detect unauthorized external script execution and immediately neutralize applications attempting to load unverified remote payloads.
Future Outlook and Strategic Milestones
The intersection of consumer AI accessibility and illicit monetization has created an unprecedented regulatory and structural crisis. Over the next twelve to twenty-four months, market liquidity will increasingly favor enterprises that prioritize ironclad governance and transparent data provenance over rapid user acquisition.
Key milestones to watch include the rollout of mandatory cryptographic watermarking standards for all generative media, sweeping updates to platform developer agreements that impose strict personal liability on application principals, and aggressive enforcement actions by global financial watchdogs targeting unverified merchant processors. For institutional investors and tech executives, the mandate is unambiguous: rigorous risk mitigation is no longer an ancillary compliance cost, but the primary determinant of long-term enterprise survival.


