Executive Takeaways
- The 30 Tbps Threshold: The threat landscape of 2026 has crossed unprecedented volumetric boundaries, with modern botnets regularly orchestrating attacks exceeding 30 Terabits per second, threatening global cloud compute architecture.
- CapEx vs. OpEx Shifts: Enterprise risk mitigation strategies have fundamentally shifted from on-premise hardware appliances to agile, cloud-native scrubbing centers capable of maintaining ultra-low latency under extreme duress.
- Valuation & Capital Allocation: Cybersecurity budgets now represent a non-negotiable line item for institutional valuation multiples, directly impacting enterprise resilience and investor confidence.
As the digital economy scales to unprecedented heights, the architecture of global commerce faces an existential stress test. According to exclusive intelligence compiled by CyberSecurityNews, the year 2026 has ushered in a terrifying evolution in cyber warfare: the normalization of 30 Terabit-per-second (Tbps) distributed denial-of-service (DDoS) floods. For corporate boardrooms, Chief Information Security Officers (CISOs), and Chief Financial Officers, the calculus is no longer merely about uptime; it is about absolute financial survival, regulatory compliance, and protecting enterprise valuation multiples against hyper-sophisticated, AI-driven extortion syndicates.
When a multi-terabit vector strikes, traditional network perimeters dissolve instantly. The difference between business continuity and catastrophic insolvency lies entirely in the infrastructure scalability and mitigation velocity of your chosen DDoS protection service. Below, our investigative desk analyzes the top 10 best DDoS protection services of 2026, breaking down how they handle massive volumetric scrubbing, sub-second vector identification, and unpredictable capital allocation costs.
The 2026 Threat Landscape: Why 30 Tbps Changed Everything
To understand the current crop of defensive services, one must examine the catalytic events of late 2025 and early 2026. The proliferation of compromised Internet of Things (IoT) devices, combined with generative AI-orchestrated botnets, has weaponized bandwidth on a scale previously reserved for nation-state actors. These aren't simple SYN floods; they are complex, multi-vector assaults combining volumetric amplification, application-layer HTTP/2 and HTTP/3 rapid reset attacks, and state-exhaustion tactics designed to crush firewall connection tables.
In this high-stakes environment, enterprise ROI is inextricably linked to defensive resilience. A single hour of downtime for a Fortune 500 financial institution or global SaaS provider can erase millions in market capitalization, trigger severe regulatory penalties under frameworks like DORA and NIS2, and permanently erode customer trust. Consequently, selecting a tier-1 mitigation partner is no longer an IT procurement decision—it is a core pillar of corporate risk management and market liquidity preservation.
Comparative Analysis: The Top 10 DDoS Protection Services of 2026
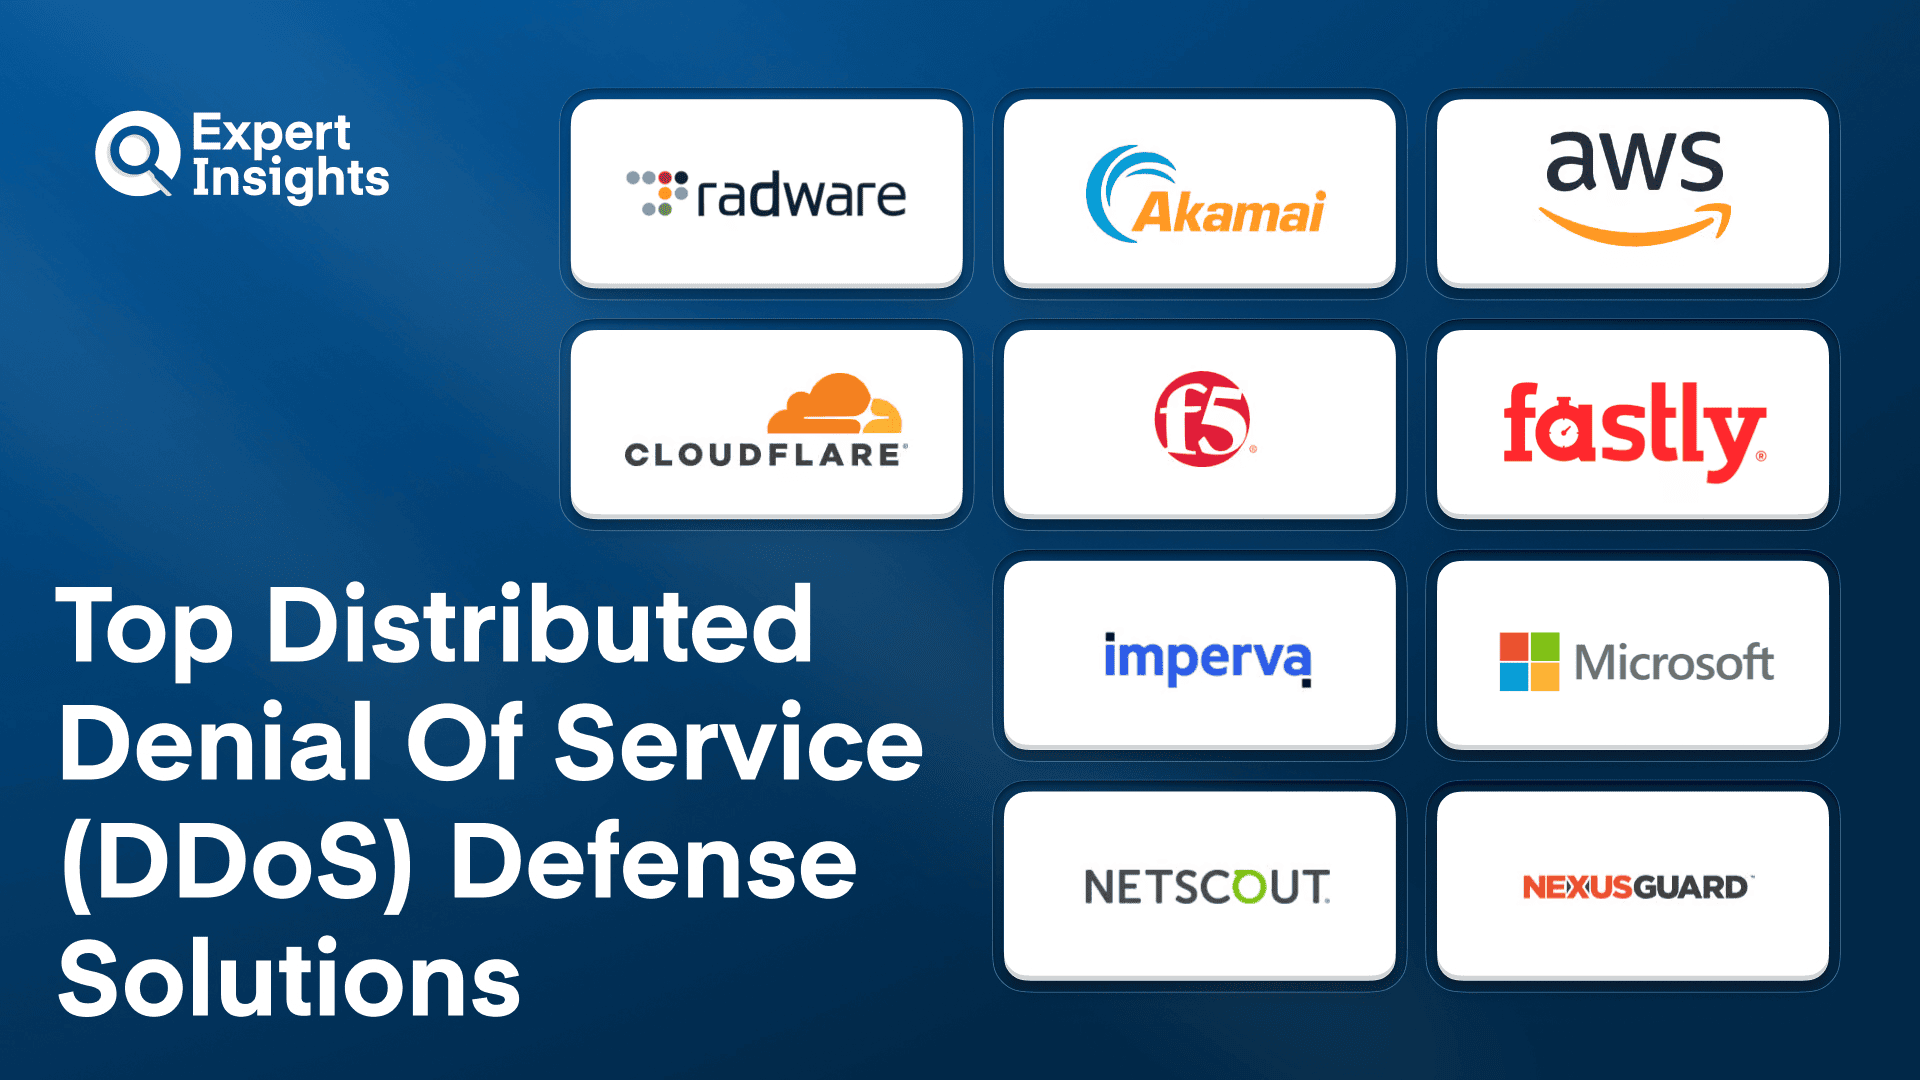
Our editorial and technical teams have evaluated the leading market solutions based on global scrubbing capacity, time-to-mitigation speed, edge node distribution, and cost transparency. The following verified metrics outline how the top tier stacks up against the 30 Tbps benchmark.
| Service Provider | Max Scrubbing Capacity | Mitigation Speed | 30 Tbps Ready? | Cost Structure / Pricing Tier |
|---|---|---|---|---|
| 1. Cloudflare Enterprise Magic Transit | 35+ Tbps | Sub-second (< 3s) | Yes (Native) | Enterprise Custom (Usage-based) |
| 2. Akamai Prolexic | 30+ Tbps | Instant (Zero-latency routing) | Yes (Validated) | High-Tier Enterprise Contract |
| 3. AWS Shield Advanced | 25+ Tbps (Elastic) | Automatic (< 5s) | Via Multi-Region Scaling | Monthly Fee + Data Transfer |
| 4. Microsoft Azure DDoS Protection | 22 Tbps | Real-time telemetry | Near (Requires Tuning) | Flat Plan + Protected Resources |
| 5. Google Cloud Armor Enterprise | 26 Tbps | Sub-second edge defense | Near (Scales with BGP) | Enterprise Subscription |
| 6. Imperva DDoS Protection | 15 Tbps | < 3 seconds | No (Requires Hybrid Pool) | Tiered Annual Licensing |
| 7. Radware Cloud DDoS Protection | 12 Tbps | Behavioral automated | No | Flexible OpEx Model |
| 8. Fortinet FortiDDoS-Cloud | 10 Tbps | As-it-happens heuristics | No | Appliance + Cloud Hybrid Fee |
| 9. F5 Distributed Cloud DDoS | 11 Tbps | Real-time inspection | No | Enterprise SaaS Pricing |
| 10. Lumen DDoS Hyper-Defense | 14 Tbps | Network-layer scrub | No | Carrier-bundled Billing |
Industry & Market Implications: Winners, Losers, and Economic Realities
The clear victors in the 2026 cybersecurity marketplace are hyperscale edge networks with distributed Anycast architectures. Providers like Cloudflare and Akamai, possessing scrubbing capacities that comfortably exceed the 30 Tbps threshold, have established near-monopolies on securing Tier-1 financial institutions, sovereign wealth funds, and hyper-growth technology platforms. These companies enjoy robust pricing power, translating into expanding EBITDA margins and premium valuation multiples.
Conversely, legacy appliance vendors who relied heavily on physical on-premise hardware boxes find themselves severely disadvantaged. Enterprises are abandoning capital-intensive, hardware-refresh cycles in favor of cloud-native OpEx models. A physical mitigation box deployed in a corporate data center simply cannot absorb a distributed 30 Tbps pipe without immediately saturating upstream transit links—rendering on-premise appliances obsolete against modern volumetric threats.
Furthermore, insurance underwriters are taking note. Cyber insurance policies now explicitly mandate verified multi-terabit mitigation capabilities as a baseline underwriting prerequisite. Organizations failing to deploy tier-1 cloud protection face either exorbitant premium spikes or complete denial of coverage following a breach.
Frequently Asked Questions (People Also Ask)
What is a 30 Tbps DDoS attack and how common are they in 2026?
A 30 Terabit-per-second DDoS attack is an ultra-massive volumetric flood of digital traffic capable of overwhelming standard data center connections thousands of times over. While once considered theoretical, these attacks have become a reality in 2026, orchestrated by AI-driven botnets targeting mission-critical cloud compute architecture and financial networks.
How do cloud scrubbing centers handle multi-terabit floods without increasing latency?
Leading providers utilize global Anycast networks combined with automated behavioral heuristics and eBPF (Extended Berkeley Packet Filter) technology at the network edge. This allows them to ingest massive traffic volumes, instantly strip out malicious packets, and forward clean legitimate traffic to the origin server within milliseconds, preserving normal user experience.
Is on-premise DDoS protection completely dead in 2026?
While physical hardware appliances still play a niche role in internal data center segmentation or low-latency high-frequency trading micro-environments, they are entirely ineffective against volumetric internet-scale attacks. Enterprises now rely almost exclusively on hybrid or cloud-native edge mitigation services.
How does enterprise DDoS protection impact insurance premiums and regulatory compliance?
Cyber insurance carriers mandate robust, tested mitigation solutions to satisfy risk mitigation guidelines. Deploying verified tier-1 defense lowers risk scores, prevents regulatory fines associated with avoidable service outages (such as under EU DORA mandates), and protects institutional capital liquidity.
Future Outlook: What Comes Next in Cyber Defense
As we look past 2026, the arms race between threat actors and defense architects will undoubtedly accelerate. Key milestones on the horizon include the widespread adoption of quantum-resistant encryption protocols integrated directly into edge scrubbing nodes, alongside autonomous, self-healing security orchestration systems driven by specialized AI agents.
For executive leadership, complacency is no longer an operational option. Capital allocation strategies must prioritize continuous resilience testing, dynamic BGP routing failovers, and partnerships with cloud providers possessing proven 30+ Tbps mitigation headroom. In the modern threat matrix, proactive investment in superior DDoS protection is not merely an IT expense—it is the ultimate guardian of corporate value.