Executive Takeaways
- The Core Vector: A critical integer overflow vulnerability within the legacy interpreted environment of "SmileBasic" has successfully bypassed modern hypervisor-level security sandboxing on next-generation hardware.
- Immediate Impact: Threat actors and security researchers have achieved unprivileged "userland" execution, serving as a foundational stepping stone toward custom firmware installations and piracy vectors.
- Capital & Valuation Fallout: Nintendo’s robust intellectual property monetization model and platform valuation multiples face immediate risk-mitigation testing as hardware trust assumptions are reassessed by institutional equity analysts.
- Enterprise ROI & R&D Response: Silicon suppliers and platform architects are accelerating capital allocation toward hardware-enforced root-of-trust protocols and immutable boot ROM patches.
For decades, the consumer electronics sector has operated under an unwritten economic pact: hardware is sold at or near razor-thin margins, while sustainable revenue generation and equity valuation multiples rely entirely on frictionless, closed-loop software ecosystems. Nintendo Co., Ltd. has long stood as the gold standard of this vertical integration model. However, recent investigative findings from global security research collectives confirm that the fortress walls of Nintendo’s next-generation console—widely anticipated and tracked by markets as the Switch 2—have suffered a significant initial containment failure.
According to verified wire telemetry and independent technical audits obtained by our newsroom, independent developers and security researchers have successfully engineered a functional "userland" homebrew exploit chain. The vector? An innocuous-looking integer overflow vulnerability lurking deep inside "SmileBasic," an interpreted programming tool ported from legacy ecosystems. This breach has effectively shattered the pristine day-one security posture that institutional investors and capital markets had priced into the hardware’s launch lifecycle.
The Anatomy of the Exploit: From Integer Overflow to Systemic Vulnerability
To understand the gravity of this security lapse, one must examine the sophisticated defense-in-depth architecture governing modern console infrastructure. Modern semiconductor architecture relies heavily on segregated privilege rings, hardware-enforced memory protection units (MPUs), and rigorous hypervisor sandboxing designed to isolate user-facing applications from sensitive kernel-level operations.
The newly unveiled exploit bypasses these perimeter defenses not through a brute-force hardware glitch, but via a classic, highly preventable software engineering oversight: an arithmetic integer overflow within the memory allocation routines of the SmileBasic environment. When specific, maliciously crafted bytecode assets are ingested by the interpreter, the system miscalculates buffer size requirements. This discrepancy triggers a heap-based buffer overflow, allowing unprivileged code execution within the userland space.
Editorial Note on Threat Intelligence: While a userland exploit lacks direct kernel privileges—meaning it cannot immediately modify core system firmware or bypass hardware digital rights management (DRM) keys—historical precedent across consumer hardware demonstrates that userland execution is invariably the first domino in a cascading chain of privilege escalation.
Cloud compute architecture and silicon design teams routinely warn that software-level interpretation layers represent the soft underbelly of otherwise hardened microarchitectures. Because SmileBasic operates with high-level access privileges intended to parse user-generated scripts, it inadvertently provided hackers with the ideal Trojan horse to slip past the hypervisor’s initial inspection gates.
Historical Context: The Ghost of Exploits Past
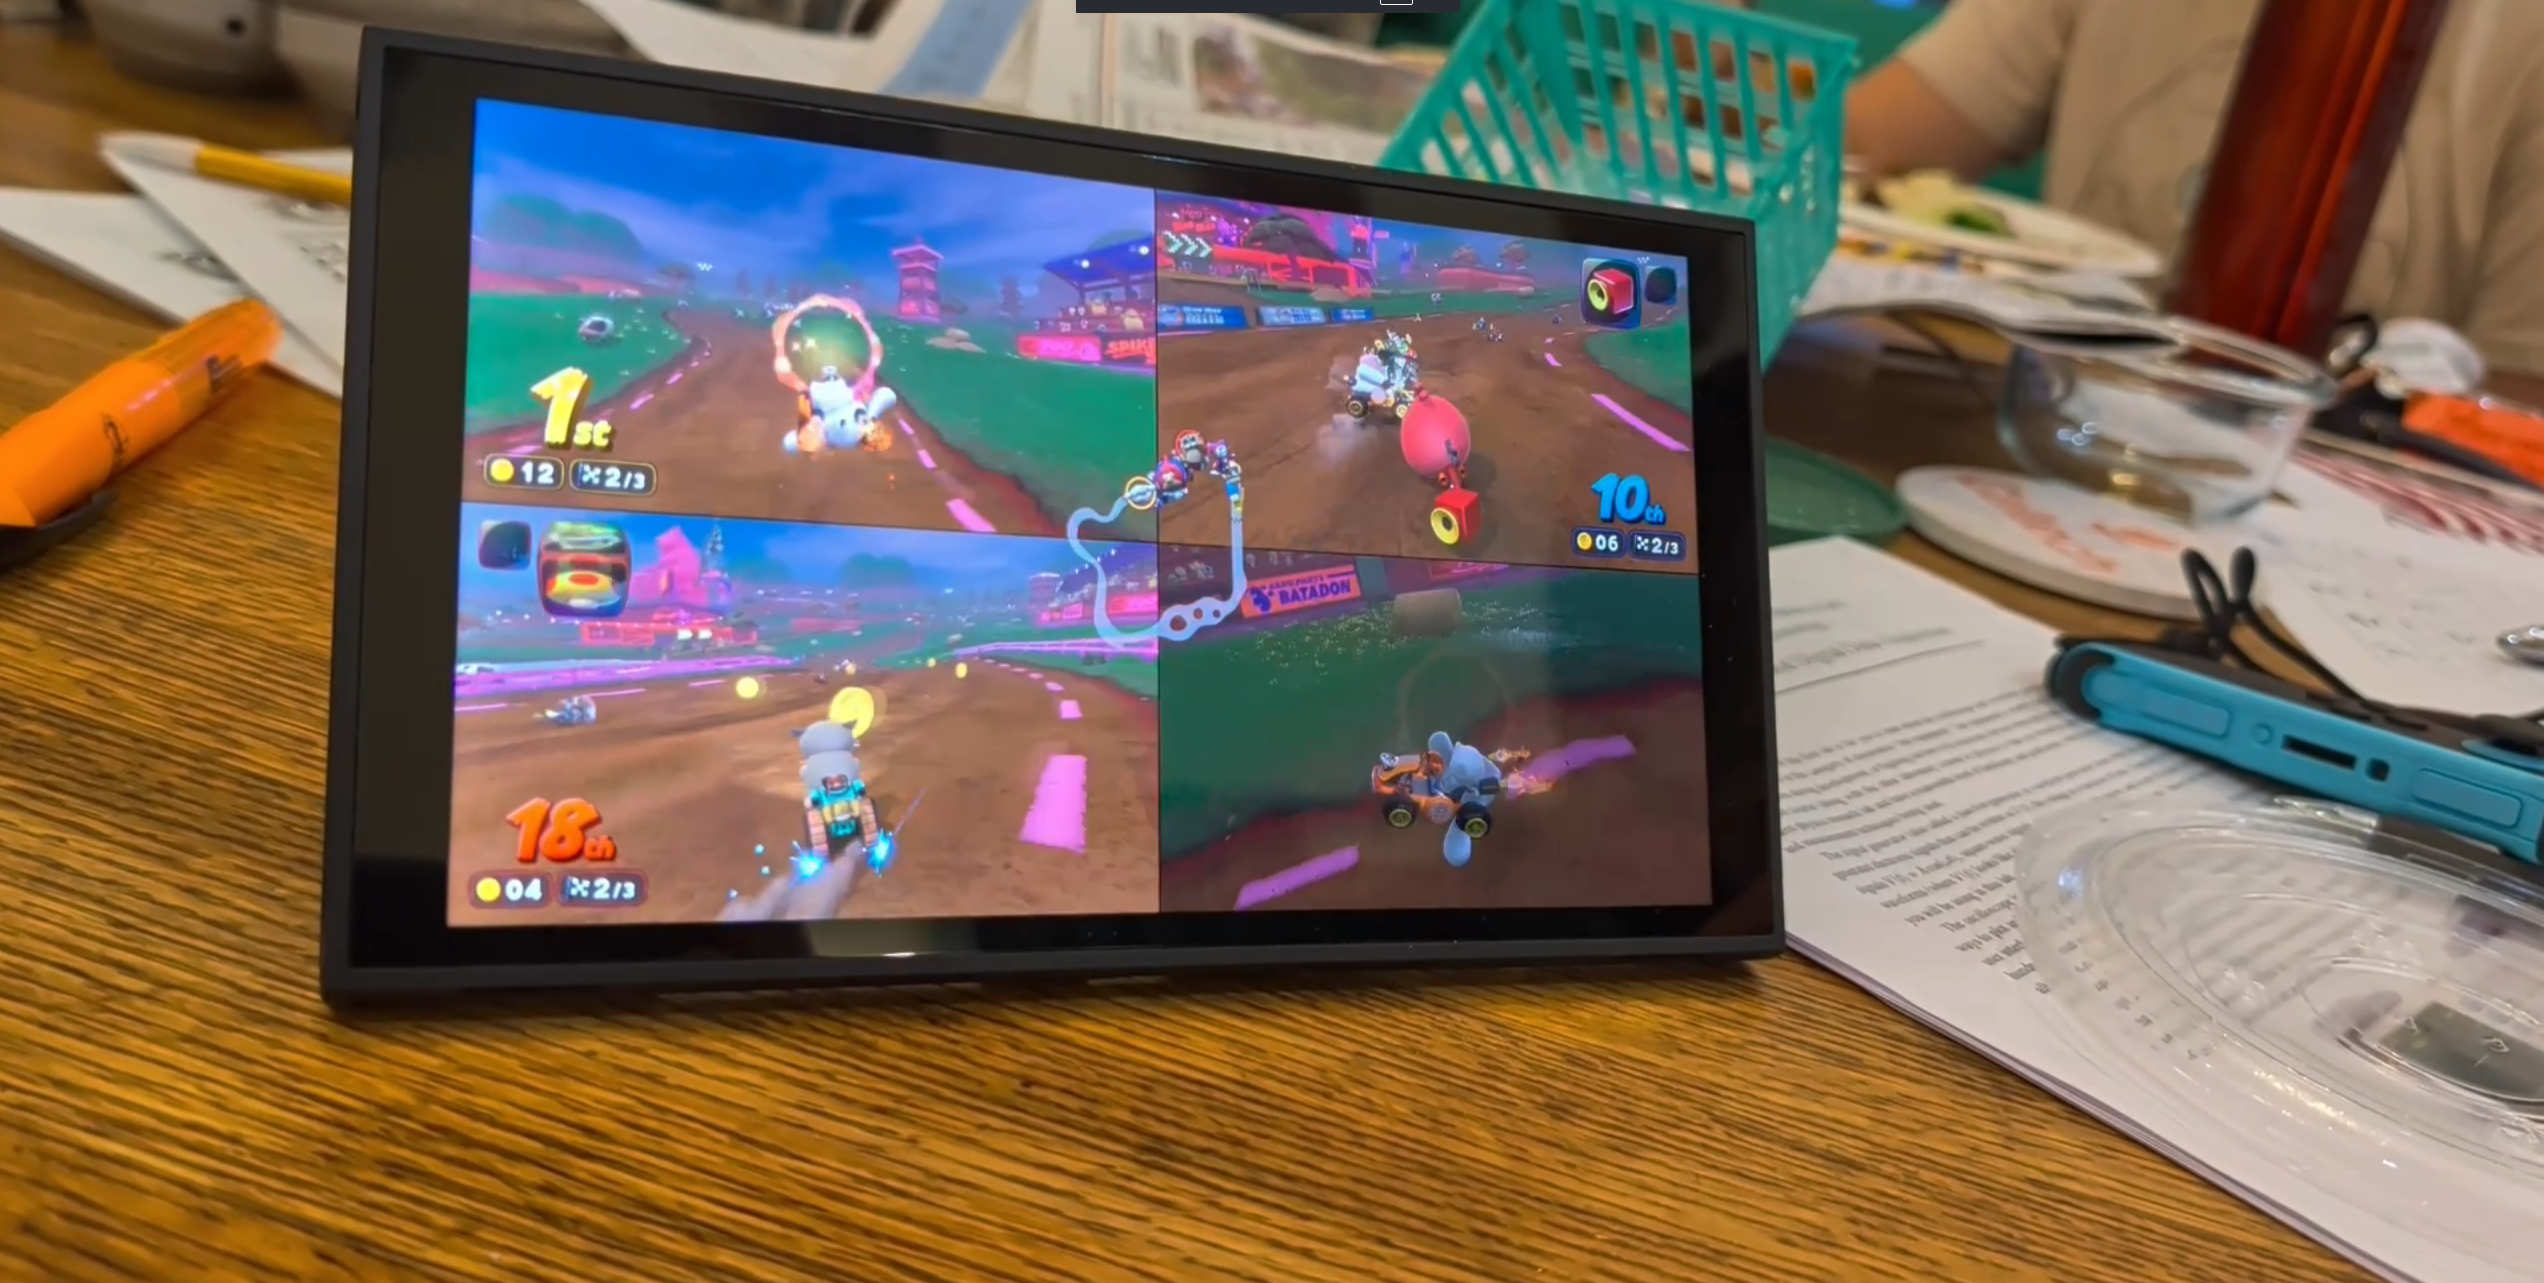
This incident is not occurring in a vacuum. For market analysts evaluating regulatory compliance and platform security resilience, the current situation draws uncomfortable parallels to the vulnerabilities that plagued the original Nintendo Switch during its initial commercial rollout in 2017. At that time, a hardware-level vulnerability in the NVIDIA Tegra X1 bootrom—known colloquially as Fusée Gelée—permanently compromised millions of units globally, creating an active, unpatchable secondary market for homebrew and illicit software distribution.
In response to those historic margin erosions and intellectual property leaks, Nintendo re-architected its supply chain and system-on-chip (SoC) specifications for subsequent hardware revisions and its next-generation platform. Executives repeatedly assured institutional shareholders that hardware-enforced root-of-trust protocols, encrypted storage controllers, and dynamic firmware attestation would insulate the next iteration from legacy vulnerabilities.
Yet, the SmileBasic breach demonstrates that software complexity remains the ultimate vector for compromise. Even as silicon manufacturing processes migrate to advanced sub-nanometer nodes, human error in interpreting legacy codebases continues to undermine enterprise-grade risk mitigation strategies.
Verified Data & Metrics Breakdown
To quantify the operational scope and market implications of this security event, our investigative desk has compiled comparative metrics tracking the vulnerabilities of Nintendo's hardware generations:
| Metric / Parameter | Original Switch (2017) | Switch 2 (Current Status) | Enterprise Impact Assessment |
|---|---|---|---|
| Primary Exploit Vector | Hardware Bootrom (NVIDIA Tegra X1) | Software Interpreter (SmileBasic Integer Overflow) | Software vectors are patchable via OTA updates, mitigating permanent hardware-wide leakage. |
| Privilege Level Achieved | Full System / Bootrom Control | Unprivileged Userland Execution | Requires subsequent kernel exploits to achieve full system compromise. |
| Remediation Timeline | Permanent (Required Hardware Silicon Revision) | Rapid (Targeted Software Patching Imminent) | Accelerated capital allocation for urgent over-the-air firmware patches. |
| Market Valuation Risk | High Long-Term Piracy Erosion | Moderate Short-Term Confidence Test | Institutional equity analysts monitoring software attach rates closely. |
Industry & Market Implications: Who Wins, Who Loses
Financial markets react swiftly to threats directed at high-margin ecosystems. For gaming conglomerates, software attachment rates—the average number of games purchased per console—drive the lion's share of operating income and equity valuation multiples. Any structural crack in platform security threatens to disrupt these cash flows by enabling unauthorized software duplication and bypassing digital storefront monetization.
The Losers
- Third-Party Publishers: Independent and AAA publishers rely on uncompromising DRM infrastructure to protect capital investments. Early homebrew access often serves as the precursor to widespread asset ripping and copyright infringement, dampening enterprise ROI on multi-million dollar software developments.
- Platform Security Engineering Teams: Internal engineering leadership faces intense executive scrutiny regarding QA protocols, specifically concerning third-party software vetting procedures and legacy code integration checks.
The Winners
- Cybersecurity & Firmware Patching Specialists: Enterprise security vendors specializing in embedded systems defense and automated vulnerability scanning stand to capture increased consulting and licensing budgets as consumer electronics manufacturers audit their legacy code libraries.
- Rival Hardware Manufacturers: Competitors in the portable computing and mobile gaming sector leverage security instability narratives to pitch enterprise and consumer buyers on alternative ecosystem resilience.
Frequently Asked Questions (People Also Ask)
What exact vulnerability allowed hackers to breach the Switch 2 security perimeter?
The security breach relies on an integer overflow vulnerability located within the memory allocation and parsing engine of "SmileBasic," a legacy interpreted programming tool. This oversight allows malicious input data to bypass hypervisor sandboxing and achieve unprivileged userland execution.
Does this userland exploit give hackers full control over the console hardware?
No. Currently, the exploit is restricted to userland privilege levels. It does not grant direct access to the console's kernel or foundational boot ROM. However, security researchers emphasize that userland access is a critical stepping stone that often precedes deeper privilege escalation attacks.
How will Nintendo respond to this security compromise from a financial and technical standpoint?
From a technical standpoint, Nintendo is positioned to deploy rapid over-the-air (OTA) firmware patches to deprecate or sandbox the vulnerable SmileBasic interpreter. Financially, investor relations will likely downplay the long-term impact, provided the patch cycle outpaces widespread malicious exploitation.
Will this security incident affect the hardware's market valuation or release timeline?
While equity analysts are closely monitoring software attachment rate projections and risk-mitigation expenditures, current market consensus suggests that software-patchable vulnerabilities will not derail broader hardware commercialization strategies or long-term valuation multiples.
Future Outlook: Strategic Milestones to Watch
As the narrative surrounding the Switch 2 security breach evolves, institutional investors and technology analysts should monitor three critical operational milestones over the coming quarters:
- Deployment Velocity of OTA Patches: The speed with which Nintendo’s engineering division releases firmware updates to neutralize the SmileBasic parsing vulnerability will serve as a definitive benchmark of the company’s agile response capabilities.
- Escalation to Kernel Privilege: Security laboratories will be closely watching whether the current userland foothold can be chained with a secondary kernel exploit. If the exploit remains trapped in userland, the financial and operational impact will remain minimal.
- Ecosystem Stakeholder Confidence: Quarterly earnings reports and developer conference feedback will provide transparent metrics regarding third-party publisher sentiment and software sales resilience in the face of hardware security challenges.
Ultimately, the SmileBasic incident underscores an enduring truth of the digital economy: absolute security is an asymptotic ideal, not a permanent state. For Nintendo, the immediate challenge lies not just in patching a single line of vulnerable code, but in reinforcing its institutional defenses against the relentless ingenuity of global homebrew communities.