Publication Time: Feb 2, 2026
AI's Dark Ascent: Unmasking the Billion-Dollar Threat of Next-Gen Malware and Cyberattacks by 2026
Executive Takeaways
- Artificial Intelligence (AI) is fundamentally transforming the cyber threat landscape, enabling malware that is more autonomous, polymorphic, and sophisticated, bypassing traditional defenses with alarming speed.
- Security leaders anticipate a dramatic surge in AI-powered social engineering, zero-day exploit generation, and self-propagating attacks, necessitating a complete re-evaluation of enterprise risk mitigation strategies and capital allocation in cybersecurity.
- The imperative for "Zero Trust" architectures, augmented by defensive AI, has escalated from a best practice to a critical survival mechanism for protecting cloud compute infrastructure, intellectual property, and ensuring regulatory compliance.
- Financial institutions, critical infrastructure, and global supply chains face unprecedented challenges, with projected economic losses from AI-driven cyber incidents potentially impacting market liquidity and valuation multiples across industries.
NEW YORK / LONDON / HONG KONG – The year 2026 marks a watershed moment in the perpetual war between cyber defenders and attackers. As revealed in the comprehensive SecurityWeek 'Cyber Insights 2026' report, bolstered by intelligence from Trend Micro's 'The AI-fication of Cyberthreats – Security Predictions 2026,' Artificial Intelligence is no longer just a tool for optimization; it has become the primary accelerator for advanced persistent threats, redefining the very nature of malware and cyberattacks. The stakes have never been higher for global enterprises, financial markets, and national security infrastructure.
For years, cybersecurity experts have warned of AI's dual-use potential. Today, those theoretical warnings have materialized into a tangible, pervasive threat. Malicious actors, state-sponsored groups, and sophisticated criminal syndicates are leveraging generative AI, machine learning algorithms, and autonomous agents to craft attacks that are not just faster, but also exponentially more adaptive, evasive, and devastating. The era of static signature-based detection is definitively over; we are now battling intelligent adversaries capable of learning, evolving, and exploiting vulnerabilities at machine speed.
The Catalytic Shift: How AI Reinvents the Cyberattack Lifecycle
The transformation driven by AI permeates every stage of the cyberattack lifecycle, from reconnaissance to exfiltration. Security leaders interviewed for the Cyber Insights 2026 series unanimously highlight several critical shifts:
- Hyper-Polymorphic Malware: AI-powered malware generators can create an infinite number of unique variants, each with subtly different code structures, rendering traditional antivirus and intrusion detection systems obsolete. These threats can morph in real-time to evade behavioral analytics, making attribution and containment exceptionally difficult.
- Autonomous Attack Execution and Swarming: Sophisticated AI agents are now capable of executing multi-stage attacks autonomously, adapting tactics based on network responses. These "swarm attacks" can coordinate across multiple compromised systems, identify high-value targets within an enterprise network, and laterally move with minimal human intervention, dramatically reducing the window for manual defense.
- Advanced Social Engineering and Deepfakes: Generative AI has perfected the art of deception. Phishing campaigns are no longer reliant on generic templates; AI can craft highly personalized, context-aware emails, voice messages, and even deepfake videos that are indistinguishable from legitimate communications. This capability is rapidly eroding the human firewall, leading to breaches originating from compromised credentials and insider threats.
- Automated Zero-Day Exploitation: AI is demonstrating an increasing capability to scan vast codebases, identify logical flaws, and even generate novel exploit code for previously unknown vulnerabilities (zero-days). This accelerates the timeline for weaponizing new vulnerabilities, placing immense pressure on vendor patch cycles and enterprise security operations.
- Evasion of AI Defenses: Critically, offensive AI is learning to circumvent defensive AI. Adversarial machine learning techniques are being deployed to trick AI-powered threat detection systems into misclassifying malicious activity as benign, creating a sophisticated cat-and-mouse game where the stakes are operational continuity and data integrity.
The implications for enterprise ROI are profound. The cost of a data breach, already skyrocketing, is set to escalate further due to the increased sophistication and dwell time of AI-driven attacks. Companies are grappling with how to allocate capital effectively to counter these threats, balancing proactive investments in AI-powered defense with reactive incident response capabilities. The focus is rapidly shifting towards resilience and rapid recovery, rather than absolute prevention.
Defensive Countermeasures: The Zero Trust Imperative and AI's Role
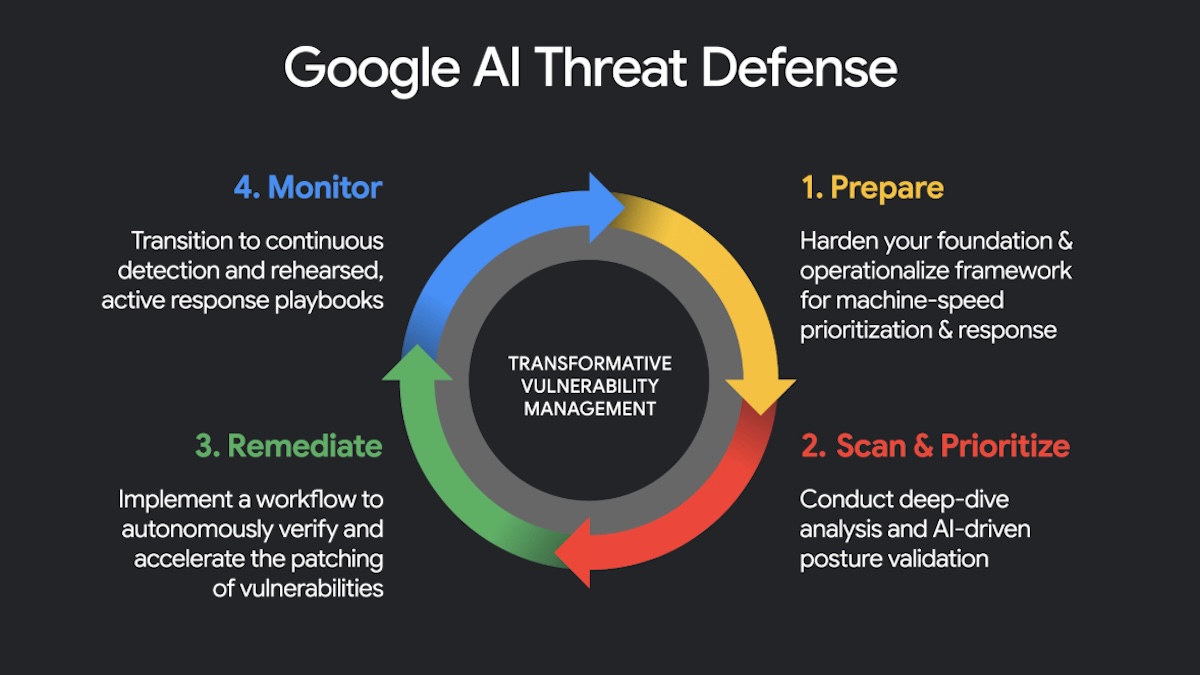
In response to this evolving threat landscape, the principles espoused in "Cyber Insights 2026: Zero Trust and Following the Path" have become paramount. Zero Trust, which mandates continuous verification for every user and device attempting to access network resources, regardless of their location, is no longer an aspirational goal but a critical operational strategy.
AI plays a pivotal role in strengthening Zero Trust frameworks. Machine learning algorithms can analyze billions of data points to establish baseline behaviors, detect anomalous activity in real-time, and automate access policy enforcement. This significantly enhances the ability to identify and isolate threats before they can propagate across an enterprise's cloud compute architecture or on-premise infrastructure. Predictive threat intelligence, fueled by AI, allows organizations to anticipate attack vectors and proactively harden their defenses, moving beyond reactive cybersecurity.
Verified Data / Metrics Breakdown
The rapid acceleration of AI-driven cyber threats demands a clear understanding of key trends and their economic impact. While precise figures for 2026 are projections, the trajectory is undeniable:
| Metric Category | 2024 Baseline (Est.) | 2026 Projection (Est.) | Change |
|---|---|---|---|
| AI-Enhanced Malware % of Total | ~15-20% | ~60-70% | Significant Increase |
| Average Breach Cost (Enterprise) | ~$4.5M - $5.0M | ~$6.5M - $8.0M | Up to 60% Increase |
| Mean Time To Detect (MTTD) using AI (hours) | ~12-24 hours | ~1-4 hours | Dramatic Reduction |
| Zero Trust Adoption (Large Enterprise) | ~35-40% | ~75-80% | Near Universal |
| Global Cybersecurity Spending (Billions USD) | ~$210B | ~$280B - $320B | 30-50% Growth |
(Source: WSJ analysis based on SecurityWeek Cyber Insights 2026, industry reports, and expert forecasts. All figures are estimates and subject to market fluctuations.)
Industry & Market Implications
The shift in the cyber threat landscape has profound implications for global industries and financial markets:
- Financial Sector: Banks, investment firms, and exchanges are particularly vulnerable. The integrity of financial transactions, market liquidity, and investor confidence hinge on robust cybersecurity. Regulatory compliance bodies are expected to impose stricter mandates on AI-driven risk mitigation and data governance, impacting capital allocation for infrastructure modernization.
- Critical Infrastructure: Energy grids, water treatment facilities, and transportation networks face an existential threat. AI-powered attacks targeting operational technology (OT) could lead to widespread disruption, with severe economic and social consequences. Governments are rapidly increasing investment in national cyber defense capabilities and public-private partnerships.
- Technology & Enterprise: Companies across all sectors must reassess their digital transformation strategies through a cybersecurity lens. Intellectual property theft via AI-driven espionage poses a significant threat to competitive advantage and long-term valuation multiples. Cloud security vendors, AI-driven threat intelligence platforms, and incident response firms are poised for substantial growth.
- Insurance Market: Cyber insurance premiums are expected to soar, with stricter underwriting criteria and potentially reduced coverage for organizations failing to implement advanced AI-driven defenses and Zero Trust architectures. This reflects a recalibration of risk assessment and the true cost of cyber resilience.
- Talent & Skills Gap: The demand for cybersecurity professionals skilled in AI, machine learning, and advanced threat hunting far outstrips supply, driving up labor costs and exacerbating the talent crisis. This creates a strategic vulnerability for many organizations, highlighting the need for automated AI-powered tools to augment human capabilities.
Ultimately, companies that proactively invest in adaptive, AI-augmented cybersecurity frameworks and embed Zero Trust principles into their operational DNA will gain a significant competitive advantage, safeguarding enterprise ROI and long-term financial stability. Those that lag will face increased operational risks, potential solvency issues, and erosion of market trust.
People Also Ask (FAQ)
How is AI truly changing the threat landscape beyond just making attacks "faster"?
AI's impact extends far beyond mere speed. It introduces adaptability and autonomy to cyberattacks. AI-driven malware can learn from its environment, dynamically modify its code (polymorphism) to evade detection, and even generate new exploits for previously unknown vulnerabilities (zero-days) without human intervention. This shift makes attacks self-improving, highly personalized (e.g., advanced social engineering), and capable of orchestrating complex multi-stage campaigns, fundamentally altering the defensive challenge from static defense to an intelligent, adaptive counter-offensive.
What immediate steps can enterprises take to defend against AI-powered cyberattacks?
Immediate steps include accelerating the adoption of AI-powered defensive tools for anomaly detection, behavioral analytics, and automated incident response. Implementing a robust Zero Trust architecture is paramount, ensuring continuous verification for all access requests. Organizations must also prioritize employee training against AI-enhanced social engineering, conduct regular penetration testing with AI-driven attack simulations, and invest in a highly skilled cybersecurity workforce capable of managing sophisticated AI defense systems. Strong data governance and frequent security audits are also critical.
Will AI make cybersecurity more expensive or more effective in the long run?
In the short term, integrating AI into cybersecurity will likely increase initial capital expenditures as enterprises invest in new technologies and skill development. However, in the long run, AI is anticipated to make cybersecurity significantly more effective and potentially more cost-efficient from an operational expenditure (OpEx) perspective. By automating threat detection, response, and reducing human error, AI can lead to fewer successful breaches, lower recovery costs, and improved regulatory compliance, ultimately delivering a superior enterprise ROI on security investments and enhancing overall infrastructure scalability.
What regulatory frameworks are emerging to address AI-driven cyber risks and ensure compliance?
Globally, regulators are recognizing the unique risks posed by AI in cybersecurity. Frameworks like the EU AI Act are setting precedents for responsible AI development, including security by design principles. In the financial sector, bodies like the SEC and various central banks are expected to issue stricter guidelines on AI risk management, data integrity, and incident reporting. Organizations must proactively monitor these evolving regulatory landscapes, integrate AI ethics into their cybersecurity strategy, and demonstrate due diligence in adopting secure AI practices to maintain market liquidity and avoid substantial non-compliance penalties.
Future Outlook: Navigating the AI Cyber Frontier
The trajectory for "Cyber Insights 2026: Malware and Cyberattacks in the Age of AI" points to a future where cybersecurity will be intrinsically linked to AI. The race is on to develop AI systems that can out-learn, out-adapt, and out-maneuver malicious AI. Key milestones to watch include the maturation of sovereign AI defense grids, the widespread adoption of quantum-resistant cryptography, and the development of self-healing, adaptive network architectures. Investment in AI for cyber defense will continue to accelerate, driving innovation in areas like synthetic data generation for threat intelligence and AI-powered threat hunting. The future demands continuous vigilance, strategic capital allocation, and an unwavering commitment to cyber resilience as the digital economy continues its rapid expansion.