Inside the Federal Takedown of Beijing’s Covert IoT Botnet: How the FBI Neutralized China’s Pre-Positioning Inside U.S. Critical Infrastructure
Executive Takeaways
- Federal Counter-Offensive: In a coordinated, court-authorized operation, the Federal Bureau of Investigation (FBI) and Department of Justice (DOJ) severed command-and-control access to a massive Chinese state-backed botnet compromising tens of thousands of consumer and enterprise Internet of Things (IoT) devices.
- Shift from Espionage to Sabotage: Intelligence agencies assess that the state-sponsored adversary was actively pre-positioning inside U.S. critical infrastructure—including power grids, municipal water treatment facilities, and defense maritime logistics—to execute destructive asymmetric strikes during a potential geopolitical crisis over Taiwan.
- Weaponization of Edge Hardware: The threat actors systematically targeted end-of-life (EoL) Small Office/Home Office (SOHO) routers, IP cameras, and network-attached storage (NAS) devices, repurposing unpatched firmware vulnerabilities into obfuscated routing infrastructure.
- Enterprise & Insurance Shocks: The disclosure triggers a seismic reassessment of enterprise cyber insurance underwriting, supply chain hardware governance, and capital allocation, as regulators eye mandatory hardware-level lifecycle accountability for enterprise vendors.
The Strike: Decapitating an Asymmetrical Digital Threat
In a coordinated national security maneuver that blurred the line between defensive cyber triage and active electronic counter-measures, federal law enforcement authorities, backed by international intelligence partners, executed an extraterritorial takedown of a pervasive, state-sponsored cyber-espionage apparatus tied directly to the People’s Republic of China (PRC). The operation, unsealed via federal court filings, marks an inflection point in Western law enforcement’s willingness to surgically intervene on private network architecture to defend national critical assets.
Operating under Title 18 judicial search and seizure authorizations, the FBI leveraged custom technical operations to issue remote operational commands to thousands of infected edge devices. The federal payloads decoupled infected SOHO routers and industrial edge gateways from the adversary's central command-and-control (C2) matrix, burned down their backdoors, and effectively blindfolded threat groups tracked across enterprise threat intelligence as Volt Typhoon, Flax Typhoon, and their operational contractor proxies.
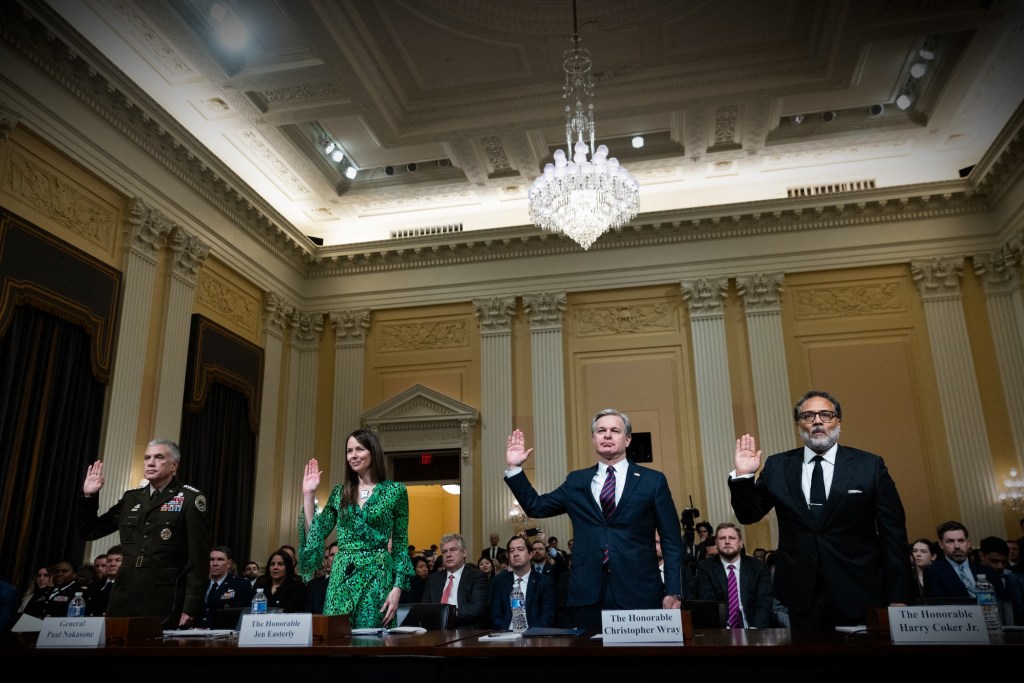
For months, senior intelligence officials, including FBI Director Christopher Wray and Cybersecurity and Infrastructure Security Agency (CISA) leadership, warned congressional committees that Beijing had abandoned its legacy playbook of intellectual property theft. The objective was no longer industrial espionage—the systematic exfiltration of commercial intellectual property that defined operations over the past two decades. Instead, the strategic directive had shifted toward deep digital sabotage: establishing entrenched footholds inside Western municipal infrastructure, industrial control systems (ICS), and maritime transport hubs to induce domestic panic and paralyze U.S. military logistics in the event of an Indo-Pacific kinetic theater activation.
Forensic Architecture: How Edge Infrastructure Was Weaponized
The forensic anatomy of the campaign reveals an ingenious exploitation of the global hardware blind spot: the distributed, unmanaged consumer and enterprise edge. Rather than deploying sophisticated zero-day exploits against heavily monitored cloud compute architectures or Fortune 500 endpoint detection and response (EDR) agents, the adversary systematically targeted the perimeter.
Exploiting legacy, unpatched vulnerabilities—predominantly known Common Vulnerabilities and Exposures (CVEs) in end-of-life hardware manufactured by vendors such as Cisco, Netgear, DrayTek, and D-Link—the hackers assembled a sprawling, multi-tiered proxy botnet. These compromised endpoints formed an anonymized intermediary mesh network. By routing their traffic through residential and small-business internet connections located within geographic proximity to their targets, the state-backed operatives masked their malicious activity within typical domestic traffic patterns.
Once inside a target’s internal environment—achieved via stolen administrative credentials, remote exploitation of edge perimeter devices, or supply-chain vectors—the hackers executed a doctrine known in tactical cybersecurity as "Living off the Land" (LotL). Rather than dropping custom-compiled malware binaries that trigger static heuristic alarms on modern enterprise threat-hunting platforms, the actors exclusively utilized native administrative utilities already baked into operating systems, such as Windows Management Instrumentation (WMI), PowerShell, and basic command-line utilities (e.g., netsh, vssadmin, and systeminfo).
This operational footprint rendered the intrusion nearly invisible. Security Operations Centers (SOCs) were unable to distinguish malicious activity from standard network administration routines. The intruders conducted silent reconnaissance, extracted sensitive pipeline schematics, mapped programmable logic controllers (PLCs), and staged persistent backdoors that bypassed Multi-Factor Authentication (MFA) via harvested enterprise session tokens.
Verified Metrics: Federal Disruption vs. Adversary Scale
The following verified metrics outline the scale of the adversary’s deployment, the infrastructural targets compromised, and the parameters of the federal disruption campaign.
| Metric / Vector | State-Sponsored Adversary Parameters | Federal Disruption Response |
|---|---|---|
| Primary Attribution | Volt Typhoon / Flax Typhoon (PRC Ministry of State Security contractors) | DOJ, FBI, CISA, NSA, Five Eyes Alliance (UK, CA, AU, NZ) |
| Vector of Compromise | Unpatched/EoL SOHO Routers, Firewalls, IP Cameras, NAS systems | Court-authorized remote execution of remediation scripts |
| Estimated Infected Endpoints | 200,000+ globally across multiple interconnected botnet networks | Surgically severed central C2 hubs; liberated thousands of domestic nodes |
| Targeted Sectors | Energy, Municipal Water Treatment, Ports, Aviation, Telecoms | Mandatory sector-wide CISA emergency directives and threat advisories |
| Primary Evasion Tactic | "Living-off-the-Land" (LotL) and localized residential IP obfuscation | Network-layer packet-level heuristic baselining and credential invalidation |
| Direct Enterprise Cost | Estimated hundreds of millions in cumulative forensic reviews | Federal infrastructure protection budgets allocated via Defense appropriations |
Capital Allocation and Market Repercussions
The implications of this federal takedown reverberate far beyond national security circles, landing squarely on the balance sheets of asset managers, critical infrastructure operators, and enterprise technology vendors. The realization that critical civilian systems are actively targeted by nation-state actors triggers profound structural shifts across several capital and operational arenas:
1. The Cyber Insurance Underwriting Crisis
The insurance-linked securities (ILS) and cyber insurance reinsurance markets are moving swiftly to adjust risk modeling. As state-sponsored operations explicitly target civilian infrastructure to establish latent disruption capabilities, underwriters are tightening policy language around "war and state-sponsored cyber exclusions." Enterprise risk officers face an environment where infrastructure-level downtime caused by nation-state collateral damage may be excluded from conventional indemnification, forcing corporations to self-insure or allocate higher capital reserves to contingency accounts.
2. Acceleration of Zero-Trust Network Architecture (ZTNA)
Enterprise capital expenditure (CapEx) is shifting rapidly away from legacy perimeter security toward Zero-Trust Network Architecture (ZTNA) and Micro-segmentation. With hardware perimeters proved porous to state-backed actors using stolen credentials, chief information security officers (CISOs) are compelled to deploy identity-based micro-perimeters around industrial control systems. The valuation multiples for cybersecurity providers offering identity governance, privileged access management (PAM), and automated behavioral anomaly detection are seeing strong support despite broader macroeconomic contractions in corporate IT budgets.
3. Hardware Vendor Liability and Lifecycle Compliance
The federal action highlights a gaping regulatory vacuum: the continued manufacturing and deployment of edge devices with no long-term security patching lifecycle. Regulators in both the U.S. and European Union are advancing "Secure-by-Design" mandates. Hardware manufacturers who abandon legacy devices without mandatory firmware security pipelines are increasingly likely to face enterprise liability lawsuits and commercial exclusion from federal procurement frameworks. This shift is set to permanently compress gross margins for low-cost hardware manufacturers while incentivizing managed hardware-as-a-service (HaaS) enterprise architectures with recurring software support contracts.
Frequently Asked Questions (People Also Ask)
What is a SOHO IoT botnet, and why are nation-state hackers using it?
A Small Office/Home Office (SOHO) Internet of Things (IoT) botnet is an interconnected network of compromised edge devices, such as residential internet routers, smart security cameras, and network-attached storage units. Nation-state adversaries leverage these networks because they lack endpoint detection software and robust administrative oversight. By routing attacks through tens of thousands of everyday domestic internet connections, the hackers bypass geolocation filters and blend their operations seamlessly into standard consumer web traffic, completely blinding enterprise defenders.
How did federal law enforcement legally alter software on privately owned routers?
The Department of Justice obtained search and seizure warrants under Rule 41 of the Federal Rules of Criminal Procedure, authorized by a federal magistrate judge. These warrants empowered the FBI to remotely communicate with the infected private routers, delete the adversary's malicious code, terminate the device's connection to the hacker-controlled command-and-control server, and implement basic safeguards to prevent immediate reinfection—all without disturbing the lawful functionality of the underlying consumer devices.
What distinguishes "Living-off-the-Land" tactics from traditional malware?
Traditional cyberattacks typically deploy custom malicious files—such as trojans, worms, or ransomware executables—onto an infected machine, which can be identified, fingerprinted, and quarantined by signature-based antivirus or behavioral endpoint detection software. "Living-off-the-Land" (LotL) tactics bypass these safeguards entirely by using legitimate, pre-installed administrative software tools native to the target operating system (such as PowerShell, command-line utilities, or administrative scripting). Because the hackers perform their actions using native tools and valid credentials, security programs struggle to distinguish unauthorized activity from everyday IT administrative tasks.
How does this federal operation impact critical infrastructure operators?
The disruption signals an immediate mandate for infrastructure operators in water, power, transport, and telecommunications to execute comprehensive credential resets, phase out non-serviceable edge equipment, and deploy multi-tiered logging solutions. Furthermore, it shifts operational risk into the regulatory sphere: companies failing to audit supply-chain hardware and eliminate end-of-life edge vulnerabilities risk substantial compliance penalties under emerging federal cybersecurity directives.
Future Outlook and Strategic Milestones
While the federal disruption successfully crippled the primary command infrastructure of this specific state-backed operation, federal intelligence leaders openly concede that this victory is tactical, not strategic. The adversary's underlying strategic imperatives remain unchanged. Industry leaders, defense analysts, and enterprise capital allocation committees must monitor several key operational inflection points in the coming quarters:
- Adversarial Reconstitution: State-sponsored actors are expected to reconstitute their proxy infrastructure by targeting newly identified zero-day vulnerabilities in broader consumer IoT ecosystems and enterprise virtualization software.
- Federal Regulatory Enforcement: Expect CISA and the Environmental Protection Agency (EPA), alongside energy regulators (FERC/NERC), to issue stricter, binding operational directives that penalize infrastructure operators who run legacy, unsupported perimeter devices.
- Corporate Governance and Supply Chain Vetting: Corporate boards will face increased shareholder scrutiny and regulatory exposure regarding their Third-Party Risk Management (TPRM) programs, forcing capital shifts toward automated, real-time supply-chain monitoring platforms.
As the geopolitical friction between Washington and Beijing deepens, cyberspace has solidified as the decisive front of asymmetric confrontation. The neutralization of this critical infrastructure botnet demonstrates that the modern battlefield is no longer defined strictly by military installations, but by the distributed, unmanaged code running quietly in the civilian background.