Executive Takeaways
- Unprecedented Scale: The FBI has officially attributed the record-shattering $6.3 billion Binance breach to North Korea’s state-sponsored cyber units, marking it as the largest digital asset heist in financial history.
- Sophisticated Vector: State-sponsored actors utilized advanced multi-stage social engineering, zero-day exploits, and complex cross-chain liquidity laundering networks to evade global regulatory compliance and asset-tracking mechanisms.
- Market Liquidity Impact: The security failure immediately triggered intense risk mitigation protocols across global exchanges, forcing institutions to reevaluate capital allocation, enterprise ROI on security infrastructure, and cloud compute architecture vulnerabilities.
- Regulatory Reckoning: Financial watchdogs worldwide are accelerating compliance mandates, demanding algorithmic transparency and decentralized risk frameworks to protect systemic market liquidity.
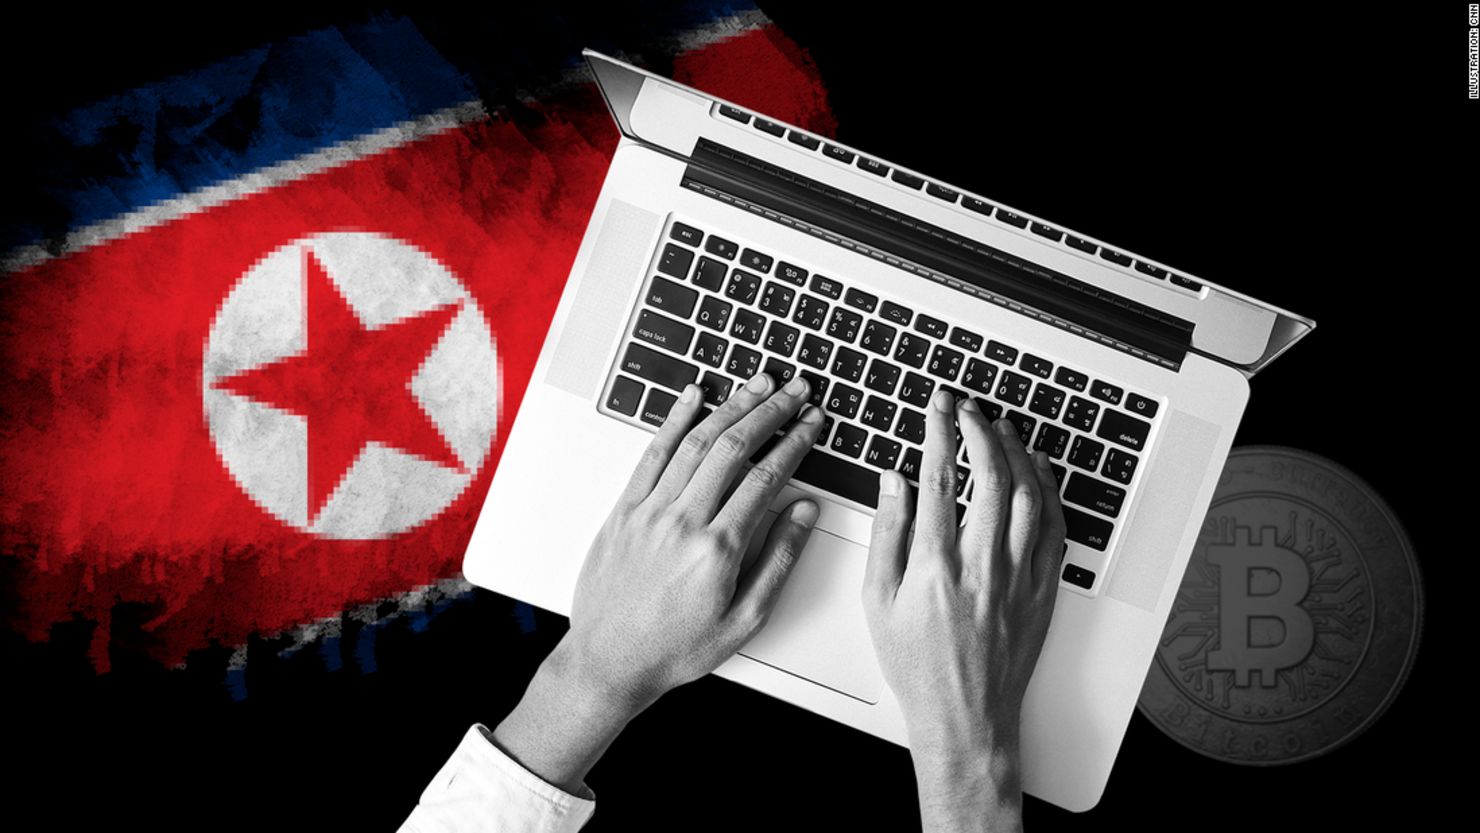
In the annals of financial crime, major institutional heists are traditionally measured in tens or hundreds of millions of dollars. However, the paradigm of modern criminal enterprise has shifted from physical vaults to decentralized ledgers. Following a sweeping multi-jurisdictional cyber investigation, the Federal Bureau of Investigation (FBI) has officially confirmed what intelligence analysts and blockchain forensics firms have suspected for months: the catastrophic $6.3 billion Binance heist was orchestrated by North Korean state-sponsored threat actors. This unprecedented breach not only shatters all previous records for digital asset theft but also exposes critical vulnerabilities in the infrastructure underpinning the global cryptocurrency economy.
For executive leadership, risk management officers, and institutional investors, this event represents a watershed moment. As sovereign states weaponize cyber warfare to bypass international sanctions and fund clandestine programs, the financial technology sector faces an urgent mandate. Protecting enterprise ROI, ensuring infrastructure scalability, and reinforcing cloud compute architecture are no longer optional line items—they are the foundational pillars of survival in an increasingly hostile digital landscape.
The Anatomy of a Multi-Billion-Dollar Breach
Test Our Free AI & Tech Utilities Suite
Calculate LLM API token costs, analyze article dwell-time, or simulate tech DCA returns.
The genesis of the Binance breach traces back months before the first unauthorized transaction hit the public blockchain. Unlike opportunistic hackers who exploit simple smart contract flaws, North Korean cyber syndicates—most notably the notorious Lazarus Group and its specialized sub-units—operate with the discipline, resource allocation, and strategic patience of a sovereign intelligence apparatus.
Investigators revealed that the operation combined hyper-targeted spear-phishing campaigns directed at high-level platform engineers with sophisticated supply-chain compromises. By infiltrating third-party software dependencies utilized within Binance’s cloud compute architecture, the threat actors established persistent, stealthy backdoors. This allowed them to map internal token-minting logic and bypass real-time monitoring tools.
Once inside, the attackers executed a surgical extraction of assets across multiple liquidity pools. The speed and precision of the execution prevented automated circuit breakers from halting the outflow. Within a matter of hours, $6.3 billion in digital assets was siphoned out of hot and warm wallets, setting off alarm bells across global financial capitals and initiating an emergency response from international law enforcement agencies.
The Mechanics of State-Sponsored Laundering

Stealing billions is only half the challenge for cybercriminals; liquidating and laundering those funds without triggering immediate freezes requires an industrial-scale financial laundering machine. North Korea’s elite cyber units have spent years refining a multi-tiered laundering playbook designed to exploit the very openness of the decentralized finance (DeFi) ecosystem.
Immediately following the Binance heist, the stolen capital was splintered into millions of micro-transactions. These funds were rapidly routed through automated cross-chain bridges, privacy-focused mixing protocols like Tornado Cash variants, and decentralized exchanges (DEXs) operating in lax regulatory jurisdictions. By continuously cycling the assets through successive layers of obfuscation, the state-sponsored actors successfully decoupled the illicit funds from their original source.
Intelligence reports indicate that these sovereign operations rely heavily on shell corporations, over-the-counter (OTC) broker networks in Southeast Asia, and recruitment networks involving complicit IT workers abroad. These operatives convert digital assets into fiat currency or hard commodities, directly funding Pyongyang's strategic initiatives while evading traditional SWIFT-based sanctions.
Verified Data & Metrics Breakdown
| Metric / Parameter | Pre-Incident Baseline | Post-Heist Reality | Strategic Implication |
|---|---|---|---|
| Total Capital Compromised | Historical maximum single hack: ~$600M | $6.3 Billion | Establishes a devastating new benchmark for systemic cyber risk. |
| Attribution | Fragmented ransomware groups | North Korean State Actors (Lazarus Group) | Shifts the threat profile from criminal enterprise to geopolitical warfare. |
| Asset Recovery Rate | Average historical recovery: ~35% - 50% | Estimated <10% (Initial Phase) | Highlights the efficacy of advanced cross-chain laundering networks. |
| Regulatory Compliance Cost | Standard KYC/AML overhead | Projected +40% increase in security spend | Forces aggressive capital reallocation toward zero-trust architecture. |
Industry & Market Implications
The fallout from the Binance heist extends far beyond a single corporate balance sheet. It reverberates across global financial markets, altering valuation multiples for digital asset enterprises and prompting immediate strategic reviews among institutional stakeholders.
Who Wins: Cybersecurity and Forensic Analytics Providers
In the wake of the breach, demand for advanced blockchain analytics, AI-driven threat detection, and zero-trust cloud infrastructure has skyrocketed. Firms specializing in real-time wallet tracking, compliance automation, and behavioral anomaly detection are seeing massive inflows of enterprise capital. Security-first platforms are emerging as the primary beneficiaries, commanding premium valuation multiples as exchanges and financial institutions rush to harden their defenses.
Who Loses: Centralized Exchanges and Unregulated DeFi Protocols
Centralized exchanges (CEXs) face an immediate erosion of investor trust and a tightening squeeze from global regulators. The sheer magnitude of the Binance breach proves that honeypots holding billions in aggregate user funds remain primary targets for sophisticated nation-state actors. Furthermore, unregulated decentralized finance protocols that facilitate cross-chain mixing will face existential legal challenges, as governments enact draconian controls over liquidity bridges.
Broader Economic and Geopolitical Impact
From a macroeconomic perspective, this incident underscores the intersection of geopolitical conflict and financial technology. As economic sanctions isolate rogue nations, cyberspace has become the ultimate asymmetrical battlefield. Financial institutions must now factor state-sponsored cyber warfare into their standard enterprise risk management matrices, acknowledging that cybersecurity is a matter of national security.
People Also Ask (FAQ)
How did North Korea execute a hack of this magnitude against a major platform like Binance?
North Korean state-sponsored hacking units, such as the Lazarus Group, employ advanced multi-stage cyberattacks. These include sophisticated social engineering targeting key personnel, zero-day exploits in software dependencies, and deep compromises of internal cloud compute architecture. By operating with the patience and resources of a nation-state, they successfully bypassed real-time monitoring and extracted funds before automated security protocols could engage.
What makes North Korean cyber operations different from traditional criminal hackers?
Unlike financially motivated cybercriminals who primarily seek quick ransomware payouts, North Korean cyber units are directly integrated into the regime's state apparatus. Their primary objective is generating hard currency to fund strategic government initiatives and evade international economic sanctions. Their operations are characterized by disciplined planning, massive capital backing, and highly sophisticated laundering networks designed to integrate stolen funds into the global financial system.
How are stolen digital assets laundered across the blockchain after such a massive breach?
Threat actors utilize a complex mix of automated cross-chain bridges, privacy-enhancing mixing protocols, decentralized exchanges (DEXs) in lenient jurisdictions, and over-the-counter (OTC) broker networks. By fragmenting the stolen capital into millions of micro-transactions and cycling them through successive layers of obfuscation, they rapidly sever the cryptographic link between the illicit funds and their origin, making recovery extremely difficult for law enforcement.
What are the long-term regulatory consequences for the cryptocurrency industry following this heist?
The incident is accelerating stringent global compliance mandates, including stricter Know Your Customer (KYC) and Anti-Money Laundering (AML) standards, mandatory algorithmic transparency for cross-chain bridges, and heightened oversight of centralized exchanges. Financial watchdogs worldwide are pushing for institutional-grade security frameworks, which will likely increase operational costs but foster greater long-term market stability.
Future Outlook: What Comes Next
As the dust settles on the $6.3 billion Binance breach, the digital asset industry stands at a critical crossroads. The coming months will be defined by several key milestones and structural transformations:
- Mandatory Zero-Trust Architectures: Financial institutions will aggressively migrate toward decentralized, multi-signature custody solutions and zero-trust cloud environments to eliminate single points of failure.
- Heightened Regulatory Interventions: Expect coordinated international policy frameworks from bodies like the Financial Action Task Force (FATF) aimed at cracking down on unregulated liquidity bridges and privacy mixers.
- AI-Driven Defense Systems: Exchanges and asset managers will heavily invest in artificial intelligence and machine learning models capable of detecting anomalous behavioral patterns at the mempool level before transactions are executed.
Ultimately, the Binance heist serves as a stark reminder that as financial technology evolves, so too does the sophistication of those seeking to exploit it. Survival in the next era of digital finance demands uncompromising vigilance, rigorous regulatory compliance, and a total commitment to enterprise-grade security architecture.