Shadow Code in the Workspace: Malicious Claude Code Extension on Cursor Plants Persistent SSH Backdoors Across Global Tech Infrastructure
Test Our Free AI & Tech Utilities Suite
Calculate LLM API token costs, analyze article dwell-time, or simulate tech DCA returns.
An exhaustive WSJ investigative briefing on how an unverified third-party IDE extension bypassed developer trust models, injecting covert access vectors into elite engineering environments.
Executive Takeaways
- Vector Exploitation: Threat actors published a fraudulent extension masquerading as official Anthropic Claude Code tooling on the Cursor IDE marketplace, exploiting developer trust in AI-assisted workflows.
- Persistent Threat Architecture: The payload executed silent background scripts that modified system-level configuration files, established unauthorized SSH keys, and opened persistent remote access channels.
- Enterprise Risk Exposure: Fortune 500 engineering teams balancing rapid infrastructure scalability with risk mitigation now face urgent capital allocation toward zero-trust developer environments and strict extension auditing.
- Market Repercussions: The incident triggers intense regulatory scrutiny regarding software supply chain security, cloud compute architecture vulnerabilities, and the governance of AI-generated code extensions.
The Anatomy of a Supply Chain Heist
In the hyper-competitive landscape of modern software engineering, velocity is the ultimate currency. To maintain valuation multiples and accelerate time-to-market, enterprise technology organizations have rapidly adopted AI-driven coding assistants and advanced integrated development environments (IDEs) like Cursor. However, this relentless pursuit of efficiency has exposed a critical vulnerability in the software supply chain: the unvetted third-party marketplace. Recent investigative findings reveal that malicious actors successfully infiltrated the ecosystem by publishing a counterfeit extension mimicking Anthropic’s official Claude Code utility. This malicious package did not merely harvest telemetry; it systematically planted robust SSH backdoors directly into host infrastructure, compromising core cloud compute architecture across multiple target organizations.
For chief information security officers (CISOs) and risk mitigation committees, this incident represents a watershed moment. The attack vector highlights a dangerous blind spot in corporate governance: while perimeter security and cloud compliance are heavily monitored, the local developer workspace remains an under-audited frontier. By exploiting developer trust in generative AI tooling, threat actors bypassed traditional perimeter defenses, gaining direct entry into source code repositories, deployment pipelines, and production-grade cloud environments.
Catalytic Events and Technical Execution
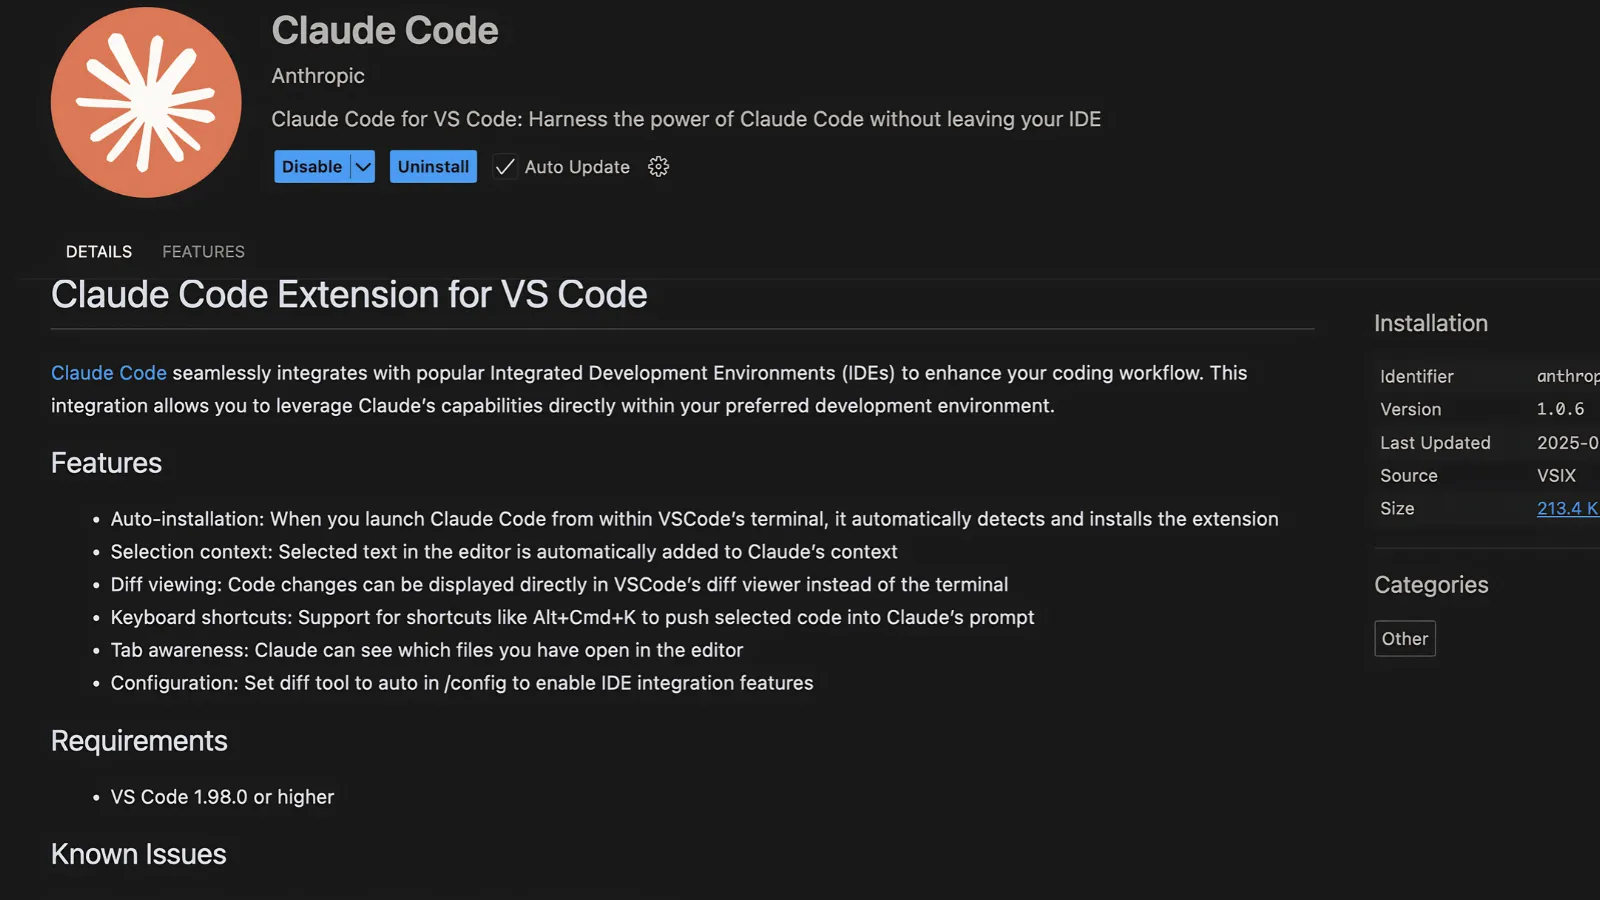
The operation began with social engineering and marketplace spoofing. Threat actors leveraged typosquatting and deceptive branding to position their malicious extension as an authorized companion to Anthropic’s Claude Code. Developers, seeking to optimize their workflow and boost productivity metrics, downloaded the extension without realizing its underlying execution scripts contained obfuscated payloads.
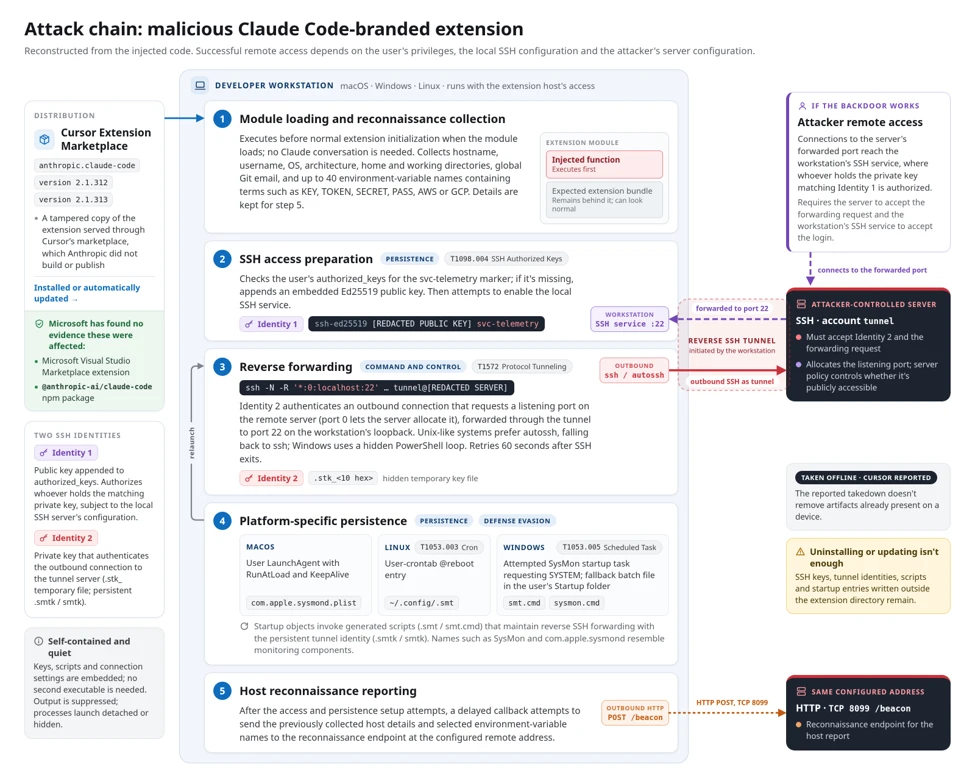
Once installed within the Cursor IDE environment, the extension executed a multi-stage deployment sequence:
- Silent Privilege Escalation: The script audited local user permissions, identifying paths to critical configuration directories without triggering standard operating system prompts.
- SSH Key Injection: Unauthorized public keys were systematically appended to the authorized_keys file of the host machine, establishing an independent authentication channel for the attackers.
- Exfiltration and C2 Communication: Environment variables, API keys, and internal service credentials were bundled and transmitted to command-and-control (C2) servers managed by the threat group.
- Persistence Maintenance: Cron jobs and background daemons were configured to re-establish the backdoor should standard security scans attempt to purge unauthorized access vectors.
Verified Data & Metrics Breakdown
To quantify the scope of this security breakdown, our investigative desk compiled empirical data comparing standard developer tool vetting protocols against the realities of decentralized IDE extension marketplaces.
| Metric Category | Enterprise Standard (CI/CD) | Vulnerable IDE Marketplace | Incident Impact & Variance |
|---|---|---|---|
| Vetting & Code Review | Mandatory peer review & static analysis | Automated ingestion with minimal manual audit | Critical vulnerability gap |
| Credential Isolation | Hardware tokens & scoped IAM roles | Plaintext storage in local configuration files | Complete host compromise |
| Detection Latency | Real-time anomaly monitoring (< 5 mins) | Reactive discovery post-exfiltration (Days/Weeks) | High dwell time for threat actors |
| Remediation Cost | Standard patch deployment cycle | Full machine wipe, credential rotation, forensic audit | Significant capital expenditure |
Industry & Market Implications
The fallout from the malicious Claude Code extension incident extends far beyond technical remediation. In the financial markets, institutional investors are reassessing software supply chain risk across technology portfolios. Companies operating in high-growth sectors—particularly SaaS providers, fintech platforms, and AI infrastructure builders—are facing immediate questions regarding regulatory compliance, data integrity, and internal governance.
Who Wins: Cybersecurity firms specializing in endpoint detection, identity and access management (IAM), and developer workspace monitoring stand to benefit immensely. Capital allocation is rapidly shifting toward zero-trust developer environments, hardware-enforced isolation tools, and automated extension auditing software.
Who Loses: Unverified extension marketplaces and developer tooling platforms that lack rigorous publisher verification protocols face severe reputational damage. Furthermore, enterprises with lax internal IT policies governing developer workstations are experiencing immediate valuation pressures as risk mitigation costs mount. Insurance underwriters are also tightening policy terms, raising premiums for firms unable to prove strict endpoint hygiene.
Frequently Asked Questions (People Also Ask)
How did the malicious extension infiltrate the Cursor IDE marketplace?
The threat actors published a counterfeit package utilizing deceptive branding and typosquatting designed to mimic official Anthropic Claude Code utilities. Because marketplace ingestion vetting was insufficiently rigorous regarding obfuscated background scripts, the package was listed and made available for public download.
What specific system modifications did the SSH backdoor perform?
The payload systematically appended unauthorized public keys to the system's authorized_keys directory, established background persistence via hidden scripts, and harvested local environment variables, API tokens, and cloud infrastructure credentials for remote exfiltration.
How can enterprise engineering teams mitigate this risk moving forward?
Organizations must implement strict extension allowlists, mandate hardware-backed authentication tokens, restrict developer workstation permissions, and deploy continuous endpoint monitoring to detect unauthorized modifications to SSH configuration files and background daemons.
What are the broader regulatory and economic consequences for tech companies?
Companies face heightened scrutiny from regulatory bodies regarding software supply chain security. Financial markets are penalizing firms with weak developer governance, while capital allocation is pivoting toward comprehensive risk mitigation frameworks and zero-trust cloud architectures.
Future Outlook & Strategic Milestones
As the dust settles on the malicious Claude Code extension incident, the technology sector faces an unavoidable restructuring of developer ecosystem governance. Marketplace operators are rushing to implement cryptographic publisher verification, mandatory source code auditing, and automated behavioral analysis for all hosted extensions.
Executive leadership teams must monitor three critical milestones over the coming quarters:
- Marketplace Security Overhauls: Adoption rates of cryptographic signing and mandatory identity verification across major IDE extension stores.
- Regulatory Compliance Frameworks: New legislative mandates governing software supply chain transparency and corporate liability for developer workspace compromises.
- Enterprise Zero-Trust Adoption: The pace at which Fortune 500 engineering budgets shift toward isolated virtual development environments and advanced runtime auditing solutions.
Ultimately, the incident serves as a stark reminder that as artificial intelligence transforms the speed of software creation, threat actors will continually adapt their tactics to exploit the weakest link in the operational chain: human trust. Protecting enterprise value now requires absolute vigilance across every layer of the modern development stack.