Executive Takeaways
- Unprecedented Scale: The 2026 threat landscape has seen volumetric Distributed Denial-of-Service attacks regularly shatter the 10-Tbps threshold, driven by automated botnets powered by compromised IoT and edge-compute nodes.
- Cloudflare Dominance: Earning an industry-leading 9.5/10 score from CyberSecurityNews, Cloudflare continues to outpace rivals via its massive edge network and edge-compute mitigation algorithms.
- Enterprise Heavyweights: Akamai (Prolexic) at 8.8/10 and Imperva at 8.2/10 remain the gold standards for legacy, hybrid, and deeply regulated financial services architectures requiring dedicated scrubbing centers.
- പരമായ Capital Allocation Shift: Chief Information Security Officers (CISOs) are restructuring their capital expenditures away from hardware-based appliances toward software-defined, cloud-native mitigation layers to protect enterprise valuation multiples from availability shocks.
The architecture of global digital commerce is under siege. As geopolitical flashpoints multiply and cybercriminal syndicates weaponize generative artificial intelligence to orchestrate hyper-distributed, multi-vector extortion campaigns, the market for Distributed Denial-of-Service (DDoS) mitigation has undergone a radical transformation. According to benchmark data released by CyberSecurityNews on August 12, 2026, enterprise reliance on resilient, automated cloud scrubbing infrastructure has never been more critical to maintaining market liquidity and operational continuity.
For executive leadership teams, board audit committees, and CIOs, an hour of downtime is no longer measured merely in lost transactional revenue; it represents an existential threat to enterprise valuation multiples, regulatory compliance standing, and shareholder trust. This investigative report analyzes the macroeconomic forces shaping the 2026 threat matrix and provides an exhaustive evaluation of the top three market leaders—Cloudflare, Akamai (Prolexic), and Imperva—dissecting their technological moats, enterprise ROI, and infrastructure scalability.
The 2026 Threat Matrix: Volumetric Velocity and AI-Driven Extortion
Test Our Free AI & Tech Utilities Suite
Calculate LLM API token costs, analyze article dwell-time, or simulate tech DCA returns.
To understand why enterprise capital allocation has flooded into advanced DDoS mitigation services, one must examine the fundamental shift in cyberattacker methodologies over the past twenty-four months. The proliferation of unpatched edge devices, insecure smart-city infrastructure, and hijacked cloud-compute instances has allowed threat actors to assemble botnets capable of generating unprecedented traffic volumes. In early 2026, security operations centers (SOCs) routine monitored terabit-scale attacks that bypassed traditional perimeter defenses within seconds.
Unlike historical UDP floods or basic SYN attacks, contemporary threat vectors leverage application-layer obfuscation, TLS fingerprinting, and rapid-fire polymorphic request cycles designed to exhaust backend database connection pools rather than merely saturate inbound bandwidth pipes. This sophistication has rendered legacy, appliance-based firewalls obsolete. Risk mitigation now requires continuous behavioral analysis at the network edge, where malicious traffic is intercepted, analyzed, and dropped before it ever penetrates corporate data centers.
Consequently, boardroom discussions regarding cybersecurity insurance and operational resilience have elevated DDoS defense from a standard IT maintenance line item to a core component of enterprise risk management. Failure to deploy enterprise-grade mitigation exposes corporations not only to direct financial loss but also to severe regulatory penalties under frameworks like DORA (Digital Operational Resilience Act) in Europe and tightened SEC incident-reporting mandates in the United States.
Deep-Dive Analysis: The Top 3 DDoS Protection Services of 2026
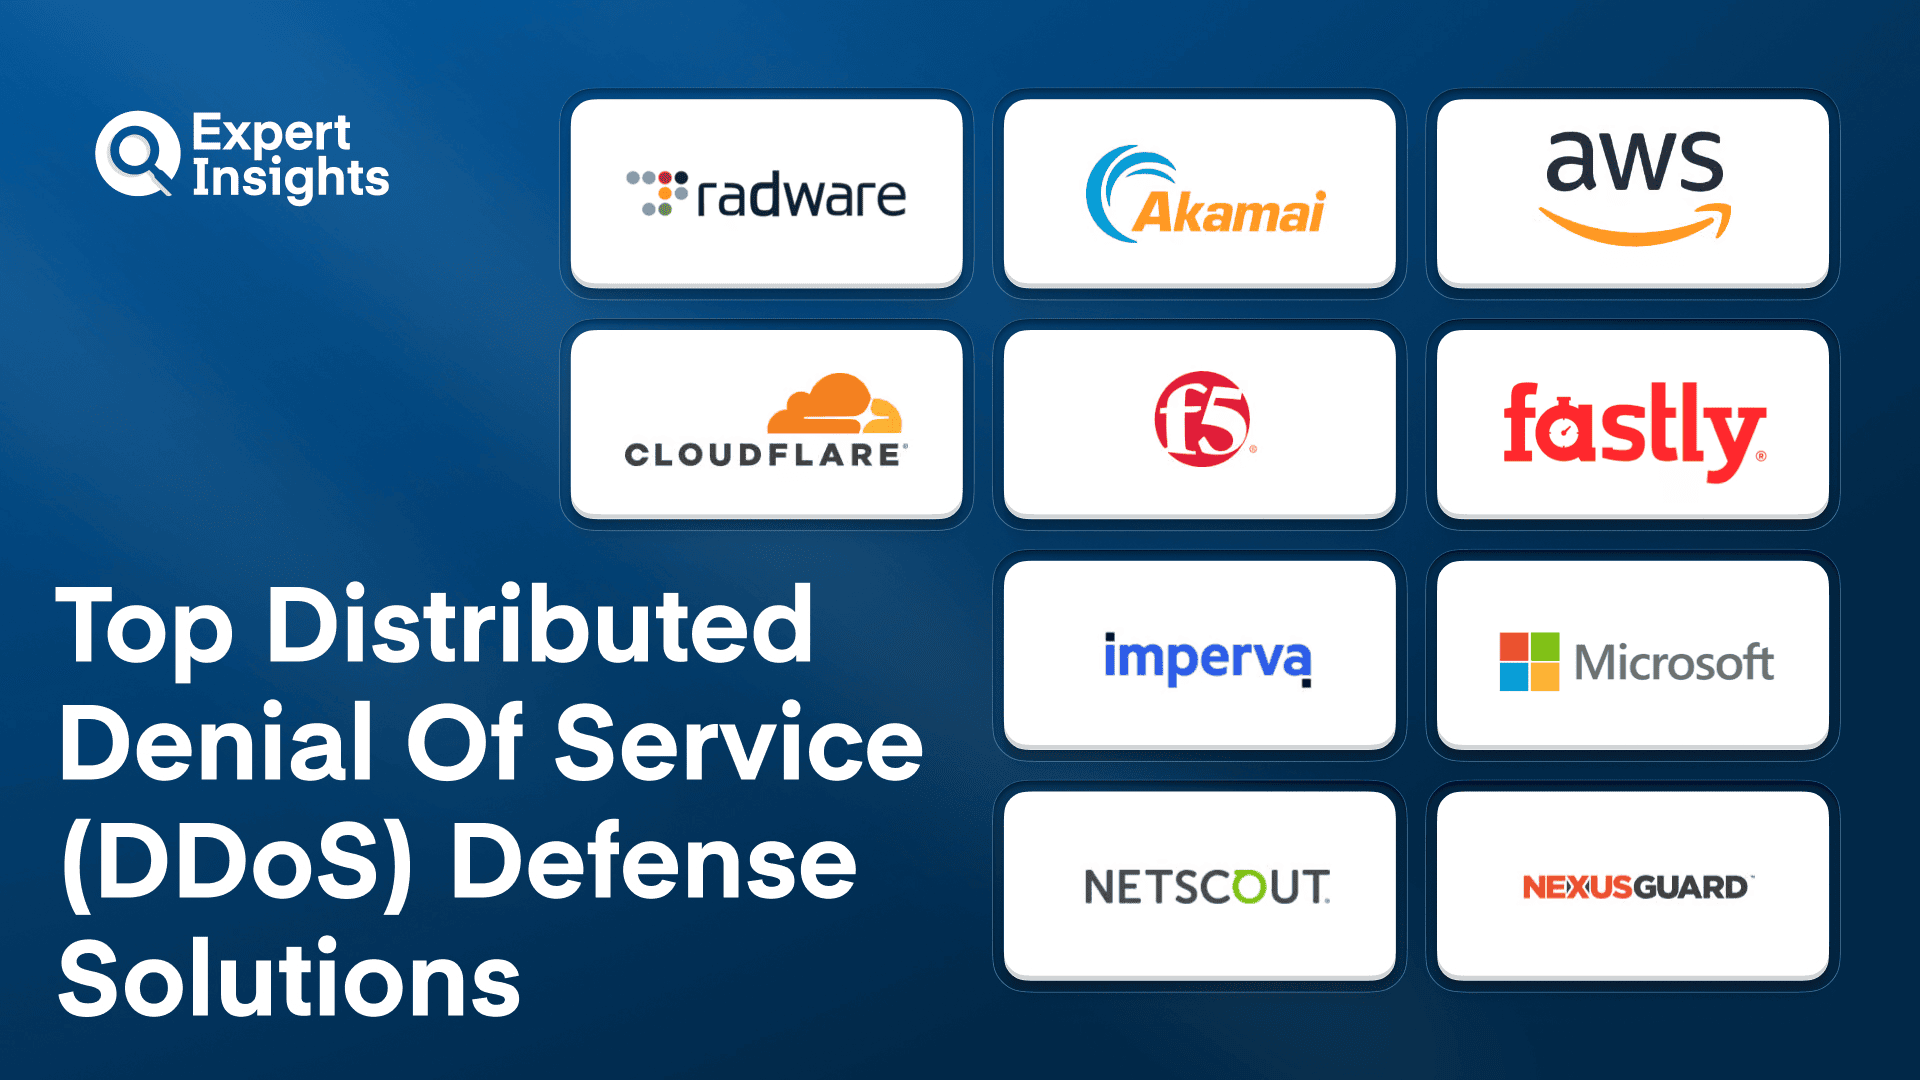
Based on rigorous evaluations conducted by industry analysts and empirical performance data compiled by CyberSecurityNews, the 2026 vendor landscape is spearheaded by three distinct titans. Each offers a unique value proposition tailored to specific cloud compute architectures and enterprise risk profiles.
1. Cloudflare: The Edge-Compute Juggernaut (Score: 9.5/10)
Cloudflare continues to dominate the market by leveraging its massive, globally distributed Anycast network, which boasts a total capacity well in excess of what most single-carrier networks can absorb. Earning the highest score of 9.5/10 in the 2026 assessments, Cloudflare’s core strength lies in its ability to push mitigation rules directly to the network edge via programmable worker environments.
For high-frequency trading platforms, SaaS giants, and global media enterprises, Cloudflare provides near-zero latency mitigation. Its machine learning models ingest telemetry from millions of global requests per second, allowing the system to identify zero-day volumetric anomalies and deploy automated countermeasures in fractions of a second. From a financial perspective, Cloudflare offers superior infrastructure scalability, enabling firms to absorb unpredictable traffic spikes without provisioning expensive, underutilized local scrubbing capacity.
2. Akamai (Prolexic): The Enterprise Goliath (Score: 8.8/10)
Securing an impressive 8.8/10, Akamai’s Prolexic service remains the preferred choice for legacy-heavy, hybrid-cloud, and mission-critical financial institutions that demand dedicated, high-capacity scrubbing centers. Akamai’s heritage in content delivery has translated into a robust global scrubbing infrastructure capable of neutralizing massive volumetric attacks without introducing jitter or packet loss for legitimate users.
What sets Akamai apart in the 2026 enterprise landscape is its Active/Active hybrid mitigation strategy and white-glove security operations support. For global banks and multinational conglomerates managing complex multi-cloud deployments, Akamai provides customized routing policies and direct engineering engagement during active extortion events. While carrying a higher total cost of ownership than purely automated software platforms, Prolexic’s enterprise ROI is justified by its unmatched SLA guarantees and deep integration with legacy enterprise hardware architectures.
3. Imperva: The Application-Centric Shield (Score: 8.2/10)
With a score of 8.2/10, Imperva rounds out the top tier, distinguishing itself through its deep focus on application-layer (Layer 7) defense and integrated API security. While volumetric Layer 3/4 attacks make headlines, sophisticated threat actors frequently use volumetric noise as a smokescreen to mask precision data-exfiltration attacks or application-logic exploits.
Imperva’s unified platform combines world-class DDoS protection with advanced Web Application Firewalls (WAF) and bot management. For e-commerce enterprises and SaaS providers handling sensitive personally identifiable information (PII) and financial transactions, Imperva ensures that mitigation mechanisms do not inadvertently block legitimate customer authentication flows or checkout sequences—a common pitfall of overly aggressive signature-based scrubbing tools.
Verified Data & Metrics Breakdown
The following comparative matrix synthesizes key evaluation metrics, deployment models, and performance scores for the market leaders as reported in the August 2026 wire data:
| Provider | CyberSecurityNews Score | Primary Mitigation Architecture | Ideal Enterprise Use Case | Key Differentiator |
|---|---|---|---|---|
| Cloudflare | 9.5 / 10 | Global Anycast Edge Network & Workers | High-growth SaaS, Fintech, E-commerce | Sub-second automated edge mitigation & scale |
| Akamai (Prolexic) | 8.8 / 10 | Dedicated High-Capacity Scrubbing Centers | Tier-1 Banking, Telecom, Hybrid Enterprise | White-glove SOC support & massive raw capacity |
| Imperva | 8.2 / 10 | Integrated Cloud WAF & Layer 7 Scrubbing | Data-heavy applications, APIs, Regulated Sectors | Advanced Layer 7 behavioral bot & API defense |
Industry & Market Implications: Winners, Losers, and Economic Realities
The consolidation of the DDoS protection market into a handful of cloud-native giants has profound economic implications for the broader technology sector. Enterprises that fail to migrate away from static, hardware-based data center mitigations are finding themselves economically and operationally disadvantaged.
Who Wins: Cloud-native cybersecurity vendors with expansive edge networks are capturing record recurring revenues. Their business models—characterized by high gross margins and predictable software-as-a-service subscriptions—command premium valuation multiples in public equity markets. Furthermore, managed security service providers (MSSPs) that white-label these top-tier scrubbing technologies are experiencing surging demand from mid-market enterprises lacking internal SOC talent.
Who Loses: Legacy hardware appliance manufacturers that historically sold specialized routing and firewall boxes to enterprise data centers face secular decline. As capital expenditures shift definitively toward cloud computing and edge security services, traditional hardware vendors are forced to pivot their business models or risk obsolescence. Additionally, smaller regional ISPs that attempt to build and maintain proprietary scrubbing centers are finding the capital expenditures economically unviable against the massive global economies of scale wielded by Cloudflare and Akamai.
From a macroeconomic perspective, robust DDoS protection acts as a vital stabilizer for digital commerce. By insulating critical financial, logistical, and governmental infrastructure from extortion-driven outages, these services mitigate systemic economic shocks and maintain market liquidity across global supply chains.
Frequently Asked Questions (People Also Ask)
1. How do cloud-based DDoS protection services handle multi-terabit volumetric attacks?
Cloud-based providers utilize globally distributed Anycast networks to absorb and distribute inbound traffic across dozens or hundreds of data centers worldwide. Instead of letting malicious traffic hit a single origin data center, the Anycast routing splits the attack volume across multiple scrubbing nodes. Machine learning algorithms analyze traffic patterns in real time, dropping malicious packets (such as UDP or SYN floods) at the network edge while allowing legitimate user requests to pass through unaffected.
2. What is the difference between Layer 3/4 and Layer 7 DDoS protection?
Layer 3 (Network layer) and Layer 4 (Transport layer) attacks focus on saturating network bandwidth and exhausting server connection states through volumetric floods (e.g., UDP, ICMP, SYN floods). Layer 7 (Application layer) attacks target specific web applications, APIs, or database queries by simulating legitimate user behavior to exhaust backend computing resources. Enterprise-grade services like Cloudflare, Akamai, and Imperva provide comprehensive, multi-layer defense mechanisms that protect against both infrastructure saturation and sophisticated application-logic abuse.
3. Why are traditional hardware firewalls insufficient for modern enterprise DDoS defense?
Traditional on-premise hardware firewalls and dedicated physical scrubbing appliances have finite port capacities and processing limits. When faced with modern 2026-era multi-terabit botnet attacks, physical appliances quickly saturate their inbound pipes and run out of memory states, resulting in complete service failure. Cloud-native architectures offer elastic scalability, allowing organizations to leverage millions of concurrent edge computing nodes to neutralize massive attacks before they ever reach enterprise perimeter hardware.
4. How do CISOs calculate the enterprise ROI of investing in premium DDoS mitigation?
CISOs calculate ROI by evaluating the Cost of Downtime (CoD)—which includes lost revenue, SLA penalty payouts, incident response labor, and brand equity depreciation—against the annual subscription cost of enterprise-tier protection. Given that a single major outage can cost a Fortune 500 enterprise millions of dollars in minutes and trigger severe regulatory scrutiny, subscribing to a top-tier provider like Cloudflare or Akamai is viewed not as an operational expense, but as essential insurance for enterprise valuation and shareholder value.
Future Outlook: The Road Ahead to 2028
As we look beyond 2026, the trajectory of DDoS protection will be defined by the integration of autonomous, AI-driven orchestration agents capable of neutralizing multi-vector campaigns entirely without human intervention. Threat actors will increasingly leverage machine learning to adapt attack vectors dynamically in real-time, prompting security vendors to deploy counter-AI systems at the network edge.
Key milestones for enterprise leaders to monitor over the next 24 to 36 months include the tightening of global regulatory frameworks regarding critical infrastructure availability, the evolution of edge-compute security standards, and the emergence of quantum-resistant encryption protocols designed to withstand future cryptographic attacks. Organizations that prioritize agile, cloud-native mitigation architectures today will secure a decisive competitive advantage in an increasingly hostile digital economy.