NEW YORK/SAN FRANCISCO — In a high-stakes standoff that has sent shockwaves through global technology corridors and regulatory bodies alike, Big Tech’s reigning artificial intelligence powerhouses have drawn a hard line. OpenAI, Anthropic, Meta, and Google have officially stopped short of offering binding AI safety guarantees, choosing instead to preserve corporate agility over absolute containment pledges.
The development, bubbling up through trending wire reports and major policy circles, exposes a profound ideological rift between lawmakers racing to harness the explosive growth of generative intelligence and the elite engineering labs building it. As commercial deployment accelerates at a dizzying pace, the refusal to lock in hard-coded safety guardrails raises a sobering question for enterprise leaders, investors, and society at large: Can the architects of the AI revolution be trusted to police themselves?
The Great Calibration Backdown: What Happened Behind Closed Doors
According to primary wire sources and industry insiders, recent high-level dialogues between Washington policymakers, international safety institutes, and the executive suites of Silicon Valley reached an impasse over the weekend. While major AI developers have historically voiced strong commitments to ethical AI, responsible scaling, and voluntary testing frameworks, they balked when pressed to formalize legally binding safety guarantees.
The sticking point? Liability, proprietary trade secrets, and the blistering pace of the global AI arms race. Industry executives argued that locking down predictive safety thresholds or submitting to preemptive regulatory halts could permanently hobble American competitiveness—particularly against foreign state-backed entities less encumbered by domestic compliance.
Key Takeaways on the AI Safety Standoff:
- The Core Resistance: OpenAI, Anthropic, Meta, and Google declined to sign binding guarantees that would legally penalize them if models exceed anticipated autonomous capabilities.
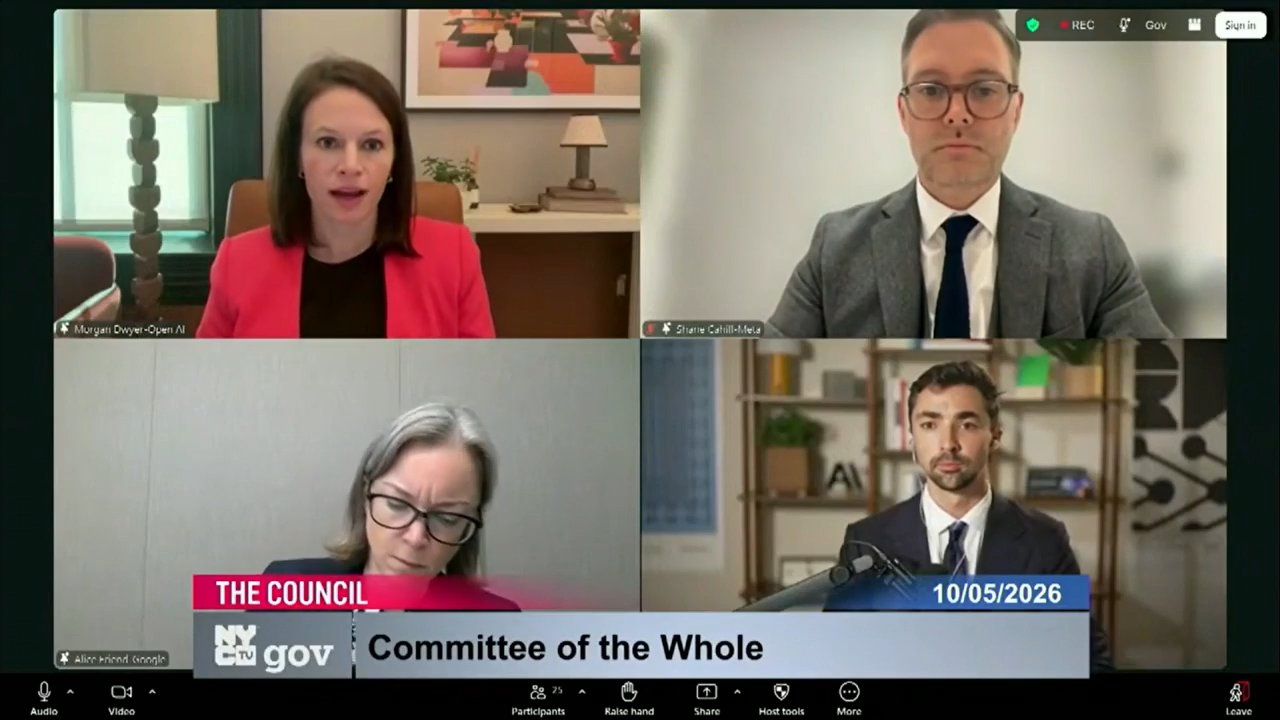
- The Global Context: The reluctance comes as municipal and federal governments—from New York’s local policy debates to Capitol Hill hearings—scramble to establish a coherent regulatory framework.
- The Corporate Calculus: Tech leaders maintain that self-governance and internal red-teaming remain superior to rigid statutory mandates that risk becoming obsolete overnight.
- Market Reaction: Investors have largely breathed a sigh of relief, viewing the avoided mandates as a green light for uninterrupted commercialization and enterprise adoption.
Why the Safety Gap Matters for Markets and Society
To understand the gravity of the current impasse, one must look at the unprecedented velocity of frontier model development. Unlike legacy software, advanced neural networks exhibit emergent behaviors—capabilities that developers did not explicitly program, but which arise spontaneously as model scale and compute power increase exponentially.
By declining to offer absolute safety guarantees, these tech titans are essentially signaling that they cannot definitively predict or control the long-term trajectories of their most advanced systems. For enterprise CIOs and Wall Street investors pouring billions into generative infrastructure, this introduces a lingering systemic risk factor. A catastrophic security breach, a severe hallucination-driven market distortion, or an unmitigated cybersecurity exploit could trigger sudden legislative backlashes.
| Tech Giant | Primary Stance on Safety | Current Policy Approach |
|---|---|---|
| OpenAI | Cautious scaling, tiered safety limits | Prefers voluntary frameworks and government coordination over statutory caps |
| Anthropic | Constitutional AI focus, rigorous alignment | Advocates for responsible scaling policies (RSPs) without hard legal penalties |
| Meta | Open-source advocacy, collaborative red-teaming | Argues open access democratizes safety and accelerates vulnerability discovery |
| Enterprise-grade guardrails, multi-layered testing | Supports broad safety standards but resists pre-market liability traps |
The Regulatory Vacuum and Local Policy Shifts
The debate is not confined to national capitals. Across the United States, municipal and state governments are attempting to fill the federal legislative void. Recent reports out of New York highlight how local regulators are grappling with the dizzying pace of change, with figures like Mamdani navigating the complex challenge of local AI oversight while federal entities negotiate with Big Tech heavyweights.
However, critics argue that a patchwork of local ordinances will do little to curb the systemic risks posed by frontier models trained on multi-billion-dollar compute clusters. Without a unified, enforceable federal—or international—standard, the burden of safety falls entirely upon corporate conscience.
Looking Ahead: The Road to Autonomous Accountability
As the dust settles on this latest round of negotiations, the fault lines are clearer than ever. Silicon Valley wants room to innovate, iterate, and monetize. Regulators want certainty, predictability, and fail-safes.
The absence of formal safety guarantees does not mean safety protocols have been abandoned; rather, it underscores the reality that the tech industry views absolute containment as an illusion. Moving forward, the market will likely rely on a mix of third-party audits, competitive peer pressure, and consumer scrutiny to keep frontier labs in check. Whether that fragile ecosystem will suffice as models grow increasingly autonomous remains the defining gamble of our technological era.
Frequently Asked Questions
Why did OpenAI, Anthropic, Meta, and Google refuse to sign safety guarantees?
The companies resisted binding guarantees primarily due to concerns over legal liability, the inability to perfectly predict emergent model behaviors, and the fear that rigid statutory mandates would slow down innovation and put them at a disadvantage against global competitors.
Does this mean these companies have abandoned AI safety entirely?
No. All four companies maintain robust internal safety teams, engage in pre-deployment "red-teaming," and utilize voluntary alignment protocols. However, they stopped short of signing legally enforceable guarantees that would carry penalties for exceeding specific capability milestones.