Executive Takeaways
- Unprecedented Mitigation Costs: Recent zero-day vulnerabilities in enterprise platforms like Kiteworks and Citrix forced organizations to take the drastic measure of completely powering down core data-protection infrastructure to halt active exploitation.
- Capital Allocation Paradigm Shift: Chief Information Security Officers (CISOs) are aggressively reallocating capital away from legacy perimeter defenses toward real-time telemetry, immutable backups, and automated zero-day containment strategies.
- Valuation and Compliance Risks: Regulatory frameworks such as SEC incident disclosure rules and DORA in Europe mean that emergency shutdowns now directly impact corporate valuations, share liquidity, and executive liability.
- Operational Continuity vs. Security: The directive to pull the plug on active enterprise platforms highlights a profound tension between maintaining business uptime and mitigating catastrophic data exfiltration risks.
In the high-stakes theater of modern enterprise technology, the margin for error has compressed to zero. Over the past three weeks, revelations surrounding zero-day exploitation incidents involving Kiteworks and Citrix have sent shockwaves through boardrooms from Wall Street to Silicon Valley. These incidents did more than highlight vulnerabilities in widely deployed enterprise software; they exposed a structural crisis in emergency incident response. When one major vendor instructed its enterprise customers to completely power down their data-protection platforms to evade active threat actors, it signaled a terrifying realization: traditional patching cycles are dead, and the cost of containment has never been higher.
For decades, enterprise IT architecture was built on the premise of resilience through redundancy and rapid patch deployment. Today, sophisticated threat groups—ranging from state-sponsored Advanced Persistent Threat (APT) syndicates to financially motivated ransomware cartels—routinely weaponize zero-day vulnerabilities faster than developers can write, test, and distribute cryptographic fixes. The recent disclosures involving Kiteworks and Citrix serve as a watershed moment, forcing corporate leadership to re-evaluate their risk mitigation frameworks, cloud compute architecture, and capital allocation strategies to survive in an era of asymmetric digital warfare.
Anatomy of a Crisis: The Kiteworks and Citrix Disclosures
Test Our Free AI & Tech Utilities Suite
Calculate LLM API token costs, analyze article dwell-time, or simulate tech DCA returns.
The catalytic events that brought zero-day incident response challenges to the forefront unfolded rapidly. Both Kiteworks—renowned for its secure file transfer and data protection solutions—and Citrix, a titan in application delivery and virtual desktop infrastructure, found themselves at the epicenter of intense security scrutiny. While the exact vectors and threat actor methodologies varied, the operational fallout shared a common, jarring denominator: extreme remediation demands.
When zero-day vulnerabilities are actively exploited in the wild, the standard playbook dictates isolating affected servers, applying emergency patches, and conducting forensic sweeps. However, the sophistication of recent attacks bypassed these conventional controls. In at least one of these high-profile instances, the recommended emergency protocol was not merely isolating a segment of the network, but entirely powering down the data-protection platform. For enterprises managing petabytes of sensitive intellectual property, financial records, and personally identifiable information (PII), pulling the plug on a core infrastructure asset is akin to a hospital shutting down its power grid during surgery.
This drastic measure underscores a profound evolution in threat actor capabilities. Attackers are no longer just seeking persistence; they are executing lightning-fast data exfiltration before defenders can comprehend the scope of the breach. Consequently, vendors are forced to recommend extreme measures that prioritize absolute containment over operational continuity, triggering massive downstream disruptions for enterprise clients who rely on these systems for daily regulatory and transactional compliance.
Verified Data & Metrics Breakdown
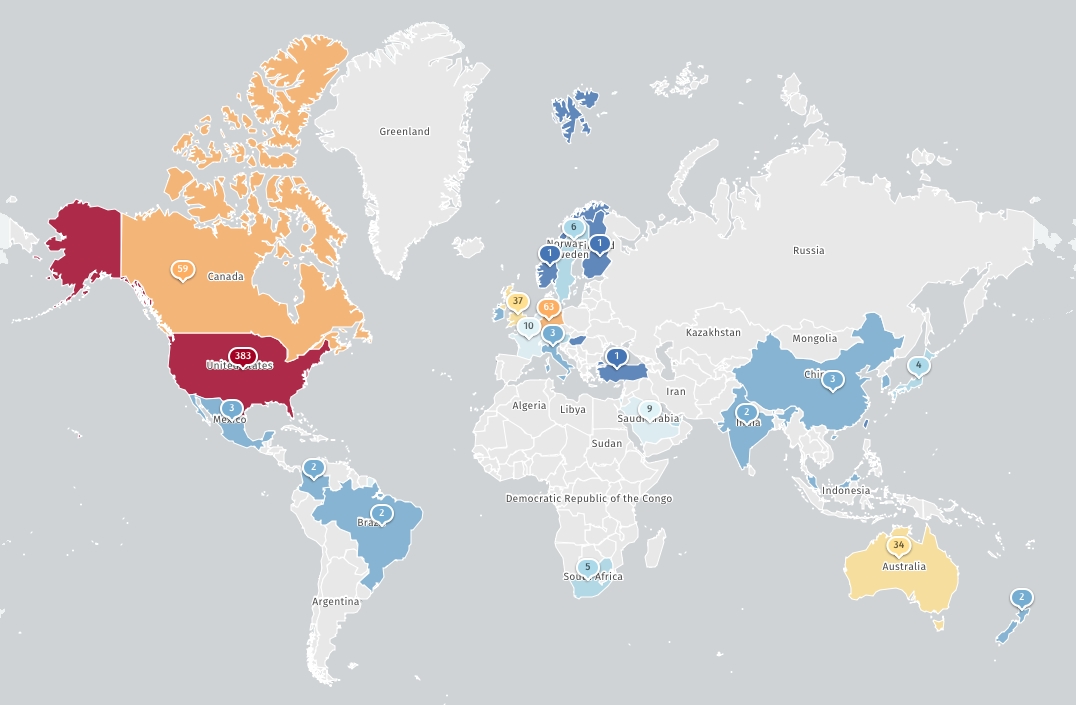
To understand the magnitude of the Kiteworks and Citrix incidents, we must examine the broader economic and operational metrics defining contemporary zero-day response challenges. The following table synthesizes key benchmarks regarding enterprise downtime costs, incident discovery timelines, and remediation impacts.
| Metric / Indicator | Pre-Incident Benchmark | Post-Kiteworks/Citrix Reality | Strategic Impact |
|---|---|---|---|
| Average Zero-Day Exploitation Window | Hours to days post-disclosure | Minutes to hours (often pre-disclosure) | Accelerates defensive automation needs |
| Emergency Shutdown Cost (Per Hour) | $300,000 – $500,000 | $1,000,000+ for Fortune 500 | Forces executive-level risk calculus |
| Regulatory Disclosure Timeline | Fragmented / State-by-state | Strict 4-day SEC / DORA mandates | Elevates legal and valuation risks |
| Infrastructure Resiliency Shift | Static perimeter defense | Zero-Trust / Ephemeral Architecture | Drives enterprise ROI to security tooling |
Industry & Market Implications
The repercussions of these incidents extend far beyond technical troubleshooting; they are reshaping market dynamics, vendor valuations, and corporate governance. In the financial markets, institutional investors are increasingly incorporating cyber resilience into their fundamental valuation models. When a major enterprise platform requires an emergency shutdown, the immediate operational paralysis translates directly into suppressed quarterly revenues, damaged customer trust, and, in severe cases, punitive regulatory fines.
Who Wins and Who Loses?
- Winners (Security Innovators & Automated Containment): Companies specializing in micro-segmentation, automated threat hunting, and immutable, air-gapped backups are seeing a surge in demand. Venture capital and enterprise IT budgets are aggressively pivoting toward solutions that allow organizations to isolate micro-services without pulling the plug on entire ecosystems.
- Losers (Legacy Monolithic Platforms): Vendors relying on legacy, tightly coupled architectures that cannot be patched or isolated dynamically are facing severe market skepticism. Enterprise buyers are demanding contractual indemnification and transparent vulnerability disclosure metrics before signing multi-year software licenses.
Furthermore, regulatory compliance has become a minefield. Under rigorous SEC guidelines in the United States and the Digital Operational Resilience Act (DORA) in the European Union, CISOs and executive boards face immense pressure to disclose material cybersecurity incidents swiftly and accurately. The chaotic nature of zero-day responses—where organizations are forced to shut down critical systems on a moment's notice—complicates compliance reporting, heightening the risk of shareholder lawsuits and executive liability.
Frequently Asked Questions (People Also Ask)
What is a zero-day vulnerability, and why are response incidents so challenging?
A zero-day vulnerability is an undiscovered software flaw known to attackers but unknown to the vendor. Response incidents are profoundly challenging because exploitation occurs before a patch exists, forcing organizations to rely on emergency containment measures—such as network isolation or complete platform shutdowns—rather than standard software updates.
Why did companies have to power down their data protection platforms during the Kiteworks and Citrix incidents?
When threat actors actively exploit zero-day flaws to bypass traditional access controls and exfiltrate data, patching alone is often insufficient because attackers may have already established persistent backdoors. Powering down the platform entirely is an extreme containment strategy designed to instantly halt active data theft and lateral network movement.
How do these zero-day incidents impact corporate valuations and regulatory compliance?
Emergency shutdowns disrupt core business operations, leading to lost revenue and increased remediation costs that can negatively affect quarterly earnings and valuation multiples. Additionally, strict regulatory frameworks like SEC disclosure rules and EU DORA mandate rapid reporting of material incidents, increasing legal scrutiny on corporate governance and incident response preparedness.
What structural changes are CISOs making to prepare for future zero-day exploits?
Security leaders are accelerating capital allocation toward Zero Trust Architecture (ZTA), micro-segmentation, continuous runtime monitoring, and automated threat containment tools. This ensures that if a core platform must be isolated or powered down, the blast radius is minimized, and business continuity is preserved.
Future Outlook: Navigating the New Era of Cyber Resilience
As we look toward the horizon, the Kiteworks and Citrix incidents will not be remembered as isolated anomalies, but as a harbinger of the new normal in enterprise technology. The velocity of modern threat actors guarantees that zero-day exploits will remain a persistent existential threat to digital infrastructure.
To thrive in this volatile environment, enterprise leadership must fundamentally rethink their approach to risk mitigation and infrastructure scalability. The era of reactive patching has officially closed. Organizations must embrace ephemeral cloud architectures, rigorous software bill of materials (SBOM) tracking, and automated containment protocols that remove human latency from the incident response equation. Ultimately, corporate valuation and market liquidity will increasingly belong to those enterprises that treat cyber resilience not as an IT checkbox, but as a core pillar of operational strategy and fiduciary duty.