Executive Takeaways
- Escalating Capital Exposure: Enterprise cyber risk has evolved from an IT compliance issue to a core determinant of valuation multiples, capital allocation, and market liquidity.
- The 2025 Threat Landscape: SentinelOne's telemetry highlights 12 distinct attack vectors shaping the modern threat matrix, ranging from autonomous AI-driven social engineering to unpatched multi-cloud misconfigurations.
- Strategic Risk Mitigation: CISOs are shifting from reactive perimeter defense to autonomous, behavioral-based endpoint detection and automated remediation workflows to safeguard enterprise ROI.
- Regulatory Pressures: Global governance standards now hold executive leadership and boards of directors personally accountable for material cybersecurity failures and delayed disclosures.
As global markets navigate a volatile macroeconomic climate, enterprise leadership faces a silent, compounding liability that threatens balance sheets with unprecedented velocity: sophisticated cyber warfare. No longer confined to the periphery of IT operations, cybersecurity has emerged as a primary determinant of corporate valuation. A single catastrophic breach can instantly compress market capitalization, disrupt supply chains, and trigger severe regulatory penalties that impair long-term capital allocation. According to recent telemetry and threat intelligence frameworks compiled by SentinelOne, the vector landscape has expanded exponentially, driven by the weaponization of artificial intelligence by threat actors and the complex sprawl of distributed enterprise cloud compute architectures.
This comprehensive investigative report examines the 12 defining cybersecurity issues shaping the enterprise threat horizon. Furthermore, we analyze the structural mitigation strategies, autonomous technologies, and risk-management frameworks required to preserve enterprise integrity, maintain investor confidence, and protect bottom-line performance.
The 2025 Threat Matrix: Dissecting the 12 Critical Cyber Security Issues
Test Our Free AI & Tech Utilities Suite
Calculate LLM API token costs, analyze article dwell-time, or simulate tech DCA returns.
The modern enterprise attack surface is vast, porous, and continuously evolving. As organizations accelerate digital transformation initiatives to capture market share, they inadvertently widen the apertures exploited by cybercriminal syndicates and state-sponsored APTs (Advanced Persistent Threats). Below is a granular breakdown of the 12 critical security vulnerabilities identified in the latest SentinelOne threat analysis, alongside tactical mitigation frameworks.
1. Autonomous AI-Driven Phishing and Social Engineering
Traditional phishing campaigns—characterized by broken syntax and obvious anomalies—have been replaced by hyper-personalized, context-aware attacks generated by large language models (LLMs). Threat actors leverage automated scraping tools to mimic executive communication styles flawlessly. Mitigation: Deploy next-generation email security powered by behavioral AI that analyzes intent and semantic context rather than relying solely on static reputation lists, coupled with continuous, context-driven workforce simulation training.
2. Multi-Cloud Misconfigurations and Identity Sprawl
As organizations distribute workloads across AWS, Microsoft Azure, and Google Cloud, fragmented visibility leads to persistent misconfigurations. Over-permissioned IAM (Identity and Access Management) roles create frictionless pathways for lateral movement. Mitigation: Implement Cloud Security Posture Management (CSPM) tools alongside zero-trust architecture (ZTA) enforcing strict least-privilege access and automated remediation of exposed storage buckets.
3. Supply Chain and Third-Party Vendor Vulnerabilities
The modern enterprise is only as secure as its weakest vendor. Software supply chain attacks, such as compromised open-source repositories and malicious updates to enterprise-grade third-party software, allow attackers to bypass perimeter controls entirely. Mitigation: Mandate rigorous Software Bill of Materials (SBOM) tracking, continuous third-party risk assessments, and real-time vendor behavioral monitoring.
4. Ransomware-as-a-Service (RaaS) and Double Extortion
Ransomware is no longer just an encryption event; it is an economic extortion enterprise. RaaS syndicates exfiltrate sensitive intellectual property and financial data before deploying file-locking payloads, threatening public exposure or regulatory disclosure. Mitigation: Move beyond legacy signature-based antivirus to autonomous Endpoint Detection and Response (EDR) platforms capable of blocking malicious encryption routines in real-time without human intervention.
5. API Vulnerabilities and Insecure Data Transmission
Application Programming Interfaces (APIs) form the connective tissue of modern digital applications, yet they frequently lack adequate authentication and rate-limiting controls, exposing sensitive enterprise endpoints. Mitigation: Establish a centralized API inventory, conduct automated vulnerability scanning during the CI/CD pipeline, and enforce robust token-based authentication.
6. Insider Threats and Privileged Access Abuse
Whether malicious or accidental, insiders possessing elevated access privileges represent an asymmetric risk to enterprise data assets. Detecting unauthorized data exfiltration disguised as routine workflow is exceptionally difficult for traditional security tools. Mitigation: Deploy User and Entity Behavior Analytics (UEBA) to baseline normal network activity and flag anomalous data-access patterns immediately.
7. Operational Technology (OT) and IoT Convergence
The convergence of IT and OT networks—driven by industrial IoT adoption—has exposed critical manufacturing, energy, and logistics infrastructure to remote cyber intrusion. Mitigation: Enforce strict network segmentation between corporate IT networks and industrial control systems (ICS), coupled with passive network monitoring designed specifically for OT protocols.
8. Living-off-the-Land (LotL) Attacks
Sophisticated threat actors increasingly eschew traditional malware, instead utilizing legitimate administrative tools already present within the operating system (such as PowerShell, WMI, and remote management utilities) to execute attacks. This technique deliberately blinds legacy security controls. Mitigation: Utilize advanced behavioral analytics and memory inspection tools that detect unauthorized command-line execution and anomalous administrative behaviors.
9. Shadow IT and Unsanctioned SaaS Applications
Employees utilizing unvetted cloud applications to boost short-term productivity inadvertently create compliance blind spots and data leakage vectors outside the control of corporate security teams. Mitigation: Utilize Cloud Access Security Brokers (CASBs) to discover, monitor, and restrict unauthorized SaaS utilization across the enterprise network.
10. Zero-Day Exploits and Patch Latency
The window between the public disclosure of a zero-day vulnerability and its exploitation by threat actors has shrunk to mere hours. Organizations crippled by bureaucratic patch management schedules remain dangerously exposed. Mitigation: Prioritize vulnerability remediation based on real-time threat intelligence rather than static CVSS scores, and deploy virtual patching capabilities to buy critical remediation time.
11. Deepfake Executive Impersonation and Financial Fraud
Generative audio and video deepfakes are now sophisticated enough to impersonate C-suite executives during live video conferences or phone calls, authorizing fraudulent wire transfers or credential disclosures. Mitigation: Establish out-of-band verification protocols, multi-party authorization limits for financial disbursements, and employee training focused on deepfake detection indicators.
12. Quantum Computing Threat Horizons (Cryptographic Agility)
While fully realized cryptographic-breaking quantum computers remain on the horizon, state actors are currently harvesting encrypted enterprise data with the intent to decrypt it retroactively once quantum capabilities mature. Mitigation: Audit current cryptographic infrastructure and transition toward post-quantum cryptography (PQC) standards to ensure long-term data confidentiality.
Verified Data & Metrics Breakdown
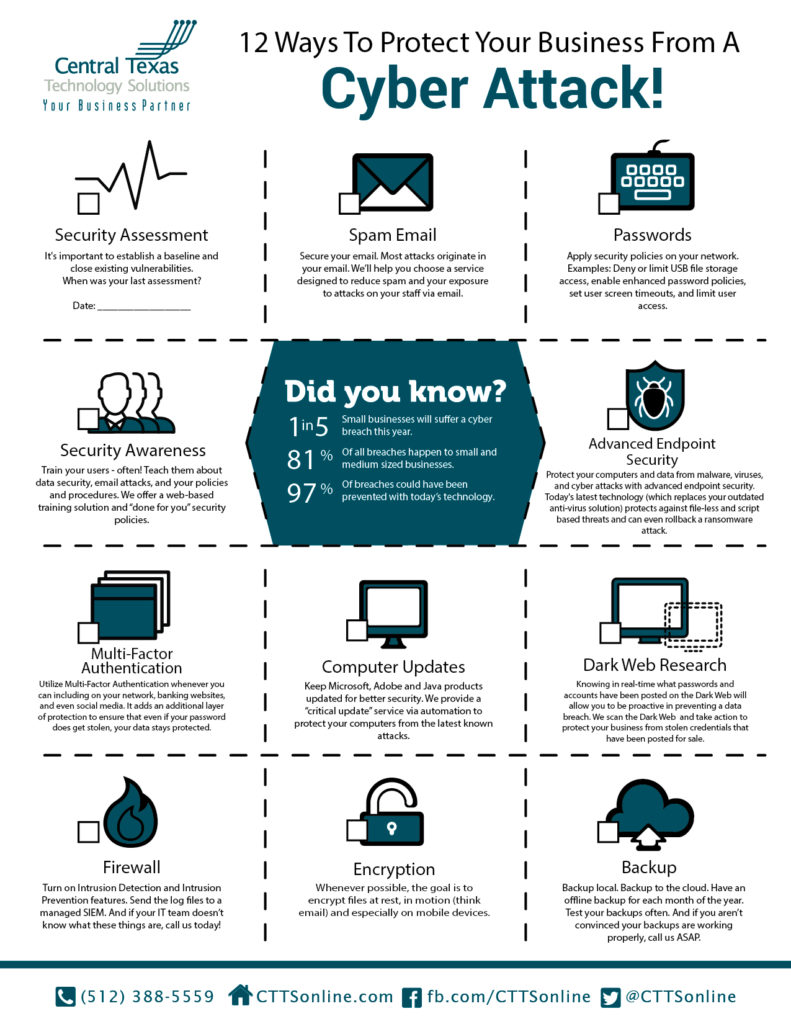
To quantify the financial and operational impact of these evolving vectors, market researchers and cybersecurity analysts track key performance indicators across global enterprises. The comparative data below illustrates the shifting dynamics of enterprise cyber risk.
| Metric Category | Historical Benchmark (2022) | Current Enterprise Reality (2025) | Strategic Implication |
|---|---|---|---|
| Average Global Cost of a Data Breach | $4.35 Million | $4.88 Million+ | Direct erosion of operating margins and liquidity reserves. |
| Mean Time to Detect (MTTD) | 207 Days | Under 30 Days (via AI automation) | Autonomous EDR significantly compresses dwell time. |
| Ransomware RaaS Attack Velocity | Days to weeks per deployment | Hours from initial access to exfiltration | Requires machine-speed automated response frameworks. |
| Cloud Misconfiguration Incidents | 35% of total breaches | 52% of enterprise data exposures | Mandates unified CSPM and automated posture enforcement. |
Industry & Market Implications: Who Wins, Who Loses
The escalating severity of these 12 cybersecurity issues is profoundly restructuring the corporate landscape, creating clear economic winners and losers across global markets.
The Winners: Enterprise-grade security platforms offering autonomous, AI-driven remediation—such as SentinelOne—are capturing significant market share. Insurtech and specialized cyber insurance underwriters equipped with rigorous technical underwriting standards are successfully expanding profit margins. Furthermore, managed detection and response (MDR) providers are experiencing unprecedented demand as mid-market enterprises struggle to recruit and retain certified cybersecurity talent.
The Losers: Organizations clinging to legacy perimeter defenses, manual patching schedules, and fragmented point solutions face severe operational and financial penalties. Private equity firms and institutional investors are increasingly penalizing M&A valuations for target companies with unverified software supply chains and unresolved technical debt in their cloud infrastructure. Additionally, executives who fail to demonstrate proactive governance face swift board-level ousters and personal legal exposure.
Frequently Asked Questions (People Also Ask)
How do AI-driven cyber threats fundamentally differ from traditional attacks?
Traditional cyber threats rely on static code signatures and predictable attack scripts that security systems can catalog and block over time. AI-driven threats utilize machine learning models to dynamically adapt their behavior, bypass traditional rules-based firewalls, automate reconnaissance, and generate hyper-realistic social engineering campaigns at a scale and speed that human security teams cannot match manually.
What is the role of SentinelOne in mitigating modern enterprise threats?
SentinelOne provides autonomous, AI-driven cybersecurity solutions designed to prevent, detect, and respond to threats at machine speed. By leveraging behavioral telemetry and automated remediation workflows across endpoints, cloud workloads, and identity vectors, SentinelOne eliminates dwell time, stops ransomware in its tracks, and reduces the operational strain on internal security operations centers (SOCs).
Why are multi-cloud misconfigurations considered such a severe financial risk?
Modern enterprises frequently distribute operations across multiple cloud providers without centralized visibility. A single misconfigured cloud storage bucket or over-privileged identity role can expose proprietary intellectual property, customer PII, and financial records to public access, triggering massive regulatory fines under GDPR, CCPA, and SEC disclosure mandates, alongside severe reputational damage.
How can boards of directors better measure return on investment (ROI) for cybersecurity spending?
Board-level cybersecurity ROI should not be measured merely by money saved from prevented breaches, but by risk-adjusted capital preservation, reduced cyber insurance premium volatility, preserved valuation multiples during funding rounds, and compliance readiness that eliminates costly regulatory penalties and litigation expenses.
Future Outlook and Strategic Milestones
As we look toward the remainder of the decade, the convergence of autonomous artificial intelligence, quantum computing horizons, and ubiquitous cloud interconnectivity will continue to redefine the parameters of digital risk. Enterprises that view cybersecurity strictly as an operational expense will find themselves at a distinct competitive disadvantage.
Executive leadership must prioritize three critical milestones over the next 12 to 18 months:
- Transition to Autonomous Defense: Discarding legacy manual security processes in favor of machine-speed, AI-driven endpoint and cloud protection platforms.
- Enforcing Zero-Trust Architectures: Implementing rigorous identity verification across every user, device, and API interaction within the corporate ecosystem.
- Alignment of Cyber Risk with Capital Strategy: Integrating real-time threat intelligence directly into enterprise risk management (ERM) frameworks to protect valuation multiples and investor trust.
Ultimately, cyber resilience is no longer an optional IT initiative—it is the bedrock of modern corporate governance and enterprise survival.