JOHANNESBURG — As the digital perimeter expands across the African continent, executive boardrooms are confronting an unforgiving economic reality: cybersecurity is no longer a localized IT expenditure, but a core determinant of enterprise valuation multiples, investor confidence, and market liquidity. Against this high-stakes backdrop, the 29th Edition of the Cyber Security Summit South Africa has officially gained unprecedented steam, drawing elite policymakers, risk officers, and chief information security officers (CISOs) to address a rapidly shifting threat landscape.
With primary intelligence indicating escalating sophistication in state-sponsored and financially motivated cyberattacks targeting critical infrastructure, financial services, and telecommunications, this year's summit serves as a critical crucible for modern enterprise defense strategies. Anchored by the central case study—Building Cyber-Resilient Enterprises in South Africa—the event arrives at a pivotal juncture where regulatory compliance, cloud compute architecture, and capital allocation strategies intersect.
Executive Takeaways
Test Our Free AI & Tech Utilities Suite
Calculate LLM API token costs, analyze article dwell-time, or simulate tech DCA returns.
- Escalating Enterprise Exposure: South African corporations face an unprecedented surge in sophisticated ransomware and distributed denial-of-service (DDoS) campaigns, threatening capital liquidity and operational continuity.
- Regulatory Pressures Mount: Strict enforcement of data protection mandates, including the Protection of Personal Information Act (POPIA), forces boards to elevate risk mitigation to the highest governance tiers.
- The ROI of Resilience: Industry leaders at the 29th summit emphasize that proactive infrastructure scalability and zero-trust frameworks directly preserve enterprise valuation and institutional investor trust.
- Collaborative Defense Ecosystems: Public-private partnerships are proving essential in sharing threat intelligence and neutralizing transnational cyber syndicates targeting emerging markets.
The Catalytic Shift: Why the 29th Summit Marks a Turning Point
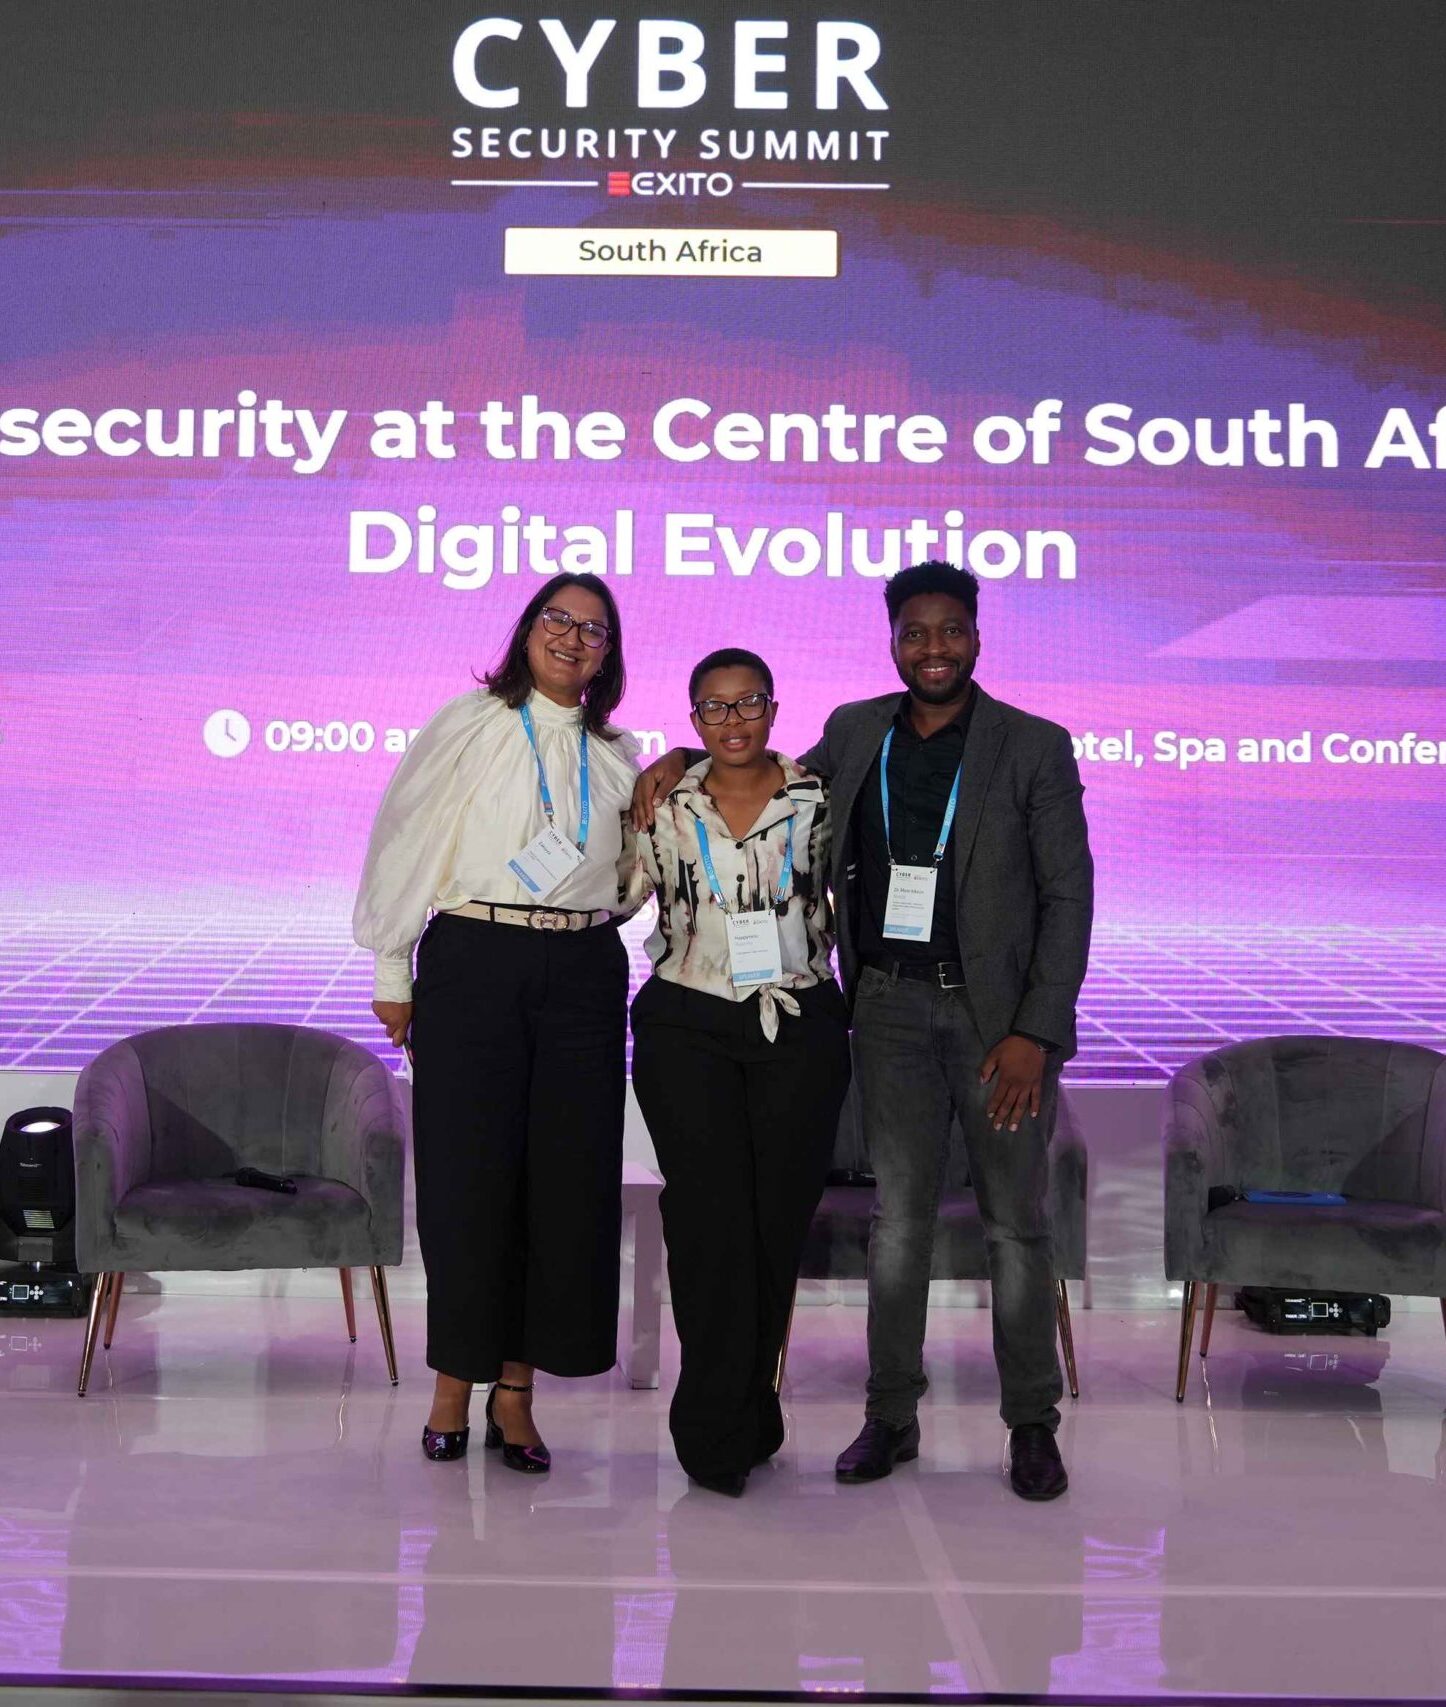
The timing of the 29th Cyber Security Summit SA is far from coincidental. Over the past twenty-four months, South Africa has solidified its position as the digital economic hub of Southern Africa, simultaneously making it the primary target for malicious cyber actors operating across global jurisdictions. As regional enterprises accelerate their digital transformation journeys—migrating core banking systems, supply chain logistics, and customer databases to hyper-scale cloud environments—the surface area for potential breaches has expanded exponentially.
According to recent industry data discussed at the summit, the average cost of a data breach for South African enterprises has scaled upward, impacting bottom-line profitability and triggering immediate contractions in market capitalization for publicly traded firms. Consequently, institutional investors are increasingly incorporating robust cybersecurity audits into their due diligence frameworks. Companies unable to demonstrate verifiable risk mitigation and regulatory compliance find themselves facing compressed valuation multiples and higher costs of capital.
The core case study headlining the event—Building Cyber-Resilient Enterprises in South Africa—delves deep into the mechanics of transforming organizational culture from reactive defense to proactive resilience. Speakers underscored that security architecture must be baked into the foundational layers of enterprise software development and cloud compute infrastructure, rather than bolted on as an afterthought.
Verified Data & Metrics Breakdown
To contextualize the scale of the challenge and the strategic focus of the 29th Cyber Security Summit SA, the following comparative framework outlines the shifting priorities in South African enterprise risk management:
| Metric / Indicator | Previous Baseline (2023–2024) | Current Summit Benchmark (2026) | Strategic Implication |
|---|---|---|---|
| Primary Threat Vector | Basic Phishing & Malware | AI-Driven Social Engineering & Ransomware-as-a-Service | Demands automated, AI-powered threat detection and zero-trust protocols. |
| Board-Level Engagement | Delegated entirely to IT Department | Direct oversight by Risk & Audit Committees | Elevates cybersecurity to a board-level fiduciary responsibility. |
| Capital Allocation Priority | Perimeter Firewalls & Compliance Checklists | Continuous Threat Exposure Management & Employee Training | Shifts spending toward operational resilience and behavioral analytics. |
| Regulatory Audit Rigor | Moderate enforcement of POPIA | Aggressive audits with severe financial penalties for data leakage | Increases legal exposure and necessitates flawless data governance. |
Industry & Market Implications: Winners and Losers
The intense focus on cyber resilience unfolding at the summit has profound macroeconomic ramifications across South African commerce. Identifying who stands to gain and who faces structural disadvantage is crucial for institutional asset managers and corporate strategists.
The Winners: Proactive Adapters and Specialized Vendors
Enterprise organizations that have treated cybersecurity as a strategic asset rather than an administrative hurdle are reaping substantial rewards. Financial institutions and telecommunications giants investing heavily in automated security orchestration, response (SOOR) platforms, and zero-trust network access (ZTNA) are successfully protecting their market share. Furthermore, specialized cybersecurity advisory firms, cloud security architects, and compliance technology vendors are experiencing surging demand, driving robust revenue growth and attractive investment returns.
The Losers: Legacy Laggards and Under-Resourced Firms
Conversely, mid-market enterprises and legacy-bound institutions that underinvest in digital defense infrastructure face severe systemic risks. A single successful breach can result in catastrophic reputational damage, regulatory fines, and operational downtime that erodes customer trust permanently. For these entities, the cost of inaction far outweighs the capital expenditure required to modernize their security stacks.
Frequently Asked Questions (People Also Ask)
What is the primary objective of the 29th Cyber Security Summit SA?
The summit aims to unite industry leaders, policymakers, and cybersecurity professionals to address escalating digital threats, share best practices in enterprise resilience, and evaluate regulatory compliance strategies tailored to the African market.
How does enterprise cyber resilience impact corporate valuation?
Institutional investors and equity analysts increasingly factor cybersecurity posture into corporate valuations. Firms with robust risk mitigation frameworks and zero-trust architectures enjoy higher valuation multiples and lower costs of capital compared to vulnerability-prone competitors.
What role does regulatory compliance play in South Africa's cybersecurity landscape?
Regulations such as the Protection of Personal Information Act (POPIA) impose strict legal obligations on enterprises handling consumer data. Non-compliance results in severe financial penalties, making regulatory alignment a critical component of board-level governance.
How are South African businesses tackling AI-driven cyber threats?
Organizations are increasingly deploying artificial intelligence and machine learning tools within their own security operations centers (SOCs) to detect anomalies in real-time, outpacing the speed and complexity of automated attacks launched by malicious actors.
Future Outlook: What Comes Next
As the 29th Edition of the Cyber Security Summit SA concludes its core sessions, the mandate for corporate leadership is unequivocally clear: passive defense is obsolete. The coming quarters will test the execution capabilities of South African enterprises as they translate summit insights into boardroom policies and operational workflows.
Key milestones to watch include the rollout of tighter central bank cybersecurity directives for financial institutions, increased enforcement actions by data protection regulators, and the integration of quantum-resistant encryption standards among early-adopting technology firms. For investors and executives alike, the message emanating from Johannesburg is unmistakable—future-proofing the enterprise begins and ends with uncompromised digital resilience.