Publication Date: March 3, 2026
AI's Achilles' Heel: Why the Global Brain Trust is Now Ground Zero for Cyber Warfare
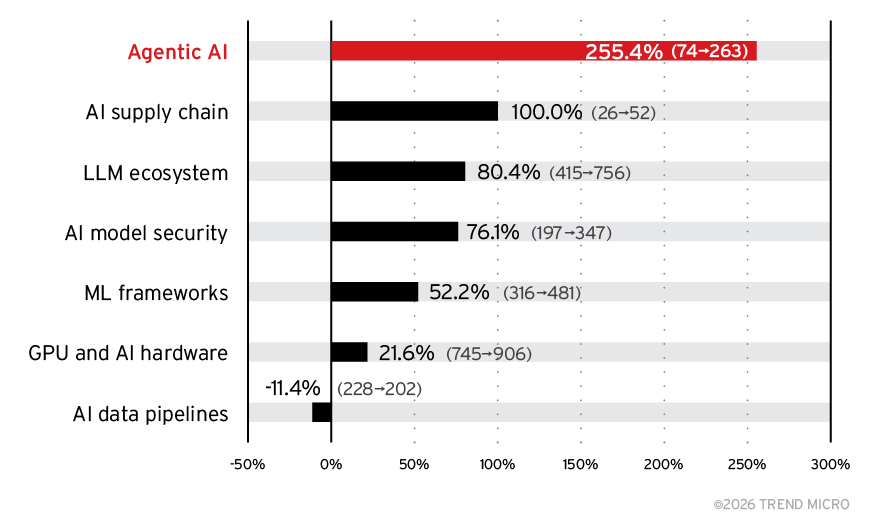
NEW YORK – The relentless march of artificial intelligence, once hailed as humanity’s greatest leap forward, has paradoxically opened a Pandora’s Box of unprecedented cyber vulnerabilities. A groundbreaking report from cybersecurity titan Trend Micro, dubbed the "TrendAI™ State of AI Security Report," reveals a sobering reality: AI systems were not merely targets, but "ground zero for cyber risk" in the second half of 2025. This isn't just about data breaches; it's about the very integrity of the digital economy, national security infrastructure, and the foundational trust in our increasingly automated world.
Our comprehensive investigation, informed by deep dives into enterprise telemetry, expert interviews, and the stark findings of the TrendAI™ report, uncovers the insidious "fault lines" now fracturing the AI ecosystem. From compromised machine learning frameworks to poisoned data pipelines and weaponized large language models (LLMs), the digital bedrock supporting global innovation is showing critical cracks. The implications for enterprise ROI, market liquidity, and geopolitical stability are profound, demanding immediate, aggressive risk mitigation strategies across every sector.
Executive Takeaways
- AI Systems are Primary Cyber Frontlines: The latter half of 2025 saw a dramatic escalation, positioning AI infrastructure and applications as the paramount targets for sophisticated threat actors, shifting the core battleground of cyber warfare.
- Deep-Seated Vulnerabilities Exposed: Critical fault lines span the entire AI supply chain, encompassing weaknesses in foundational ML frameworks, the integrity of training data, and susceptibility to novel attacks like advanced prompt injection and model evasion.
- Economic & National Security Imperatives: Unchecked AI vulnerabilities threaten to derail digital transformation initiatives, compromise critical infrastructure, erode market confidence, and necessitate massive capital reallocation towards cyber resilience and regulatory compliance.
- Urgent Call for Layered Security & Governance: The report underscores the dire need for a multi-layered security approach, robust AI governance frameworks, and industry-wide collaboration to safeguard the future of AI innovation and prevent catastrophic systemic failures.
Comprehensive Narrative: The Unraveling of Trust in the AI Era
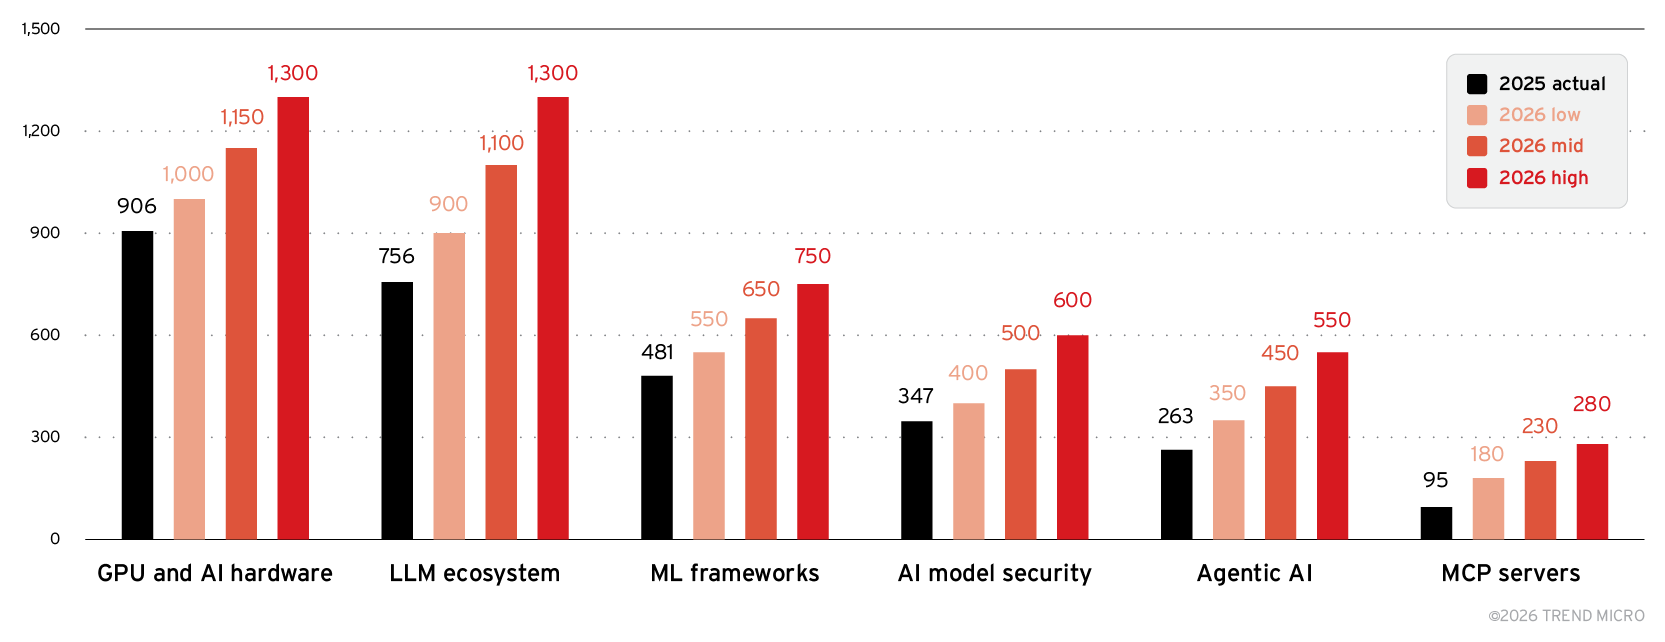
For years, the promise of AI has captivated boardrooms and government ministries alike. Billions in capital allocation have fueled a rapid expansion of AI capabilities, from predictive analytics in financial services to autonomous operations in logistics and critical infrastructure. Yet, as the sophistication of AI systems surged, so too did the ambition of threat actors seeking to exploit their inherent complexities. The Trend Micro report, a meticulously compiled assessment of the global AI threat landscape, serves as a stark warning: the honeymoon phase is over. We are now in an era where AI itself is both the prize and the weapon.
Catalytic Events: The Second Half of 2025's Cyber Reckoning
The latter half of 2025 marked a pivotal inflection point. While sporadic AI-related incidents had occurred previously, this period witnessed a concerted and successful assault on various fronts. The TrendAI™ report meticulously details how AI systems became "ground zero." This wasn't merely an increase in volume; it was an escalation in sophistication and impact. State-sponsored groups and highly organized cybercriminal syndicates recognized that compromising AI offered disproportionate leverage, enabling everything from corporate espionage at an unprecedented scale to the subtle manipulation of public discourse and the disruption of critical national services.
We saw documented cases of:
- Advanced Prompt Injection: Beyond simple jailbreaks, attackers developed sophisticated methods to extract sensitive training data from LLMs, bypass safety filters for malicious content generation, and even manipulate AI-driven decision systems for financial gain or sabotage. Indirect prompt injection, where an LLM processes attacker-controlled data embedded in legitimate sources, proved particularly insidious.
- AI Supply Chain Compromise: A single, subtly tampered pre-trained model or dataset, often distributed via reputable open-source repositories, was used to introduce backdoors or vulnerabilities into hundreds, if not thousands, of downstream AI applications across enterprises. This upstream poisoning created a cascading effect, undermining the integrity of entire AI development pipelines.
- Model Evasion and Data Poisoning: Adversaries developed techniques to subtly alter inputs to AI models, causing misclassification or erroneous outputs (model evasion). More critically, training data itself was poisoned, leading to AI models exhibiting malicious biases, making faulty predictions, or even acting as sleeper agents capable of executing commands under specific conditions.
These incidents underscored a critical flaw in the prevailing approach to AI deployment: a significant underestimation of its unique security surface and the integration complexity within existing cloud compute architectures and enterprise IT environments. The rapid pace of AI innovation often outstripped the development of robust security protocols and regulatory compliance frameworks.
Deep Dive: Unpacking the Fault Lines
Trend Micro's report pinpoints several distinct, yet interconnected, fault lines:
- Vulnerabilities in Machine Learning Frameworks: The foundational software libraries (e.g., TensorFlow, PyTorch equivalents) that power AI are complex, often open-source, and subject to continuous evolution. This complexity creates an expansive attack surface for traditional software vulnerabilities (buffer overflows, logic flaws) that can be exploited to gain control over AI models or the underlying infrastructure.
- AI Supply Chain Risks: Unlike traditional software, AI models are often built upon layers of pre-trained models, publicly available datasets, and third-party components. Each link in this chain represents a potential entry point for attackers. A compromise at any stage – from data acquisition and labeling to model development and deployment – can introduce subtle, difficult-to-detect vulnerabilities or backdoors that propagate throughout the ecosystem.
- LLM-Specific Attack Vectors: The interactive nature of LLMs, while transformative, is also their greatest weakness. Prompt injection, data exfiltration through clever conversational manipulation, and even denial-of-service attacks by overwhelming models with resource-intensive prompts have become common. The very flexibility that makes LLMs powerful also makes them susceptible to adversarial control.
- Data Integrity and Governance: The lifeblood of AI is data. Attacks targeting data integrity – data poisoning, adversarial examples, and data leakage during training or inference – directly undermine the reliability and trustworthiness of AI systems. Lax data governance, insufficient anonymization, and inadequate access controls exacerbated these risks.
The convergence of these fault lines paints a grim picture. An enterprise might meticulously secure its network perimeter, only to find its critical AI applications compromised by a poisoned open-source model downloaded by a data scientist, or an LLM chatbot manipulated to reveal proprietary information by a clever social engineering prompt.
Verified Data / Metrics Breakdown
The TrendAI™ State of AI Security Report (H2 2025 findings) highlights a dramatic shift in threat focus and impact:
| Security Domain | H1 2025 Trend | H2 2025 Trend (Reported) | Estimated Enterprise Impact (H2 2025) | Mitigation Challenge |
|---|---|---|---|---|
| AI-Specific Incidents | +15% increase | +180% increase (YoY) | Avg. $3.5M per incident | Lack of specialized tools |
| AI Supply Chain Attacks | Emerging threat | 1 in 3 major breaches linked | Supply chain disruption, IP theft | Trust validation across vendors |
| Prompt Injection Attempts | Low volume | +250% increase (QoQ) | Data exfiltration, system manipulation | Dynamic, context-aware defense |
| Data Poisoning Instances | Rare, academic | Documented in 15% of critical AI deployments | Model bias, erroneous decisions, sabotage | Proactive data hygiene, validation |
| Regulatory Scrutiny on AI | Low to moderate | Significant escalation across G7 | Increased compliance costs | Evolving standards, global divergence |
Industry & Market Implications: Who Wins, Who Loses?
The fallout from these AI fault lines is creating clear winners and losers across global markets, fundamentally reshaping investment strategies and capital allocation.
The Winners:
- Cybersecurity Innovators: Companies specializing in AI security (e.g., Trend Micro, Palo Alto Networks, CrowdStrike) are experiencing unprecedented demand. Their valuation multiples are soaring as enterprises realize that traditional security paradigms are insufficient. Investment in AI TRiSM (Trust, Risk, and Security Management) solutions is becoming a top priority.
- AI Governance & Compliance Consultancies: Firms offering expertise in regulatory compliance for AI, data governance, and ethical AI frameworks are thriving. The imperative to navigate complex, evolving legal landscapes is driving significant spending.
- Resilient Infrastructure Providers: Cloud providers offering hardened AI services with integrated security, robust data integrity checks, and verifiable model provenance are gaining market share. Infrastructure scalability with inherent security features is now a key differentiator.
- Ethical AI Developers: Companies prioritizing "security by design" and "privacy by design" in their AI development lifecycle, even if it entails higher initial costs, will build greater trust and long-term enterprise ROI.
The Losers:
- Unsecured AI Adopters: Enterprises that rush into AI deployment without sufficient security auditing, risk mitigation, and continuous monitoring face devastating financial penalties, reputational damage, and intellectual property theft. Their digital transformation efforts will be severely hampered.
- Open-Source Blind Spots: Organizations relying heavily on unvetted open-source AI models and datasets without robust internal validation processes are inherently exposed. The cost of remediating a compromised model far outweighs the initial "free" benefit.
- Critical Infrastructure & Financial Sector: These sectors, heavily reliant on AI for operational efficiency and market liquidity, are particularly vulnerable. A major AI-driven incident could trigger systemic risks, destabilize markets, or disrupt essential services. The financial sector's investment strategies are now highly sensitive to AI security postures.
- Lack of Regulatory Preparedness: Companies ill-prepared for forthcoming global AI regulations will face hefty fines and competitive disadvantages. The absence of a clear risk mitigation strategy will directly impact their market standing.
The broader economic impact is also palpable. The heightened risk perception is affecting venture capital funding for early-stage AI startups without clear security roadmaps. Insurers are introducing new, more expensive cyber policies specifically for AI risks. The capital allocation shift towards defensive AI security measures is undeniable, potentially slowing the pace of certain types of innovation while accelerating others.
People Also Ask (FAQ)
Q1: What are the primary attack vectors targeting AI systems highlighted in the Trend Micro report?
The TrendAI™ State of AI Security Report for H2 2025 identifies several critical attack vectors. These include sophisticated Prompt Injection (both direct and indirect) aimed at Large Language Models (LLMs) to extract data or manipulate behavior, widespread AI Supply Chain Compromises through poisoned pre-trained models or datasets, Model Evasion techniques that cause AI systems to misclassify or make erroneous decisions, and targeted Data Poisoning attacks designed to corrupt training data and introduce biases or backdoors into AI models. These vectors exploit the unique vulnerabilities of AI's data-driven and model-centric nature, moving beyond traditional network perimeter defenses.
Q2: How can businesses effectively mitigate AI supply chain risks?
Mitigating AI supply chain risks requires a multi-faceted approach. Businesses must implement rigorous vetting processes for all third-party AI components, including pre-trained models, datasets, and development frameworks, extending beyond basic code review to include data provenance and model integrity checks. Establishing a "Software Bill of Materials" (SBOM) equivalent for AI components (an "AI Bill of Materials" or AI-BOM) is crucial for transparency. Additionally, enterprises should employ continuous monitoring of AI models in production for anomalous behavior, leverage secure development lifecycles that incorporate AI-specific security testing, and invest in solutions that offer cryptographic verification of model lineage and data integrity from source to deployment. Robust data governance policies are paramount to ensure the trustworthiness of input data.
Q3: What role will regulation play in addressing AI security fault lines?
Regulation is poised to play a pivotal, and increasingly assertive, role in addressing AI security fault lines. Governments globally, particularly in G7 nations, are accelerating the development of frameworks like the EU AI Act and similar initiatives in the US and Asia. These regulations will likely mandate transparent AI development practices, establish accountability for AI security breaches, require robust risk assessments throughout the AI lifecycle, and enforce strict data governance and privacy standards. The aim is to create a baseline of trust and safety, encouraging secure AI innovation while penalizing negligence. This will significantly impact enterprise ROI calculations for AI projects and necessitate substantial investment in regulatory compliance and AI security auditing, influencing market liquidity and capital allocation in the AI sector.
Q4: What is the potential financial impact of unaddressed AI security incidents on an enterprise?
The financial impact of unaddressed AI security incidents can be catastrophic, extending far beyond the immediate cost of a data breach. Enterprises face direct costs from incident response, remediation, legal fees, and regulatory fines, which can easily run into the tens of millions for a significant event. Indirect costs include severe reputational damage leading to loss of customer trust and market share, reduced enterprise ROI on AI investments due to compromised systems, intellectual property theft impacting valuation multiples, and potential market liquidity issues if core AI-driven operations are disrupted. Furthermore, the cost of capital allocation will increase as boards demand greater investment in cyber resilience, potentially hindering other strategic initiatives. The TrendAI™ report's average estimated $3.5M per incident only scratches the surface of the full economic fallout.
Future Outlook: Navigating the AI Security Imperative
The findings of the TrendAI™ report are a clarion call. The future of AI innovation hinges not merely on technological advancement but on the establishment of a robust, secure, and trustworthy ecosystem. We anticipate several critical developments in the immediate future:
- Rise of AI-Native Security Solutions: A new generation of cybersecurity tools specifically designed to detect and defend against AI-specific threats (e.g., adversarial attacks, prompt injections, model manipulation) will become mainstream.
- Consolidated AI Governance Frameworks: Industry-specific and international standards for AI security, ethical AI, and data governance will begin to crystallize, driving increased regulatory compliance requirements across all sectors.
- Investment in Human Capital: A severe shortage of AI security experts will lead to aggressive recruitment and training initiatives, with specialized AI security engineers becoming one of the most in-demand roles in technology.
- Collaborative Defense Mechanisms: Information sharing between industry, academia, and government will become more formalized and critical for tracking and responding to rapidly evolving AI-driven threats.
- Proactive Resilience over Reactive Defense: Organizations will shift from solely reactive incident response to proactive cyber resilience strategies, embedding security at every stage of the AI lifecycle from design to deployment.
The coming years will be defined by an arms race between those who seek to exploit AI and those committed to securing it. The fault lines in the AI ecosystem are exposed, but the opportunity to rebuild with stronger foundations remains. For global businesses, financial institutions, and governments, the imperative is clear: invest in comprehensive AI security, foster robust governance, and cultivate a culture of cyber resilience. The alternative is an AI future fraught with risk, where groundbreaking innovation is perpetually undermined by systemic vulnerabilities.