Executive Takeaways
- Escalating Enterprise Threat Vectors: The 29th Edition of the Cyber Security Summit SA convenes at a critical juncture, as South African corporations face unprecedented ransomware sophistication and cross-border cyber espionage.
- phasisedCapital Allocation Shift: C-suite executives are pivoting from reactive IT security spending to strategic, preventative infrastructure scalability and quantified risk mitigation.
- Regulatory Pressures Mount: Implementation of stricter compliance mandates forces boards to integrate cyber-resilience frameworks directly into enterprise valuation multiples.
- Blueprint for Survival: Through rigorous case studies like "Building Cyber-Resilient Enterprises in South Africa," industry leaders are redefining modern cloud compute architecture and third-party vendor governance.
JOHANNESBURG — In the high-stakes corridors of global finance and corporate governance, digital vulnerability is no longer classified as a back-office IT glitch; it is an existential threat to market liquidity and enterprise valuation. As the 29th Edition of the Cyber Security Summit SA gathers momentum, industry titans, risk officers, and cybersecurity pioneers have converged to confront a sobering reality: South Africa remains one of the primary targets for sophisticated cybercriminal syndicates operating across emerging and developed markets.
Drawing on exhaustive reporting from primary wire sources including CIO Africa, this investigation unpacks the underlying catalysts, technical architectures, and financial implications driving the 29th iteration of this landmark summit. With enterprise ROI hanging in the balance, market participants are being forced to rethink their entire security posture.
The Catalytic Shift: Why the 29th Summit Matters Now
Test Our Free AI & Tech Utilities Suite
Calculate LLM API token costs, analyze article dwell-time, or simulate tech DCA returns.
The timing of the 29th Cyber Security Summit SA is far from coincidental. Over the past twenty-four months, South Africa’s financial services, telecommunications, and logistics sectors have sustained a barrage of calculated cyber attacks. Ransomware-as-a-Service (RaaS) operations, supply chain compromises, and insider threats have exposed deep vulnerabilities in legacy cloud compute architecture.
According to preliminary insights released at the summit, the average cost of a data breach for South African enterprises has surged past previous historical baselines. This financial hemorrhaging has forced boards of directors to elevate cybersecurity from an operational line item to a core pillar of corporate governance. Capital allocation is undergoing a seismic shift. Chief Information Security Officers (CISOs) are no longer begging for budgets; they are being tasked with proving how every dollar spent translates directly into risk mitigation and operational continuity.
Case Study Spotlight: Building Cyber-Resilient Enterprises in South Africa
At the heart of the summit’s agenda sits a flagship case study session: "Building Cyber-Resilient Enterprises in South Africa." This analytical deep-dive serves as a masterclass in modern defense strategy, dissecting how domestic conglomerates and multinational subsidiaries operating within the region can engineer fail-safes into their digital ecosystems.
Analysts note that the case study focuses heavily on three critical vectors:
- Zero-Trust Architecture (ZTA): Moving away from perimeter-based defense models toward continuous verification of every user and device attempting to access corporate resources.
- Third-Party Risk Management: Securing extended supply chains where vendors and external contractors often represent the weakest link in corporate infrastructure.
- Incident Response Agility: Implementing automated threat-hunting tools and immutable backup systems to neutralize ransomware deployments before data exfiltration occurs.
Verified Data & Metrics Breakdown
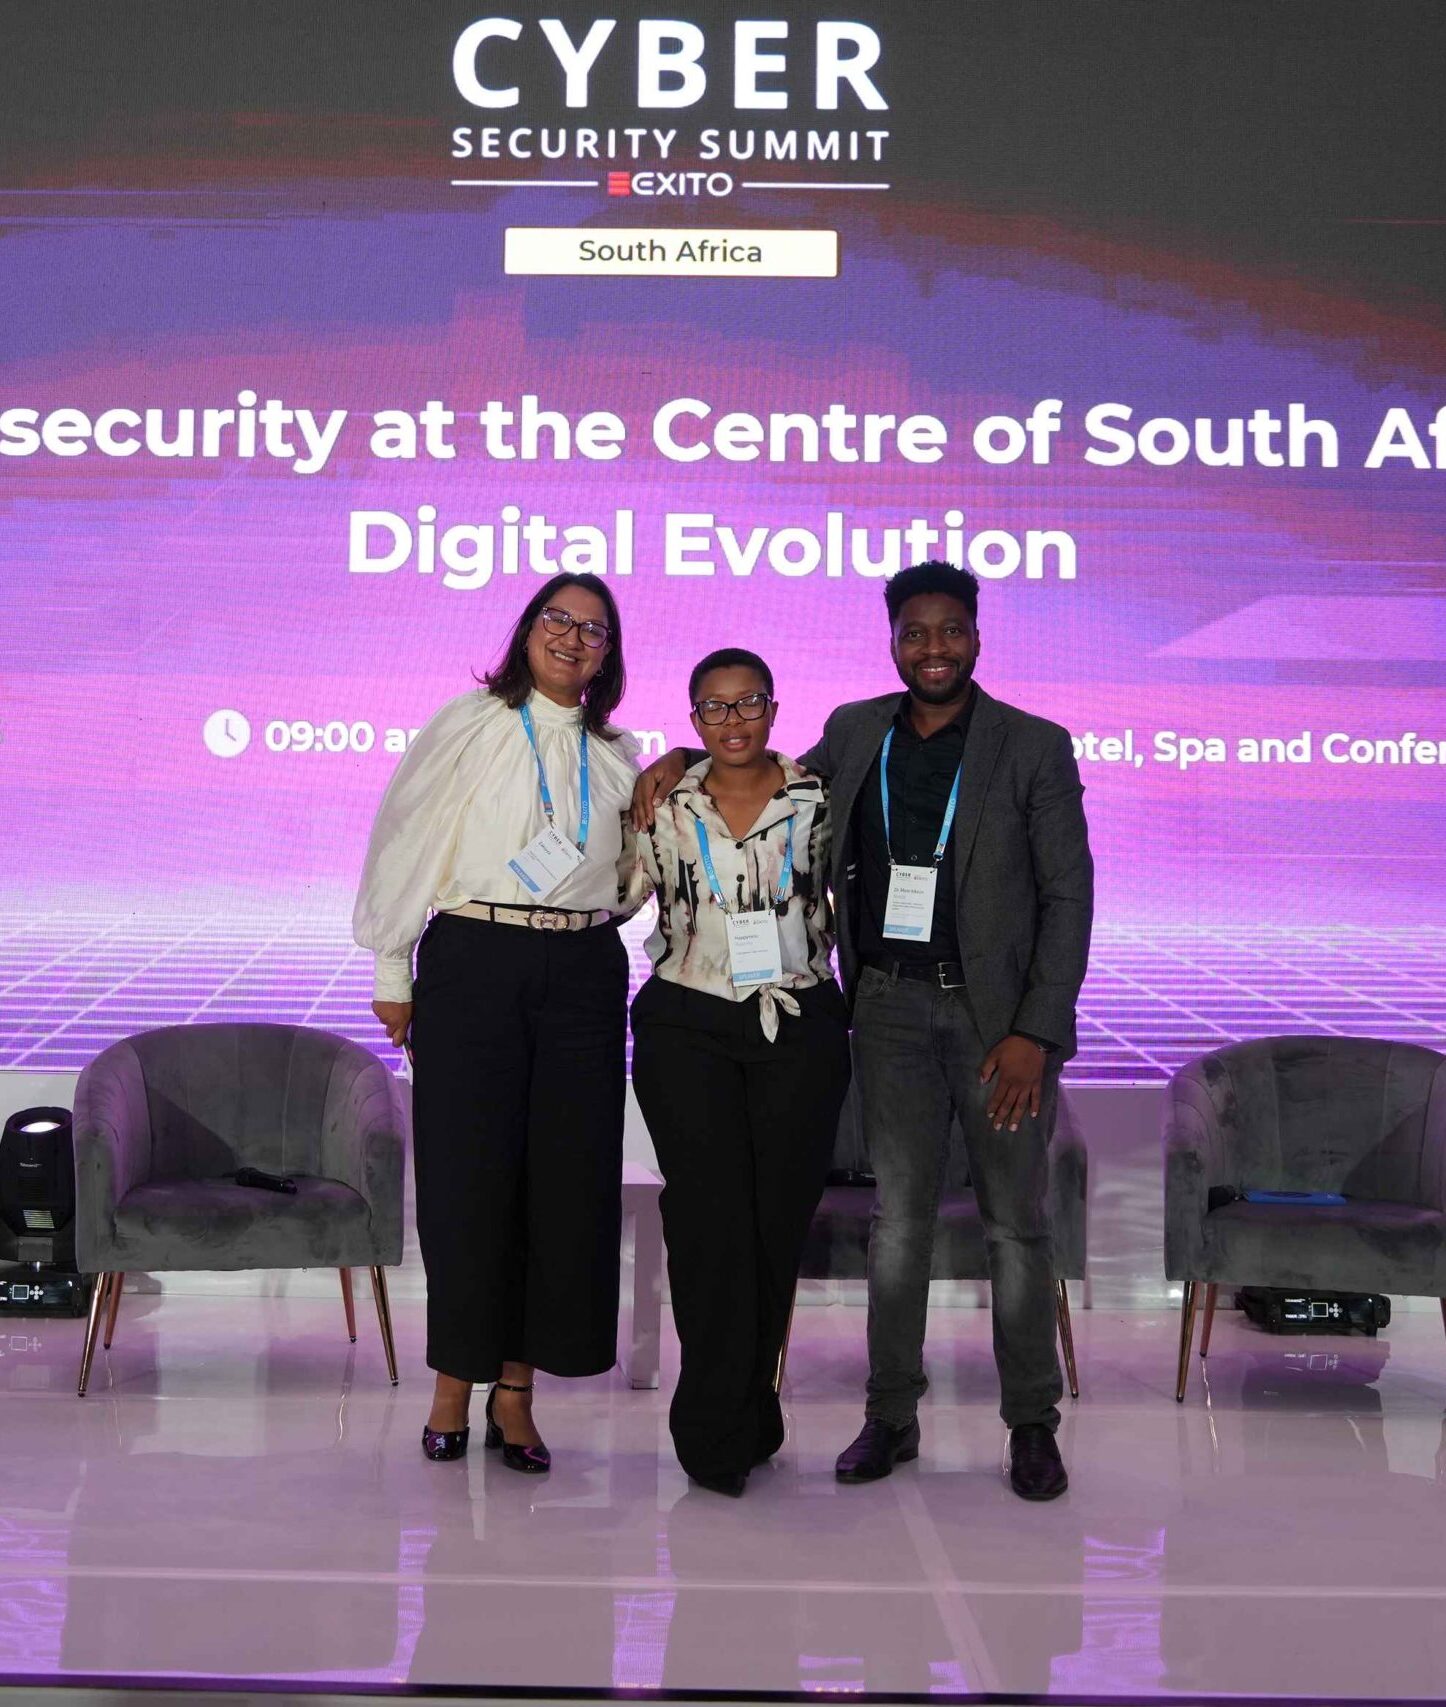
To understand the economic gravity of the discussions at the 29th Cyber Security Summit SA, one must examine the macro-level indicators defining the South African cybersecurity landscape.
| Metric / Indicator | Current Market Baseline | Strategic Implication |
|---|---|---|
| Average Enterprise Breach Cost | Multi-million Rand impact per incident | Direct erosion of quarterly net margins and equity valuation. |
| Regulatory Compliance Pressure | POPIA & international standards enforcement | Non-compliance leads to severe statutory fines and reputational damage. |
| Cloud Migration Vulnerability | ~65% of firms accelerating hybrid cloud adoption | Increased attack surface requiring automated posture management. |
| Skills Shortage Gap | Critical deficit in certified tier-1 SOC analysts | Forces reliance on Managed Detection and Response (MDR) partners. |
Industry & Market Implications: Winners and Losers
The macroeconomic ramifications of the strategies discussed at the summit will profoundly reshape the South African corporate landscape over the next three to five years.
The Winners: Forward-thinking enterprises that embrace integrated security orchestration, automated response platforms, and rigorous employee training programs will capture market share. Specialized cybersecurity vendors, managed security service providers (MSSPs), and cloud-native architects stand to experience exponential revenue growth as corporate clients aggressively upgrade their digital defenses.
The Losers: Laggards, legacy-bound institutions, and firms treating cybersecurity as an administrative afterthought face severe existential risks. Regulatory penalties, catastrophic data leaks, and plummeting investor confidence will depress valuation multiples for unprepared organizations. In a hyper-connected global economy, a single compromised endpoint can trigger a catastrophic loss of institutional trust.
Frequently Asked Questions (People Also Ask)
What is the primary focus of the 29th Cyber Security Summit SA?
The summit centers on building robust enterprise resilience, examining advanced threat vectors, mitigating ransomware risks, and navigating complex regulatory compliance frameworks within the South African and broader African digital economy.
Why are South African enterprises facing heightened cyber threats?
Rapid digital transformation, accelerated cloud adoption, and legacy infrastructure upgrades have expanded the corporate attack surface. Simultaneously, well-funded cybercriminal syndicates increasingly target emerging markets perceived to have gaps in incident response capabilities.
How does the summit address enterprise ROI on cybersecurity?
Industry leaders and financial analysts at the conference evaluate security spending not as a cost center, but as an essential risk-mitigation strategy that protects equity valuation, avoids regulatory fines, and preserves business continuity.
What role do case studies like "Building Cyber-Resilient Enterprises" play?
These sessions provide actionable, real-world blueprints derived from actual security incidents, offering CISOs and executive boards proven methodologies for deploying zero-trust frameworks and hardening supply chain security.
Future Outlook: What Comes Next
As the curtains close on the 29th Edition of the Cyber Security Summit SA, the trajectory for the region's digital ecosystem is clear. The convergence of artificial intelligence in both cyber attacks and defense mechanisms means that speed and automation will dictate market survival. Over the next twelve months, watch for stricter enforcement of data protection laws, increased consolidation among enterprise security vendors, and a mandatory cultural shift where boardrooms treat digital hygiene with the same rigor as financial auditing.
For South African enterprises, the message emanating from Johannesburg is unequivocal: resilience is no longer an optional luxury; it is the ultimate prerequisite for doing business in the twenty-first century.