WASHINGTON — In the hyper-connected architecture of modern global commerce and national security, the physical and digital worlds have converged into a singular, volatile attack surface. Five hours ago, primary intelligence disclosures via CyberSecurityNews revealed an unprecedented cyber espionage campaign orchestrated by the elite state-sponsored Chinese threat actor known as Volt Typhoon. Utilizing an obscured, highly localized telecommunications and operational technology backbone colloquially dubbed the "Silent Train" network, these operators bypassed perimeter defenses to execute zero-day exploits against United States federal agencies, premier defense contractors, and critical infrastructure operators.
For months, chief risk officers, compliance directors, and capital allocators across the defense and technology sectors have modeled risk around traditional cloud compute vectors and perimeter firewalls. However, this revelation upends foundational assumptions regarding enterprise ROI on cybersecurity spend. By weaponizing subterranean logistics and transit data channels—traditionally sequestered from mainstream enterprise monitoring—state-backed actors have established a resilient, low-signature conduit for kinetic-digital reconnaissance and lateral movement.
This investigative report breaks down the anatomy of the Silent Train intrusion vector, examines the economic and geopolitical fallout for institutional stakeholders, and evaluates the mandatory shifts in capital allocation required for enterprise risk mitigation.
Executive Takeaways
Test Our Free AI & Tech Utilities Suite
Calculate LLM API token costs, analyze article dwell-time, or simulate tech DCA returns.
- Asymmetric Ingress: Volt Typhoon bypassed conventional perimeter defenses by tunneling through the "Silent Train" network, an isolated operational technology (OT) and transit communications grid.
- Target Saturation: The multi-vector campaign targeted high-value U.S. government agencies, tier-1 defense prime contractors, and critical infrastructure sub-sectors, deploying previously unknown zero-day vulnerabilities.
- Capital Allocation Paradigm Shift: Enterprise risk mitigation strategies must immediately pivot from IT-centric perimeter defense to holistic convergence of OT security, regulatory compliance, and supply chain visibility.
- Market Liquidity & Valuation Impacts: Defense technology valuation multiples face downward repricing pressures as institutional investors demand rigorous audit trails for underlying supply chain and logistics IT dependencies.
The Anatomy of the "Silent Train" Infiltration
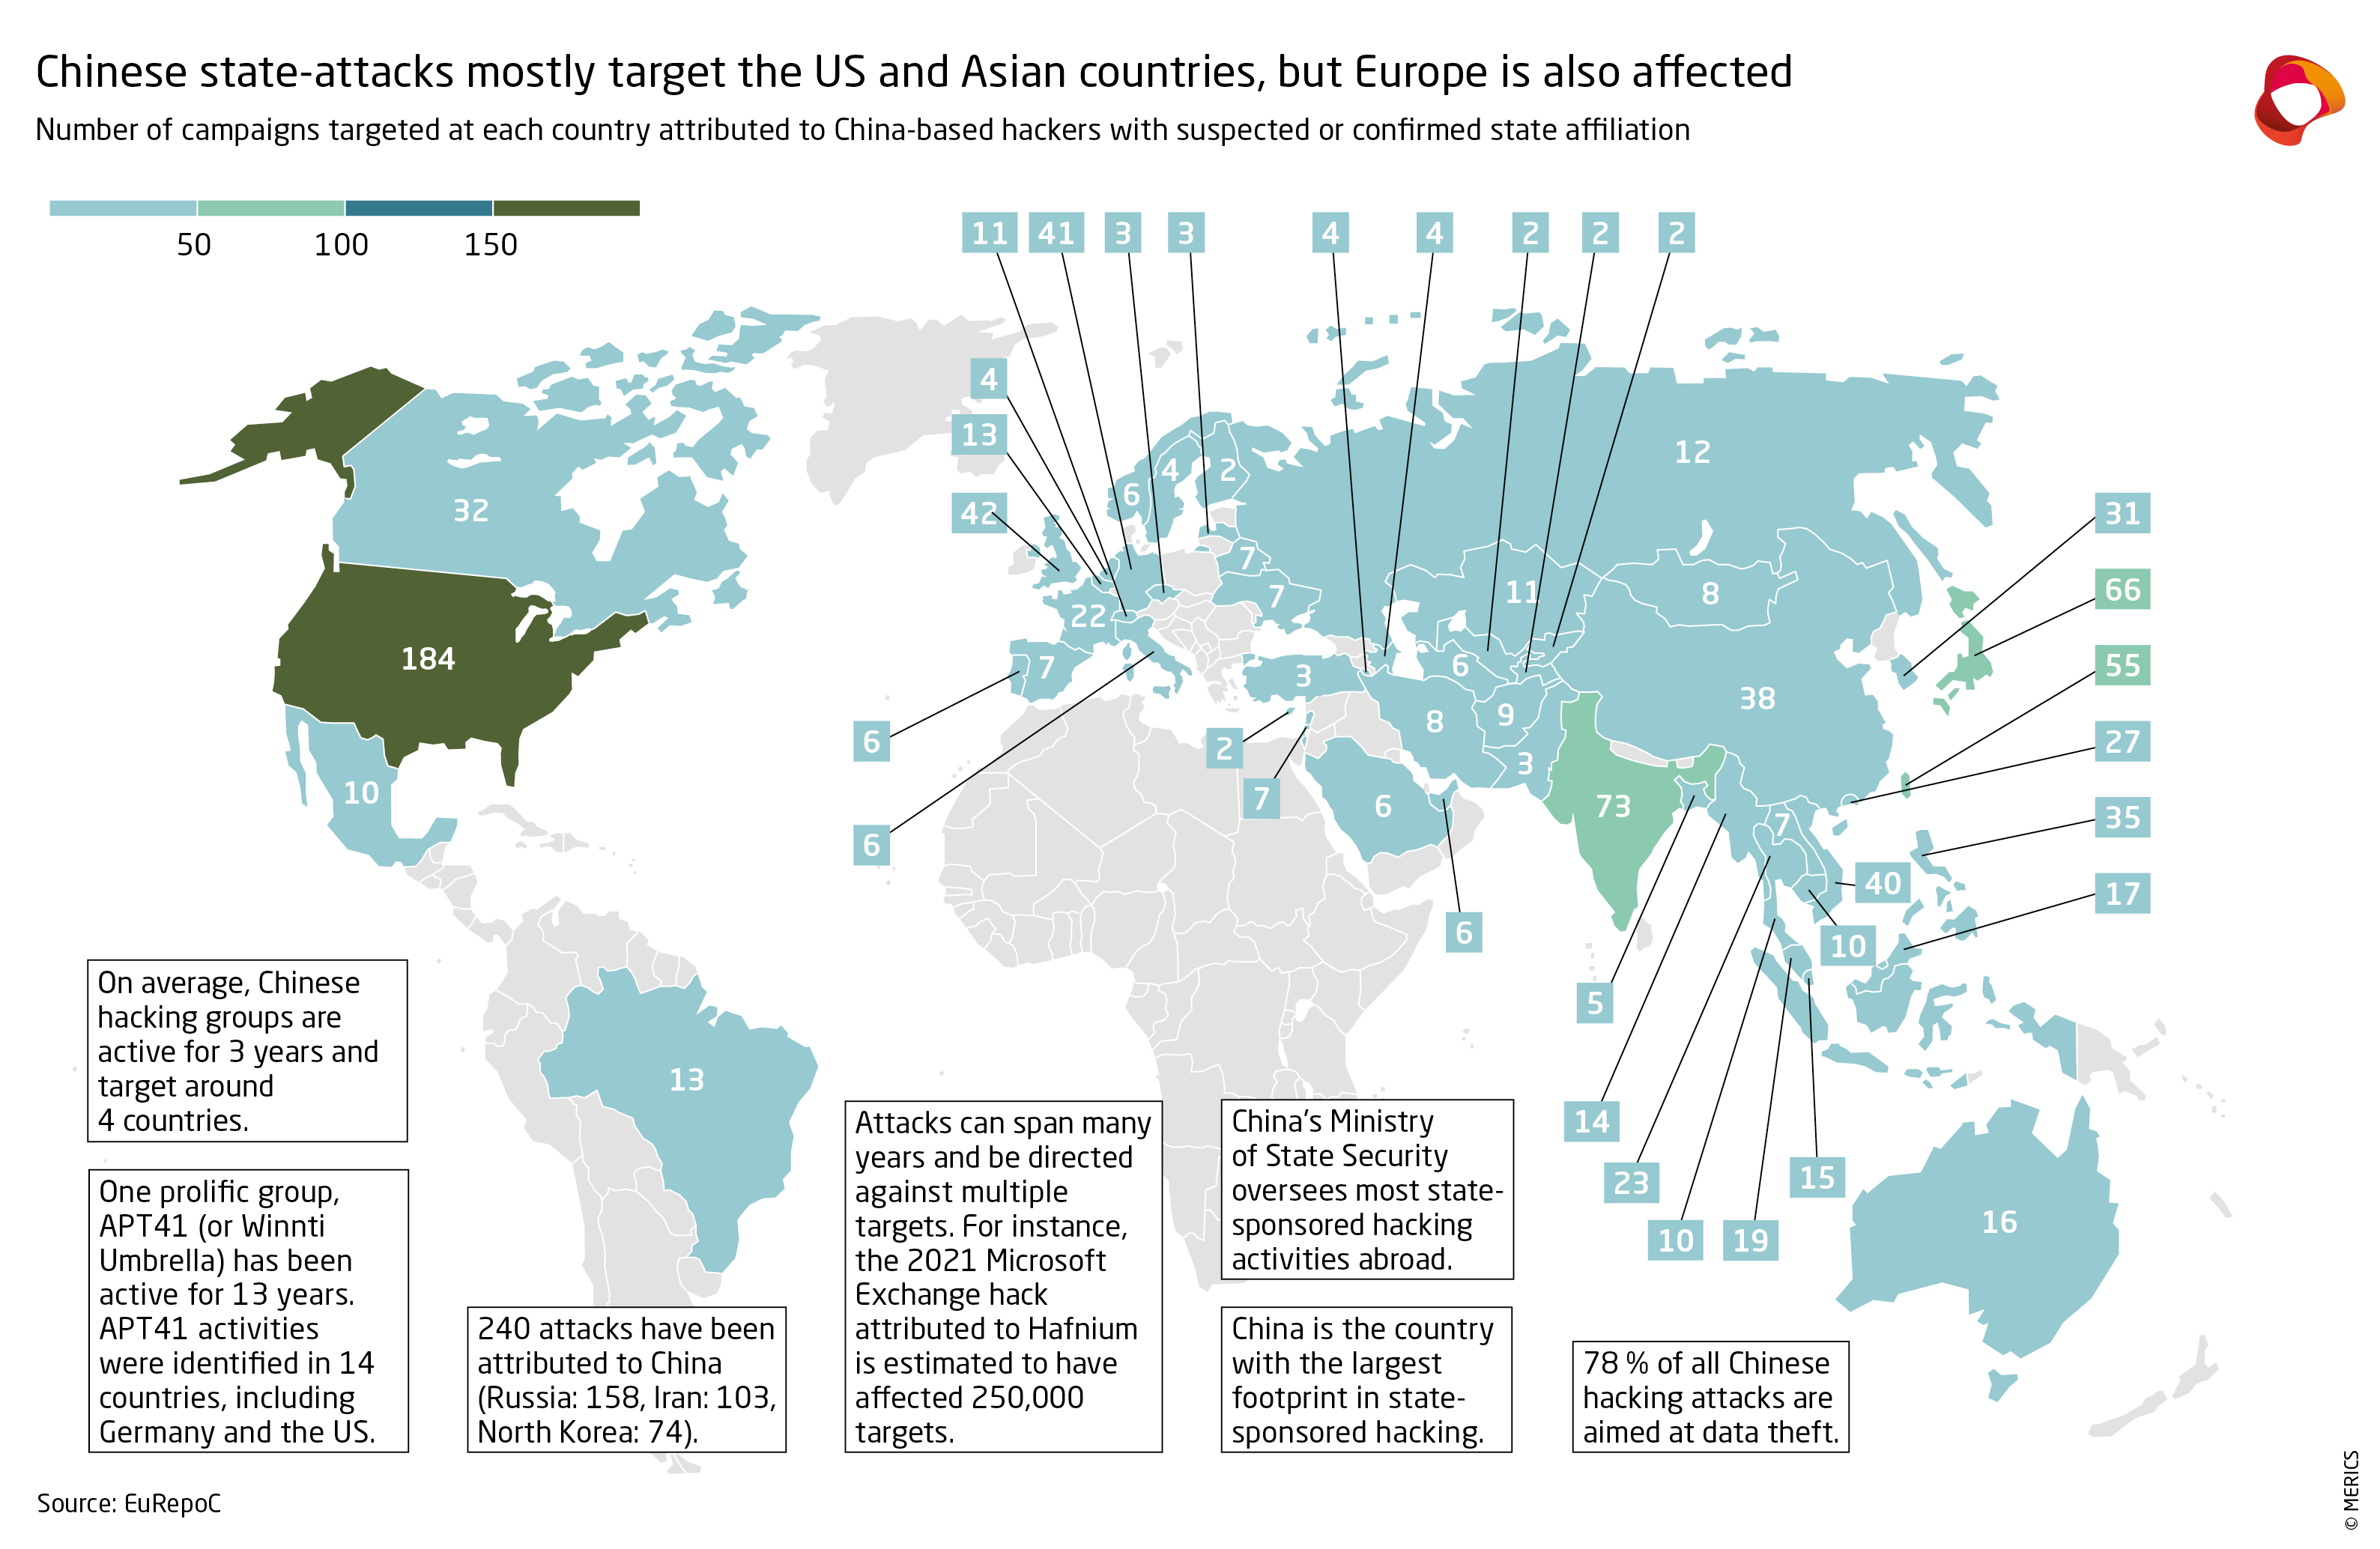
To understand the mechanics of the recent Volt Typhoon campaign, security architects must examine the convergence of administrative rail networks and critical defense logistics. The "Silent Train" network is not a single fiber-optic line, but rather a complex, proprietary web of wayside signaling systems, closed-loop communications, and municipal transit data exchanges designed to optimize high-speed rail and freight logistics across strategic corridors.
Historically, these operational technology networks were protected by a linguistic and structural "air gap"—isolated from the public internet and managed by legacy firmware. However, as infrastructure scalability initiatives mandated the digitization of supply chains, these rail networks were increasingly connected to enterprise resource planning (ERP) clouds and third-party logistics vendors. Volt Typhoon capitalized on this integration friction.
By compromising peripheral municipal contractors and secondary supply chain vendors who possessed administrative credentials to the transit grid, the threat actors established persistent footholds. From these internal positions, they executed living-off-the-land (LotL) techniques, utilizing native administrative tools like PowerShell, WMI, and legitimate network management protocols to blend in with baseline traffic. This effectively neutralized commercial endpoint detection and response (EDR) solutions that rely on behavioral anomaly detection.
Exploiting Zero-Day Vulnerabilities in Transit Gateways
The tactical breakthrough occurred when the attackers deployed zero-day exploits targeting proprietary gateway devices manufactured by prominent industrial automation vendors. These gateways, positioned at the intersection of enterprise IT environments and transit OT grids, lacked modern telemetry capabilities. Consequently, traffic traversing the Silent Train backbone remained blind to federal sensors.
Once inside the target environment, Volt Typhoon operators harvested credentials with elevated privileges, mapping active directory structures belonging to federal logistics agencies and defense subcontractors. The intent was not immediate disruption or ransomware monetization; rather, the campaign exhibited classic hallmarks of strategic reconnaissance and long-term positioning—establishing deep, dormant access capable of facilitating espionage or future infrastructure degradation during a geopolitical crisis.
Verified Data & Metrics Breakdown
A quantitative evaluation of the campaign highlights the systemic scale and operational breadth of the intrusion vector:
| Metric / Parameter | Pre-Incident Benchmark | Post-Incident Impact / Reality | Strategic Implications |
|---|---|---|---|
| Primary Attack Vector | Traditional Cloud & Perimeter Firewalls | Sub-surface Transit OT ("Silent Train" Network) | Mandates immediate OT/IT convergence auditing. |
| Primary Threat Actor | Volt Typhoon (State-Sponsored APT) | Advanced Persistent Threat with Living-off-the-Land focus | Elevates threat profile from cybercrime to geopolitical risk. |
| Primary Targets | Public-facing SaaS applications | U.S. Federal Agencies & Defense Prime Contractors | Triggers stringent CMMC and federal compliance reviews. |
| Detection Timeframe | Average 14 to 30 days (Industry standard) | Months of undetected lateral movement | Highlights critical visibility gaps in supply chain logistics. |
Industry & Market Implications: Winners, Losers, and Economic Fallout
The exposure of the Silent Train vulnerability sends shockwaves through global financial markets, directly influencing capital allocation, valuation multiples, and regulatory compliance frameworks across the defense and technology sectors.
Defense Primes and Enterprise Risk Mitigation
Major defense contractors face an immediate reckoning regarding their supply chain security postures. Institutional investors and asset managers are reassessing valuation multiples for firms with heavy exposure to legacy logistics infrastructure. Companies that fail to demonstrate end-to-end visibility across both their corporate IT networks and embedded OT systems risk capital flight and punitive valuation markdowns.
Conversely, specialized cybersecurity vendors focusing on OT-IT network convergence, automated asset discovery, and supply chain risk intelligence stand to capture significant market share. Enterprise ROI on security spend will increasingly favor solutions that bridge the visibility gap between corporate boardrooms and physical transit or manufacturing floors.
Regulatory Compliance and Government Oversight
In Washington, Capitol Hill lawmakers and intelligence committees are preparing aggressive legislative responses. The Cybersecurity Maturity Model Certification (CMMC) framework, long debated by defense suppliers, is poised for accelerated enforcement with heightened emphasis on third-party logistical dependencies. Federal agencies will likely institute mandatory continuous monitoring clauses for all vendors operating near critical infrastructure nodes, increasing administrative and technological overhead for mid-tier defense suppliers.
Frequently Asked Questions (People Also Ask)
What is the "Silent Train" network, and how was it used in the cyberattacks?
The "Silent Train" network refers to the obscured operational technology (OT) and communications infrastructure underpinning municipal rail systems and transit logistics. Volt Typhoon exploited this network because it often bridges the physical transit grid with corporate supply chain vendors, offering an unmonitored backdoor into high-value defense and government targets.
Who is Volt Typhoon, and what are their primary objectives?
Volt Typhoon is a state-sponsored cyber espionage group linked to the People's Republic of China. Unlike financially motivated ransomware groups, Volt Typhoon focuses on long-term persistence, reconnaissance, and pre-positioning within critical infrastructure and defense networks to gather intelligence and potentially disrupt operations during geopolitical crises.
How did the hackers bypass advanced endpoint detection and response (EDR) tools?
The attackers utilized "living-off-the-land" (LotL) techniques, leveraging native administrative utilities, legitimate system scripts, and valid credentials already present within the compromised networks. This approach allows malicious activity to blend in with normal administrative traffic, evading signature-based EDR alerts.
What steps should enterprise and defense organizations take to mitigate this risk?
Organizations must immediately audit their OT-IT convergence points, enforce strict network segmentation between corporate enterprise environments and physical logistics grids, deploy advanced behavioral anomaly detection across transit gateways, and vet the cybersecurity postures of all third-party supply chain vendors.
Future Outlook & Strategic Milestones
As state-sponsored espionage operations evolve, the boundary between physical infrastructure and digital security has permanently dissolved. The weaponization of transit networks like the Silent Train paradigm signals a permanent shift in advanced persistent threat methodologies. Over the next twelve to eighteen months, market participants must monitor several key milestones:
- Regulatory Enforcement: The rollout of stringent CMMC mandates and Department of Defense guidelines addressing OT supply chain security.
- Technology Convergence: Increased merger and acquisition (M&A) activity as cybersecurity giants acquire specialized OT monitoring startups to capture enterprise market share.
- Geopolitical Escalation: Heightened attribution and retaliatory diplomatic measures from Western intelligence alliances aimed at disrupting state-backed infrastructure pre-positioning.
For executive leadership, the mandate is clear: passive compliance is no longer a viable shield. Protecting enterprise value and national security requires an aggressive, holistic reimagining of risk mitigation that accounts for every hidden track in the global supply chain.