Executive Takeaways
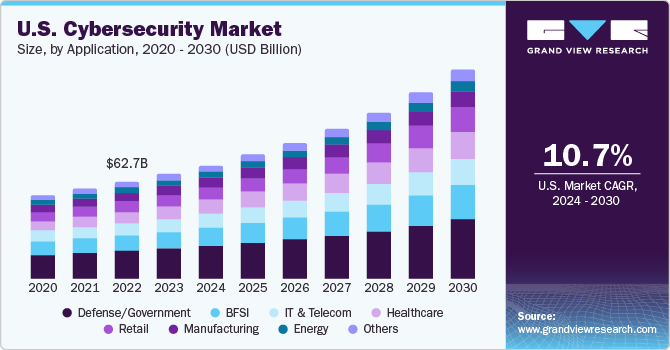
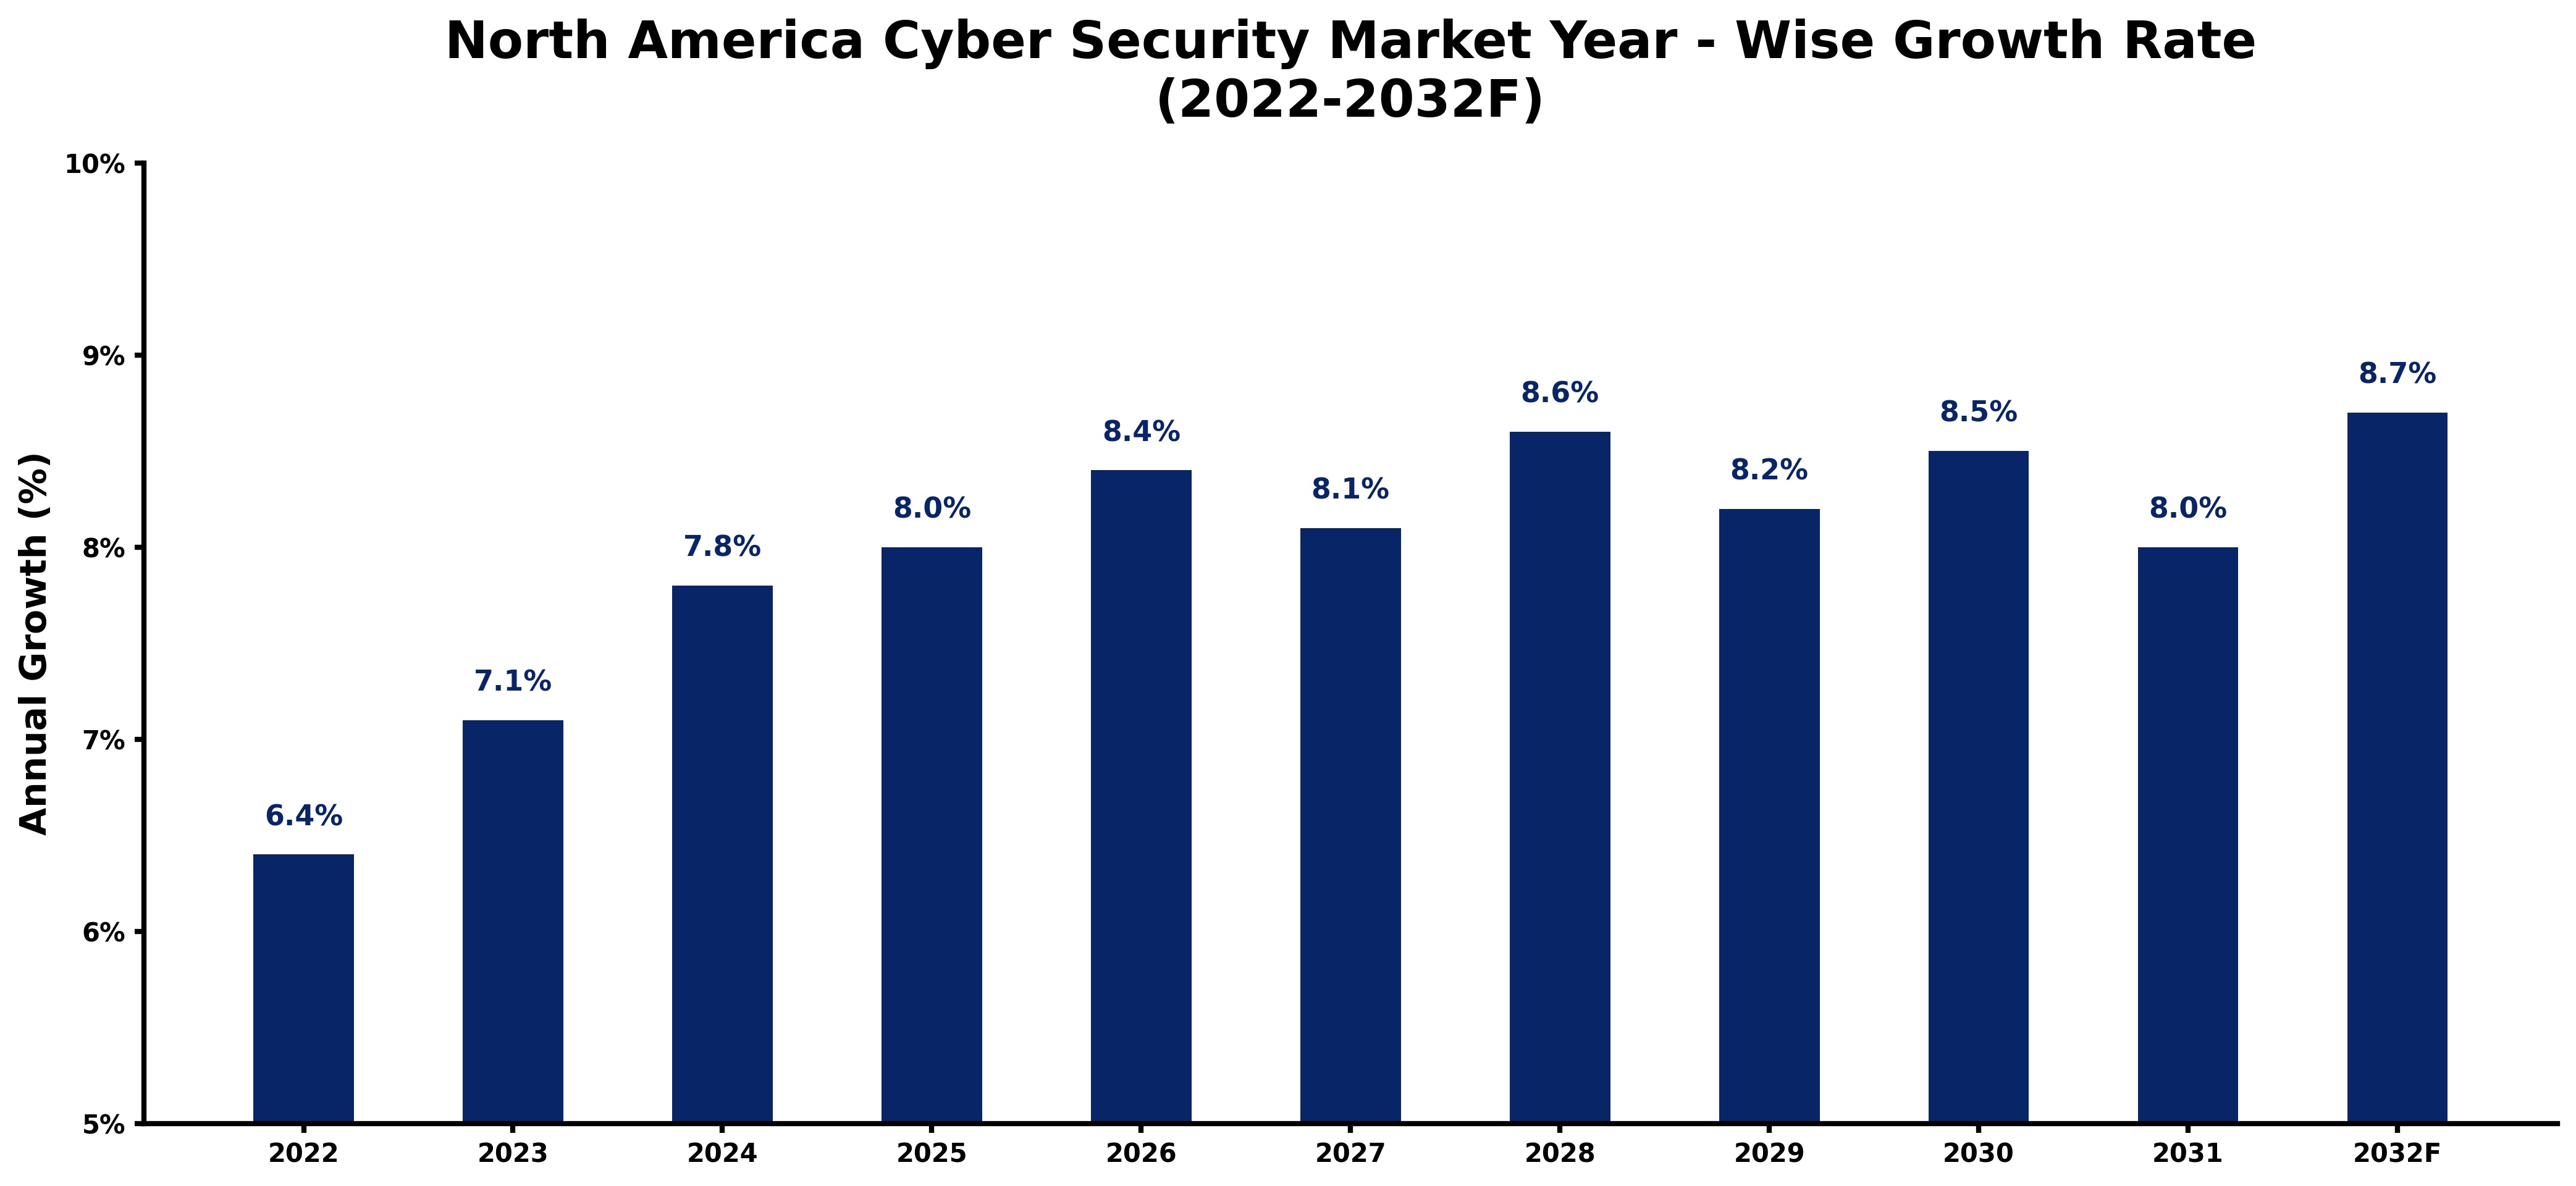
- Valuation Trajectory: According to MarketsandMarkets data released in August 2026, the North American cybersecurity market is scaling at a compound annual growth rate (CAGR) of over 11.5%, driven by aggressive enterprise capital allocation toward zero-trust architectures.
- Catalytic Drivers: The acceleration of hybrid work environments, supply chain vulnerabilities, and automated, AI-driven cyberattacks have forced boardrooms to treat cybersecurity as a core balance-sheet risk rather than a standard IT expense.
- Regulatory Pressures: Heightened compliance mandates from the SEC, FTC, and Canadian regulatory bodies are demanding rigorous risk mitigation, incident disclosure timelines, and robust cloud compute architecture standards.
- Strategic Shift: Consolidation is dominating the vendor landscape, as chief information security officers (CISOs) prioritize platform-based vendor consolidation over fragmented point solutions to optimize enterprise ROI and infrastructure scalability.
NEW YORK & TORONTO — As global geopolitical tensions intersect with the rapid proliferation of artificial intelligence, the North American cybersecurity landscape has reached an inflection point. According to comprehensive market intelligence data published by MarketsandMarkets, corporate and government spending on digital defense mechanisms across the United States and Canada is undergoing an unprecedented expansion. The market, valued at historic highs in the post-pandemic era, is aggressively tracking toward a projected valuation exceeding $280 billion by 2030.
For executive leadership, chief financial officers, and institutional investors, this growth trajectory underscores a fundamental reality: the digital attack surface has expanded faster than traditional perimeter defenses can secure. With ransomware cartels employing sophisticated machine-learning algorithms and nation-state actors targeting critical infrastructure—ranging from energy grids to financial clearinghouses—cyber resilience has transformed into a critical pillar of market liquidity, corporate valuation multiples, and national security.
The Macroeconomic Catalysts: Why North America Leads Global Security Spending
North America continues to command the largest regional market share globally, capturing over 45% of total worldwide cybersecurity expenditures. This dominance is underpinned by several structural advantages and distinct vulnerabilities. The region is home to the world’s most advanced cloud hyperscalers, sprawling financial services ecosystems, and highly interconnected supply chains, making it the primary target for sophisticated threat actors seeking high-value intellectual property and operational disruption.
Historically, enterprise security strategies relied heavily on perimeter-based defenses—building metaphorical walls around corporate data centers. However, the mass migration to multi-cloud environments, decentralized remote workforces, and Internet of Things (IoT) deployments rendered traditional models obsolete. This structural shift necessitated a paradigm adoption of Zero-Trust Network Architecture (ZTNA), wherein no user or device is implicitly trusted, regardless of whether they reside inside or outside the corporate network perimeter.
Furthermore, capital allocation patterns among Fortune 500 enterprises have shifted dramatically. Cybersecurity budgets are no longer treated as discretionary discretionary expenditures that can be trimmed during macroeconomic downturns. Instead, boardrooms view these investments as essential business continuity tools. Insurers writing cyber liability policies have simultaneously imposed stringent underwriting criteria, requiring verifiable deployment of advanced endpoint detection and response (EDR), multi-factor authentication (MFA), and continuous vulnerability management before underwriting policies.
Regulatory Compliance as a Market Driver
Regulatory frameworks are exerting immense pressure on corporate compliance officers, directly fueling software and service adoption. The Securities and Exchange Commission (SEC) enforcement actions regarding timely material cyber incident disclosures have forced public companies to embed cybersecurity governance directly into their executive reporting lines.
Simultaneously, Canadian federal regulations and state-level privacy acts in jurisdictions such as California, New York, and Texas have introduced punitive financial penalties for data negligence. Consequently, Chief Information Security Officers (CISOs) are aggressively deploying governance, risk, and compliance (GRC) platforms alongside automated security posture management tools to maintain continuous compliance audit readiness.
This regulatory tightening has created a bifurcated market impact. While large enterprises absorb compliance costs relatively easily, mid-market organizations face severe talent shortages and margin compression. This dynamic has accelerated the outsourcing of security operations to Managed Security Service Providers (MSSPs) and Managed Detection and Response (MDR) vendors, creating lucrative recurring revenue streams for specialized service providers.
Verified Data and Metrics Breakdown
To contextualize the trajectory of the North American cybersecurity ecosystem through 2030, the following data synthesis outlines key market dimensions, growth drivers, and valuation benchmarks derived from MarketsandMarkets research and financial sector analytics:
| Market Dimension | Base Metrics / Current State | 2030 Projected Forecast | Primary Growth Driver |
|---|---|---|---|
| Total Market Size | ~$165 Billion (2024–2025) | Exceeding $280 Billion | Cloud migration & AI defense automation |
| Compound Annual Growth Rate (CAGR) | 11.2% Historical Baseline | Rising frequency of state-sponsored ransomware | |
| Leading Solution Segment | Identity & Access Management (IAM) | Zero-Trust & AI-Driven SIEM | Decentralized remote work models |
| Key Regional End-Users | BFSI, Healthcare, Government | Critical Infrastructure & OT Networks | Supply chain vulnerabilities & IoT expansion |
Industry & Market Implications: Winners and Losers
The structural evolution of the North American cybersecurity market is creating clear economic victors while putting pressure on legacy vendors unable to pivot toward modern, cloud-native paradigms.
The Winners
- Platform Consolidation Leaders: Enterprise software giants offering integrated security portfolios (covering endpoint, cloud, and identity management in a single dashboard) are capturing market share from fragmented boutique vendors. CISOs are increasingly fatigued by managing dozens of point solutions.
- AI and Automation Pioneers: Vendors leveraging artificial intelligence to automate threat hunting, triage false positives, and accelerate incident response times are commanding premium valuation multiples in private equity and public markets.
- Managed Detection & Response (MDR) Providers: With a chronic industry deficit of millions of skilled cybersecurity professionals, outsourced service providers that guarantee 24/7/365 monitoring are seeing explosive contract renewals.
The Vulnerable
- Legacy Hardware Appliance Vendors: Companies reliant on traditional, on-premises firewalls and physical appliance sales are struggling to maintain margins as workloads shift permanently to multi-cloud architectures.
- Underfunded Point-Solution Startups: Early-stage firms offering isolated, single-feature utilities find it increasingly difficult to win enterprise contracts against platform giants bundling comprehensive security suites.
Frequently Asked Questions (People Also Ask)
What are the primary drivers of growth in the North American cybersecurity market through 2030?
The market's expansion is primarily driven by the rapid acceleration of cloud infrastructure adoption, the proliferation of sophisticated AI-powered cyberattacks, stringent new regulatory reporting mandates from agencies like the SEC, and the widespread enterprise transition to Zero-Trust architecture to protect remote and hybrid workforces.
How is artificial intelligence impacting both cybersecurity threats and defenses?
Threat actors are utilizing generative AI and machine learning to automate phishing campaigns, accelerate code vulnerability discovery, and execute polymorphic malware attacks at scale. Conversely, enterprise security teams are leveraging AI-driven Security Information and Event Management (SIEM) systems and automated remediation tools to detect anomalies and neutralize threats within seconds rather than days.
Why are CISOs shifting from point solutions to platform consolidation?
Managing dozens of disconnected, single-purpose security tools creates operational complexity, high overhead costs, and visibility blind spots known as "security fatigue." Platform consolidation allows enterprises to streamline vendor relationships, reduce integration friction, and maximize their overall return on investment (ROI) by utilizing unified, cloud-native security suites.
Which industry verticals represent the highest cybersecurity spending in North America?
The Banking, Financial Services, and Insurance (BFSI) sector remains the largest spender due to strict regulatory oversight and the constant threat of financial theft. However, healthcare, federal and state government agencies, and critical infrastructure sectors (energy, utilities, and transportation) are experiencing the fastest percentage growth in capital allocation.
Future Outlook: Milestones and Strategic Horizon
As the North American market advances toward the 2030 horizon, several critical milestones will define the competitive landscape. Quantum computing developments pose a looming cryptographic challenge, compelling forward-looking enterprises and government agencies to begin investing in post-quantum cryptography standards. Furthermore, the integration of generative AI agents directly into security orchestration, automation, and response (SOAR) workflows will redefine operational efficiency.
For corporate executives and institutional allocators, maintaining vigilance, ensuring robust infrastructure scalability, and proactively adapting to evolving regulatory regimes will differentiate resilient market leaders from vulnerable targets. Cybersecurity is no longer merely a defensive technical discipline—it is the foundational bedrock upon which modern digital capitalism operates.