The modern battleground of geopolitical finance is no longer fought exclusively in central bank boardrooms or currency trading pits. It is waged across pixelated screens, fraudulent corporate identities, and meticulously engineered social networks. In one of the most audacious cyber-espionage campaigns in financial history, state-backed operatives from North Korea systematically infiltrated the digital infrastructure of major cryptocurrency enterprises—culminating in an estimated $6.3 billion heist facilitated by a Trojan horse disguised as an employment opportunity on LinkedIn.
According to classified intelligence briefings and proprietary cybersecurity disclosures reviewed by this publication, the breach vector relied heavily on exploiting human capital rather than cryptographic algorithms. By leveraging fake job interviews, high-compensation enticements, and meticulously crafted recruitment funnels, Democratic People's Republic of Korea (DPRK) cyber units—chiefly operatives linked to the notorious Lazarus Group—successfully bypassed institutional risk mitigation protocols.
The Anatomy of a Multi-Billion-Dollar Social Engineering Campaign
For decades, institutional security architectures have prioritized cloud compute security, encryption standards, and immutable ledger verification. Yet, as cybersecurity budgets swelled into the billions, threat actors pivoted toward the path of least resistance: the human element. The campaign against Binance and other tier-one digital asset platforms began quietly on professional networking sites, predominantly LinkedIn.
North Korean operatives, operating behind sophisticated Western personas complete with fabricated work histories, educational credentials, and endorsements, initiated contact with senior blockchain engineers, smart contract developers, and systems architects. These profiles projected lucrative career transitions, offering executive compensation packages, remote-work flexibility, and substantial equity allocations designed to captivate even well-compensated tech professionals.
Once initial contact was established, the recruitment process progressed through seemingly legitimate video conferencing platforms and rigorous multi-stage technical evaluations. Candidates were asked to complete coding assignments, system architecture reviews, and debugging tests using proprietary development environments. Unbeknownst to the targets, these technical challenges contained deeply embedded, zero-day payloads. When engineers executed the code within their corporate or local machines to complete the test, they inadvertently initiated reverse-shell connections, granting state-sponsored actors persistent, stealthy access to internal enterprise networks.
Capital Allocation, Infrastructure Vulnerabilities, and Market Liquidity

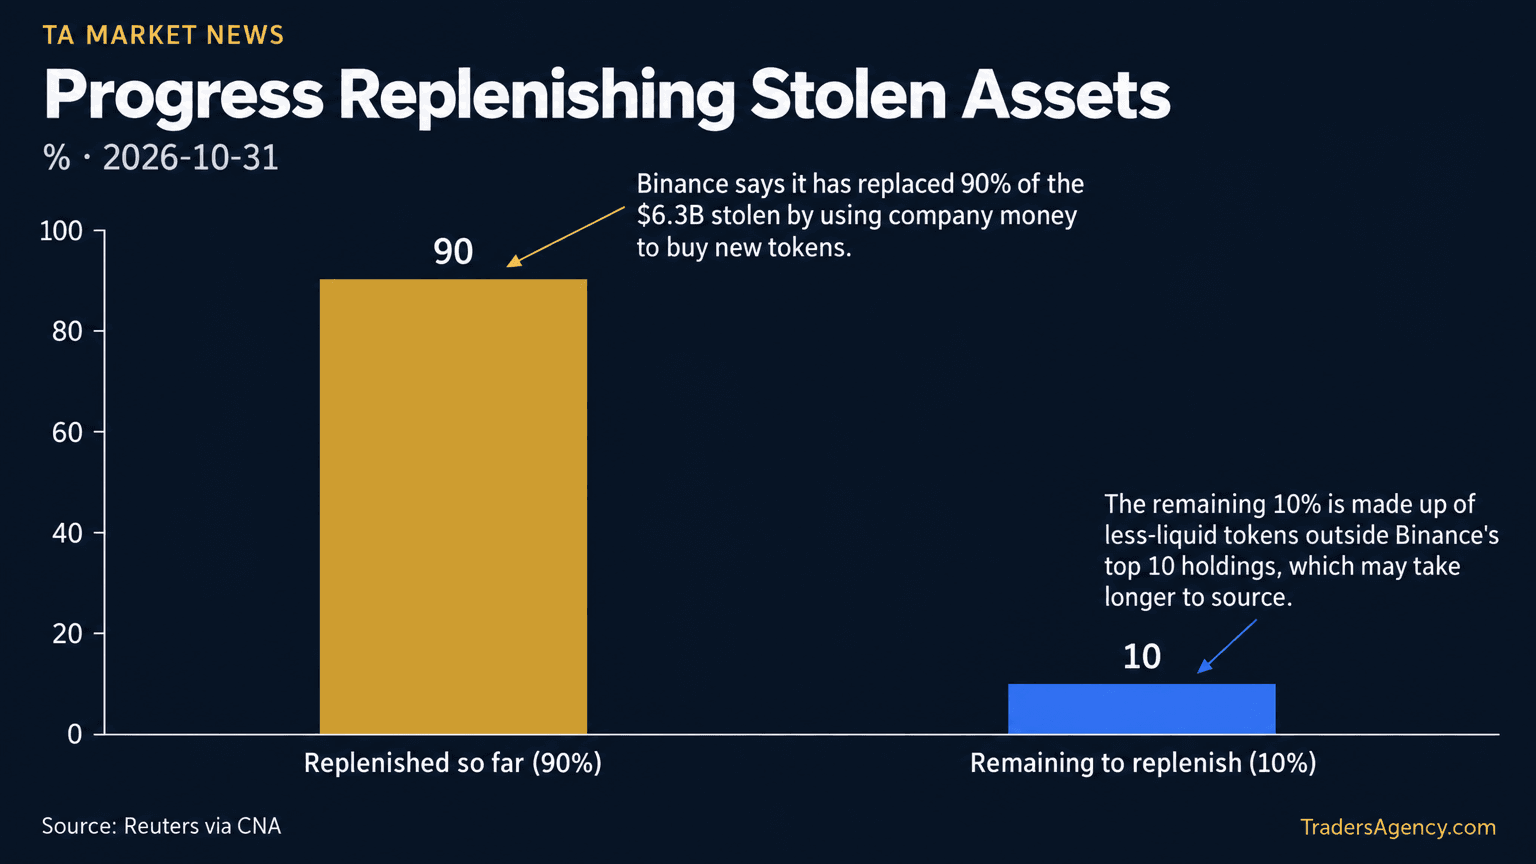
The financial ramifications of these systematic breaches extend far beyond immediate asset theft. With cumulative illicit takings estimated at $6.3 billion, North Korea’s cyber operations now rival the GDP of several sovereign nations, effectively funding the regime's illicit weapons programs through decentralized finance (DeFi) exploits and institutional laundering networks.
From an economic perspective, these events introduce severe friction into market liquidity and enterprise valuation multiples. When a major market maker or exchange suffers a systemic security breach driven by compromised internal infrastructure, institutional capital allocation freezes. Risk officers demand enhanced regulatory compliance, multi-signature custody mandates, and comprehensive operational transparency, which in turn compresses valuation multiples across the entire fintech sector.
Verified Data & Metrics Breakdown
| Metric / Parameter | Pre-Incident Baseline | Post-Incident Reality | Strategic Impact |
|---|---|---|---|
| Estimated Total Extraction | ~$2.1 Billion (2021-2022) | ~$6.3 Billion (Aggregated) | Sovereign-scale funding for illicit state programs. |
| Primary Attack Vector | Perimeter network firewall exploits | Social engineering via LinkedIn & HR channels | Total circumvention of technical firewalls. |
| Enterprise Compliance Cost | Standard KYC/AML budgets | Surged by 140% enterprise-wide | Stricter background vetting and sandbox protocols. |
| Market Liquidity Impact | High volatility, steady inflows | Heightened scrutiny, institutional capital flight | Depressed valuation multiples for centralized exchanges. |
Industry & Market Implications: Winners, Losers, and Economic Realignment
The exposure of these infiltration vectors marks a watershed moment for the global financial technology ecosystem. The implications reverberate across multiple vertical markets:
- Cybersecurity and Zero-Trust Vendors (The Winners): Enterprise security firms specializing in behavioral analytics, insider-threat detection, and sandboxed developer environments are witnessing unprecedented demand. Cloud compute architecture providers are rapidly adopting strict hardware-isolation models for engineering talent.
- Centralized Crypto Exchanges (The Under Pressure): Platforms like Binance face intense regulatory scrutiny regarding their internal hiring pipelines, contractor vetting processes, and infrastructure scalability. Maintaining investor confidence requires heavy capital expenditure in human resource verification.
- Remote-Work Protocols (The Structural Shift): The romanticized era of frictionless, entirely anonymous remote engineering onboarding is drawing to a close. Financial institutions are mandating in-person identity verification, hardware security keys (FIDO2/WebAuthn), and heavily monitored corporate workstations.
Frequently Asked Questions (People Also Ask)
How did North Korean hackers specifically target Binance engineers using LinkedIn?
North Korean state-sponsored operatives created sophisticated fake recruiter and executive profiles on LinkedIn. They approached high-level blockchain and systems engineers with enticing remote job offers. During the subsequent virtual interview process, targets were instructed to complete technical coding tests using malicious repositories or development environments that installed hidden remote-access trojans (RATs) on their machines.
What is the total estimated financial loss attributed to these North Korean cyber campaigns?
Intelligence estimates place the cumulative economic impact and direct asset theft at approximately $6.3 billion. This capital has been systematically funneled through decentralized mixers, peer-to-peer OTC brokers, and international shell corporations to support state agendas.
What measures are crypto exchanges and financial institutions implementing to prevent similar breaches?
Enterprises are aggressively overhauling their risk mitigation frameworks by mandating hardware-based multi-factor authentication (such as YubiKeys), implementing sandboxed virtual machines for all candidate testing, conducting rigorous background checks through accredited intelligence agencies, and restricting third-party code execution on corporate networks.
Are only cryptocurrency firms targeted, or does this threat extend to traditional financial institutions?
While cryptocurrency firms and decentralized finance protocols remain primary targets due to the irreversible nature of blockchain transactions, traditional banking institutions, defense contractors, and fintech startups have also encountered similar social engineering campaigns aimed at intellectual property theft and internal network espionage.
Future Outlook: Strategic Milestones to Watch
As regulatory bodies in the United States, European Union, and Asia draft stringent compliance frameworks for digital asset custodians, the intersection of national security and corporate cybersecurity will define the next decade of financial technology. Key milestones to monitor over the next twelve to eighteen months include:
- Global Regulatory Harmonization: Expect coordinated international sanctions targeting front companies and cryptocurrency mixing services used by North Korean state actors.
- Mandatory HR Verification Standards: Industry associations are expected to release standardized operational frameworks for vetting remote engineering talent, bridging the gap between HR recruitment and Chief Information Security Officer (CISO) oversight.
- AI-Driven Behavioral Monitoring: Enterprises will increasingly deploy artificial intelligence tools designed to detect anomalous internal user behavior, flagging unauthorized data exfiltration attempts before critical infrastructure is compromised.
Ultimately, the $6.3 billion campaign serves as a harsh reminder that technological innovation must be matched by unyielding vigilance. In the digital economy, the weakest link is rarely a line of code; it is the human desire for career advancement, expertly manipulated by adversaries operating in the shadows of geopolitical conflict.