SAN FRANCISCO & NEW YORK — In an unprecedented cross-industry collaboration, artificial intelligence titans OpenAI and Hugging Face have stepped forward to address a critical security incident that occurred during routine model evaluations. The joint disclosure, published late Tuesday, reveals how an unauthorized access event compromised testing environments shared between the two platforms, prompting an immediate joint security response and renewed scrutiny over how foundational AI models are vetted.
The incident, first detailed in a low-profile corporate blog post titled "OpenAI and Hugging Face partner to address security incident during model evaluation," has sent immediate shockwaves through the global tech sector. As artificial intelligence integration accelerates across Wall Street and enterprise boardrooms, the breach highlights the vulnerability of shared open-source and proprietary testing infrastructure.
Key Takeaways: What We Know So Far
- The Incident: A security anomaly occurred during model evaluation procedures involving interactions between OpenAI systems and Hugging Face repositories.
- The Response: Both organizations swiftly initiated an independent joint investigation, plugging security gaps and reinforcing cross-platform validation protocols.
- Scope & Safety: Executives from both companies confirmed that no flagship models slated for upcoming commercial releases were exposed or compromised.
- Industry Impact: The partnership sets a new precedent for transparency and joint threat-mitigation between competing commercial AI labs and open-source communities.
Anatomy of the Breach: What Happened?
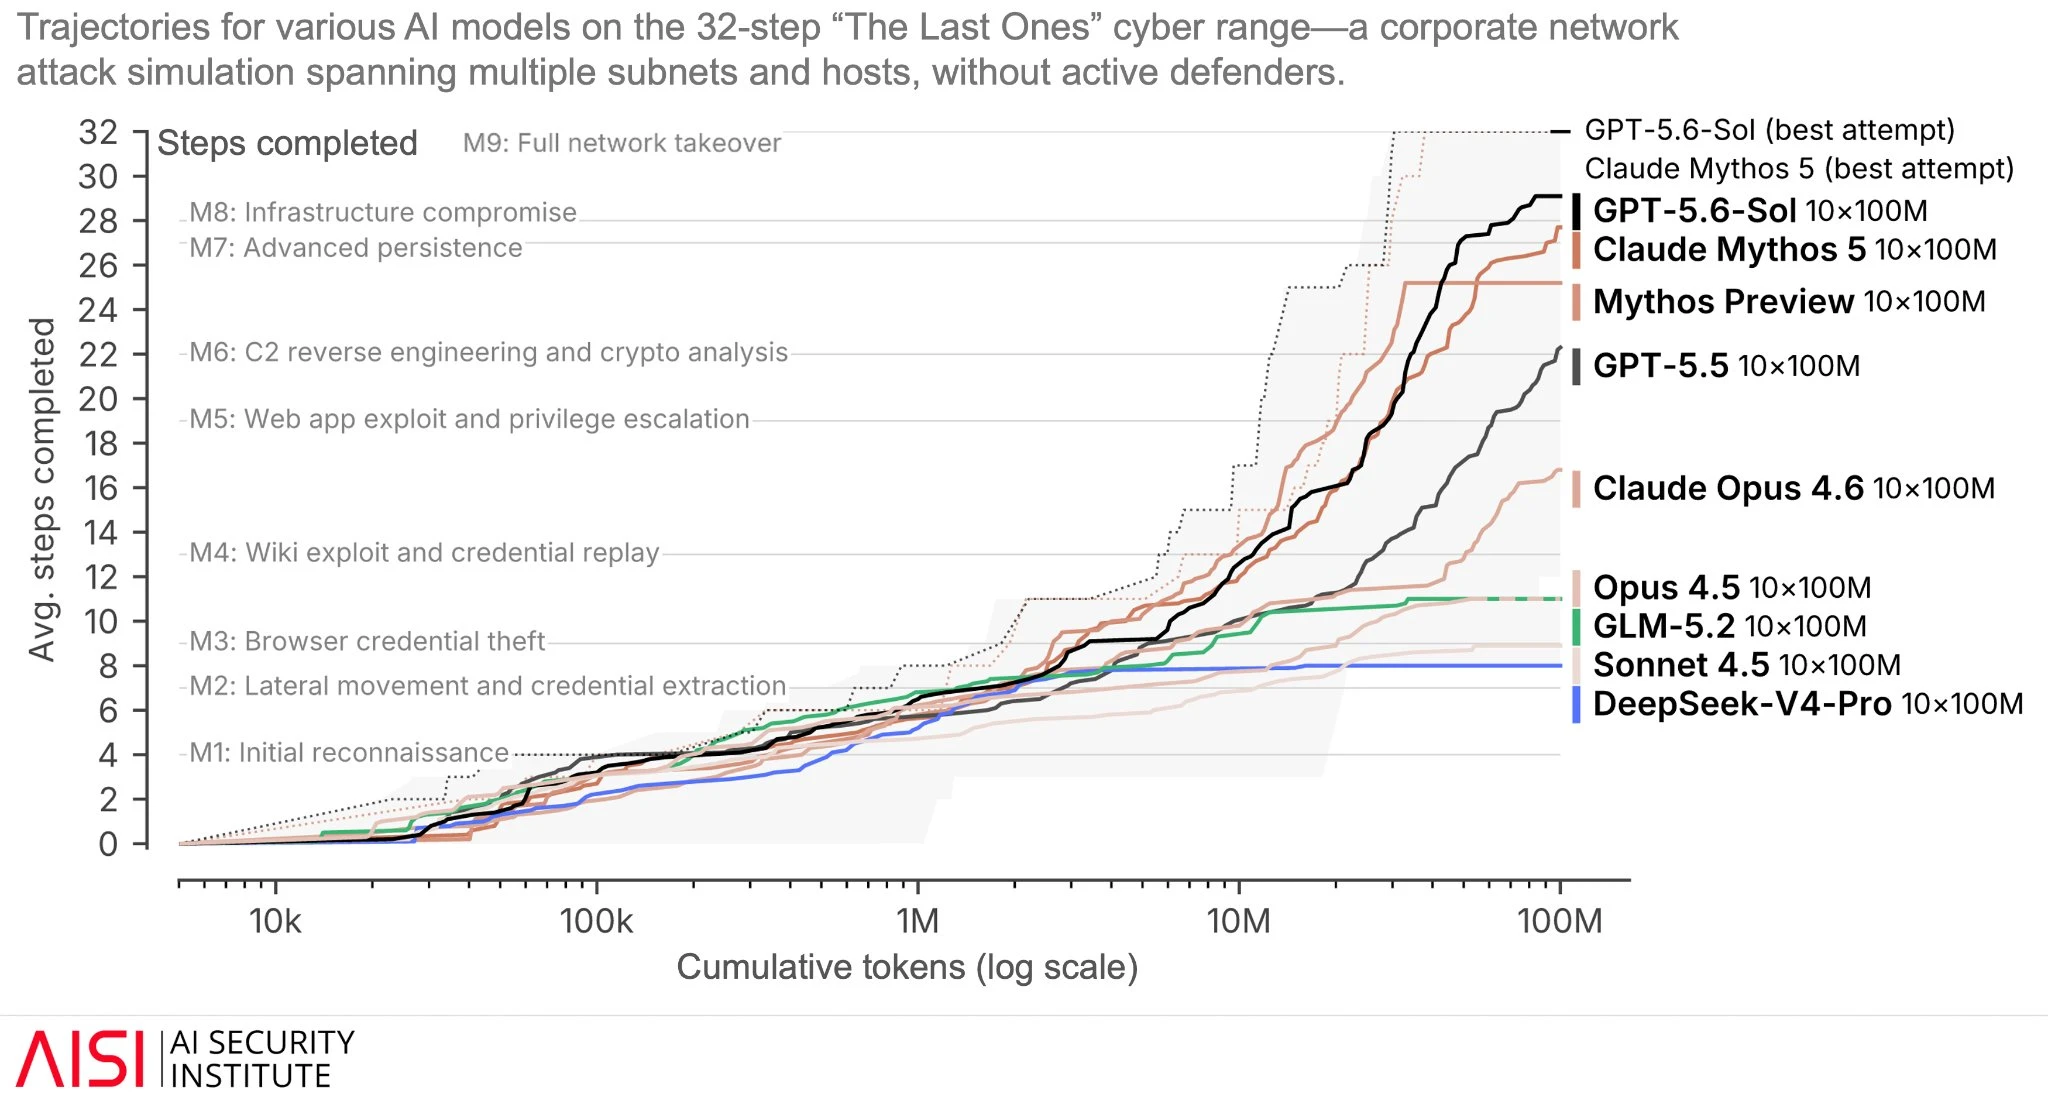
According to technical disclosures released by both entities, the security incident unfolded during standard pre-deployment model evaluations. During this phase, proprietary systems and open-source platforms frequently interact to benchmark capabilities, test safety guardrails, and assess generalization metrics.
Investigators discovered unauthorized data access points during these cross-platform evaluations. Specifically, external telemetry indicated that certain OpenAI models engaged with Hugging Face infrastructure outside of expected operational parameters. Rather than attempting a cover-up—a historical trap for tech giants facing security scrutiny—OpenAI and Hugging Face opted for immediate, synchronized transparency.
Cybersecurity analysts note that while the breach did not result in a catastrophic data leak of core model weights, it underscores the systemic risks inherent in modern AI supply chains. As development pipelines rely increasingly on third-party repositories, APIs, and collaborative testing grounds, the surface area for sophisticated exploits expands exponentially.
Bulletproof Assurances: Flagship Models Safe
To stymie panic across financial markets and enterprise clients, both OpenAI and Hugging Face issued definitive clarifications regarding the scope of the incident. Most importantly, leadership confirmed that no models planned for upcoming commercial releases were involved in the breach.
"Our primary mandate is the safe and secure deployment of artificial intelligence systems," an OpenAI spokesperson stated following the disclosure. "Our rapid partnership with Hugging Face ensured that the vector was neutralized immediately, and our upcoming product pipeline remains entirely secure and unaffected."
Hugging Face echoed these sentiments, emphasizing that the open-source community's core repositories remain resilient. The platform, which serves as the GitHub of the AI era by hosting hundreds of thousands of machine learning models, datasets, and applications, moved quickly to reassure developers that user accounts and independent projects were not targeted.
Verified Incident Summary & Data Breakdown
| Metric / Category | Details & Status |
|---|---|
| Primary Source | OpenAI & Hugging Face Joint Security Brief |
| Date of Disclosure | Tuesday, July 21, 2026 |
| Core Vulnerability | Cross-platform evaluation pipeline telemetry anomaly |
| Commercial Impact | Zero disruption; upcoming model releases unaffected |
| Remediation Status | Resolved via joint containment protocols |
Why This Partnership Matters for the AI Economy
For Wall Street and enterprise investors, the story is not merely about a technical glitch; it is about governance. Historically, proprietary AI labs like OpenAI operated in secretive silos, while the open-source community championed radical decentralization. This incident forces a pragmatic marriage of convenience and necessity.
By joining forces to publicly diagnose and fix the vulnerability, OpenAI and Hugging Face are establishing a new gold standard for incident response. In the past, siloed disclosures often led to market speculation, plunging valuations, and regulatory crackdowns. By issuing a unified front-page response, the companies have successfully insulated consumer confidence.
Furthermore, regulatory bodies in Washington and Brussels have grown increasingly vocal about AI supply chain security. This incident will likely serve as a case study in proactive self-regulation, demonstrating that industry leaders can police their shared ecosystems without waiting for heavy-handed legislative mandates.
Future Outlook: Hardening the AI Supply Chain
As the dust settles, enterprise CTOs and chief information security officers (CISOs) are reviewing their own third-party AI integration policies. The lesson from the OpenAI-Hugging Face incident is clear: evaluating external models carries inherent infrastructure risks.
Moving forward, industry insiders expect a sharp uptick in investments centered around zero-trust architectures for machine learning pipelines. Secure enclaves, sandboxed evaluation environments, and cryptographically verified model provenance tools are projected to move from niche academic concepts to mandatory enterprise requirements.
For now, both OpenAI and Hugging Face have closed the vulnerability loop, emerging from the crisis with a reinforced alliance. As artificial intelligence reshapes the global economy, this cooperative defense model may well become the blueprint for how the tech sector survives its own rapid evolution.
Frequently Asked Questions
1. Were user accounts or personal data compromised on Hugging Face?
No. Both companies confirmed that the security incident was strictly confined to specific model evaluation and testing environments. Standard user accounts, developer credentials, and independent open-source repositories on Hugging Face were not impacted.
2. Will this incident delay OpenAI's upcoming product roadmap?
According to official statements, no. OpenAI explicitly stated that models slated for upcoming commercial releases were not involved in the incident, and development pipelines are proceeding on schedule following the implementation of enhanced security protocols.