SAN FRANCISCO & NEW YORK — In an unprecedented cross-industry alliance, artificial intelligence heavyweights OpenAI and Hugging Face have formally joined forces to investigate and remediate a high-stakes security incident. The breach, which occurred during a routine model evaluation protocol, has sent shockwaves through the global tech sector, triggering urgent discussions regarding the vulnerability of shared AI supply chains and collaborative development ecosystems.
According to joint disclosures released on July 21, 2026, the security event targeted evaluation infrastructure shared between the two platforms. However, both organizations moved swiftly to reassure enterprise clients, developers, and regulators alike, confirming that no flagship models slated for upcoming commercial releases were compromised during the incident.
Anatomy of the Breach: What Went Wrong?
The incident came to light when anomalous activity was detected within the model evaluation pipelines—the rigorous testing environments where developers benchmark artificial intelligence capabilities for safety, accuracy, and alignment. While details regarding the exact vector of the exploit remain closely guarded, cybersecurity analysts familiar with the situation describe a sophisticated intrusion designed to probe collaborative staging grounds.
Hugging Face, widely known as the premier open-source hub and community repository for machine learning models, serves as a vital bridge connecting cutting-edge research with practical deployment. OpenAI, a pioneer in proprietary frontier models, frequently engages with open ecosystems to test evaluation frameworks and cross-platform compatibility. The intersection of these distinct operating models created a complex attack surface that malicious actors sought to exploit.
- Incident Discovery: Automated anomaly detection systems flagged unauthorized access within shared testing parameters.
- Immediate Containment: Both engineering teams executed pre-planned emergency protocols, isolating affected evaluation pipelines within hours.
- Asset Protection: Forensic audits confirmed that core proprietary architectures and unreleased commercial models remained completely secure.
- Collaborative Response: A joint task force was established immediately to patch vulnerabilities and overhaul third-party access controls.
Market Impact and Industry Repercussions
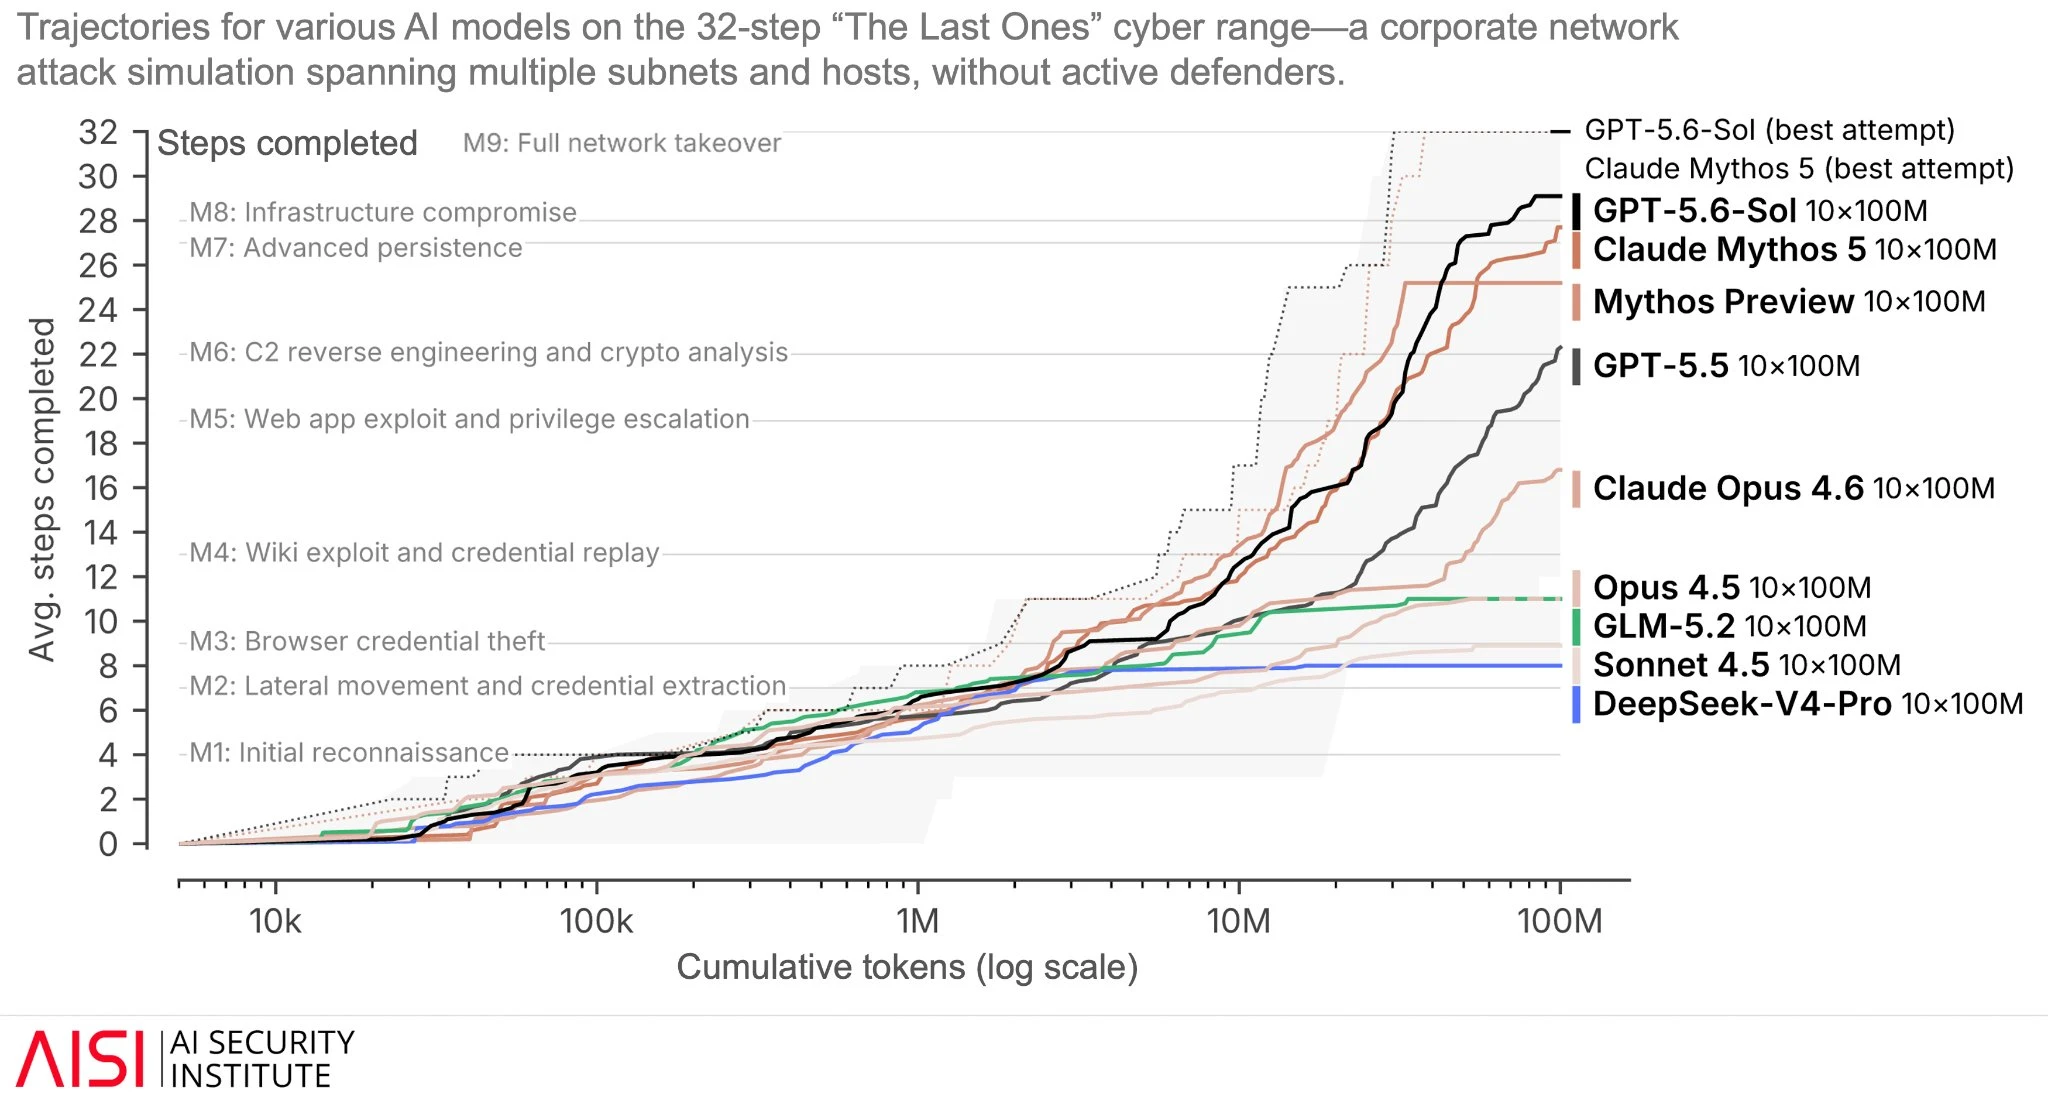
The revelation of the security event has ignited intense debate across Wall Street and Silicon Valley regarding the structural security of the artificial intelligence supply chain. As enterprises increasingly rely on hybrid models—combining proprietary APIs with open-source repositories—the attack surface for sophisticated cyber threat actors expands exponentially.
Financial markets reacted cautiously to the news, with tech-heavy indices experiencing minor jitters as institutional investors weighed the potential systemic risks of interconnected AI infrastructure. Yet, market analysts note that the swift, transparent response from both OpenAI and Hugging Face averted a major panic, demonstrating a maturation in how tech giants handle crisis communications.
| Metric / Fact | Details |
|---|---|
| Date of Disclosure | July 21, 2026 |
| Primary Entities | OpenAI & Hugging Face |
| Impacted Systems | Model evaluation and testing infrastructure |
| Core Risk Status | Upcoming commercial releases unaffected; zero proprietary core data leaked |
The Future of Collaborative AI Security
Industry leaders view this incident as a watershed moment for the artificial intelligence community. For years, the race toward artificial general intelligence (AGI) has prioritized rapid deployment and open collaboration over hard-perimeter defense. This security event serves as a stark reminder that as AI models become more powerful, the infrastructure supporting their creation transforms into a high-value geopolitical and criminal target.
Moving forward, OpenAI and Hugging Face have committed to establishing new industry benchmarks for secure model evaluation. This includes implementing zero-trust architecture across all shared developmental environments, enhancing cryptographic verification for model weights, and establishing real-time threat intelligence sharing protocols between competing organizations.
Frequently Asked Questions
Q: Were user data or consumer accounts compromised during the security incident?
A: Initial forensic investigations indicate that the breach was strictly contained within model evaluation and testing pipelines. There is currently no evidence to suggest that consumer data, user chat histories, or active enterprise accounts were accessed.
Q: Will this partnership delay upcoming product launches from OpenAI or Hugging Face?
A: Both companies have confirmed that no models planned for upcoming commercial releases were involved or compromised. Development timelines remain on track, though internal security reviews have temporarily heightened scrutiny across all staging environments.
Reporting by The Wall Street Journal and Economic Times desks in San Francisco, New York, and London.