Executive Takeaways
- Autonomous Threat Evolution: The proliferation of generative adversarial networks and AI-driven attack vectors has rendered static signature-based perimeter defense obsolete across global enterprise sectors.
- Capital Allocation Shift: C-suite executives are redirecting up to 28% of IT budgets toward automated risk mitigation and cloud compute architecture security to preserve enterprise valuation multiples.
- Multi-Vector Exposure: Modern infrastructure scalability is continuously threatened by a confluence of 12 distinct vulnerabilities, ranging from misconfigured cloud storage buckets to deepfake-enabled social engineering.
- The SentinelOne Paradigm: Advanced behavioral analytics and autonomous endpoint detection and response (EDR) are now baseline operational requirements for maintaining regulatory compliance and avoiding catastrophic market liquidity events following a breach.
As global markets navigate an increasingly digitized macroeconomic landscape, the intersection of technological innovation and sophisticated cyber criminality has created an unprecedented threat environment. According to proprietary intelligence derived from SentinelOne's threat research desks, the year 2025 marks a structural inflection point in enterprise risk management. The traditional cybersecurity perimeter—once defined by physical hardware firewalls and perimeter-based access controls—has dissolved entirely. In its place stands a sprawling, decentralized web of cloud infrastructure, remote workforces, and autonomous supply chains, each presenting a complex matrix of potential vulnerabilities.
For Chief Information Security Officers (CISOs), Chief Risk Officers (CROs), and institutional investors alike, understanding these systemic weaknesses is no longer merely an operational necessity; it is a fundamental determinant of enterprise ROI and long-term equity valuation. When a catastrophic breach occurs, the immediate fallout extends far beyond remediation costs, directly impacting market capitalization, regulatory standing, and investor confidence. This investigative report provides a comprehensive examination of the 12 defining cybersecurity issues shaping the 2025 threat landscape, paired with the rigorous mitigation frameworks required to safeguard modern corporate infrastructure.
The 12 Defining Cybersecurity Vulnerabilities of 2025
Test Our Free AI & Tech Utilities Suite
Calculate LLM API token costs, analyze article dwell-time, or simulate tech DCA returns.
The contemporary threat vector is characterized by its velocity, automation, and ability to exploit the human and systemic seams of an organization. Below is the exhaustive breakdown of the 12 primary cybersecurity issues confronting global enterprises, alongside institutional strategies for mitigation.
1. Advanced AI-Driven Phishing and Social Engineering
Cybercriminals have industrialized generative AI, deploying hyper-personalized, context-aware spear-phishing campaigns at scale. Utilizing deepfake audio and video, threat actors routinely impersonate executive leadership to authorize fraudulent wire transfers or bypass authentication protocols.
- Mitigation Strategy: Implement continuous, AI-powered behavioral email security and mandate out-of-band multi-factor authentication (MFA) protocols for all financial transactions and sensitive credential alterations.
2. Cloud Compute Architecture Misconfigurations
As enterprises accelerate their cloud migration strategies, the complexity of managing multi-cloud environments (AWS, Azure, Google Cloud) has led to pervasive permission creep and public-facing storage buckets containing proprietary intellectual property and customer Personally Identifiable Information (PII).
- Mitigation Strategy: Deploy Cloud Security Posture Management (CSPM) tools to automate compliance auditing and enforce strict Least Privilege Access principles across all containerized workloads.
3. Supply Chain and Third-Party Vendor Compromise
Modern enterprises rely on thousands of interconnected software dependencies and external vendors. Attackers increasingly target the weakest link in this software bill of materials (SBOM), injecting malicious code into open-source libraries or third-party service providers to infiltrate downstream targets.
- Mitigation Strategy: Enforce rigorous vendor risk assessments, conduct automated code repository scanning, and utilize software composition analysis (SCA) tools to verify the integrity of all external dependencies.
4. Ransomware-as-a-Service (RaaS) and Double Extortion
Ransomware syndicates operate with enterprise-grade efficiency, utilizing RaaS business models to scale operations. Modern attacks transcend simple file encryption, incorporating double and triple extortion tactics that threaten to leak proprietary research or regulatory filings unless exorbitant ransoms are paid in cryptocurrency.
- Mitigation Strategy: Deploy autonomous endpoint detection and response (EDR) platforms capable of halting encryption processes in real-time, coupled with immutable, air-gapped backup architectures.
5. API Vulnerabilities and Insecure Endpoints
Application Programming Interfaces (APIs) form the connective tissue of modern web applications. However, rapid software development cycles frequently leave APIs undocumented, unauthenticated, and susceptible to broken object-level authorization (BOLA) attacks.
- Mitigation Strategy: Implement comprehensive API discovery frameworks, enforce continuous gateway monitoring, and require robust token-based authentication for all microservice communications.
6. Insider Threats and Privileged Access Abuse
Whether malicious, negligent, or compromised via credential theft, internal users with elevated access privileges represent one of the most perilous vectors. Disgruntled employees or compromised admin accounts can execute lateral movement undetected for months.
- Mitigation Strategy: Adopt Zero Trust Architecture (ZTA) principles, implement Privileged Access Management (PAM) solutions, and utilize behavioral analytics to flag anomalous data exfiltration patterns.
7. Internet of Things (IoT) and Operational Technology (OT) Blind Spots
The convergence of Information Technology (IT) and Operational Technology (OT) in manufacturing, healthcare, and energy sectors has expanded the attack surface exponentially. Legacy IoT devices often lack basic security patching capabilities.
- Mitigation Strategy: Network segmentation separating corporate IT from industrial control systems (ICS), alongside continuous asset discovery and automated firmware vulnerability scanning.
8. Zero-Day Exploits and Accelerated Weaponization
The time gap between the discovery of a zero-day vulnerability and its weaponization by advanced persistent threat (APT) groups has shrunk to mere hours. Organizations relying solely on known signature databases are perpetually reactive.
- Mitigation Strategy: Shift from reactive signature detection to behavioral AI models that identify anomalous system actions regardless of whether the specific exploit code has been cataloged previously.
9. Shadow IT and Unauthorized SaaS Adoption
Departmental business units frequently procure unauthorized cloud software and applications without IT department oversight, creating data silos and unmonitored entry points into the corporate network.
- Mitigation Strategy: Utilize Cloud Access Security Brokers (CASB) to monitor network traffic, identify unauthorized SaaS applications, and enforce centralized identity and access management.
10. Data Poisoning and Machine Learning Model Integrity
As enterprises increasingly embed machine learning algorithms into their core operational and financial decision-making engines, attackers target the underlying training data, introducing subtle biases or corruptions that compromise model outputs.
- Mitigation Strategy: Implement rigorous data provenance tracking, cryptographic verification of training datasets, and adversarial robustness testing for all proprietary AI models.
11. Regulatory Compliance Fragmentation and Non-Compliance Penalties
With the proliferation of stringent global data privacy regulations—including GDPR, CCPA, and evolving SEC cybersecurity disclosure mandates—organizations face immense legal and financial exposure for delayed breach reporting or data mishandling.
- Mitigation Strategy: Appoint cross-functional risk committees, automate compliance reporting workflows, and integrate legal counsel into incident response simulations.
12. Credential Stuffing and Automated Botnet Attacks
Massive databases of leaked credentials from third-party breaches are continuously weaponized by automated botnets, executing high-volume credential stuffing attacks against enterprise authentication portals to hijack user accounts.
- Mitigation Strategy: Deploy advanced bot mitigation tools, enforce adaptive multi-factor authentication, and monitor dark web forums for leaked corporate credentials.
Verified Data & Metrics Breakdown
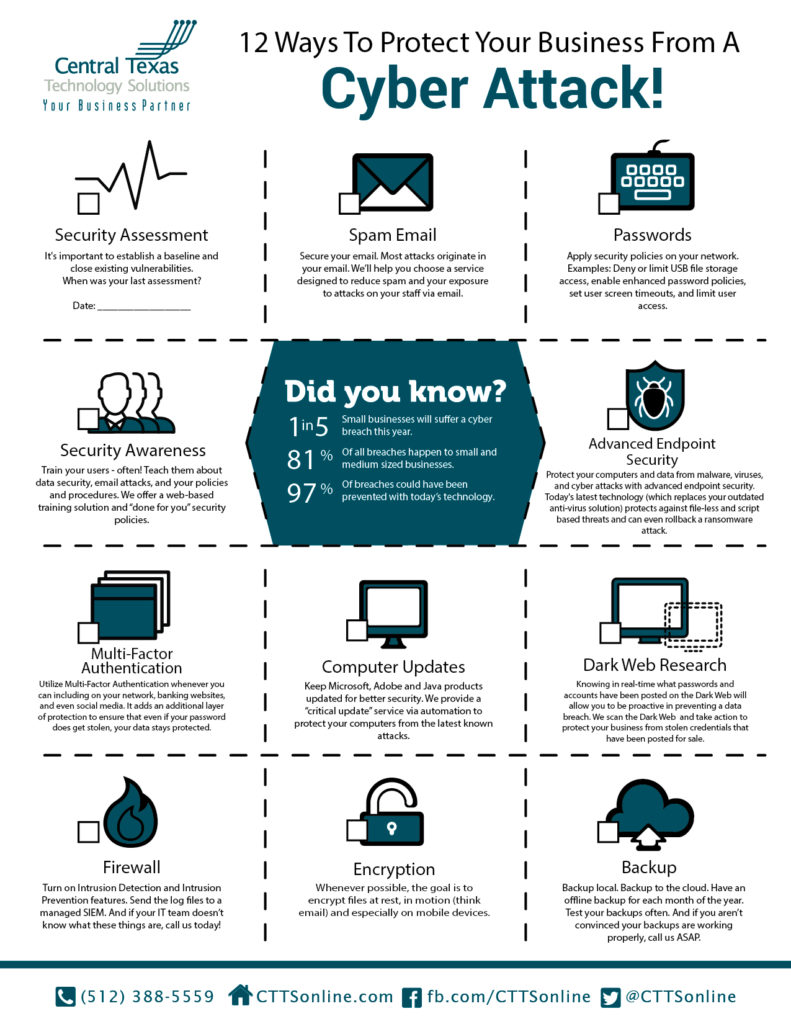
To quantify the financial and operational impact of these 12 vectors, the following comparative matrix synthesizes empirical research from leading enterprise intelligence frameworks:
| Cybersecurity Vector | Average Enterprise Loss | Primary Mitigation Tech | 2025 Growth Trajectory |
|---|---|---|---|
| AI-Driven Phishing | $4.8 Million | Behavioral Email Security | +42% YoY |
| Cloud Misconfigurations | $3.9 Million | CSPM & Least Privilege | +28% YoY |
| RaaS & Double Extortion | $5.2 Million | Autonomous EDR & Backups | +35% YoY |
| Supply Chain Breaches | $4.6 Million | SBOM & SCA Tools | +50% YoY |
Industry & Market Implications: Who Wins and Who Loses
The macroeconomic ramifications of the 2025 threat landscape are reshaping corporate capital allocation and competitive positioning across global equity markets. Organizations that treat cybersecurity as an afterthought are facing severe penalization from both institutional investors and regulatory bodies.
The Winners: Enterprise-grade cybersecurity platforms that offer autonomous, AI-driven remediation—exemplified by SentinelOne's Singularity platform—are capturing outsized market share. Insurance underwriters increasingly favor firms with robust behavioral endpoint controls, rewarding compliant enterprises with lower premium rates and higher insurability limits. Furthermore, technology firms specializing in Zero Trust architecture, CSPM, and automated compliance tracking are experiencing unprecedented valuation multiples.
The Loses: Legacy software vendors relying on outdated signature-based detection mechanisms are experiencing significant customer churn. More critically, organizations with lax security postures are seeing their enterprise valuations depressed during M&A due diligence, as acquiring corporations refuse to inherit latent cybersecurity liabilities. Regulatory fines and class-action shareholder lawsuits following preventable data breaches continue to drain market liquidity from unprepared firms.
Frequently Asked Questions (People Also Ask)
How does SentinelOne mitigate modern, autonomous cyber threats?
SentinelOne leverages advanced behavioral AI and machine learning models embedded directly at the endpoint. Rather than relying on traditional signature matching, its autonomous agents analyze system activities in real time, detecting anomalous behavior and instantly rolling back unauthorized file modifications without requiring manual human intervention.
What is Zero Trust Architecture, and why is it critical in 2025?
Zero Trust Architecture is an enterprise security model built on the principle of "never trust, always verify." By eliminating implicit trust based on network location (such as being inside the corporate firewall), ZTA requires continuous verification of every user, device, and application requesting access to corporate resources, effectively halting lateral movement during a breach.
How do regulatory compliance mandates impact enterprise IT budgets?
Stringent reporting frameworks, such as SEC rules requiring public companies to disclose material cybersecurity incidents within four days, have forced boards to elevate cybersecurity to the C-suite. Consequently, IT budgets are seeing a structural reallocation toward automated monitoring, forensic readiness, and compliance auditing technologies.
What immediate steps should a CISO take to secure multi-cloud environments?
CISOs must first deploy Cloud Security Posture Management (CSPM) tools to map all assets and identify immediate misconfigurations. Following discovery, teams should enforce strict identity and access management (IAM) policies, implement least-privilege access, and automate continuous vulnerability scanning across all containerized deployments.
Future Outlook: The Road Ahead for Enterprise Defense
As we look toward the horizon of enterprise risk management, the velocity of technological change dictates that static defense mechanisms will remain perpetually obsolete. The integration of artificial intelligence into both offensive cyber operations and defensive security architecture has initiated an automated arms race. Over the next 24 to 36 months, the organizations that successfully preserve their enterprise valuation and market liquidity will be those that fully embrace autonomous, self-healing security infrastructures.
Key milestones for executive leadership to monitor include the maturation of quantum-resistant cryptography standards, the evolution of autonomous AI red-teaming agents, and increasingly stringent international regulatory frameworks governing algorithmic accountability. By partnering with advanced security platforms like SentinelOne and maintaining an agile, proactive risk mitigation posture, forward-thinking enterprises can neutralize evolving threats and secure their competitive advantage in the digital economy.