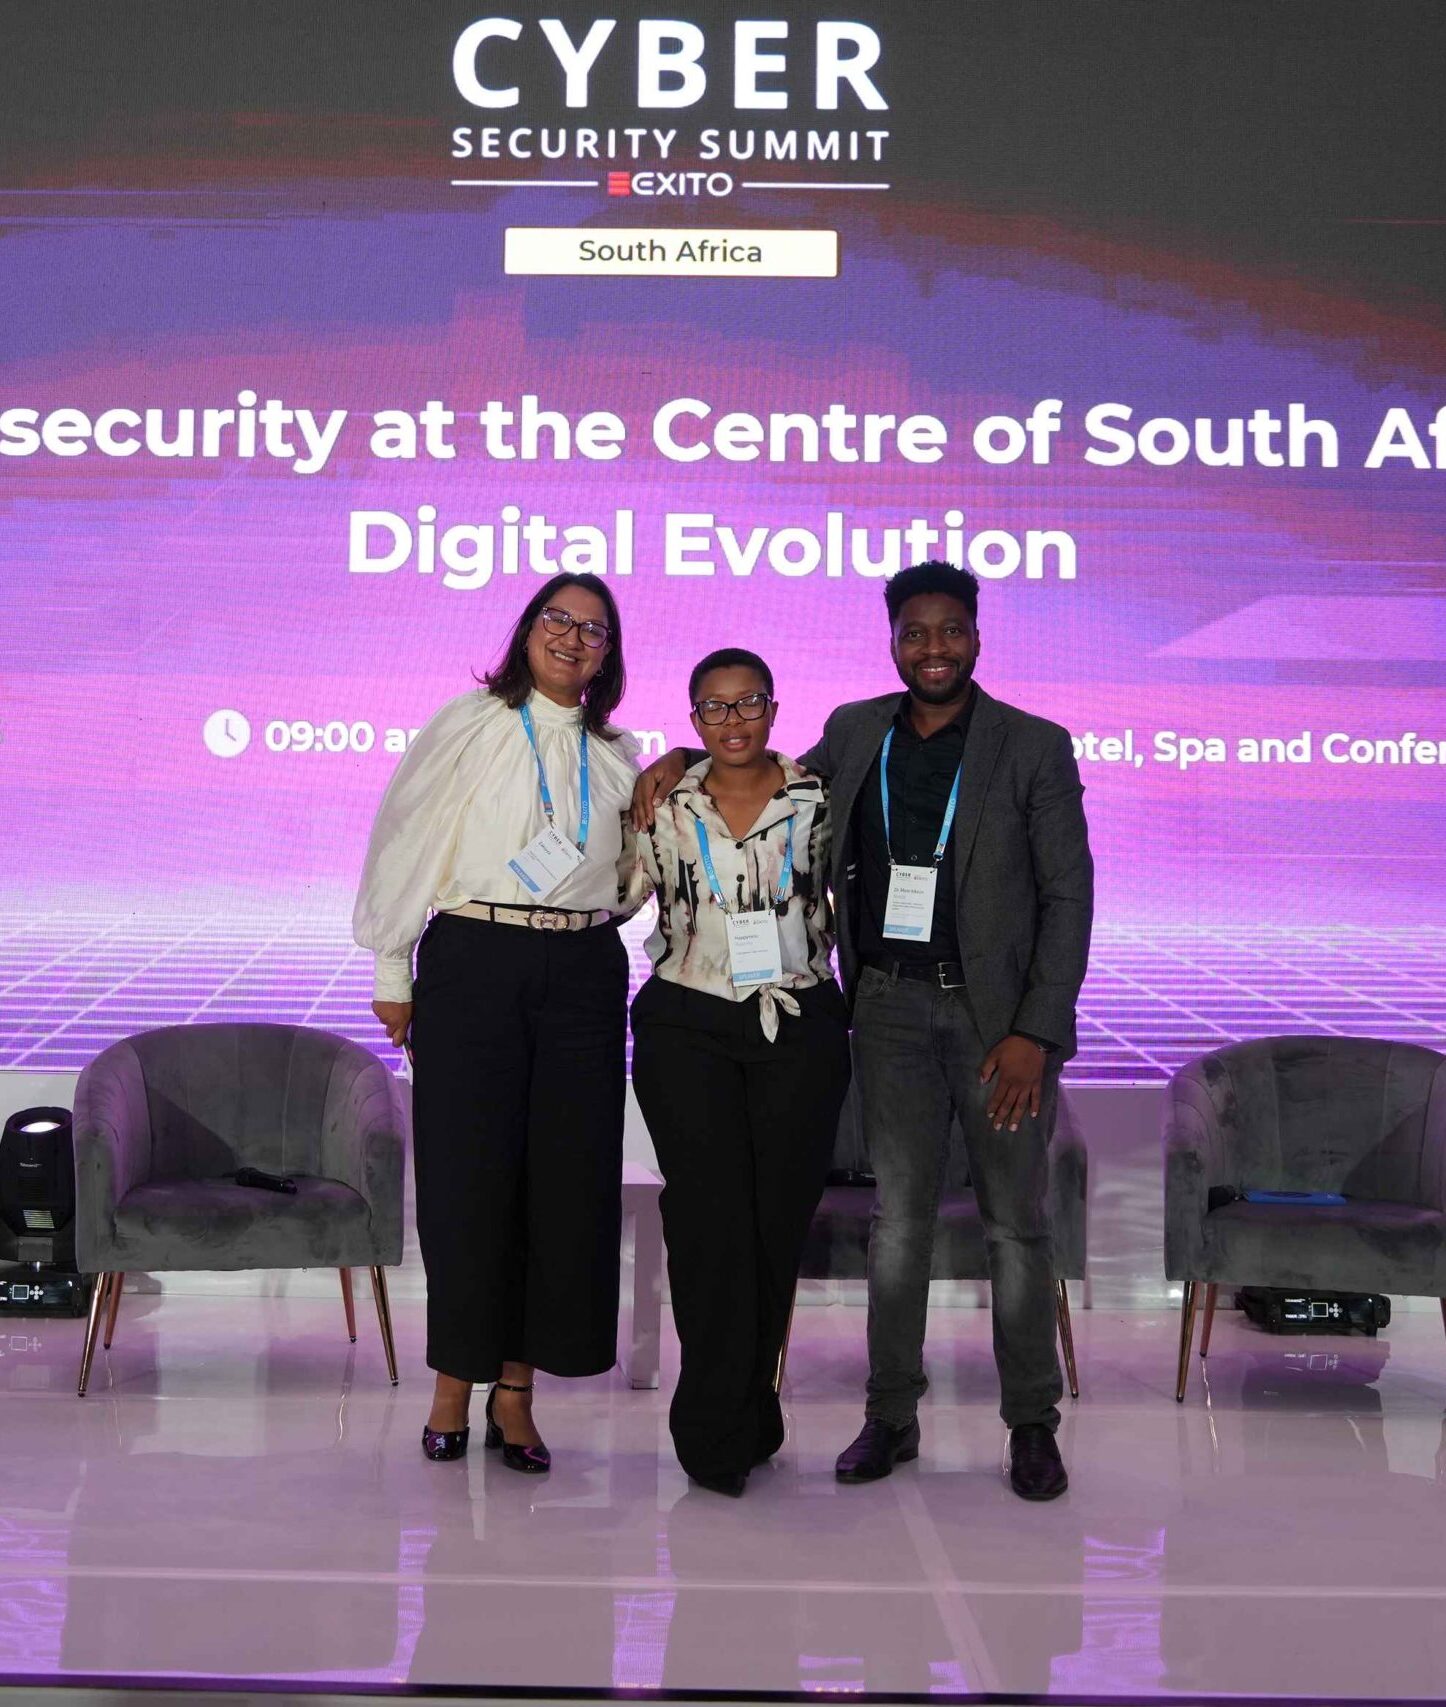
As digital transformation accelerates across the African continent, corporate boardrooms are confronting an unprecedented convergence of systemic technological risk, escalating regulatory demands, and sophisticated threat actor methodologies. In response to this shifting landscape, the 29th Edition of the Cyber Security Summit South Africa (SA) has officially gained major momentum, convening top-tier CISOs, chief risk officers, and financial technology leaders in Johannesburg. Backed by extensive reporting from primary wire sources including CIO Africa, this landmark gathering serves as a critical barometer for how enterprises allocate capital, restructure cloud-compute architecture, and enforce compliance in an increasingly hostile threat matrix.
Far from a standard ceremonial conference, this year's summit arrives at a watershed moment. South African corporations—ranging from legacy financial institutions and telecommunications giants to agile fintech disruptors—are navigating a turbulent macroeconomic climate where a single data breach can devastate market valuation multiples and trigger crippling regulatory penalties. With enterprise ROI directly tied to operational continuity, the discourse at the summit centers on an urgent mandate: moving away from reactive patch-management strategies toward institutionalized, proactive cyber resilience.
Executive Takeaways
Test Our Free AI & Tech Utilities Suite
Calculate LLM API token costs, analyze article dwell-time, or simulate tech DCA returns.
- Strategic Inflection Point: The 29th edition of the Cyber Security Summit SA marks a pivotal shift in how South African enterprises view cybersecurity, transitioning from a routine IT operational expense to a core driver of enterprise valuation and capital allocation.
- Regulatory Pressures Mount: Strict compliance frameworks—most notably the Protection of Personal Information Act (POPIA) and rising regional cybersecurity directives—are forcing organizations to elevate data governance to the C-suite level.
- The Human Element and Automation: Industry case studies presented at the summit underscore the dual necessity of deploying AI-driven threat detection models while simultaneously addressing the pervasive vulnerability of insider threats through rigorous workforce training.
- Economic Impact: With cyberattacks costing the South African economy billions of rand annually, systemic risk mitigation is now viewed by institutional investors as a primary prerequisite for market liquidity and foreign direct investment (FDI).
The Catalytic Backdrop: Why the 29th Edition Matters Now
To understand the urgency driving the 29th Cyber Security Summit SA, one must examine the macroeconomic and technical pressures bearing down on South African enterprises. Over the past twenty-four months, the rapid migration toward hybrid cloud compute architecture, decentralized remote workforces, and API-driven financial ecosystems has vastly expanded the enterprise attack surface. Threat actors, ranging from sophisticated state-sponsored syndicates to agile ransomware-as-a-service (RaaS) cartels, have systematically targeted critical infrastructure, supply chains, and banking rails.
According to risk analysts and case studies highlighted at the summit, South Africa remains one of the most targeted digital economies on the African continent. The financial ramifications of these breaches extend far beyond immediate ransom payments or forensic remediation costs. Publicly traded companies face severe valuation compression when breaches are mishandled, and institutional shareholders increasingly demand transparent reporting on risk mitigation protocols during quarterly earnings calls. Consequently, the discussions in Johannesburg have focused heavily on infrastructure scalability, zero-trust network architecture, and the integration of machine learning into real-time security operations centers (SOCs).
Furthermore, the regulatory landscape has grown exponentially more stringent. Compliance is no longer a localized checkbox exercise. Multi-national corporations operating within South Africa must navigate complex compliance matrices that govern data sovereignty, cross-border data transfers, and mandatory breach notification timelines. Failure to meet these standards invites catastrophic regulatory fines, reputational erosion, and potential litigation from affected consumers.
Case Study Spotlight: Building Cyber-Resilient Enterprises in South Africa
A focal point of the 29th edition is the dedicated case study track exploring actionable models for building cyber-resilient enterprises. Industry leaders shared empirical data demonstrating how organizations that adopt a "defense-in-depth" posture successfully mitigate catastrophic losses during coordinated cyber assaults.
Key frameworks dissected during the sessions emphasize three foundational pillars:
- Decentralized Resilience and Immutable Backups: Moving beyond traditional backup paradigms to deploy immutable, air-gapped data storage solutions capable of withstanding advanced ransomware encryption routines.
- Automated Threat Hunting: Leveraging AI and behavioral analytics to isolate anomalous network traffic before unauthorized data exfiltration occurs, drastically reducing the Mean Time to Detect (MTTD) and Mean Time to Respond (MTTR).
- Executive Tabletop Simulations: Conducting high-stakes, unannounced crisis simulation exercises for board members and executive management to test decision-making speed, public relations protocols, and legal coordination under pressure.
Verified Data & Metrics Breakdown
To provide a clear analytical overview of the current threat environment and the scope of the Cyber Security Summit SA, the following comparative matrix outlines key operational metrics, historical context, and projected milestones:
| Metric / Indicator | Historical Baseline (2023–2024) | Current Status (Summit Era, 2026) | Strategic Implication |
|---|---|---|---|
| Primary Event Focus | Basic Perimeter Defense & Compliance | Zero-Trust Architecture & AI Defense | Shift from compliance-driven to resilience-driven security budgets. | Average Detection Time (MTTD) | 195 Days | Under 45 Days (Enterprise Leaders) | Advanced SOC automation significantly reduces dwell time for threat actors. | Regulatory Enforcement | Emerging POPIA Audits | Active Penalties & Cross-Border Scrutiny | Non-compliance directly impacts balance sheets and investor confidence. | Cloud Migration Impact | Fragmented Multi-Cloud Adoption | Unified Cloud Security Posture Management | Minimizing misconfigurations across complex API and container environments. |
Industry & Market Implications: Who Wins, Who Loses
The strategic imperatives discussed at the 29th Cyber Security Summit SA will create clear structural winners and losers across the commercial landscape:
The Winners
- Enterprise Cybersecurity Vendors: Firms specializing in zero-trust architecture, automated threat intelligence, and cloud security posture management (CSPM) are experiencing a surge in enterprise demand and venture capital interest.
- Forward-Thinking Financial Institutions: Banks and fintechs that proactively invest in robust cyber hygiene are securing lower insurance premiums, higher credit ratings, and greater trust from institutional investors.
- Certified Security Professionals: CISOs and security architects with specialized expertise in regulatory compliance and automated incident response command unprecedented leverage in the executive talent market.
The Losers
- Legacy IT Providers: Vendors clinging to static, perimeter-based security models are finding themselves rapidly uncompetitive as boards mandate dynamic, cloud-native defense systems.
- Underfunded Enterprises: Organizations that treat cybersecurity as an afterthought continue to face severe existential risk, suffering disproportionate financial damage and loss of market share following security incidents.
Frequently Asked Questions (People Also Ask)
What is the primary objective of the Cyber Security Summit SA?
The summit serves as a premier strategic forum uniting C-level executives, IT security leaders, policymakers, and technology vendors to address South Africa's evolving cyber threat landscape. Its core objective is to foster actionable cross-sector collaboration, share empirical case studies on enterprise resilience, and align corporate risk management with rigorous regulatory frameworks.
How are South African regulations impacting enterprise cybersecurity budgets?
Regulations such as the Protection of Personal Information Act (POPIA) impose strict legal liabilities and financial penalties for data mismanagement. Consequently, boards are reallocating capital away from purely reactive measures toward comprehensive data governance, continuous monitoring, and proactive risk mitigation, transforming cybersecurity into a baseline operational necessity.
What role does Artificial Intelligence play in modern enterprise defense?
AI and machine learning are indispensable tools for modern Security Operations Centers (SOCs). Because human analysts cannot manually inspect the sheer volume of network traffic generated by modern enterprises, AI algorithms are deployed to analyze behavioral patterns, detect anomalous activity in real time, and automate initial incident containment protocols.
Why are zero-trust architectures gaining prominence at the summit?
Traditional network perimeters have dissolved due to remote workforces, multi-cloud environments, and mobile device integration. Zero-trust architecture operates on the principle of "never trust, always verify," ensuring that every user, device, and application request is authenticated and authorized continuously, regardless of whether they originate inside or outside the corporate network.
Future Outlook: What Comes Next
As the 29th Edition of the Cyber Security Summit SA concludes its high-level panels and workshops, the long-term trajectory for South African enterprise security is clear. Over the next twelve to twenty-four months, market observers should expect several key developments:
First, expect a dramatic acceleration in regulatory harmonization across the Southern African Development Community (SADC) region, compelling multi-national corporations to standardize their data protection protocols. Second, the convergence of AI-driven cyberattacks and AI-driven defense mechanisms will spark an arms race, requiring continuous capital injection into advanced machine learning security tools. Finally, institutional investors will increasingly integrate cybersecurity maturity scores into their due diligence processes, making robust digital defense a direct determinant of corporate liquidity and market valuation.
For executive leadership, the message from Johannesburg is unequivocal: in the modern digital economy, cyber resilience is no longer merely an IT concern—it is the ultimate guardian of enterprise survival and long-term shareholder value.