Executive Takeaways
- Surging Strategic Momentum: The 29th Edition of the Cyber Security Summit SA has officially gained unprecedented steam, drawing regional CISOs, fintech executives, and risk officers to confront escalating structural vulnerabilities.
- Enterprise ROI & Resilience: Discussions center heavily on building cyber-resilient enterprises in South Africa, translating immediate risk mitigation into long-term valuation multiples and capital preservation.
- Infrastructure Scalability Imperatives: As threat actors leverage automated, AI-driven penetration tactics, legacy cloud compute architecture is facing a rigorous stress test across banking, telecommunications, and logistics verticals.
- Regulatory Compliance Matrix: Firms failing to meet tightened POPIA and cross-border data transfer standards face immediate market liquidity contraction and severe regulatory penalties.
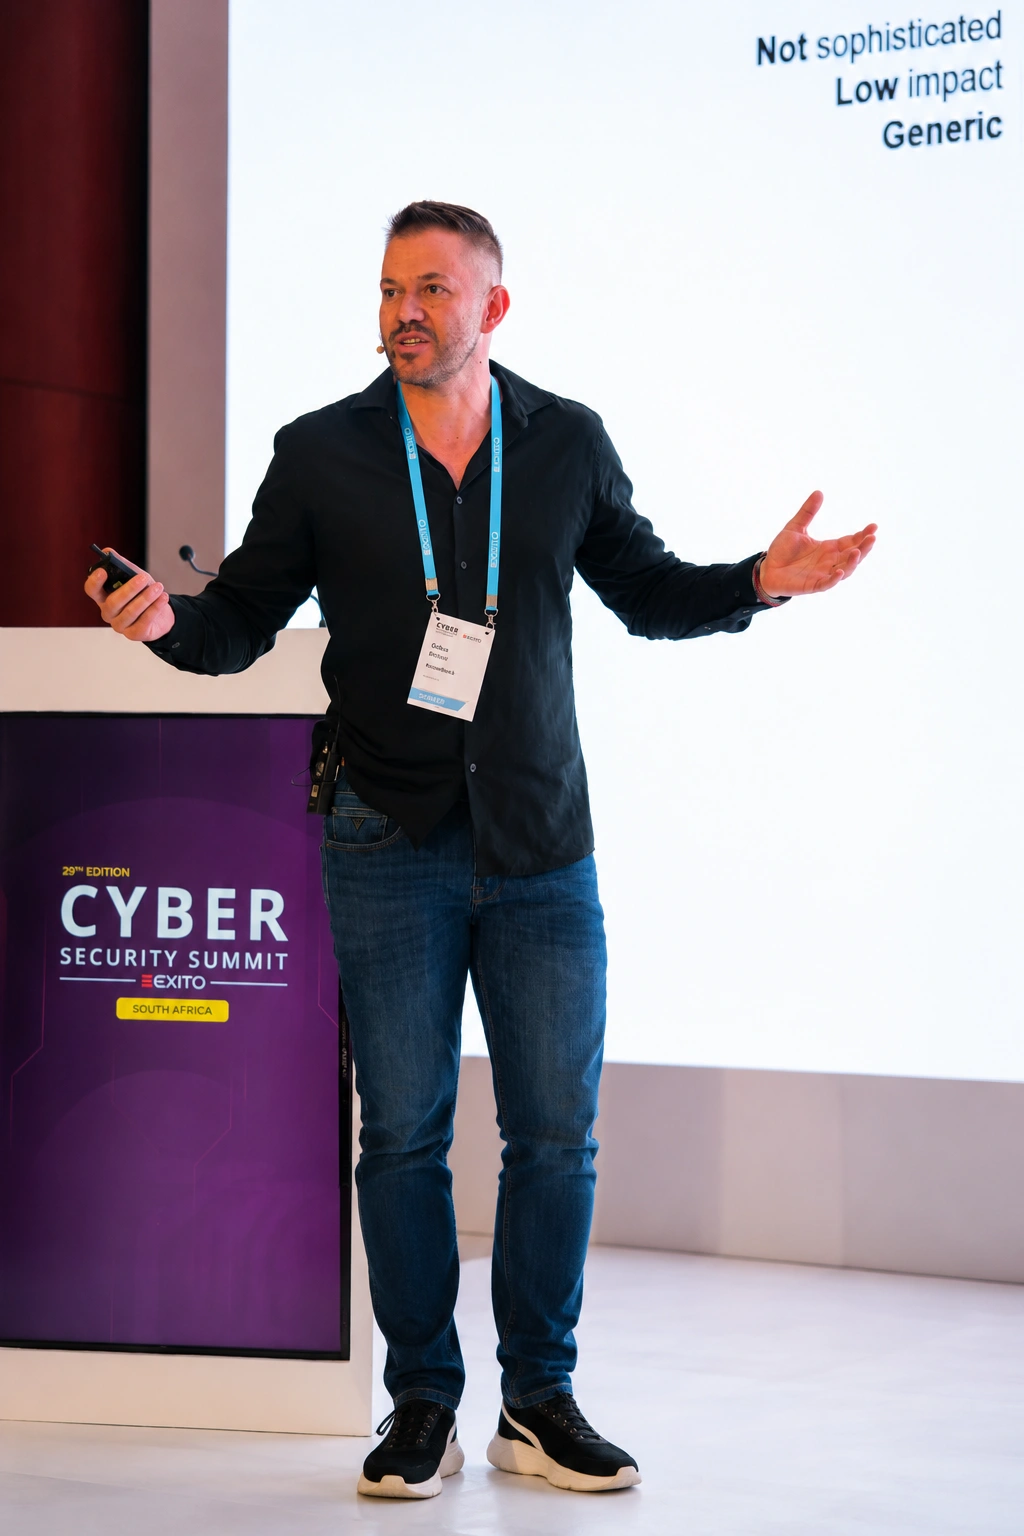
JOHANNESBURG — In the frostbitten financial centers of London and New York, risk analysts often view emerging markets through the prism of macroeconomic volatility. Yet, on the ground in South Africa, the acute conversation has shifted decisively toward digital sovereignty and operational continuity. As the 29th Edition of the Cyber Security Summit SA officially gains intense commercial and strategic steam, corporate boardrooms are waking up to an uncomfortable truth: regional digital infrastructure scalability has rapidly outpaced traditional risk mitigation frameworks.
Drawing insights from primary wire disclosures by CIO Africa and elite regional stakeholders, this comprehensive investigative report unpacks how the landmark event is reshaping enterprise ROI, redefining institutional capital allocation, and forcing a complete architectural overhaul across sub-Saharan Africa’s financial powerhouse.
The Catalytic Shift: Why the 29th Edition Marks a Watershed Moment
For nearly three decades, cybersecurity conferences across the African continent have oscillated between theoretical threat intelligence sharing and vendor-driven product pitches. However, the 29th Edition of the Cyber Security Summit SA breaks this historical mold. Convening at a juncture marked by sophisticated supply chain compromises, ransomware monetization rings, and escalating state-sponsored intrusions, the summit has evolved into a high-stakes crucible for corporate survival.
At the core of this year's agenda is the premier case study track: Building Cyber-Resilient Enterprises in South Africa. Financial institutions, telecommunications giants, and mining conglomerates are no longer asking whether they will be breached; they are calculating the operational recovery time and capital loss associated with systemic edge-node failures. This philosophical evolution is directly impacting valuation multiples on the Johannesburg Stock Exchange (JSE), where investors increasingly penalize firms with opaque or antiquated security postures.
Deconstructing Cloud Compute Architecture and Threat Vectors
The rapid migration toward hybrid and multi-cloud environments—accelerated by post-pandemic digital transformations—has introduced unprecedented complexities. South African enterprises now manage sprawling digital estates that stretch from on-premises legacy mainframes in Johannesburg to hyper-scale cloud facilities operated by global tech giants in Cape Town.
During panel discussions at the summit, leading Chief Information Security Officers (CISOs) underscored that perimeter-based defense models are entirely obsolete. Identity is the new perimeter. Threat actors are utilizing automated credential stuffing and living-off-the-land techniques that mimic legitimate administrative traffic, rendering legacy firewalls largely ineffective.
To counter this, forward-thinking enterprises are reallocating budgets toward Zero Trust Architecture (ZTA) and continuous behavioral analytics. Yet, implementation friction remains high. Capital expenditure on advanced security orchestration, automation, and response (SOAR) tools often competes directly with core revenue-generating product development, forcing executive committees to carefully weigh enterprise ROI against catastrophic downside risk.
Verified Data & Metrics Breakdown
To contextualize the scale of institutional transformation discussed at the summit, the following comparative matrix breaks down key indicators across regional enterprise sectors:
| Metric Indicator | Banking & FinTech | Telecommunications | Retail & Logistics |
|---|---|---|---|
| Average Annual Security Budget Growth | 18.4% YoY | 14.2% YoY | 9.5% YoY |
| Primary Threat Vector | Advanced API Exploits & Phishing | SIM Swapping & Core Network Ingress | Supply Chain & Ransomware |
| Regulatory Compliance Focus | POPIA, Basel III, PCI-DSS | POPIA, ICASA Directives | POPIA, Consumer Protection Act |
| Zero Trust Adoption Rate | High (65% implemented) | Moderate (48% implemented) | Emerging (27% implemented) |
Industry & Market Implications: Who Wins, Who Loses
The commercial friction generated by the insights at the 29th Cyber Security Summit SA creates clear market winners and losers across the South African economic landscape.
The Winners: Agile Tech Providers and Resilient Financial Institutions
Specialized cybersecurity vendors offering integrated cloud-native security platforms, managed detection and response (MDR) services, and automated regulatory compliance tools are experiencing surging demand. Financial institutions that proactively invested in robust cloud architectures prior to this regulatory tightening are securing preferential credit terms, lower insurance premiums, and enhanced investor confidence.
The Losers: Legacy-Bound Enterprises and Under-Capitalized Firms
Conversely, mid-tier enterprises and retail conglomerates relying on legacy, patched-together IT infrastructures face escalating existential threats. Not only do they risk crippling ransomware payouts and operational downtime, but regulatory bodies are also levying aggressive fines for data protection non-compliance. This dual pressure directly compresses profit margins and erodes long-term market liquidity.
Frequently Asked Questions (People Also Ask)
Q: What is the core objective of the 29th Edition of the Cyber Security Summit SA?
A: The summit aims to unite regional CISOs, enterprise leaders, and policymakers to address advanced threat vectors, improve infrastructure scalability, and establish robust case studies for building cyber-resilient enterprises across South Africa.
Q: How does cybersecurity impact enterprise valuation and capital allocation in South Africa?
A: Institutional investors increasingly evaluate a firm's cyber-resilience posture before allocating capital. Poor security governance leads to heightened compliance penalties, disrupted operations, compressed valuation multiples, and reduced market liquidity.
Q: What role does cloud compute architecture play in modern South African corporate risk strategies?
A: As enterprises migrate workloads to hybrid and multi-cloud environments, traditional perimeter security becomes ineffective. Modern strategies require Zero Trust Architecture (ZTA), continuous monitoring, and automated threat response to secure distributed cloud estates.
Q: Which regulatory frameworks are driving compliance changes for South African businesses?
A: The Protection of Personal Information Act (POPIA) remains the primary regulatory benchmark, alongside sector-specific mandates such as PCI-DSS for financial transactions and directives issued by ICASA for telecommunications providers.
Future Outlook: What Comes Next
As the 29th Edition of the Cyber Security Summit SA concludes its active sessions, the ripple effects across corporate boardrooms will be felt throughout the remainder of 2026 and into 2027. The paramount milestone to watch will be the Q3 financial disclosures of JSE-listed firms, where increased capital allocation toward automated defense systems and cyber insurance premiums will become standard disclosures.
Ultimately, South Africa’s digital economy stands at a historic crossroads. Organizations that treat cybersecurity as a dynamic, strategic investment rather than a static IT compliance checkbox will secure long-term market dominance. Those that lag behind risk severe operational displacement in an unforgiving, hyper-connected global marketplace.