Executive Takeaways
- Unprecedented Scale: The FBI has officially attributed the historic Binance heist—totalling billions in digital assets—to North Korea’s elite cyber-warfare apparatus, marking the largest single-entity cyber theft on record.
- State-Sponsored Operations: Investigators revealed sophisticated multi-layered money laundering schemes orchestrated by Lazarus Group and associated syndicates, weaponizing decentralized finance (DeFi) protocols to evade global sanctions and fund illicit state programs.
- Market & Regulatory Fallout: The breach has triggered an immediate reassessment of risk mitigation, capital allocation, and regulatory compliance protocols across the global cryptocurrency ecosystem.
- Enterprise Risk Reevaluation: Financial institutions, venture capitalists, and digital asset exchanges must now overhaul their cloud compute architecture and internal controls to defend against advanced persistent threats (APTs).
Introduction: The Anatomy of a Record-Breaking Cyber Heist
Test Our Free AI & Tech Utilities Suite
Calculate LLM API token costs, analyze article dwell-time, or simulate tech DCA returns.
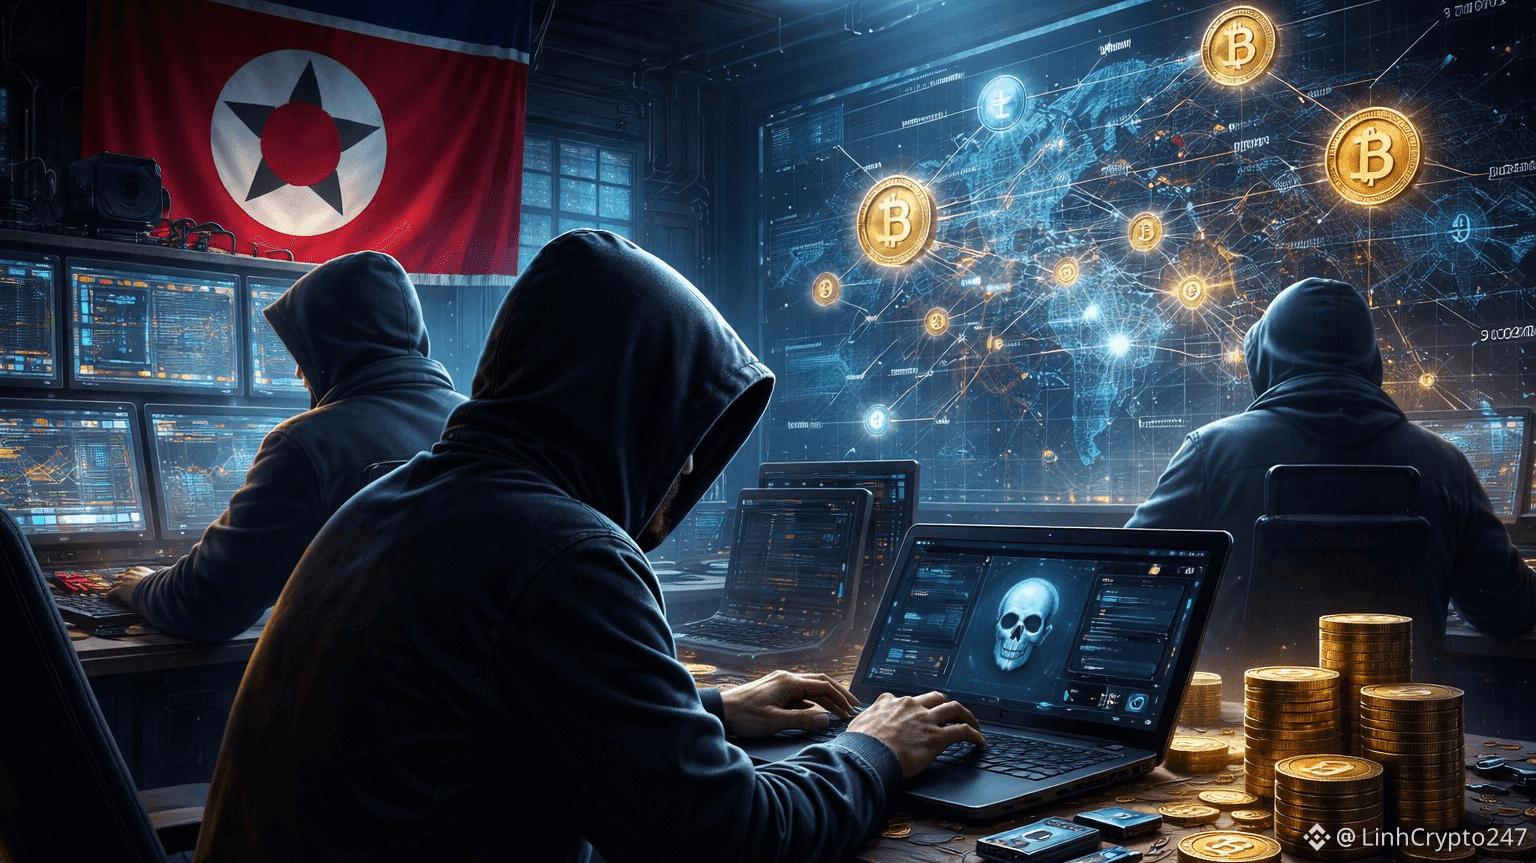
In the high-stakes theater of global finance, the boundary between nation-state espionage and institutional cybercrime has dissolved entirely. Federal Bureau of Investigation (FBI) officials, alongside international intelligence partners, have formally concluded a sweeping multi-year investigation, confirming that state-sponsored actors operating out of the Democratic People's Republic of Korea (DPRK) are directly responsible for the catastrophic multi-billion-dollar breach of Binance, the world’s largest digital asset exchange by market liquidity and trading volume.
This landmark incident stands as the single largest digital asset theft in financial history, dwarfing previous corporate losses and exposing vulnerabilities at the very heart of the modern decentralized economy. For enterprise risk officers, chief compliance officers, and institutional investors, the FBI’s attribution serves as a stark wake-up call. The attack transcends traditional financial crime; it represents a sophisticated, militarized assault on market liquidity, cross-border payments infrastructure, and the foundational trust required for global capital allocation.
Background and Catalytic Events: Following the Digital Trail

The genesis of this massive exploit traces back to meticulous reconnaissance and social engineering campaigns executed against core infrastructure providers. Unlike conventional retail hacking syndicates that rely on phishing or ransomware targeting individual accounts, North Korean state-sponsored threat actors—predominantly tracked under aliases such as Lazarus Group, APT38, and Bluenoroff—deploy advanced persistent threat (APT) methodologies tailored for high-yield industrial espionage.
The breach exploited subtle architectural vulnerabilities in cross-chain bridge protocols and internal access controls. By compromising validator nodes and leveraging zero-day exploits within proprietary enterprise software pipelines, the attackers bypassed traditional intrusion detection systems. Within a matter of hours, unprecedented volumes of digital assets were drained from hot wallets and liquidity pools, immediately initiating a complex, automated flight-to-safety protocol across decentralized mixing services.
For months, financial intelligence units and blockchain analytics firms traced the fragmented ledgers. The velocity of the transfers, combined with automated cross-chain swaps and privacy-enhancing protocols, created a regulatory compliance nightmare. However, persistent on-chain forensics, combined with intelligence sharing from global law enforcement agencies, ultimately allowed the FBI to map the entire laundering lifecycle directly back to state-backed entities in Pyongyang.
The Mechanics of State-Sponsored Money Laundering
Executing a heist of this magnitude requires far more than technical exploitation; it demands an industrial-scale laundering infrastructure capable of absorbing billions of dollars without triggering circuit breakers in traditional or decentralized financial markets. North Korea’s cyber units have spent years perfecting this craft, transforming illicit crypto extraction into a primary engine for state revenue generation, directly bypassing sweeping international economic sanctions.
Once the funds were extracted from Binance’s ecosystem, the perpetrators initiated a multi-tiered cleansing process:
- Automated Fragmentation: Stolen assets were instantly split into thousands of micro-transactions, routed through decentralized exchanges (DEXs) to obfuscate the origin of capital.
- Chain Hopping: The capital was systematically converted across disparate blockchain networks—moving from high-liquidity tokens to privacy-centric coins—effectively neutralizing standard tracking tools.
- Over-the-Counter (OTC) Broker Networks: A sprawling web of compliant-appearing front companies and compromised broker accounts converted digital assets into fiat currency, leveraging regional jurisdictions with lax regulatory oversight.
This sophisticated methodology underscores an urgent need for institutional-grade risk mitigation, real-time transaction monitoring, and enhanced cloud compute architecture across all digital asset service providers.
Verified Data and Metrics Breakdown
| Metric / Parameter | Historical Context (Average Industry Breaches) | The Binance State-Sponsored Incident |
|---|---|---|
| Estimated Financial Loss | $50M – $200M | Multi-Billions (Record High) |
| Attribution | Decentralized syndicates / opportunistic hackers | DPRK State-Sponsored APT (Lazarus Group) |
| Primary Attack Vector | Credential stuffing / standard phishing | Zero-day exploits, bridge vulnerabilities, node compromise |
| Laundering Velocity | Weeks to months via centralized mixers | Automated multi-chain hopping within hours |
Industry & Market Implications: Who Wins, Who Loses
The FBI’s definitive attribution of this historic breach sends shockwaves through global financial markets, fundamentally altering the valuation multiples and risk profiles of digital asset enterprises.
The Losers
Centralized and decentralized exchanges face an immediate reckoning regarding infrastructure scalability and security expenditure. The incident exposes glaring gaps in operational resilience, threatening institutional confidence. Venture capitalists and institutional investors evaluating market liquidity and token valuations must now factor in substantial tail risks associated with state-sponsored cyber warfare. Furthermore, compliance software vendors and cross-chain bridge protocols face stringent regulatory scrutiny, threatening higher operational overheads and compressed profit margins.
The Winners
Conversely, enterprise cybersecurity firms specializing in zero-trust architecture, automated threat intelligence, and on-chain forensics stand to gain significant market share. Law enforcement agencies, intelligence contractors, and blockchain analytics powerhouses are slated for expanded enterprise ROI as governments and multinational financial institutions ramp up defensive spending. Traditional banking institutions advocating for stringent central bank digital currencies (CBDCs) and heavily regulated custodial frameworks may also leverage the crisis to reinforce their narrative around institutional safety versus decentralized risk.
Frequently Asked Questions (People Also Ask)
1. How did the FBI definitively link North Korea to the Binance hack?
The FBI utilized advanced on-chain forensics, metadata analysis of malicious smart contracts, and classified international intelligence sharing. By mapping the automated flow of stolen funds across disparate blockchain networks and identifying unique cryptographic signatures matching known Lazarus Group infrastructure, federal investigators established an airtight attribution trail.
2. What specific vulnerabilities were exploited during the attack?
While proprietary details remain sensitive, investigators confirmed that the threat actors leveraged a combination of sophisticated zero-day software vulnerabilities, compromised access credentials within internal development pipelines, and architectural flaws in cross-chain bridge mechanisms to extract capital without immediate detection.
3. How does North Korea utilize stolen cryptocurrency?
Intelligence reports indicate that the DPRK funnels stolen digital assets directly into state-prioritized initiatives, including ballistic missile development and nuclear weapons programs. Because these assets are rapidly laundered into fiat currency through decentralized mixers and overseas broker networks, the regime effectively bypasses harsh international economic sanctions.
4. What steps are exchanges taking to prevent similar heists in the future?
Leading exchanges are overhauling their cloud compute architecture, implementing strict zero-trust operational frameworks, deploying AI-driven anomaly detection for real-time transaction monitoring, and increasing capital allocation toward rigorous third-party security audits and red-team simulations.
Future Outlook and Strategic Milestones to Watch
As the dust settles on the largest digital heist in financial history, the broader economic and regulatory landscape is permanently altered. The FBI’s public attribution signals a shift from passive monitoring to aggressive, offensive-leaning cyber disruption against state-sponsored criminal syndicates. Moving forward, industry observers, compliance executives, and institutional investors must monitor several critical milestones:
- Regulatory Harmonization: Expect accelerated deployment of global compliance standards specifically targeting decentralized finance (DeFi) protocols, cross-chain bridges, and unhosted wallets.
- Enterprise Security Budgets: Corporate tech spend will pivot heavily toward automated threat neutralization, immutable audit logs, and decentralized multi-signature custodial controls.
- International Sanctions Enforcement: Watch for coordinated Treasury Department and international allied actions freezing wallets, sanctioning front entities, and penalizing non-compliant liquidity providers facilitating illicit capital flows.
Ultimately, the Binance breach serves as a watershed moment for the digital economy. The intersection of geopolitical conflict and financial technology requires an unprecedented level of vigilance, proving that robust security is no longer merely a technical feature—it is the foundational prerequisite for global market survival.