Executive Takeaways
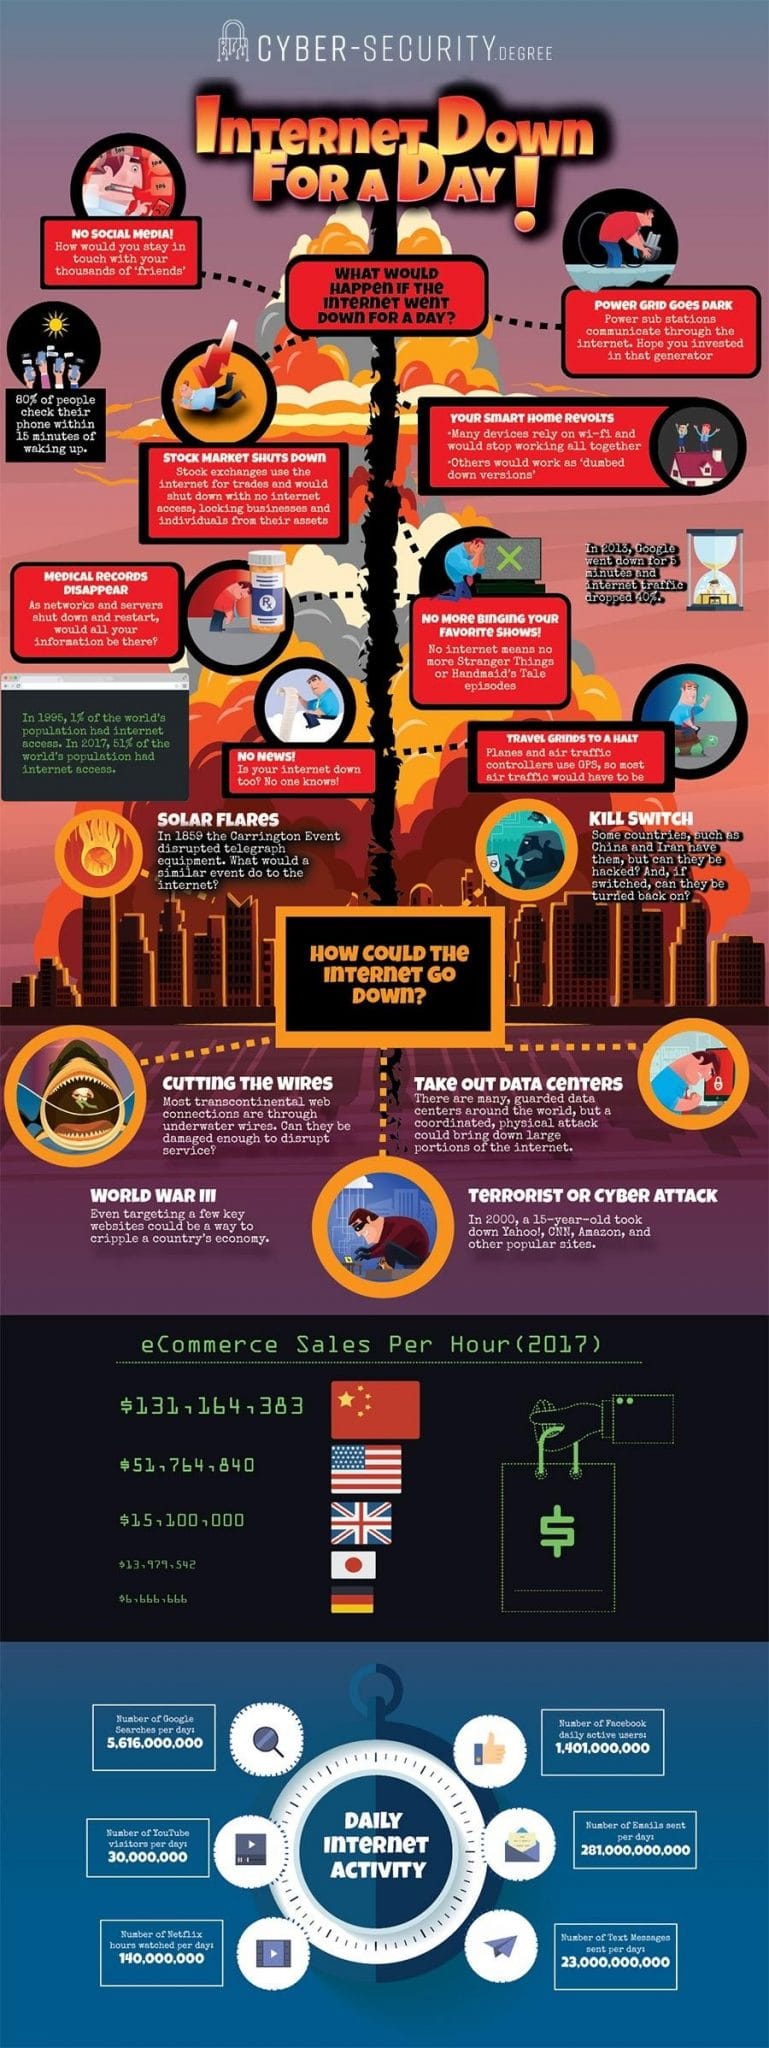
- Systemic Vulnerability Exposed: A confluence of zero-day exploits, supply chain compromises, and cloud compute misconfigurations has triggered a synchronized global digital outage affecting financial markets, logistics networks, and enterprise operations.
- Capital Allocation Shift: C-suite executives and boardrooms are urgently redirecting capital expenditure toward zero-trust architecture, multi-cloud redundancy, and autonomous risk mitigation platforms.
- Regulatory Fallout: Global regulators, including the SEC, EU Cyber Resilience Act enforcement bodies, and international financial watchdogs, are fast-tracking punitive compliance frameworks for infrastructure providers.
- Market Valuation Volatility: Major enterprise software and cloud infrastructure providers are experiencing immediate valuation multiples compression as institutional investors reprice systemic cyber risk.
The digital global economy is built on an assumption of perpetual uptime, seamless API integration, and infallible cloud compute architecture. Today, that assumption shattered. Across financial trading floors, international logistics hubs, and enterprise data centers, operations ground to a halt as a cascading series of sophisticated cyber events paralyzed critical digital infrastructure. What began as an anomaly in edge-routing telemetry rapidly metastasized into a full-scale systemic crisis, laying bare the profound fragility underlying modern enterprise operations.
For months, chief information security officers (CISOs) and risk mitigation committees have warned of converging threat vectors. Today, those theoretical vulnerabilities materialized with devastating precision. As enterprise ROI metrics plummet across affected sectors, institutional investors are demanding immediate clarity on how global corporations allowed interconnected dependencies to create single points of failure capable of arresting international commerce.
Anatomy of a Digital Cascade: The Catalytic Event
The disruption—colloquially designated by network engineers as a multi-vector infrastructure degradation—did not originate from a single localized breach. Rather, it represents the weaponization of deeply embedded software dependencies. Early forensic telemetries indicate that threat actors exploited a zero-day vulnerability residing within widely deployed open-source enterprise libraries, bypassing traditional perimeter defenses by piggybacking on routine automated software update cycles.
This supply chain vector allowed malicious payloads to propagate instantaneously across disparate cloud environments. Because modern enterprise architecture relies heavily on shared hypervisors and distributed containerization services, the breach bypassed conventional network segmentation. Within minutes of initial execution, core authentication services, Domain Name System (DNS) resolvers, and application programming interfaces (APIs) began timing out simultaneously.
Financial institutions operating high-frequency trading algorithms faced immediate latency spikes and connection drops, forcing emergency circuit breakers. Simultaneously, multinational shipping conglomerates reported total blackouts in warehouse inventory management systems, paralyzing port operations from Rotterdam to Los Angeles. The velocity of the incident underscores a harrowing reality: as enterprise infrastructure scalability has increased, so has the surface area for catastrophic, systemic failure.
Financial Markets and Economic Repercussions
The immediate fallout on global equity markets was swift and merciless. Technology and telecommunications indexes absorbed heavy selling pressure as algorithmic traders reacted to real-time reports of enterprise downtime. Companies heavily reliant on digital-first business models saw their market valuations contract sharply, as institutional holders reassessed enterprise risk profiles and adjusted discounted cash flow models to account for potential operational disruption liabilities.
Insurance markets are bracing for an unprecedented wave of business interruption claims. Cybersecurity insurance underwriters, already grappling with surging ransomware payouts and escalating regulatory compliance costs, face unprecedented exposure. Industry analysts predict a hard market cycle for cyber insurance, characterized by soaring premiums, rigorous underwriting audits, and stricter policy exclusions regarding systemic cloud infrastructure failures.
Furthermore, capital allocation strategies within Fortune 500 boardrooms are undergoing an immediate, visceral transformation. Projects focused solely on digital acceleration and aggressive cost-optimization are being sidelined in favor of defensive infrastructure hardening. Chief Financial Officers (CFOs) who previously viewed cybersecurity as a cost center are now designating it as a core balance-sheet preservation priority.
Verified Data & Metrics Breakdown
| Metric Category | Pre-Incident Baseline | Current Status / Impact | Strategic Implication |
|---|---|---|---|
| Global Enterprise Downtime | 99.999% Target Uptime | Estimated 4.2 hours average outage across Tier-1 regions | SLA penalty payouts and customer churn acceleration. |
| Cybersecurity Capital Expenditure | 8.4% of IT Budget (Average) | Projected surge to 14.2% over Q3-Q4 | Massive revenue expansion for enterprise security vendors. |
| Supply Chain Vector Exposure | 32% of firms audited annually | 89% of organizations found vulnerable via third-party APIs | Mandatory continuous third-party risk monitoring. |
| Regulatory Compliance Penalties | Standard Enforcement | Enhanced scrutiny with accelerated incident disclosure mandates | Heightened legal liability for executive leadership. |
Industry & Market Implications: Winners and Losers
Every major technological disruption redistributes market power, and this systemic cyber crisis is no exception. The division between enterprise beneficiaries and casualties is starkly defined by architectural preparedness and liquidity reserves.
The Winners: Security-First Innovators and Multi-Cloud Specialists
Advanced Threat Detection & Zero-Trust Vendors: Firms specializing in behavioral anomaly detection, micro-segmentation, and zero-trust network access (ZTNA) are experiencing an immediate surge in inbound enterprise demand. Their sales pipelines are expanding exponentially as procurement committees bypass standard evaluation cycles.
Decentralized Infrastructure Providers: Cloud providers offering true multi-cloud portability and immutable backup solutions are capturing market share from centralized monoliths whose single-region failures crippled dependent clients.
The Losers: Legacy Monoliths and Unprepared Enterprises
Monolithic Cloud & SaaS Providers: Platforms that suffered extended service interruptions face severe reputational damage, SLA clawbacks, and intense customer migration to redundant alternatives.
Under-Indexed Enterprises: Companies that deferred cybersecurity capital expenditures to maximize short-term operating margins are absorbing catastrophic financial losses, regulatory investigations, and permanent brand erosion.
Frequently Asked Questions (People Also Ask)
What caused the widespread internet and cybersecurity disruption today?
The disruption was triggered by a sophisticated, multi-vector exploit targeting widely utilized open-source software libraries within cloud compute supply chains. This enabled malicious code to propagate rapidly across authentication, DNS, and API services, bypassing perimeter security models and causing widespread service timeouts.
How are global financial markets and banking institutions responding?
Financial institutions activated emergency business continuity protocols, relying on redundant trading systems and localized failovers. Simultaneously, executive leadership teams are aggressively reallocating capital toward enhanced infrastructure resilience, continuous third-party risk auditing, and robust zero-trust security frameworks.
What long-term impacts will this event have on corporate governance and compliance?
Boardrooms are facing heightened accountability from regulatory bodies such as the SEC and international financial watchdogs. Corporations will be required to implement stricter incident reporting protocols, maintain verifiable multi-cloud redundancy, and conduct continuous security audits of all third-party software dependencies to avoid severe penalties.
Are small and medium-sized enterprises (SMEs) affected by this global cyber event?
Yes. While large enterprises experienced the most visible operational freezes, SMEs relying on third-party SaaS applications, cloud-based accounting platforms, and digital logistics tools faced severe downstream disruptions, highlighting the interconnected vulnerability of the modern digital ecosystem.
Future Outlook: Strategic Milestones to Watch
As emergency mitigation teams restore baseline operational status across the affected networks, the true work of systemic remediation begins. The events of today have permanently altered the calculus of digital commerce. Moving forward, market participants and enterprise leaders must monitor several critical milestones:
- Regulatory Enforcement Actions: Anticipate swift investigative findings from international financial and data protection regulators, likely resulting in stringent new compliance baselines for critical infrastructure providers.
- Insurance Market Restructuring: Watch for the introduction of new cyber insurance policy structures that explicitly exclude systemic cloud failures unless rigorous multi-cloud verification standards are met.
- Enterprise Architecture Overhaul: Track the acceleration of zero-trust adoption metrics and the migration away from monolithic, single-provider cloud architectures toward resilient, distributed multi-cloud frameworks.
Ultimately, the internet's "bad cybersecurity day" serves as a brutal, necessary wake-up call. In an economy where digital connectivity dictates market capitalization, systemic resilience is no longer an optional IT checkbox—it is the foundational prerequisite for economic survival.