Executive Takeaways
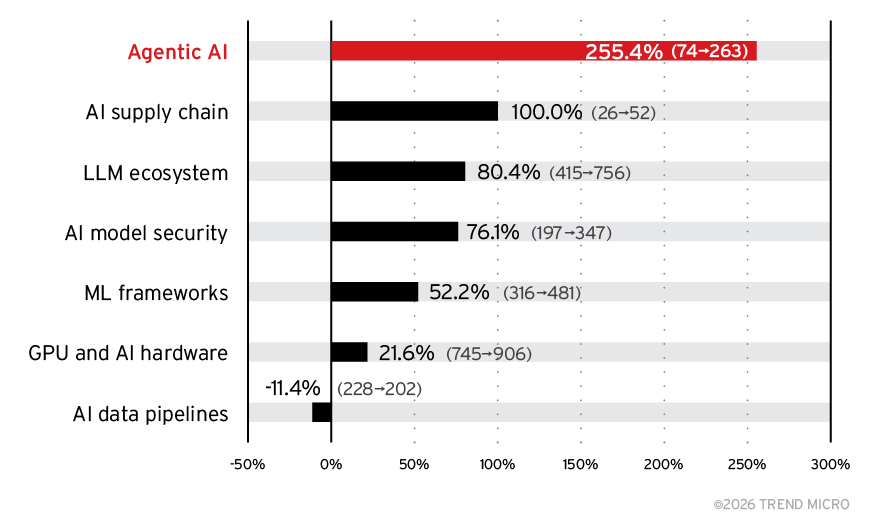
- AI as Ground Zero for Enterprise Risk: The second half of 2025 marked an inflection point where artificial intelligence shifted from an enterprise productivity catalyst to the primary corporate attack surface, according to Trend Micro’s TrendAI™ State of AI Security Report.
- Pervasive Machine Learning Supply Chain Compromise: Critical vulnerabilities embedded in open-source ML frameworks, serialized model weights, and containerized pipeline runtimes now expose Fortune 500 compute architectures to lateral network movement and remote code execution.
- Next-Generation Injection Tactics: Threat actors have transitioned beyond crude jailbreaks to sophisticated, layered prompt injection representations capable of evading static system guardrails and manipulating autonomous agentic workflows.
- Capital Allocation and Regulatory Exposure: Escalating adversarial risk is compressing enterprise AI valuation multiples, compelling chief risk officers to divert substantial digital-transformation budgets toward algorithmic runtime governance, zero-trust inference validation, and compliance with strict EU AI Act and SEC disclosure regimes.
When enterprise chief information officers authorized historic capital expenditure cycles between 2023 and 2025, the investment thesis was straightforward: deploy generative and agentic intelligence across customer workflows, compress human operating overhead, and accelerate enterprise ROI. However, an exhaustive investigation based on Trend Micro’s groundbreaking TrendAI™ State of AI Security Report reveals that this race for technological primacy outpaced foundational defense engineering, leaving deep systemic fault lines across the global AI ecosystem.
Throughout the latter half of 2025, artificial intelligence systems ceased to be speculative vectors for academic proof-of-concepts; they became ground zero for cyber warfare and corporate espionage. The vulnerabilities are not confined to superficial chatbot interfaces. Instead, they reside deep within the underlying plumbing: open-source model repositories, untrusted tensor deserialization frameworks, distributed inference infrastructure, and complex retrieval-augmented generation (RAG) pipelines.
The Anatomy of a Fracture: How ML Supply Chains Became Systemic Vectors
For decades, enterprise cybersecurity focused on defending traditional software supply chains—securing npm packages, verifying open-source C++ libraries, and scanning container images. The explosive adoption of foundational models, however, introduced an entirely unvetted dependency architecture. The modern enterprise AI tech stack relies on community-hosted model weights, pre-packaged orchestration frameworks, and specialized mathematical acceleration libraries, creating unprecedented vectors for silent, persistent exploitation.
Trend Micro’s threat intelligence highlights a rapid acceleration in adversarial actors weaponizing serialized model files. Historically, data scientists shared weights utilizing legacy serialization formats such as Python’s pickle, which inherently execute arbitrary code upon deserialization. While the industry pushed toward safer formats like safetensors, threat actors adapted in late 2025 by targeting the conversion utilities, loader dependencies, and dynamic quantization runtimes that enterprise teams rely on to optimize cloud compute architecture.
By compromising a single upstream repository hosting an ostensibly benign fine-tuned model, state-sponsored and financially motivated syndicates can execute poisoned parameter injection. This attack vector subtly alters specific model weights to create an algorithmic backdoor: the model behaves normally under standard enterprise benchmarking, yet reliably triggers malicious instruction sets or data exfiltration routines when presented with an adversary's specific cryptographic trigger phrase.
Guarding LLMs: The Shift Toward Layered Prompt Injection Representations
The most immediate and pervasive operational risk documented in the TrendAI™ investigation lies in the weaponization of Large Language Model (LLM) prompts. In early corporate deployments, security teams treated prompt injection as a simple input-sanitization problem, deploying elementary regex filters or basic blacklisting wrappers. That defensive paradigm has systematically collapsed.
Adversaries in the second half of 2025 deployed layered, multi-modal prompt injection payloads. Rather than attempting to bypass safety filters using single-stage, overt adversarial strings, modern attacks distribute malicious intent across fragmented semantic layers. An exploit payload can be split across benign user queries, multi-modal image metadata, external web documents indexed via RAG pipelines, and conversational context windows. When an autonomous enterprise agent aggregates these disparate inputs, the model reconstructs the adversarial command internally, executing unauthenticated API calls, altering database records, or exfiltrating privileged corporate context.
In response, Trend Micro’s research underscores the imperative of Layered Prompt Injection Representation. Defending modern LLMs requires breaking free from monolithic guardrails in favor of deep architectural inspection. This involves analyzing semantic intent at multiple abstraction layers: token probability distribution, semantic vector space clustering, and dynamic downstream tool invocation monitoring. Without this layered telemetry, enterprise AI agents operating across enterprise resource planning (ERP) and customer relationship management (CRM) databases remain fundamentally indefensible.
Enterprise Exposure: Attack Surface Dynamics in the H2 2025–2026 Cycle
The operational and financial ramifications of these AI ecosystem vulnerabilities are stark. The table below delineates the primary systemic threat vectors identified in recent intelligence data, their operational mechanics, and their direct impact on enterprise balance sheets and regulatory compliance profiles.
| Threat Vector | Primary Exploitation Vector | Prevalence Growth (H2 2025) | Mean Time to Detect (MTTD) | Regulatory & Financial Impact Exposure |
|---|---|---|---|---|
| Adversarial Model Poisoning | Contaminated public fine-tuning datasets and upstream serialized weight tampering. | +184% YoY | 182 Days | Direct violation of EU AI Act Art. 15; invalidates enterprise IP; severe capital write-downs. |
| Layered Indirect Prompt Injection | Adversarial payloads embedded in untrusted RAG corporate data ingestion streams. | +312% YoY | 14 Days | Unauthorized database modification; data leakage subject to GDPR and SEC disclosure mandates. |
| Inference Runtime Exploits | Memory corruption and buffer overflows in Triton, vLLM, and CUDA-accelerated serving stacks. | +96% YoY | 41 Days | Full container escape, lateral enterprise network movement, compute infrastructure theft. |
| Autonomous Agent Hijacking | Privilege escalation via unbounded tool-use frameworks and synthetic session manipulation. | +240% YoY | 9 Days | Unauthorized transactional settlement, illicit API token harvesting, enterprise workflow disruption. |
Capital Allocation, Valuation Multiples, and the Corporate Realignment
The discovery of these deep fault lines has triggered a fundamental reassessment across institutional boardrooms, venture capital syndicates, and private equity firms. The initial era of unconstrained AI capital deployment—where public markets rewarded companies purely on compute expenditure announcements—has abruptly ended. Enterprise valuation multiples are increasingly decoupled from raw AI deployment velocity and are now anchored to operational resilience, algorithmic provenance, and quantifiable risk mitigation.
Chief Financial Officers and audit committees now face a severe underwriting challenge. The corporate liability of an undetected model vulnerability extends far beyond traditional intellectual property theft. Under contemporary regulatory enforcement—such as the operational resilience mandates of the European Union’s AI Act and heightened SEC public-company incident disclosure rules—an unchecked algorithmic failure resulting in unauthorized market manipulation or mass data leakage carries non-negotiable statutory penalties alongside reputational destruction.
Consequently, institutional capital is pivoting aggressively toward runtime governance. Chief Information Security Officers (CISOs) are renegotiating master service agreements with foundational model providers and hyperscalers, demanding hardware-enforced isolation, zero-trust token provenance, and strict software bill of materials (SBOM) coverage that encompasses weights, training datasets, and inference microservices. Specialized cybersecurity vendors capable of delivering deep, non-invasive runtime observability for AI pipelines are capturing premium budget allocations originally earmarked for raw model experimentation.
Frequently Asked Questions (People Also Ask)
What are the primary "fault lines" identified in the TrendAI™ State of AI Security Report?
The fault lines encompass systemic vulnerabilities spanning the entire machine learning lifecycle. These include untrusted open-source dependencies in the ML supply chain, serialized model weights carrying hidden execution payloads, vulnerable containerized inference servers, and sophisticated, multi-stage prompt injection attacks capable of hijacking autonomous enterprise agents connected to mission-critical backend systems.
How does layered prompt injection evade traditional enterprise security guardrails?
Traditional guardrails inspect raw textual inputs against established blacklists, static heuristics, or superficial classifier models. Layered prompt injection attacks circumvent these checks by deconstructing adversarial payloads across multiple modalities, token fragments, or external data repositories utilized in retrieval-augmented generation (RAG). When the host model ingests and reconstructs these disparate inputs into a single contextual window, the adversarial payload executes internally, bypassing exterior perimeter defenses entirely.
How do ML supply chain attacks affect enterprise cloud infrastructure?
Because enterprise data science environments often enjoy elevated permissions to interact with distributed storage buckets, high-performance computing clusters, and proprietary data lakes, an exploit executed through an ML framework or compromised model loader can lead to full container escapes. Threat actors leverage these footholds to execute lateral network movement, exfiltrate sensitive corporate telemetry, or commandeer costly GPU infrastructure for illicit cryptomining and secondary attacks.
What regulatory liabilities do enterprises face if their AI models are compromised?
Organizations face aggressive regulatory scrutiny under global frameworks including the EU AI Act, the FTC’s algorithmic fairness and security mandates, and the SEC’s mandatory cyber incident disclosure regulations. Failures stemming from unverified training datasets, compromised model integrity, or unauthorized data dissemination can result in statutory fines reaching up to €35 million or 7% of global annual turnover, alongside mandatory algorithmic disgorgement—the legally forced deletion of compromised models and their associated weights.
Future Outlook: Navigating the Post-Euphoria Security Landscape
As enterprises navigate the remainder of 2026, the artificial intelligence landscape is entering an era of sober technical accountability. The structural vulnerabilities cataloged in Trend Micro’s TrendAI™ State of AI Security Report demonstrate that treating advanced algorithmic systems as isolated, self-securing software components is an unsustainable strategy that invites catastrophic enterprise exposure.
Over the next eighteen months, market leadership will bifurcate. Organizations that invest early in verifiable model provenance, cryptographic model watermarking, continuous autonomic red-teaming, and layered prompt injection representations will successfully insulate their operational margins and maintain customer trust. Conversely, organizations that prioritize rapid deployment over structural runtime defense will find themselves increasingly uninsurable, subject to aggressive regulatory enforcement, and exposed to sophisticated adversaries dedicated to exploiting the delicate, widening fault lines of the global AI ecosystem.