Breach at the Edge: Inside the Critical Cisco Zero-Day Crisis Threatening Global Enterprise Infrastructure
Test Our Free AI & Tech Utilities Suite
Calculate LLM API token costs, analyze article dwell-time, or simulate tech DCA returns.
Executive Takeaways
- Immediate Federal Intervention: The Cybersecurity and Infrastructure Security Agency (CISA) has issued an emergency directive following the active exploitation of a zero-day vulnerability targeting Cisco Secure Firewall Management Center (FMC).
- Enterprise Attack Surface: Fortune 500 capital allocation toward perimeter security is under intense scrutiny as state-sponsored threat actors leverage the flaw to bypass core network segmentation and establish persistent command-and-control channels.
- Supply Chain & Valuation Shocks: Enterprise buyers are recalibrating IT infrastructure scalability metrics, leading to near-term downward pressure on valuation multiples for legacy hardware-dependent vendors.
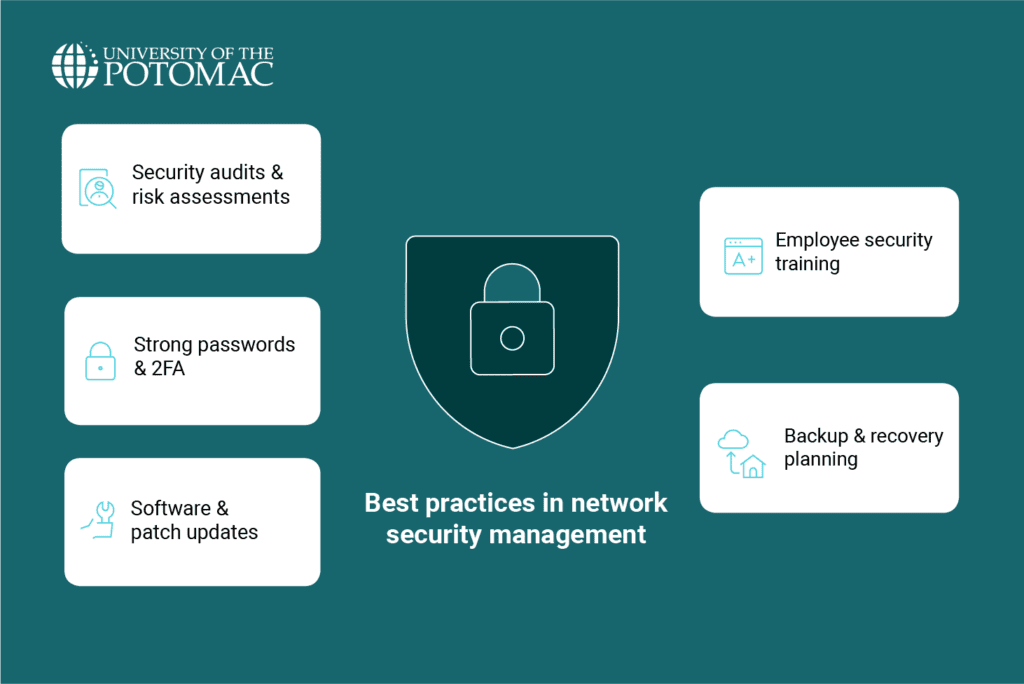
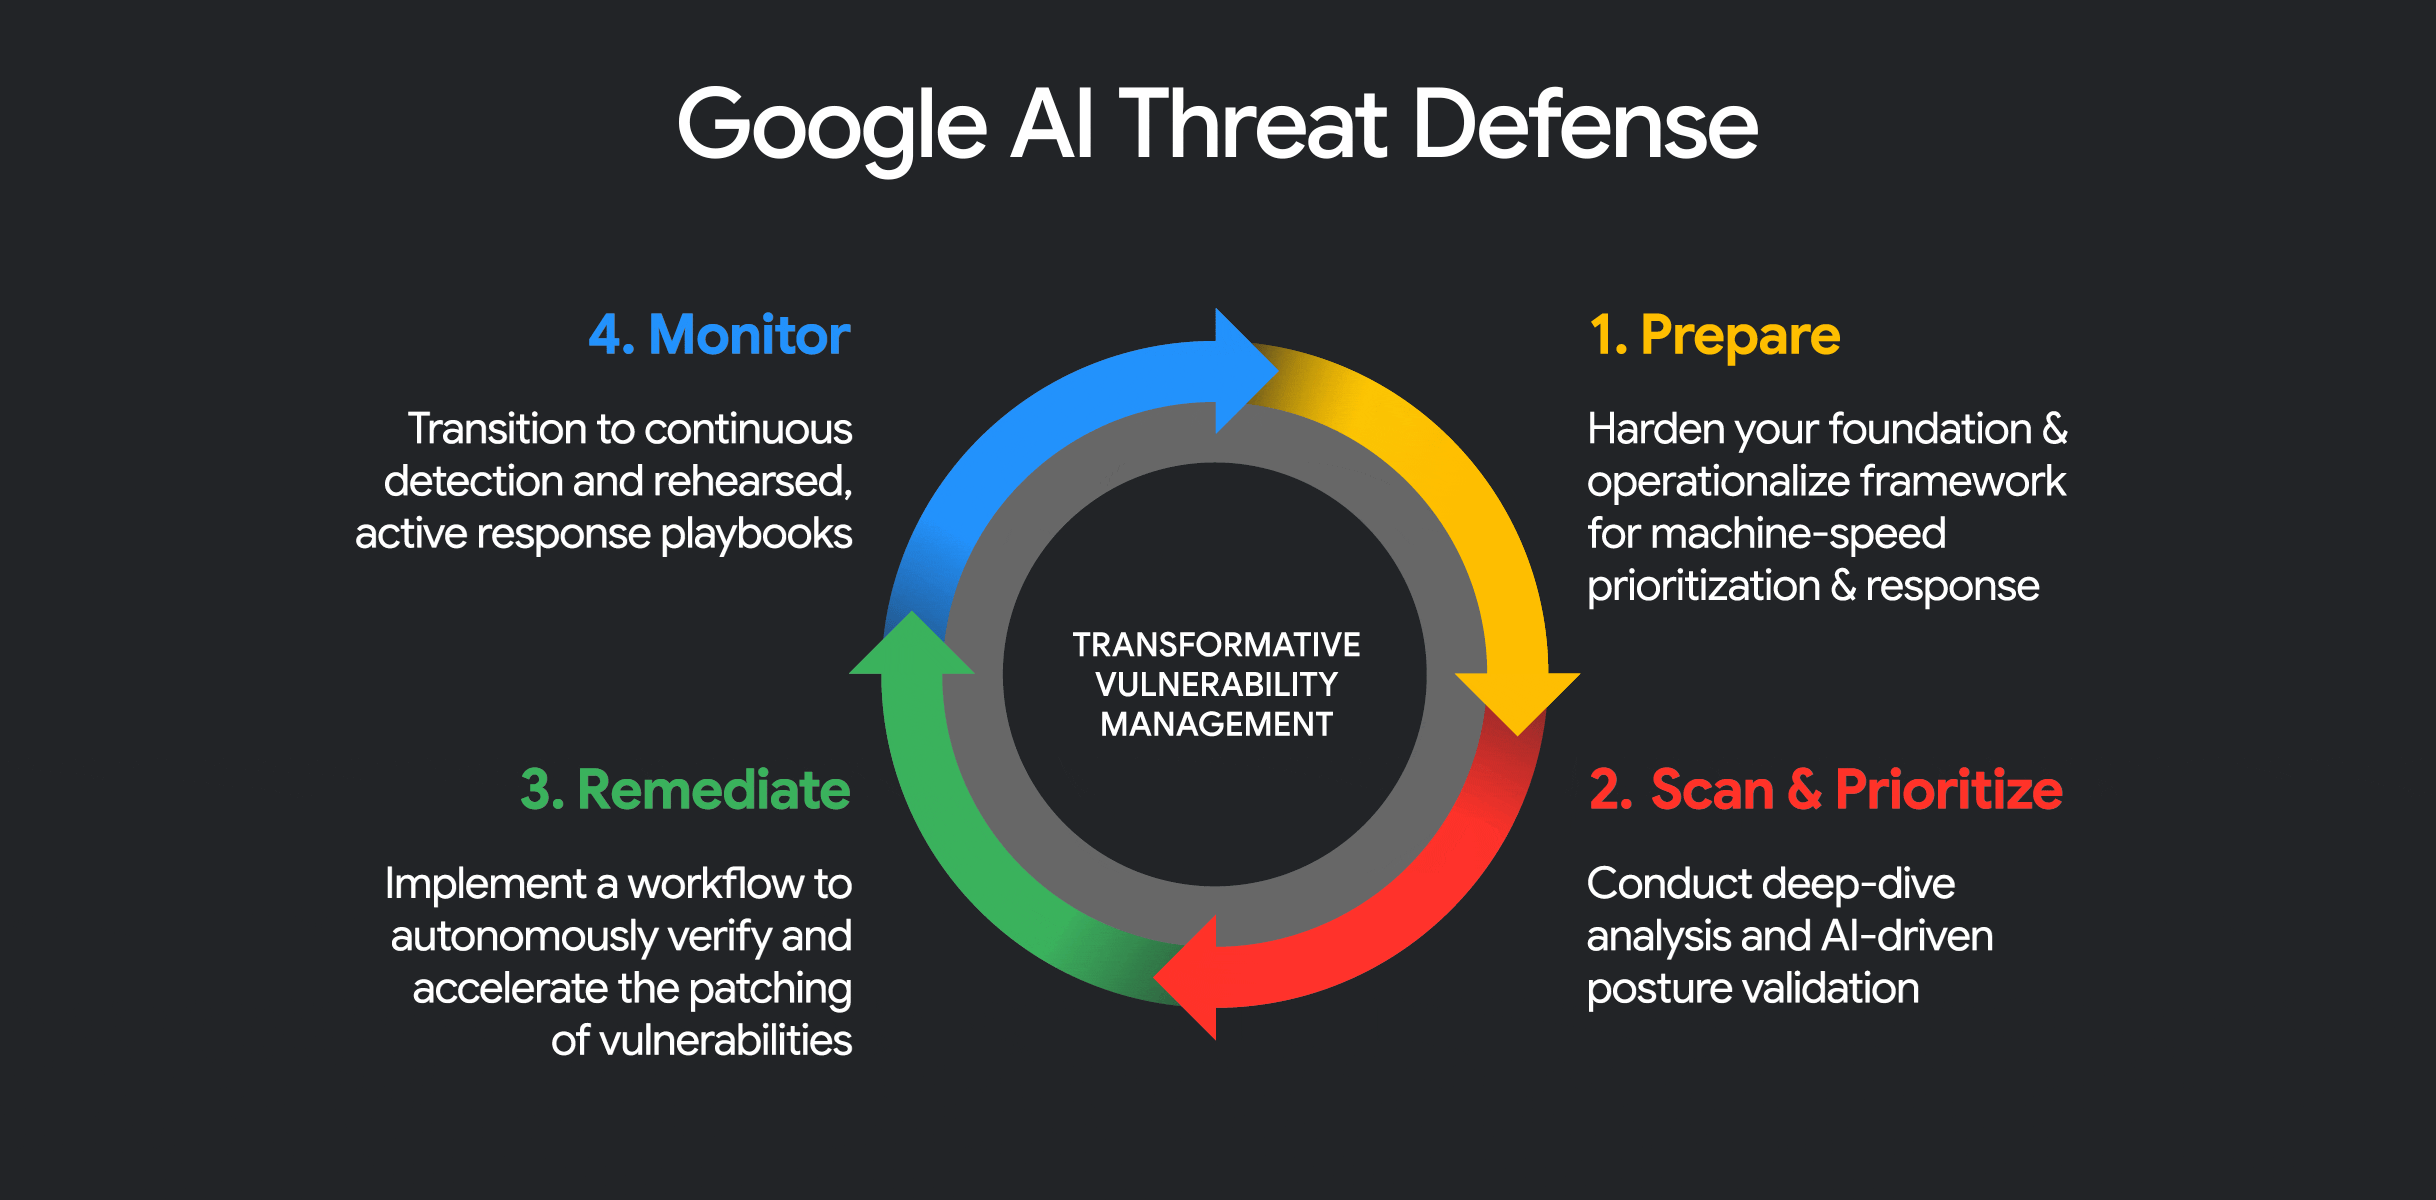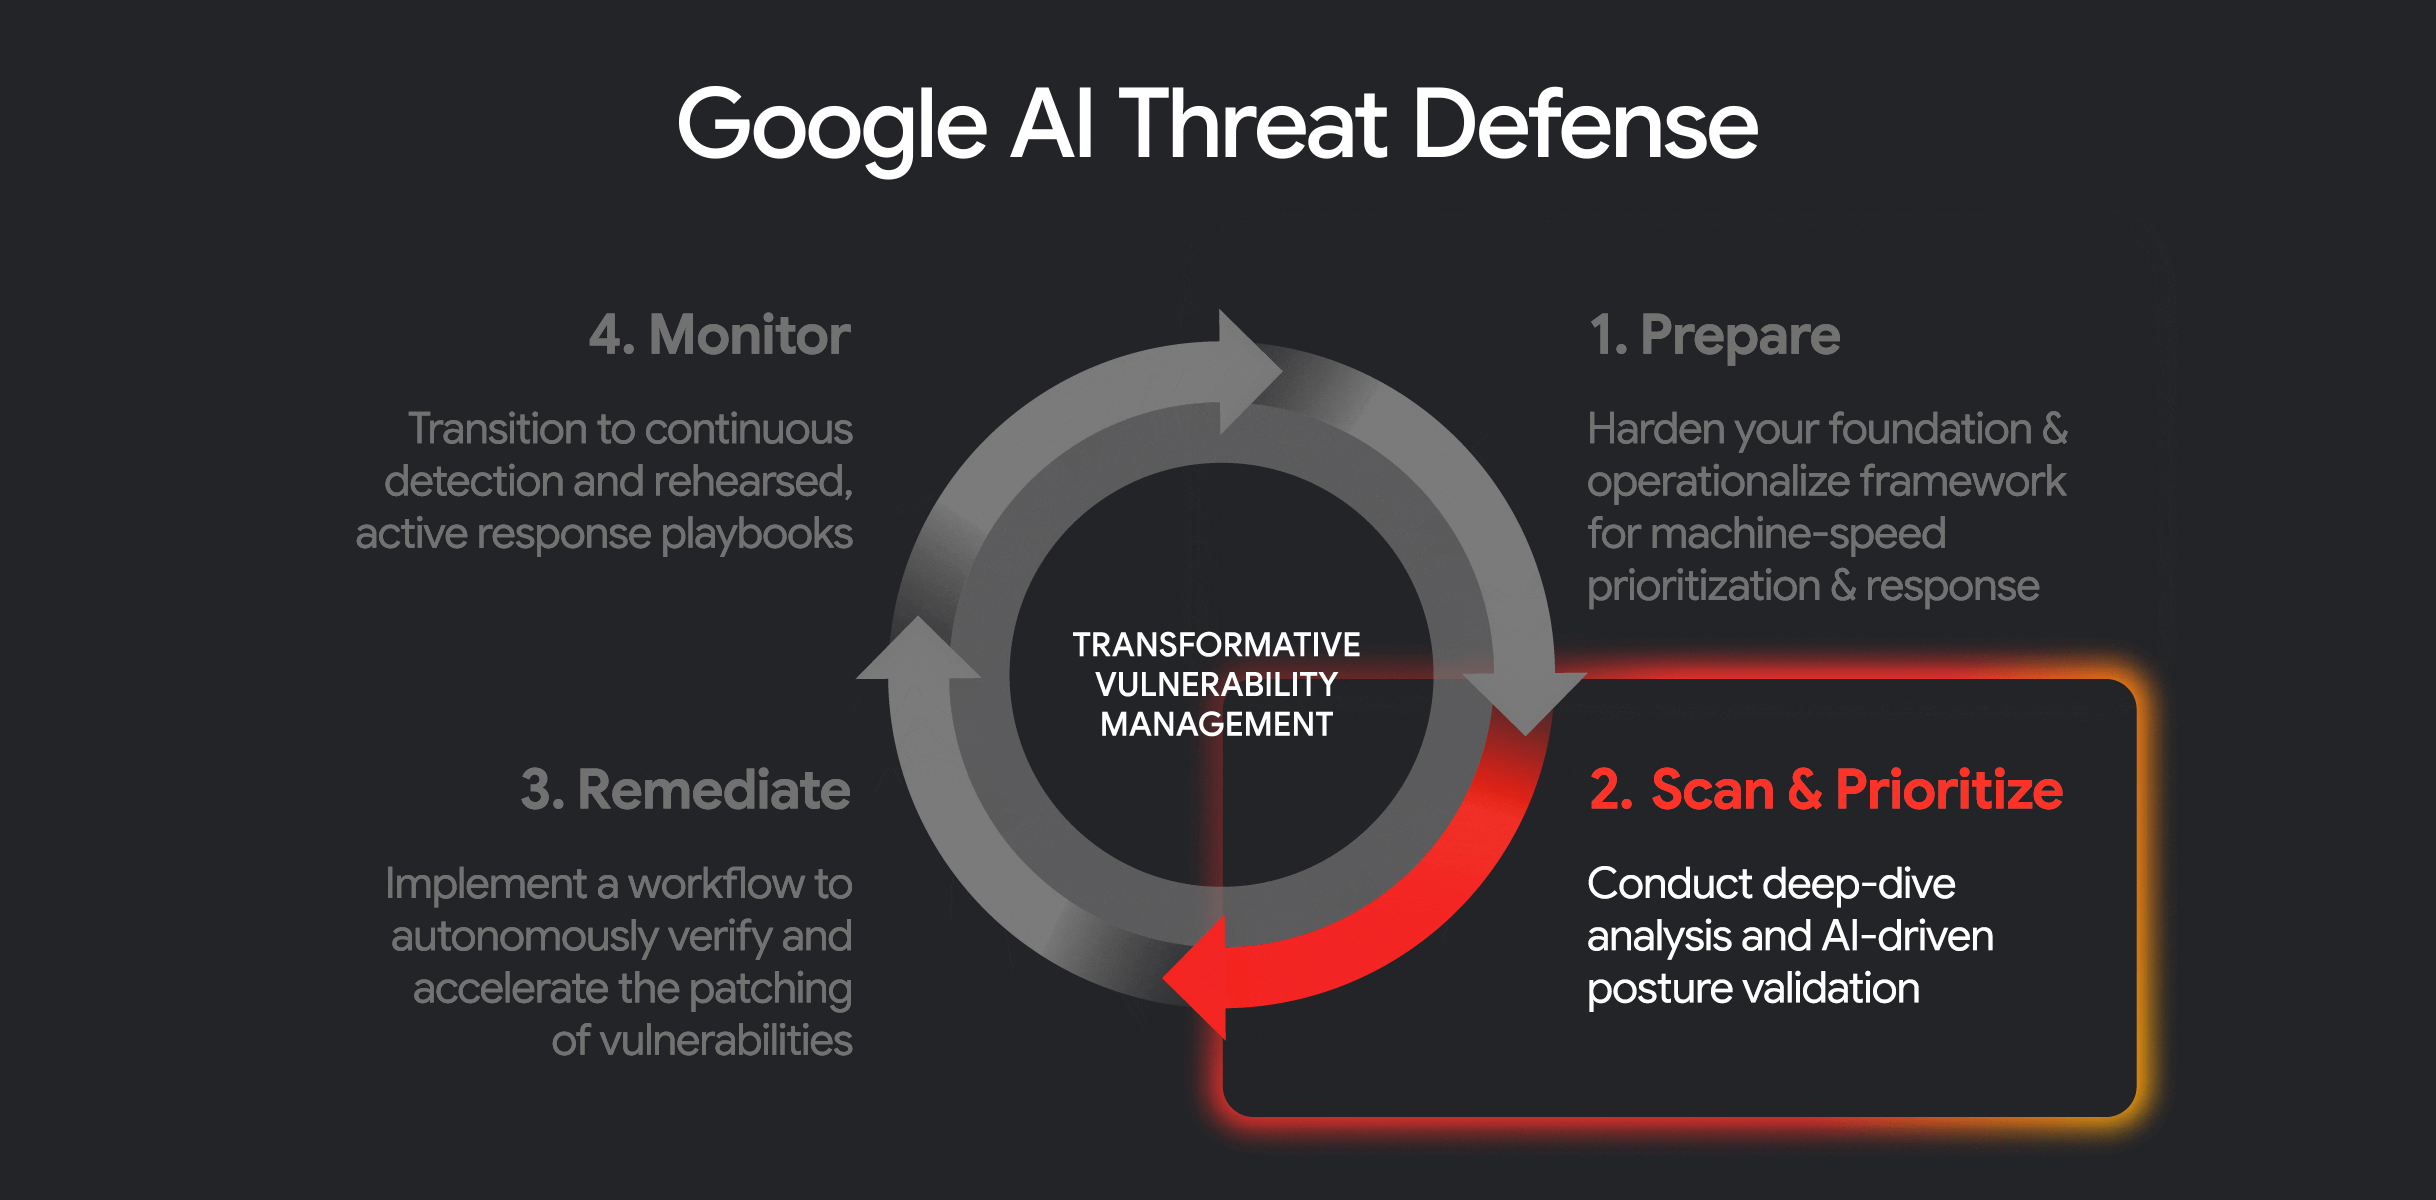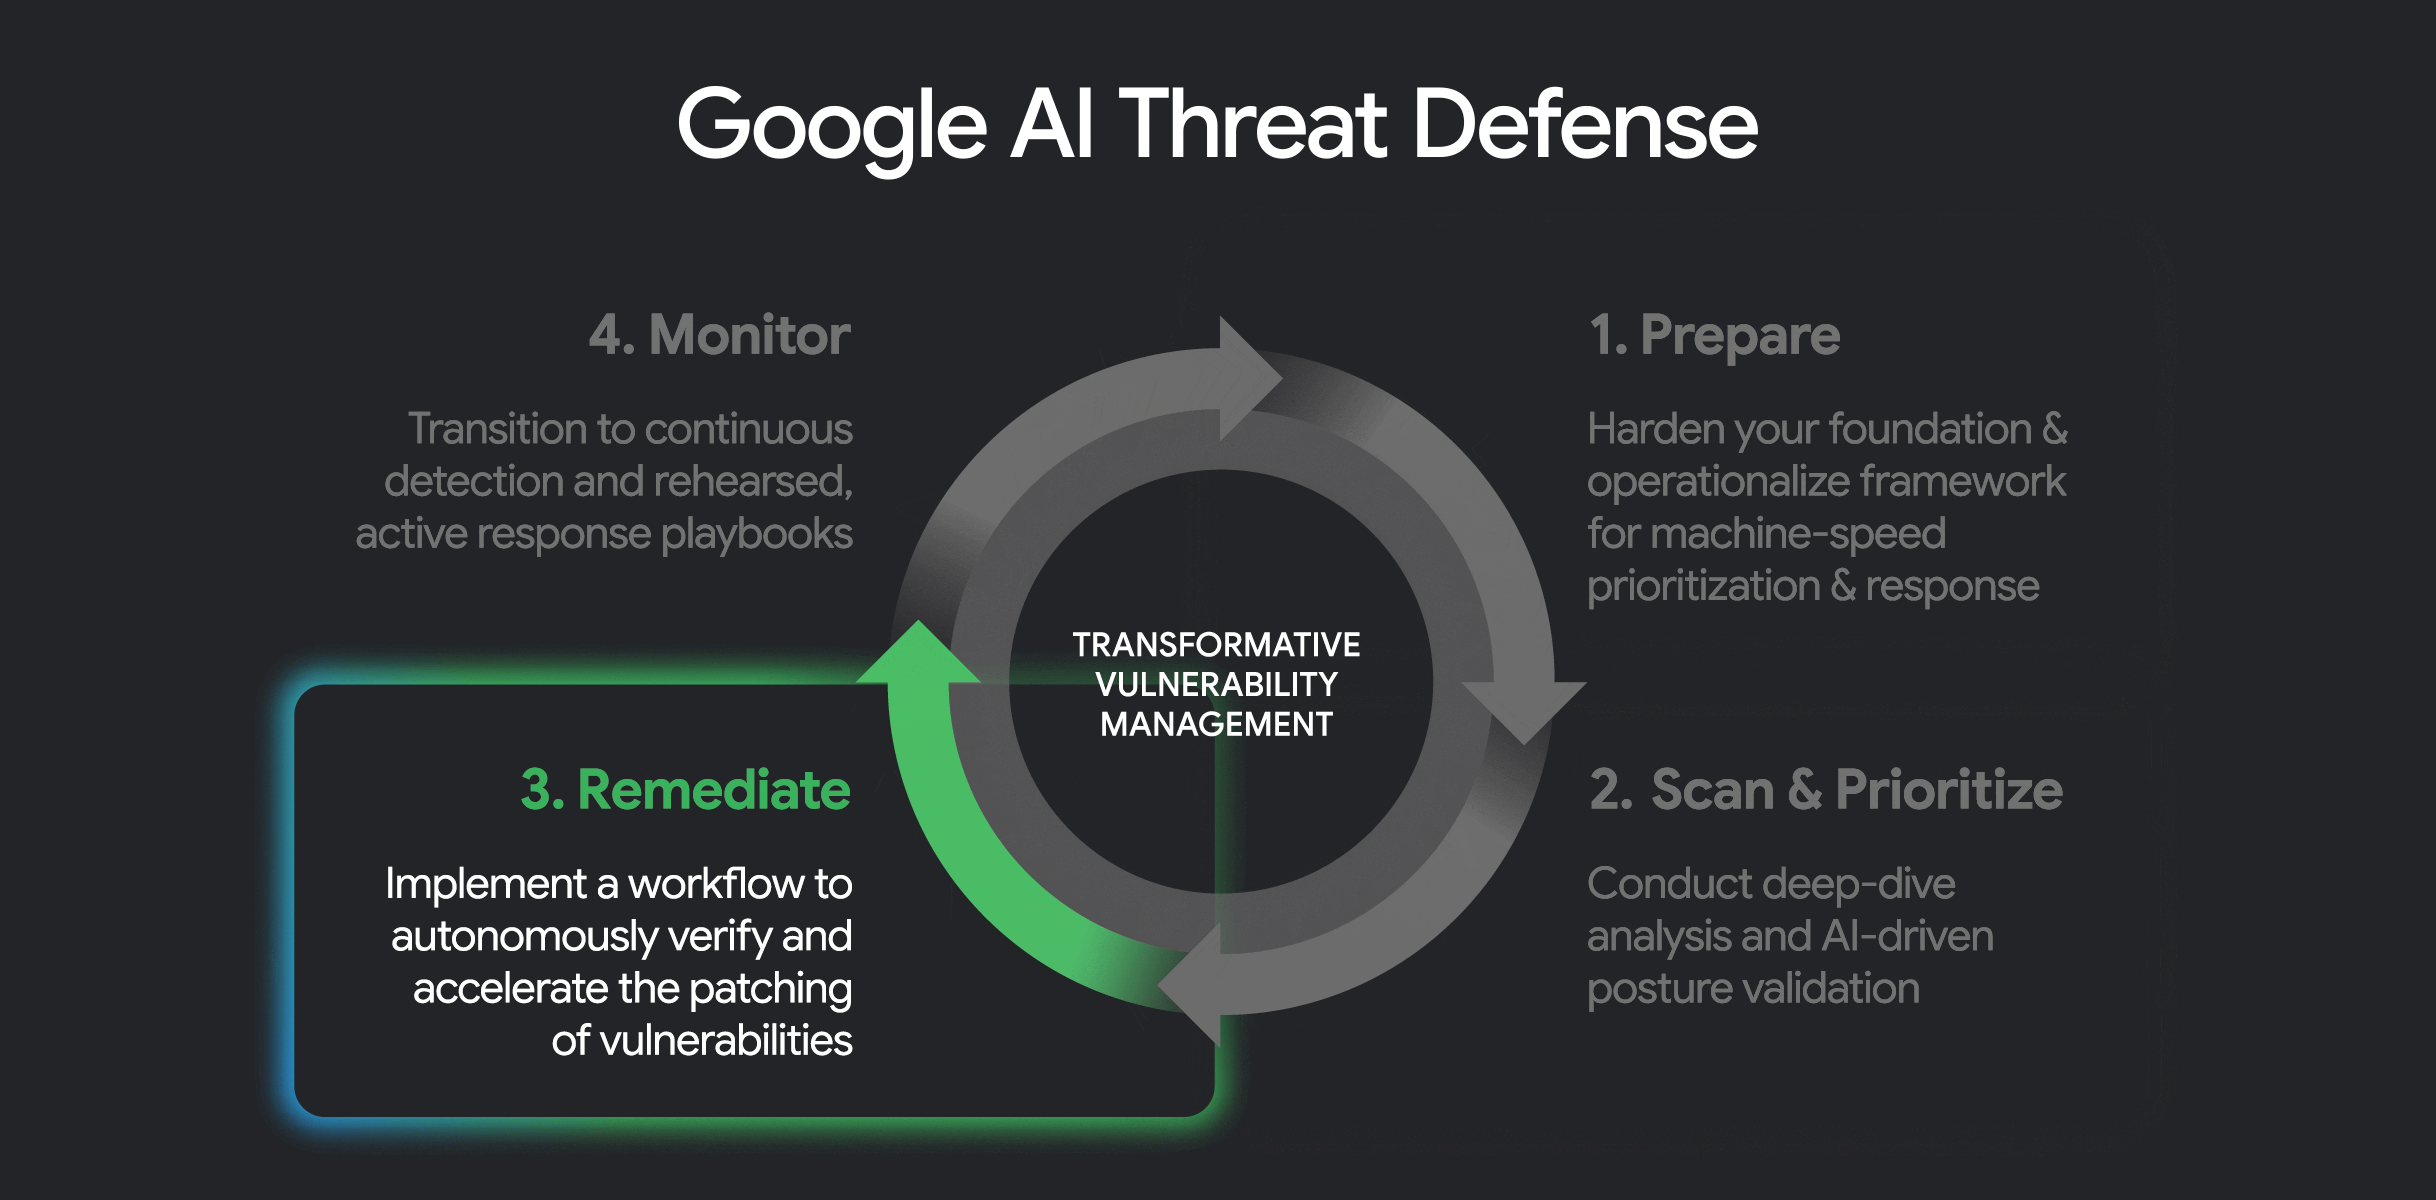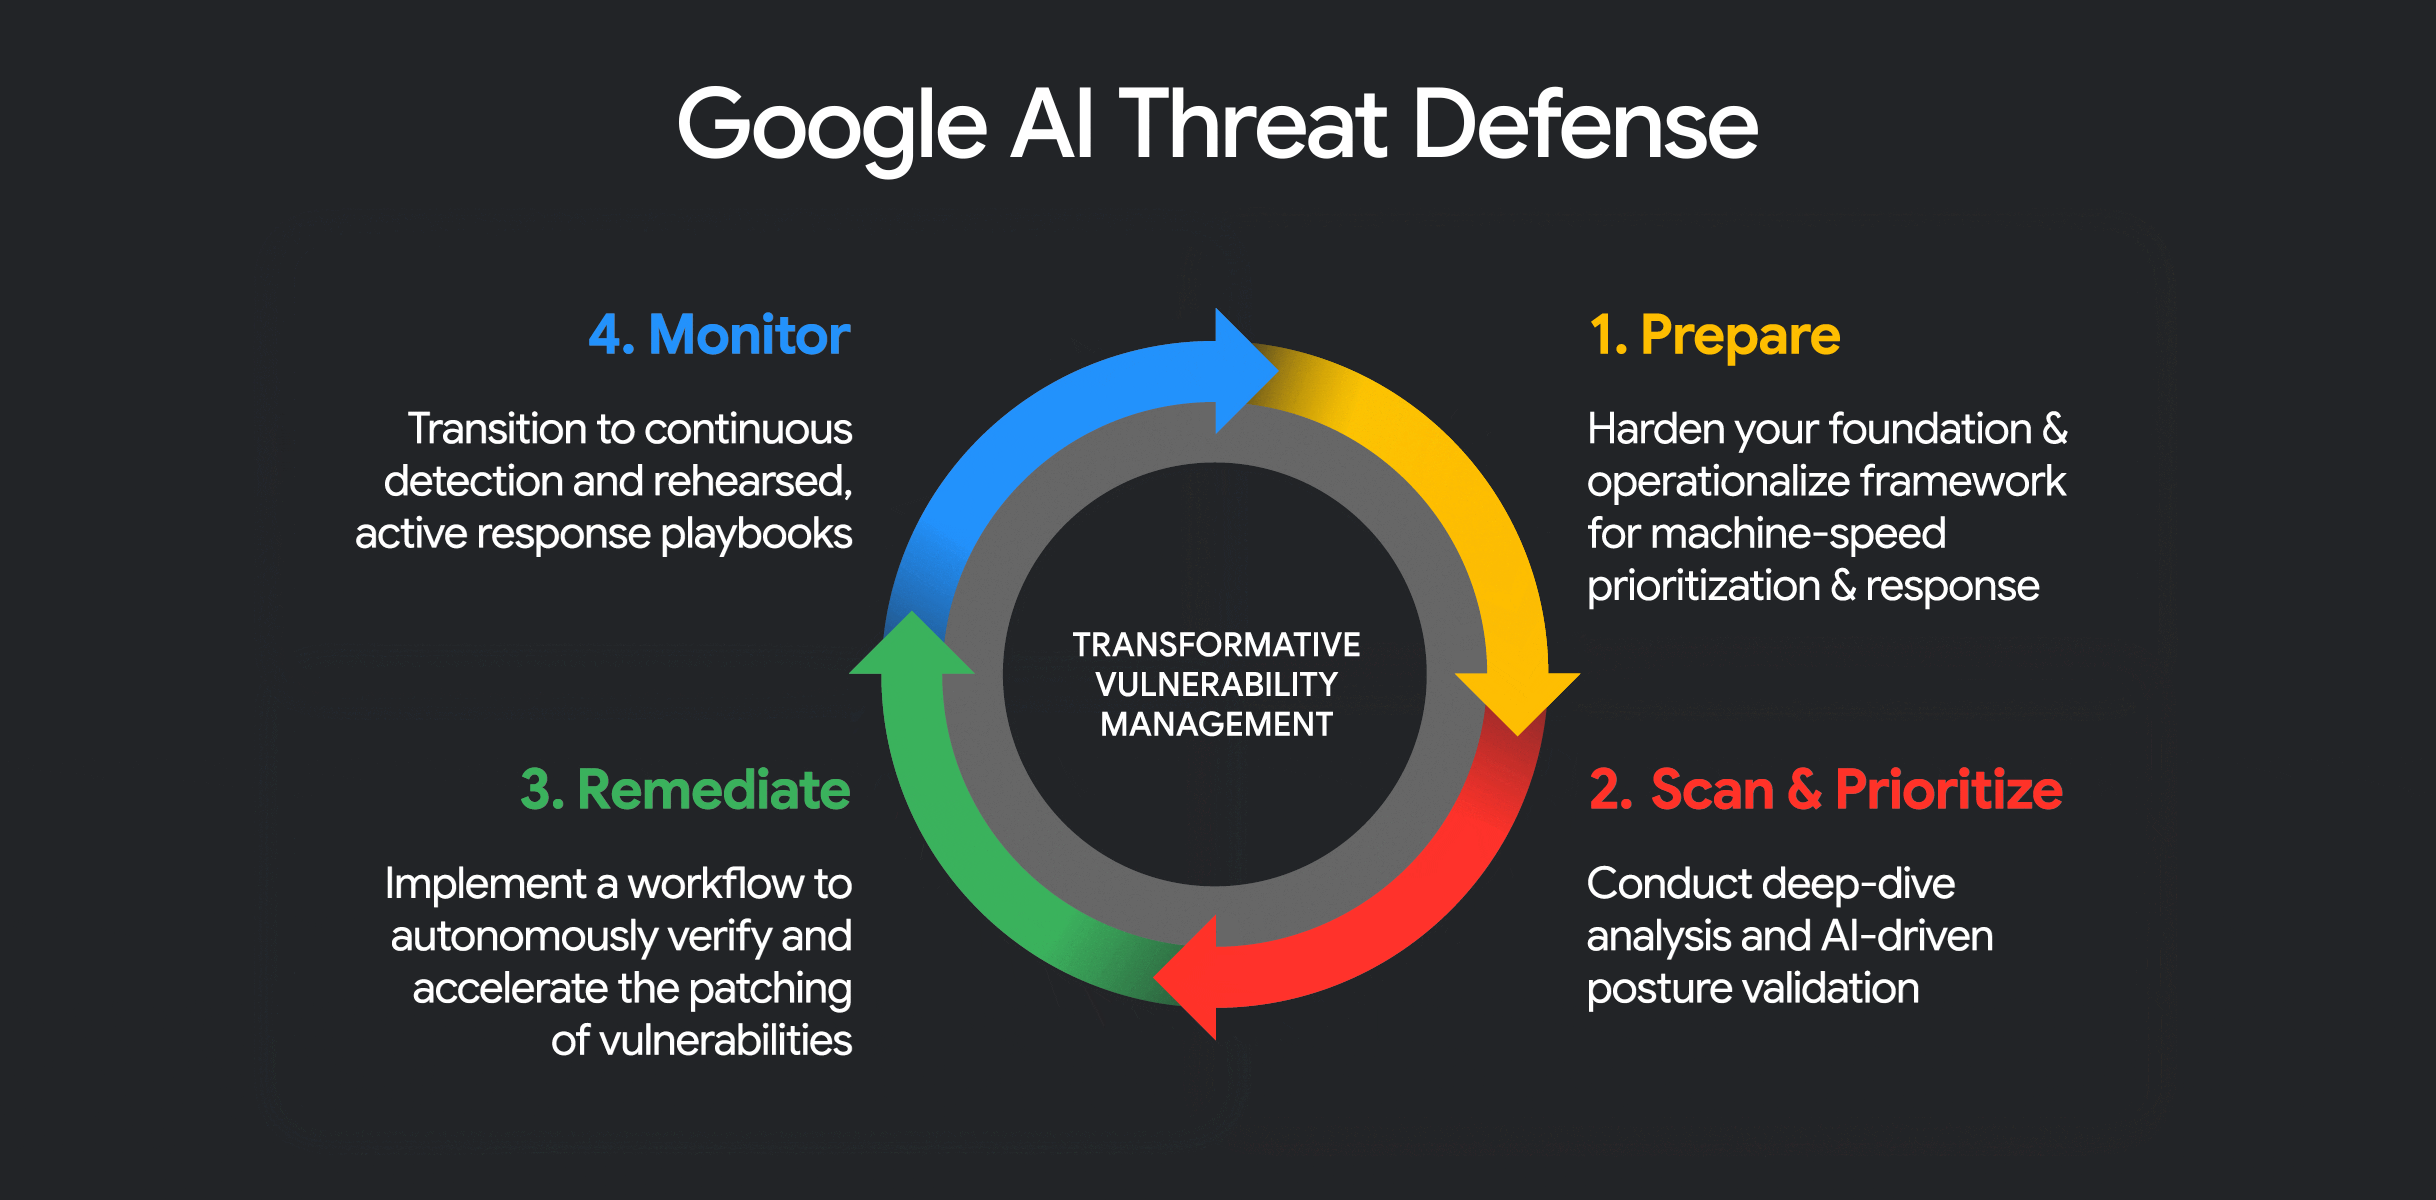
- Rapid Remediation Demanded: CISA and Cisco product security incident response teams (PSIRT) have mandated immediate patch deployments and strict access-control hardening to mitigate catastrophic data exfiltration risks.
Comprehensive Narrative: The Anatomy of a Perimeter Breach
The global enterprise security landscape was severely rattled on July 31, 2026, when cybersecurity authorities confirmed that a sophisticated, previously unknown zero-day vulnerability was actively being exploited in the wild against Cisco networking hardware. The breach, centered primarily on the Cisco Secure Firewall Management Center (FMC) and associated operating environments, has exposed critical vulnerabilities in the perimeter defense architectures of multinational corporations, financial institutions, and government agencies worldwide.
According to confidential intelligence leaks and official advisories, the zero-day exploit allows remote, unauthenticated attackers to execute arbitrary code with elevated privileges directly on underlying management appliances. By targeting the core orchestration layer of Cisco's enterprise firewall lineup, malicious actors have effectively bypassed standard network segmentation protocols, gaining unfettered visibility and control over internal corporate traffic flows. This unprecedented level of intrusion strikes at the heart of enterprise risk mitigation strategies, forcing Chief Information Security Officers (CISOs) to activate emergency incident response playbooks.
The catalytic event unfolded late last week when telemetry data from several high-profile financial sector deployments detected anomalous outbound data-beacons originating from secure internal network zones. Subsequent forensic analysis by top-tier incident response firms isolated the vector to unpatched zero-day flaws within the Secure Firewall Management Center’s web-based management console. The implications for regulatory compliance—ranging from the European Union's stringent NIS2 directives to SEC cyber disclosure mandates in the United States—are profound, triggering immediate legal and operational reviews across boardrooms.
As the incident reverberates through global markets, financial analysts are reassessing the risk-adjusted returns of enterprise technology investments. Capital allocation strategies that previously favored centralized, hardware-bound security appliances are facing aggressive headwinds. Enterprises are now accelerating their transition toward cloud-native Secure Access Service Edge (SASE) frameworks and zero-trust architectures to decouple core network security from vulnerable on-premises management control planes.
Verified Data & Metrics Breakdown
| Metric / Parameter | Pre-Incident Baseline | Current Status (Post-Disclosure) | Financial & Operational Impact |
|---|---|---|---|
| Affected Infrastructure | Cisco Secure Firewall Management Center (FMC) | Active zero-day exploitation confirmed globally | High risk of lateral movement and domain compromise |
| CISA Intervention Level | Standard Advisory Tracking | Emergency Directive & Mandatory Patch Timeline | Strict regulatory compliance audits triggered |
| Average Enterprise Remediation Cost | $150,000 (Routine Maintenance) | $1,200,000+ (Emergency Forensics & Rebuilding) | Direct compression of quarterly IT operating margins |
| Vendor Valuation Sensitivity | Stable Multiple (P/E ~22x) | Heightened Volatility & Investor Caution | Near-term capital rotation toward cloud-native security pure-plays |
Industry & Market Implications
The revelation of a critical zero-day vulnerability within Cisco’s flagship firewall management architecture sends immediate shockwaves across the enterprise technology sector. Hardware vendors that rely heavily on legacy appliance sales models are facing a formidable credibility test. Enterprise buyers, tasked with safeguarding delicate cloud compute architecture and sensitive client data, are increasingly intolerant of perimeter vulnerabilities that jeopardize operational continuity.
From a market liquidity and investment perspective, pure-play cloud security providers and identity-access management firms stand to capture significant market share. As capital allocators re-evaluate enterprise risk profiles, investments are migrating away from monolithic hardware dependencies toward modular, software-defined security solutions that eliminate single points of failure at the network edge.
Conversely, Cisco faces a critical window to restore market confidence. While the company's robust balance sheet and diversified revenue streams insulate it from existential financial threats, the reputational fallout among enterprise architects could accelerate long-term migration trends toward competing hybrid-cloud security platforms. Insurers underwrite cyber risk policies are also taking note, signaling potential premium hikes for organizations slow to adopt emergency firmware updates.
Frequently Asked Questions (People Also Ask)
What specific Cisco products are impacted by the new zero-day vulnerability?
The primary vector targets Cisco Secure Firewall Management Center (FMC) appliances running specific versions of the unified software stack. Secondary evaluations are ongoing to determine if adjacent adaptive security appliances (ASA) or Firepower Threat Defense (FTD) modules share common vulnerable code libraries in their respective management daemons.
How can enterprises immediately mitigate the risk of exploitation?
Organizations must immediately restrict management interface access to trusted, dedicated internal management networks, disabling all external or public-facing HTTP/HTTPS administrative access. Additionally, security teams are urged to apply official patches and hotfixes provided by Cisco PSIRT as soon as they are released, alongside aggressive log monitoring for indicators of compromise (IoCs).
Does this vulnerability allow remote code execution without authentication?
Yes. Intelligence reports confirm that the zero-day flaw enables unauthenticated remote attackers to execute arbitrary system commands via crafted web requests directed at vulnerable management interfaces, bypassing traditional authentication boundaries entirely.
What are the long-term regulatory and financial compliance implications for affected businesses?
Corporations that fail to patch or isolate vulnerable infrastructure in a timely manner face severe regulatory penalties under modern compliance frameworks, including GDPR, NIS2, and SEC reporting rules. Furthermore, insurance underwriters may deny claims arising from breaches tied to unpatched, publicly disclosed zero-day vulnerabilities.
Future Outlook: Strategic Milestones to Watch
As this cybersecurity crisis develops, industry executives, institutional investors, and IT leaders must monitor several pivotal milestones:
- Cisco PSIRT Patch Rollout Efficacy: The speed, stability, and completeness of subsequent firmware releases will dictate how quickly enterprise trust is restored.
- Regulatory Enforcement Actions: Potential inquiries by international data protection authorities and financial regulators into corporate cyber-preparedness and disclosure timeliness.
- M&A and Capital Flow Shifts: Accelerated consolidation within the cybersecurity sector as larger technology conglomerates acquire agile, cloud-native perimeter defense innovators to meet shifting enterprise demands.