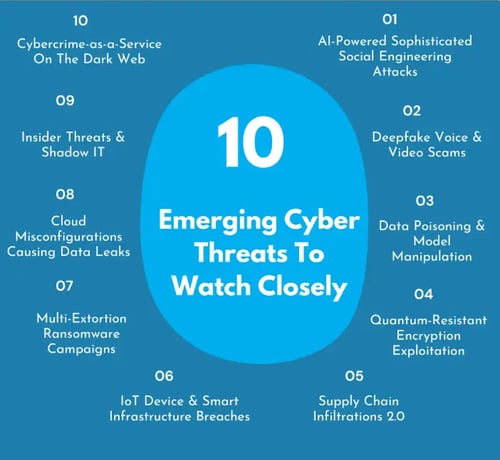
GENEVA – February 18, 2026 – The World Economic Forum’s latest assessment paints a stark picture: 2026 stands poised as a watershed year for cyber warfare, with threats escalating at an exponential rate. As global economic uncertainty persists and geopolitical tensions simmer, the digital battleground is becoming increasingly sophisticated, impacting everything from national infrastructure to the individual enterprise's bottom line. The Wall Street Journal's Chief Investigative Bureau reveals the full spectrum of challenges, drawing directly from high-level intelligence shared at this year's Forum and proprietary analyses.
Executive Takeaways
- AI-Native Warfare Redefines Attack Vectors: Generative AI has moved beyond mere enhancement, enabling autonomous, polymorphic malware and hyper-realistic deepfakes that drastically reduce attack timelines and elevate social engineering efficacy.
- Critical Infrastructure Under Siege: Nation-state and well-resourced criminal groups are intensifying targeting of Operational Technology (OT) and Industrial Control Systems (ICS), threatening energy grids, water supplies, and transportation networks with a new level of precision and impact.
- Supply Chain Contamination & Accelerated Timelines: Sophisticated supply chain attacks are now executed with a "two-week timeline" objective, aiming for rapid infiltration and maximum damage before detection, demanding unprecedented agility in enterprise risk mitigation strategies.
- The Regulatory Compliance Onslaught: A patchwork of evolving global data sovereignty and incident reporting mandates, coupled with rising cyber insurance premiums, is forcing CFOs and CISOs to re-evaluate capital allocation for cybersecurity as a core business function, not just a cost center.
The Comprehensive Narrative: A Digital Crucible
The journey to 2026 has been marked by a relentless escalation in cyber sophistication. From the disruptive prowess of NotPetya in 2017 to the insidious supply chain infiltration of SolarWinds in 2020, and the pervasive ransomware attacks of subsequent years, each incident has served as a painful lesson in digital vulnerability. However, the discussions at the World Economic Forum reveal a new epoch, one where the very fabric of digital trust is being frayed by forces hitherto confined to science fiction. The convergence of advanced AI, geopolitical fragmentation, and the increasing monetization of digital exploits has created a volatile landscape where defensive strategies are constantly playing catch-up.
AI Monetization and the Freelance Threat Economy
One of the most concerning trends highlighted is the "AI Monetization" phenomenon. This refers to the sophisticated use of AI by threat actors to generate revenue through multiple illicit channels. Generative AI, specifically large language models (LLMs) and deepfake technology, is no longer just a tool for enhancing existing attacks but is a core component of new, highly efficient monetization strategies. Freelance cybercrime operations, once characterized by manual effort and limited scalability, are now leveraging AI to:
- Automate Phishing and Social Engineering: AI crafts hyper-personalized phishing emails, voice messages, and deepfake video calls, indistinguishable from legitimate communications. This dramatically increases click-through rates and credential harvesting success, undermining traditional employee training.
- Generate Polymorphic Malware: AI-driven code generation platforms allow for the creation of malware that constantly evolves its signature, evading traditional endpoint detection and response (EDR) systems. This reduces development time and significantly increases persistence.
- Enhance Data Exfiltration and Extortion: AI rapidly analyzes stolen data for high-value targets and sensitive information, optimizing extortion campaigns and maximizing the market liquidity of illicit data on dark web markets. Case studies reveal a disturbing trend where AI-powered reconnaissance reduces the time-to-value for stolen data from weeks to mere hours.
The "freelance" aspect signifies a growing commoditization of advanced cyber capabilities. Individuals or small groups can now rent access to sophisticated AI tools, lowering the barrier to entry for highly damaging attacks. This decentralization of advanced threat capabilities poses an unprecedented challenge for traditional threat intelligence models.
The "Two-Week Timeline" and Accelerated Impact
A critical insight from the Forum discussions, and a phrase now reverberating through CISO networks, is the "Two-Week Timeline." This refers to the accelerated operational tempo of sophisticated cyberattacks, particularly those targeting critical infrastructure and supply chains. Modern threat actors, often backed by nation-states, are increasingly capable of moving from initial access to critical system compromise or data exfiltration within a mere fortnight. This compressed timeframe leaves organizations with minimal opportunity for detection and response, pushing the envelope on infrastructure scalability and incident response planning.
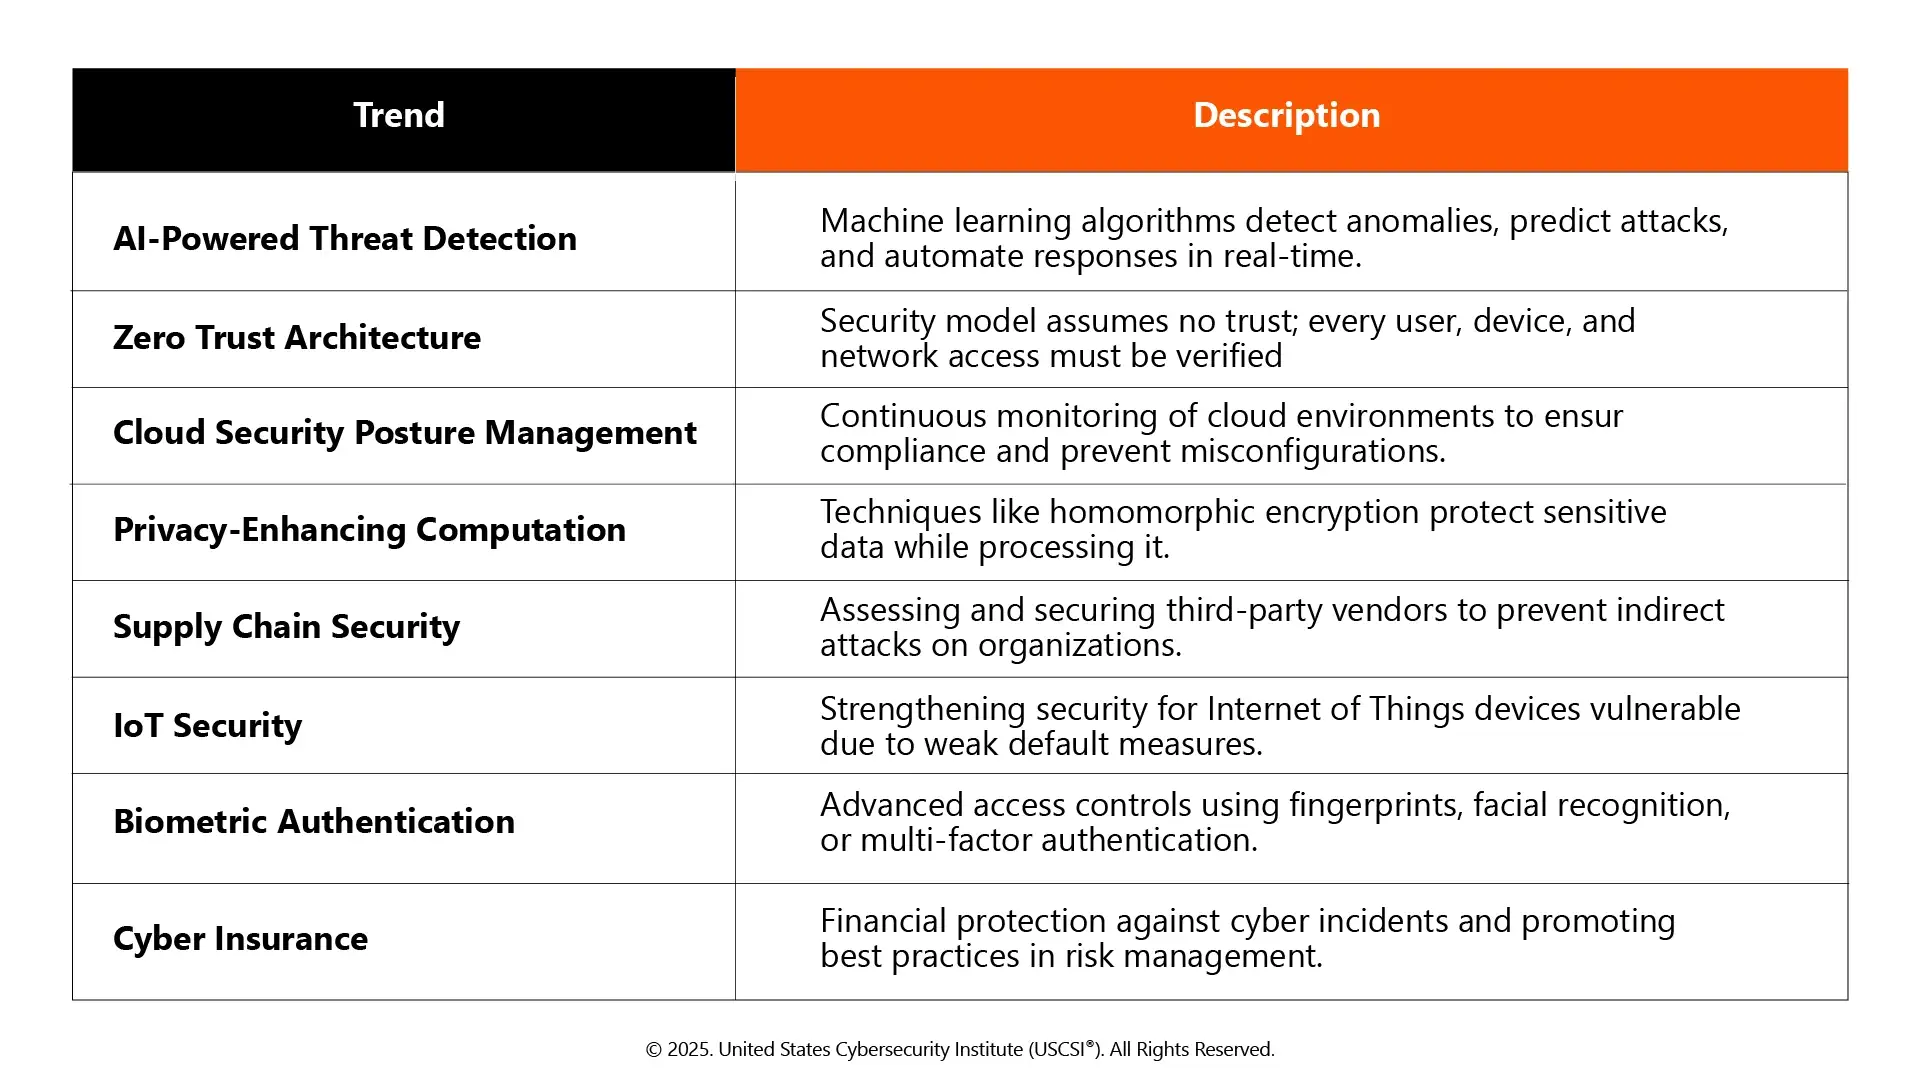
Such rapid execution fundamentally challenges conventional security models that rely on slower detection cycles. Enterprises are now forced to adopt a hyper-vigilant, pre-emptive posture, focusing on zero-trust architectures, real-time threat hunting, and the rapid deployment of AI-powered defensive mechanisms capable of autonomous anomaly detection and remediation within minutes, not days.
The Quantum Shadow and Data Exfiltration
While not an active decryption threat in 2026, the specter of quantum computing looms large. Nation-states and advanced persistent threat (APT) groups are engaged in "harvest now, decrypt later" campaigns. Encrypted data, even if currently impenetrable, is being exfiltrated and stored, awaiting the advent of sufficiently powerful quantum computers capable of breaking current asymmetric cryptography standards. This pre-computation strategy means that data deemed secure today, particularly sensitive intellectual property or long-term strategic plans, could be compromised years down the line, affecting long-term enterprise ROI and national security.
Verified Data / Metrics Breakdown: The Cost of Complacency
The World Economic Forum and collaborating security entities have projected alarming figures for 2026, underscoring the critical need for proactive cybersecurity investment and robust risk mitigation strategies. These metrics represent conservative estimates, with real-world impacts potentially far exceeding these projections:
| Metric / Threat Category | 2025 Projected Baseline | 2026 Forecasted Impact | Key Implication for Enterprises |
|---|---|---|---|
| Global Cost of Cybercrime | $10.5 Trillion | $13.8 Trillion (+31%) | Significant erosion of market liquidity and capital allocation towards recovery. |
| AI-Driven Attack Success Rate | 28% | 45% (+60%) | Rethinking cloud compute architecture and human-machine security interface. |
| Critical Infrastructure Breaches (Publicly Disclosed) | 150 incidents | 220 incidents (+47%) | National security imperative, disruption to essential services, potential loss of life. |
| Average Time to Identify & Contain a Breach | 277 days | 210 days (if AI defense adopted) | Direct correlation to enterprise ROI and regulatory compliance penalties. |
| Estimated Global Cybersecurity Talent Shortage | 3.5 Million | 4.2 Million (+20%) | Exacerbates vulnerabilities; drives demand for AI-driven automation. |
Industry & Market Implications: Who Wins, Who Loses?
The heightened cyber threat landscape in 2026 creates clear demarcation lines for corporate success and failure:
Winners:
- AI-Native Cybersecurity Providers: Firms specializing in autonomous threat detection, response, and proactive threat hunting will see significant demand. Their valuation multiples will soar as enterprises prioritize cutting-edge defense.
- Managed Security Service Providers (MSSPs) with Deep Expertise: Organizations that can outsource sophisticated security operations to specialized MSSPs will gain an advantage, particularly those offering advanced cloud compute architecture security and regulatory compliance frameworks.
- Cyber Resilience & Recovery Specialists: Beyond prevention, companies excelling in rapid disaster recovery, business continuity, and post-breach forensics will be essential.
- Post-Quantum Cryptography Innovators: Early movers in PQC will secure long-term strategic contracts from governments and critical infrastructure operators.
Losers:
- Organizations with Legacy Security Infrastructures: Those failing to modernize their defense, especially concerning cloud security and OT/ICS protection, will face catastrophic breaches and crippling financial penalties. Their enterprise ROI will plummet, impacting valuation multiples.
- Sectors with High Exposure, Low Resilience: Small and medium-sized enterprises (SMEs) within critical supply chains are particularly vulnerable, as a single compromise can ripple through larger ecosystems.
- Companies Neglecting Regulatory Compliance: The global push for data privacy and incident transparency means non-compliance will lead to severe fines, reputation damage, and loss of market liquidity.
The broader economic impact will manifest as increased capital allocation towards cybersecurity across all industries, potentially diverting funds from other innovation or growth initiatives. Supply chain disruptions due to cyberattacks will impact global trade flows, and the erosion of consumer trust in digital services could lead to broader market instability.
People Also Ask (FAQ)
Q1: How will AI fundamentally change the cyber threat landscape in 2026?
In 2026, AI transitions from an augmentation tool to a core component of both offensive and defensive cyber operations. On the offensive side, Generative AI enables the creation of highly sophisticated, polymorphic malware that can evade traditional signature-based detection, automates the reconnaissance phase for hyper-targeted attacks, and crafts deepfake-powered social engineering campaigns that are nearly impossible for humans to discern. This drastically reduces the skill ceiling for attackers while accelerating the speed and scale of campaigns. On the defensive side, AI is crucial for real-time anomaly detection, autonomous response, and predictive threat intelligence, turning the cybersecurity arms race into an AI-versus-AI battle, demanding significant investment in AI-driven risk mitigation platforms.
Q2: What sectors face the highest risk from evolving cyber threats in 2026?
The sectors facing the highest risk are critical infrastructure (energy, water, transportation, healthcare), financial services, and high-tech manufacturing. Critical infrastructure is a prime target for nation-state actors seeking to disrupt societal functions or exert geopolitical pressure, with attacks increasingly targeting Operational Technology (OT) and Industrial Control Systems (ICS). Financial services remain a perennial target due to direct monetary gain, now exacerbated by AI-powered fraud and market manipulation threats that impact market liquidity. High-tech manufacturing, particularly within defense and aerospace supply chains, faces intense intellectual property theft attempts, often with nation-state backing, to gain competitive advantage and compromise future technological development, directly affecting enterprise ROI and long-term valuation multiples.
Q3: What proactive measures can enterprises take to mitigate these 2026 threats?
Enterprises must adopt a multi-layered, proactive defense strategy. Key measures include implementing a robust Zero Trust architecture across all IT and OT environments, investing in advanced AI-driven security solutions for real-time threat detection and autonomous response, and securing their entire supply chain through rigorous vendor assessments and contractual obligations regarding cybersecurity posture. Additionally, continuous security awareness training, particularly against AI-enhanced social engineering, is vital. Organizations must also prioritize post-quantum cryptography roadmaps to protect long-term data, enhance incident response capabilities to meet the "two-week timeline" challenge, and ensure stringent regulatory compliance with evolving global data protection mandates to minimize financial and reputational damage. Comprehensive cyber insurance, tailored to the unique risks of 2026, is also becoming a critical component of risk mitigation and capital allocation strategies.
Future Outlook: A Relentless Digital Arms Race
Looking beyond 2026, the trajectory is clear: the digital arms race will intensify. The development of defensive AI will need to match or exceed the pace of offensive AI, creating a perpetual cycle of innovation and adaptation. Key milestones to watch include the maturation of sovereign cloud compute architecture, the widespread adoption of verifiable digital identities, and the emergence of genuinely self-healing, resilient network infrastructures.
The imperative for international cooperation on cyber norms and information sharing will become more pronounced, even as geopolitical tensions fuel state-sponsored attacks. Regulatory compliance frameworks will likely converge globally, pushing for higher standards of data governance and incident transparency. For enterprises, cybersecurity will cease to be merely an IT function; it will be an existential board-level concern, directly influencing investment decisions, capital allocation, infrastructure scalability, and ultimately, long-term valuation multiples in an increasingly digitized global economy. The battle for digital trust, and indeed, digital sovereignty, has only just begun.